
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended
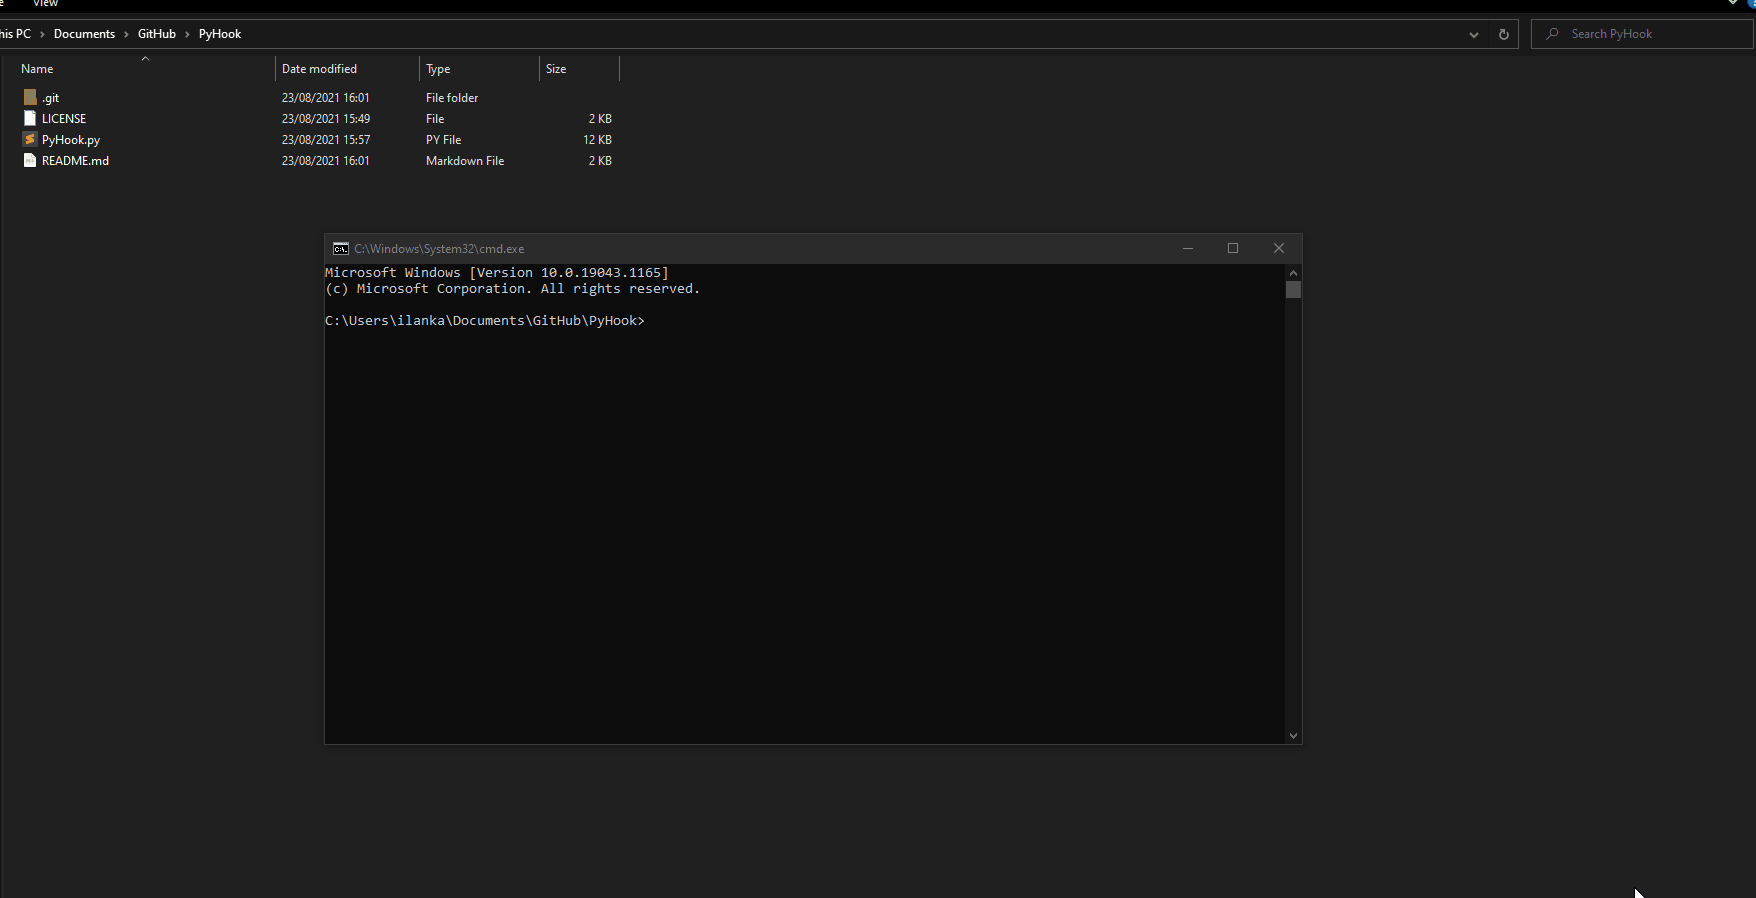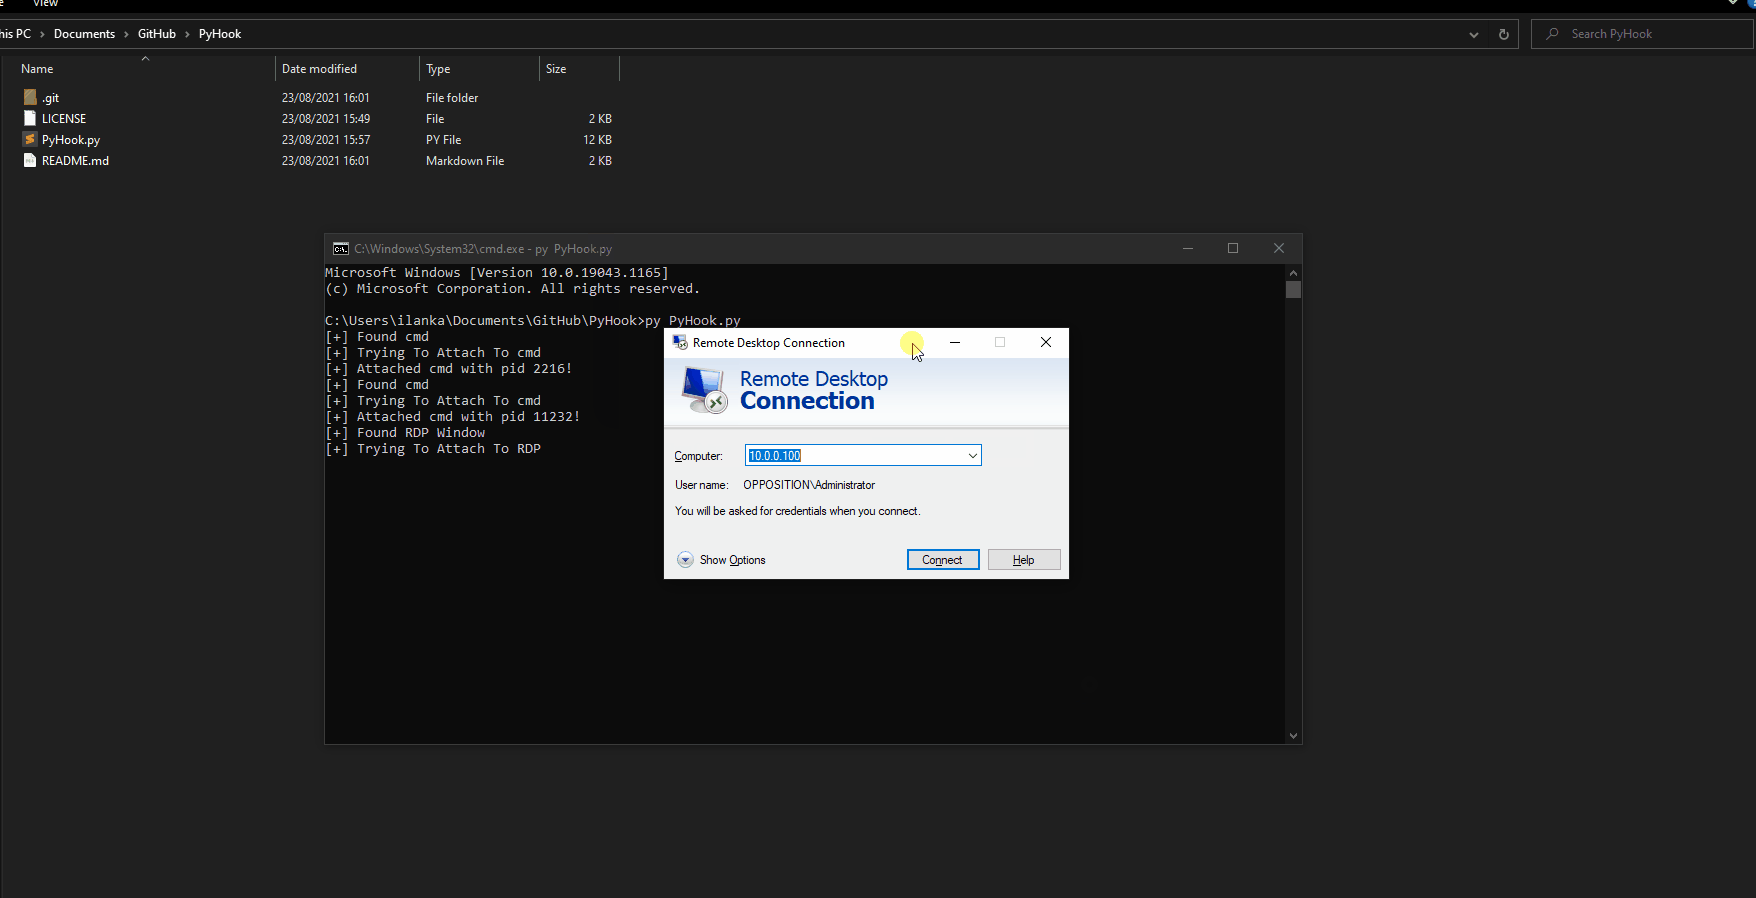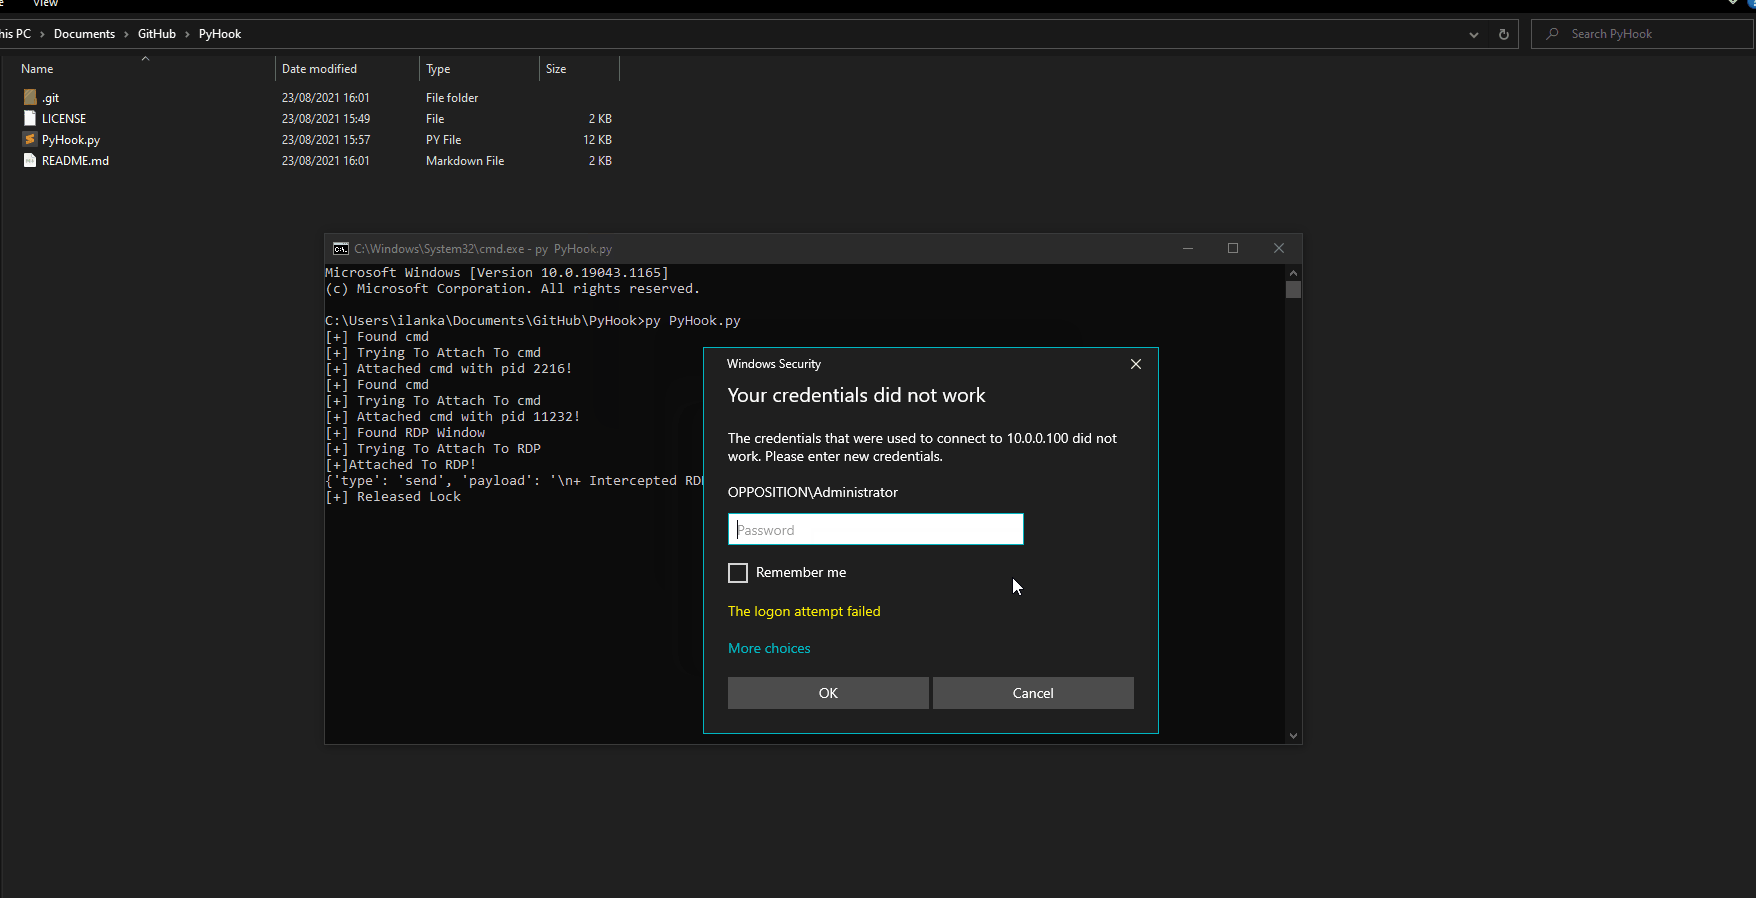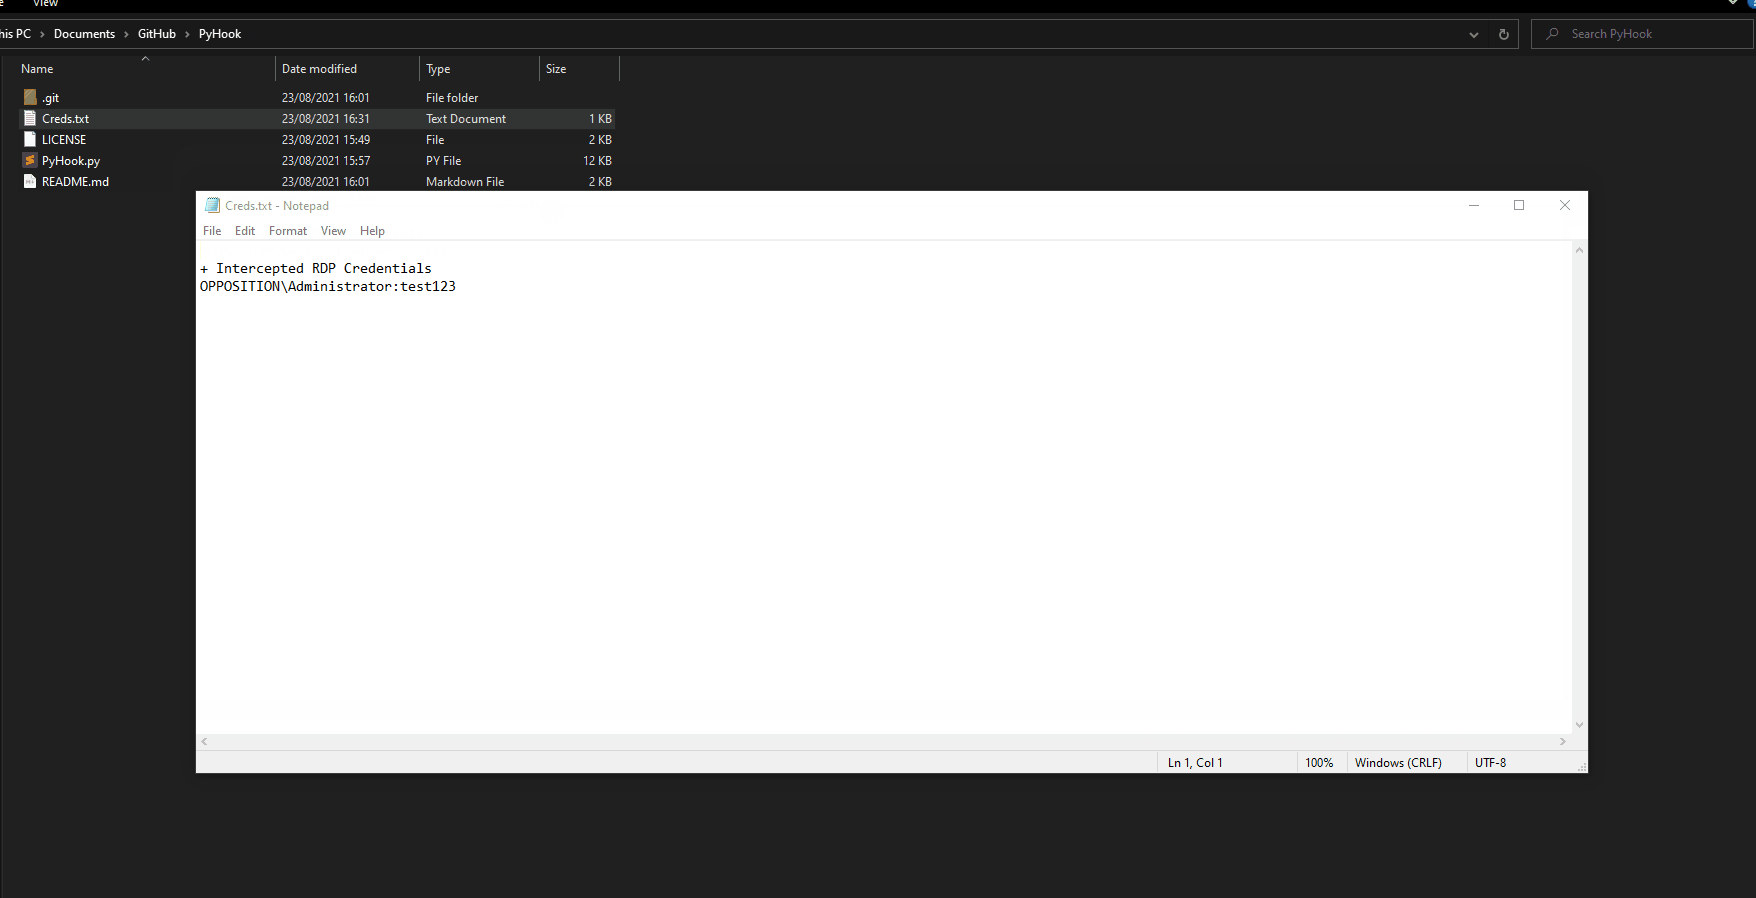
 ilankalendarov/pyhook
Offensive API hooking tool using Frida to intercept Windows API calls and capture credentials from processes like mstsc, runas, PowerShell, cmd,…
 r3ggi/electroniz3r
Take over macOS Electron apps' TCC permissions
 noptrix/sshprank
A fast SSH mass-scanner, login cracker, banner grabber and password auth checker tool using the python-masscan and shodan module.
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 leo4j/invoke-sessionhunter
Retrieve and display information about active user sessions on remote computers. No admin privileges required.
 rad9800/wtsrm2
Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
 yolop0wn/echodrv
Exploitation of echo_driver.sys

 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 sadreck/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
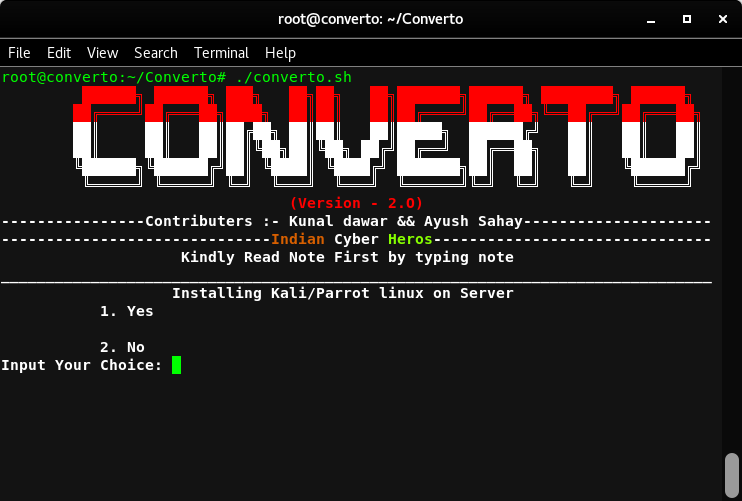 developerkunal/converto
Installing Kali linux on Vps Server
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).








