
 #1
Tools for gathering information about targets and identifying attack surfaces.
Kitploit recommended
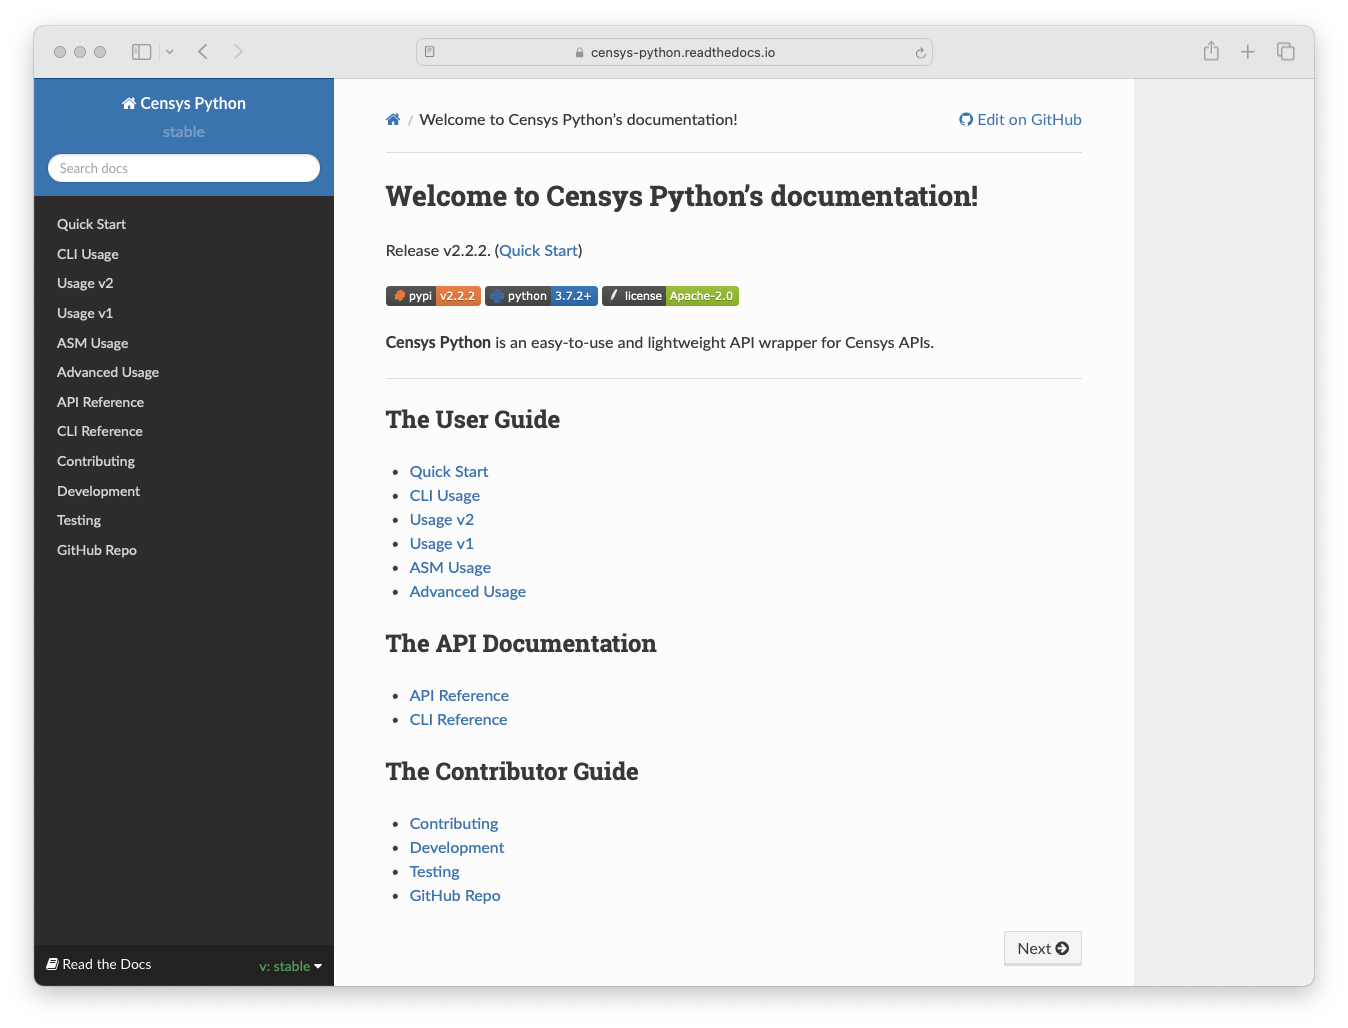
 censys/censys-python
An easy-to-use and lightweight API wrapper for Censys APIs.
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 vatsalgupta67/all-in-one-cybersecurity-resources
List of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
 ooni/probe-cli
Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…
 p0dalirius/apachetomcatscanner
A python script to scan for Apache Tomcat server vulnerabilities.
 itsmehacker/darkscrape
OSINT Tool For Scraping Dark Websites
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 vonahisec/leprechaun
This tool is used to map out the network data flow to help penetration testers identify potentially valuable targets.
 tomcarver16/adsearch
A tool to help query AD via the LDAP protocol
 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
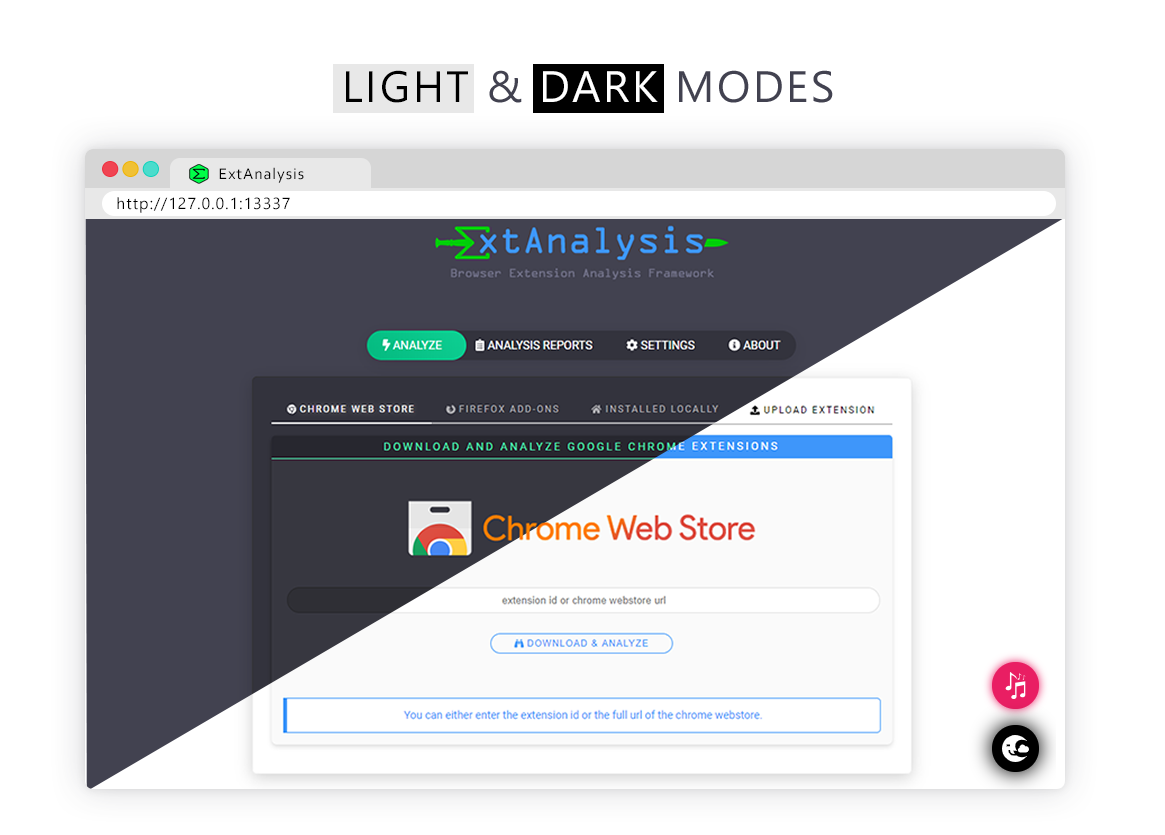 tuhinshubhra/extanalysis
Browser Extension Analysis Framework - Scan, Analyze Chrome, firefox and Brave extensions for vulnerabilities and intels
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 esc4icescesc/skanuvaty
Dangerously fast DNS/network/port scanner
 caster0x00/above
Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
 knavesec/max
Suite of tools for BloodHound that enables domain password auditing, privilege path analysis, edge manipulation, and custom Cypher queries to…
 hisxo/reconaizer
A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!








