
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 fatrodzianko/get-rbcd-threaded
Tool to discover Resource-Based Constrained Delegation attack paths in Active Directory environments
 nmulasmajic/cve-2018-8897
Implements the POP/MOV SS (CVE-2018-8897) vulnerability by bugchecking the machine (local DoS).
 jollheef/libreoffice-remote-arbitrary-file-disclosure
Proof of concept of LibreOffice remote arbitrary file disclosure vulnerability
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
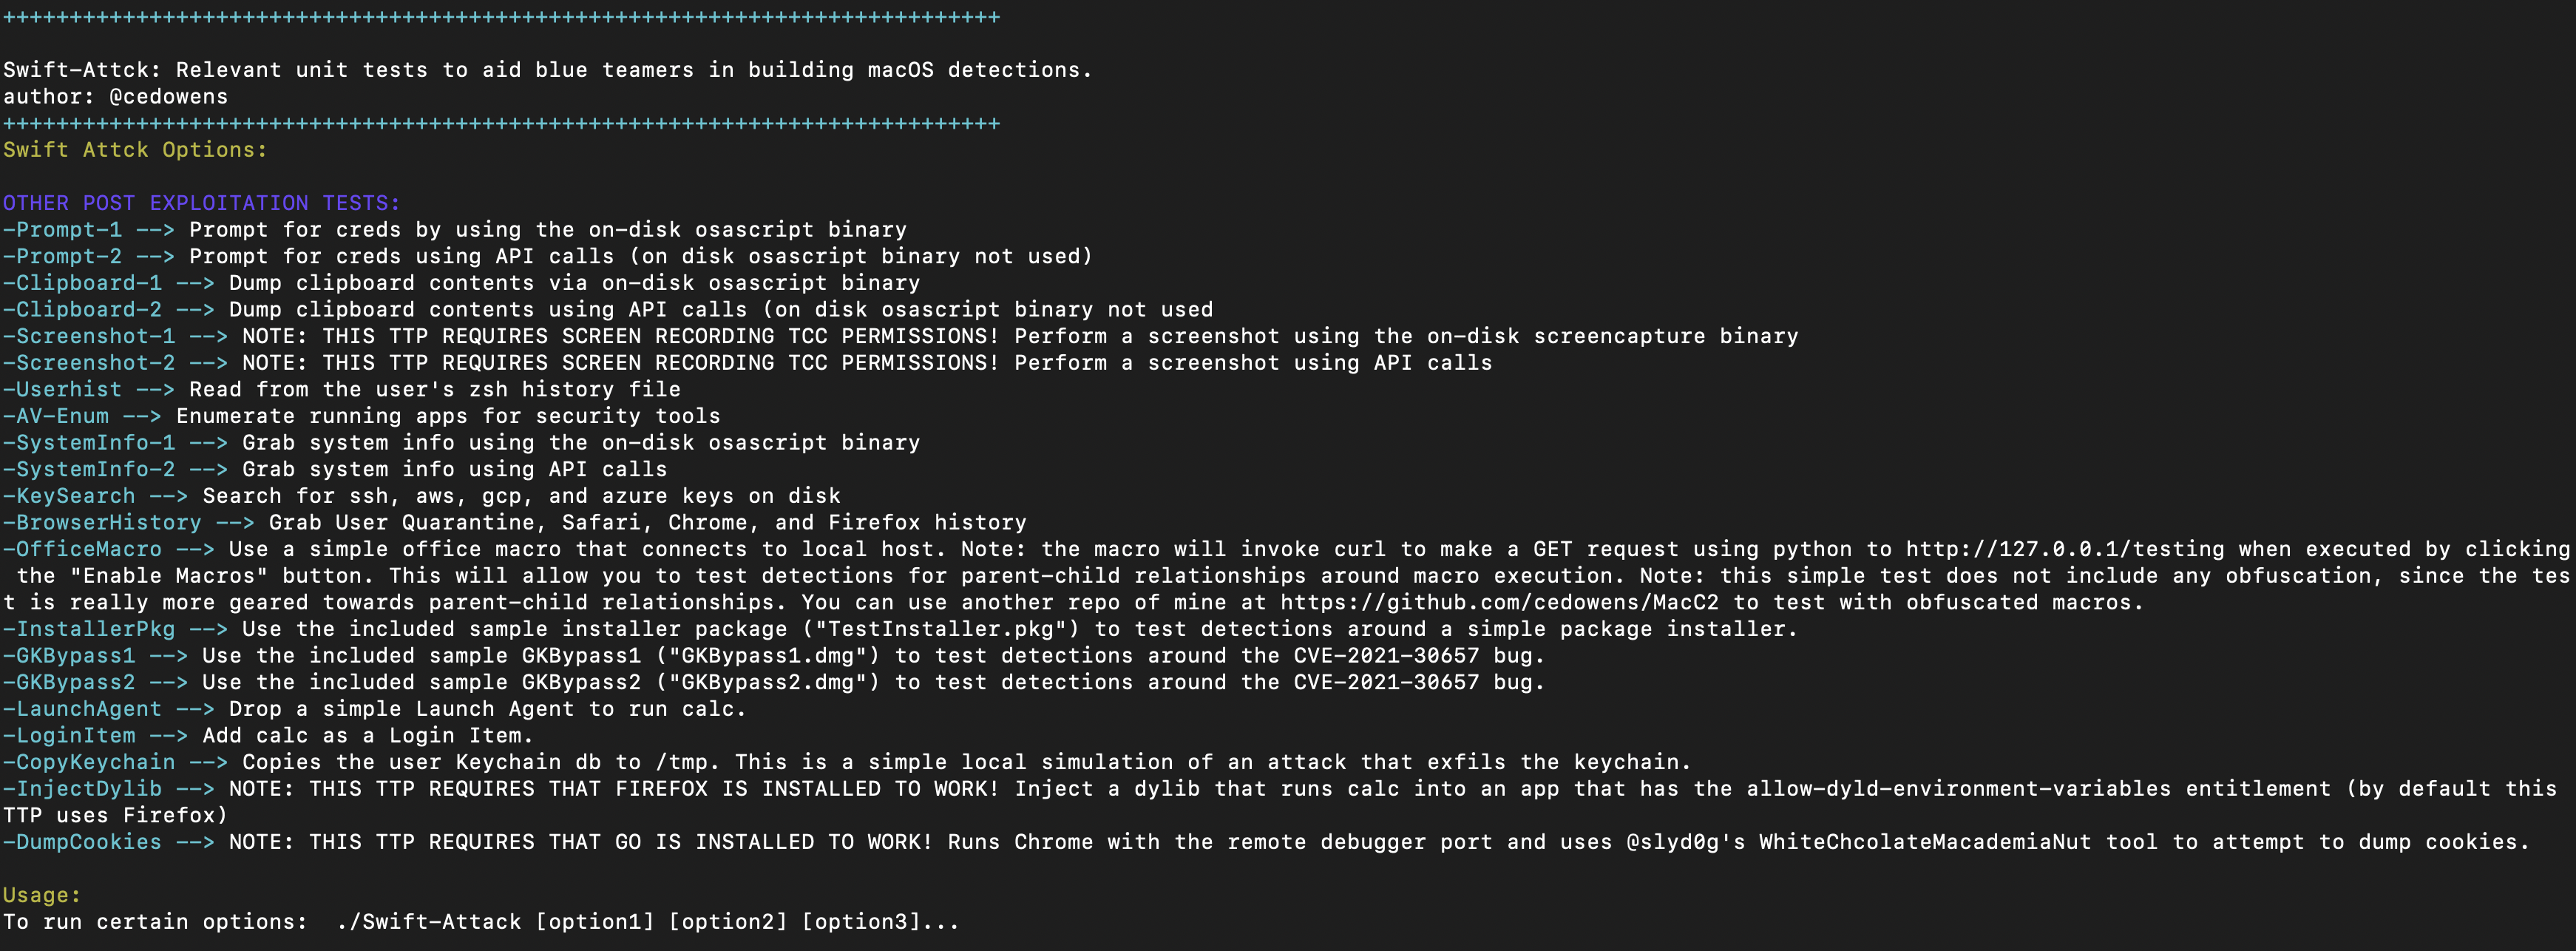 cedowens/swift-attack
Unit tests for blue teams to aid with building detections for some common macOS post exploitation methods.
 deadjakk/reg1c1de
Registry permission scanner written in C# for finding potential privesc avenues within registry
 estimated1337/lenovo_exec
CVE-2022-3699 with arbitrary kernel code execution capability
 deh00ni/ntdumpbof
Cobalt Strike BOF that creates an LSASS minidump in memory and exfiltrates it over the C2 callback for offline credential parsing with Mimikatz or…
 zcgonvh/ms16-032
MS16-032(CVE-2016-0099) for SERVICE ONLY
 manizada/cifswitch
Proof-of-concept exploit for CVE-2026-46243, leveraging a fake NSS library and namespace manipulation to escalate privileges via cifs.upcall.
 secdev02/easytokens
Kali365 - EvilTokens Replica
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
 connectedlucy/plague
Default Detections for EDR








