
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended

 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
 nilotpalbiswas/auto-root-exploit
Auto Root Exploit Tool
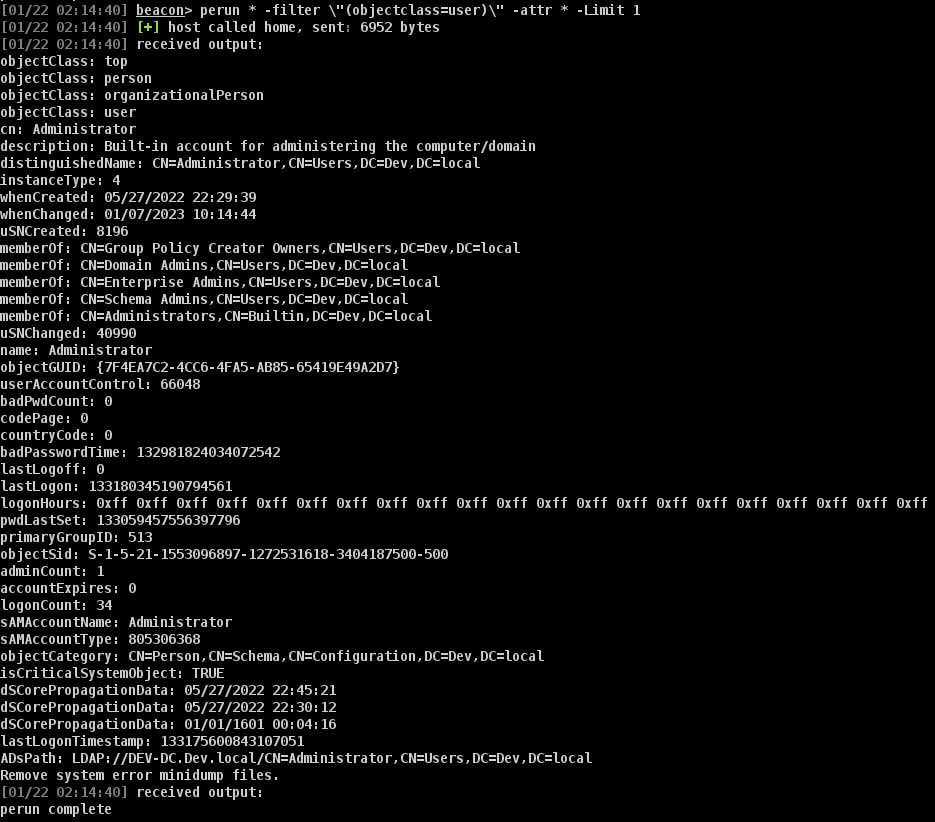 octoberfest7/inline-execute-pe
Execute unmanaged Windows executables in CobaltStrike Beacons
 chudry/xerror
fully automated pentesting tool
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 empireproject/empire-gui
Empire client application
 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 dec0ne/hwsyscalls
HWSyscalls is a new method to execute indirect syscalls using HWBP, HalosGate and a synthetic trampoline on kernel32 with HWBP.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 defaultnamehere/cookie_crimes
Read local Chrome cookies without root or decrypting
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 cenglin123/steganographiergui
将文件隐写进MP4/MKV文件中 (Embed files into MP4/MKV files.)
 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 d4vinci/pyloggy
A python keylogger that does more than any other keylogger - Key logger, Clicks logger and Screenshots








