
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended
 v-byte-cpu/sx
:vulcan_salute: Fast, modern, easy-to-use network scanner
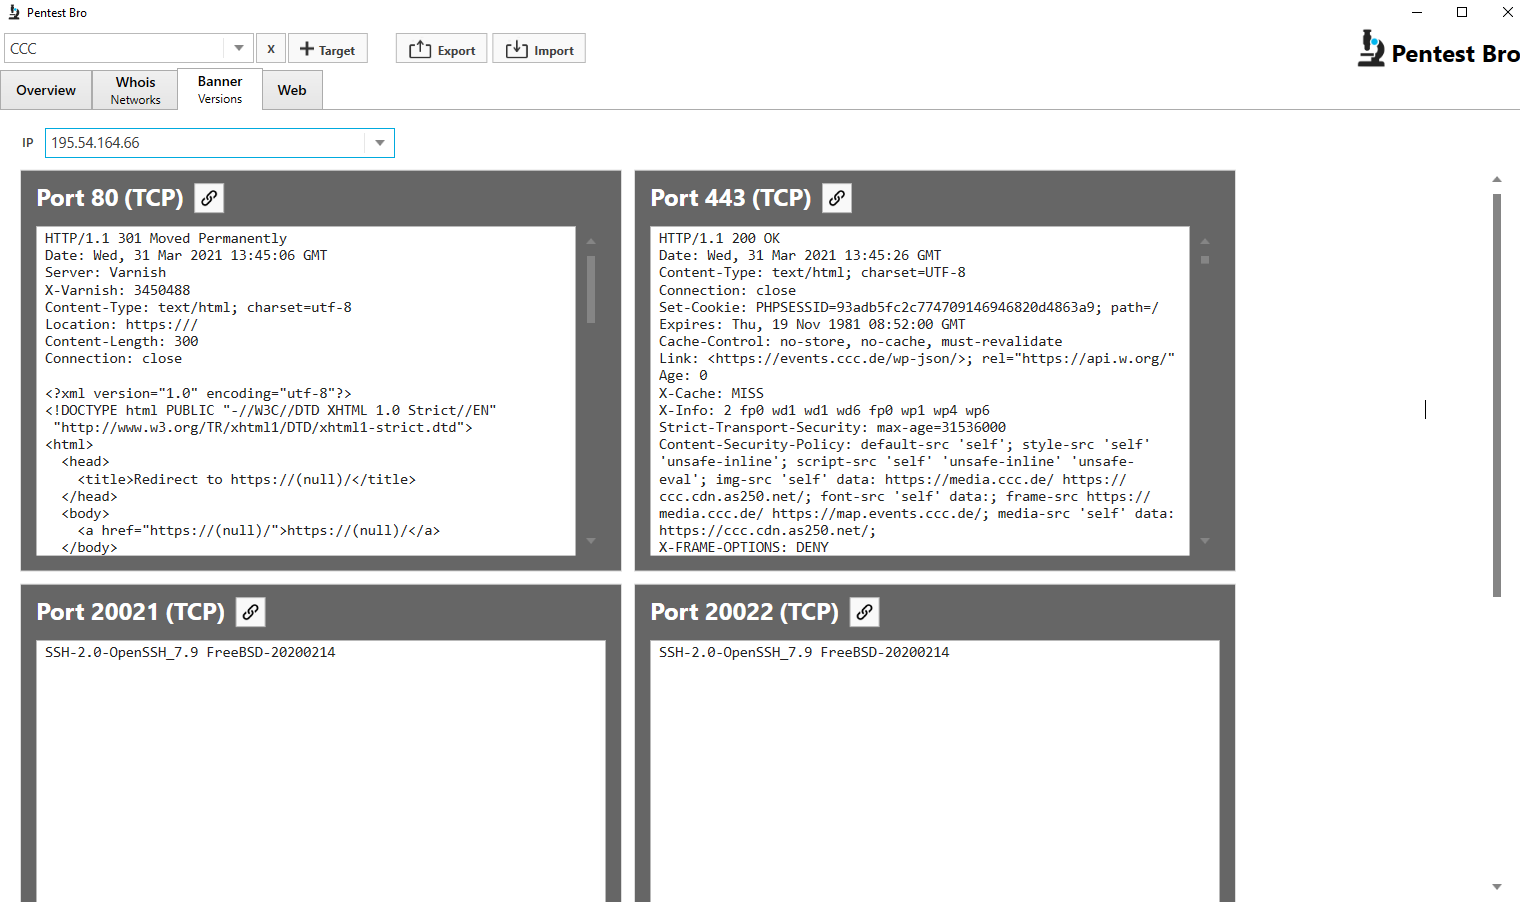 marius-rothenbuecher/pentestbro
Windows-based reconnaissance tool combining subdomain enumeration, port scanning, banner grabbing, whois lookups, and web path enumeration for…
 snovvcrash/divideandscan
Divide full port scan results and use it for targeted Nmap runs

 isnic/prober
Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 codingo/reconnoitre
A security tool for multithreaded information gathering and service enumeration whilst building directory structures to store results, along with…
 robertdavidgraham/masscan
TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 firefart/wordpresspingbackportscanner
WordpressPingbackPortScanner
 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 pownjs/recon
A powerful target reconnaissance framework powered by graph theory.
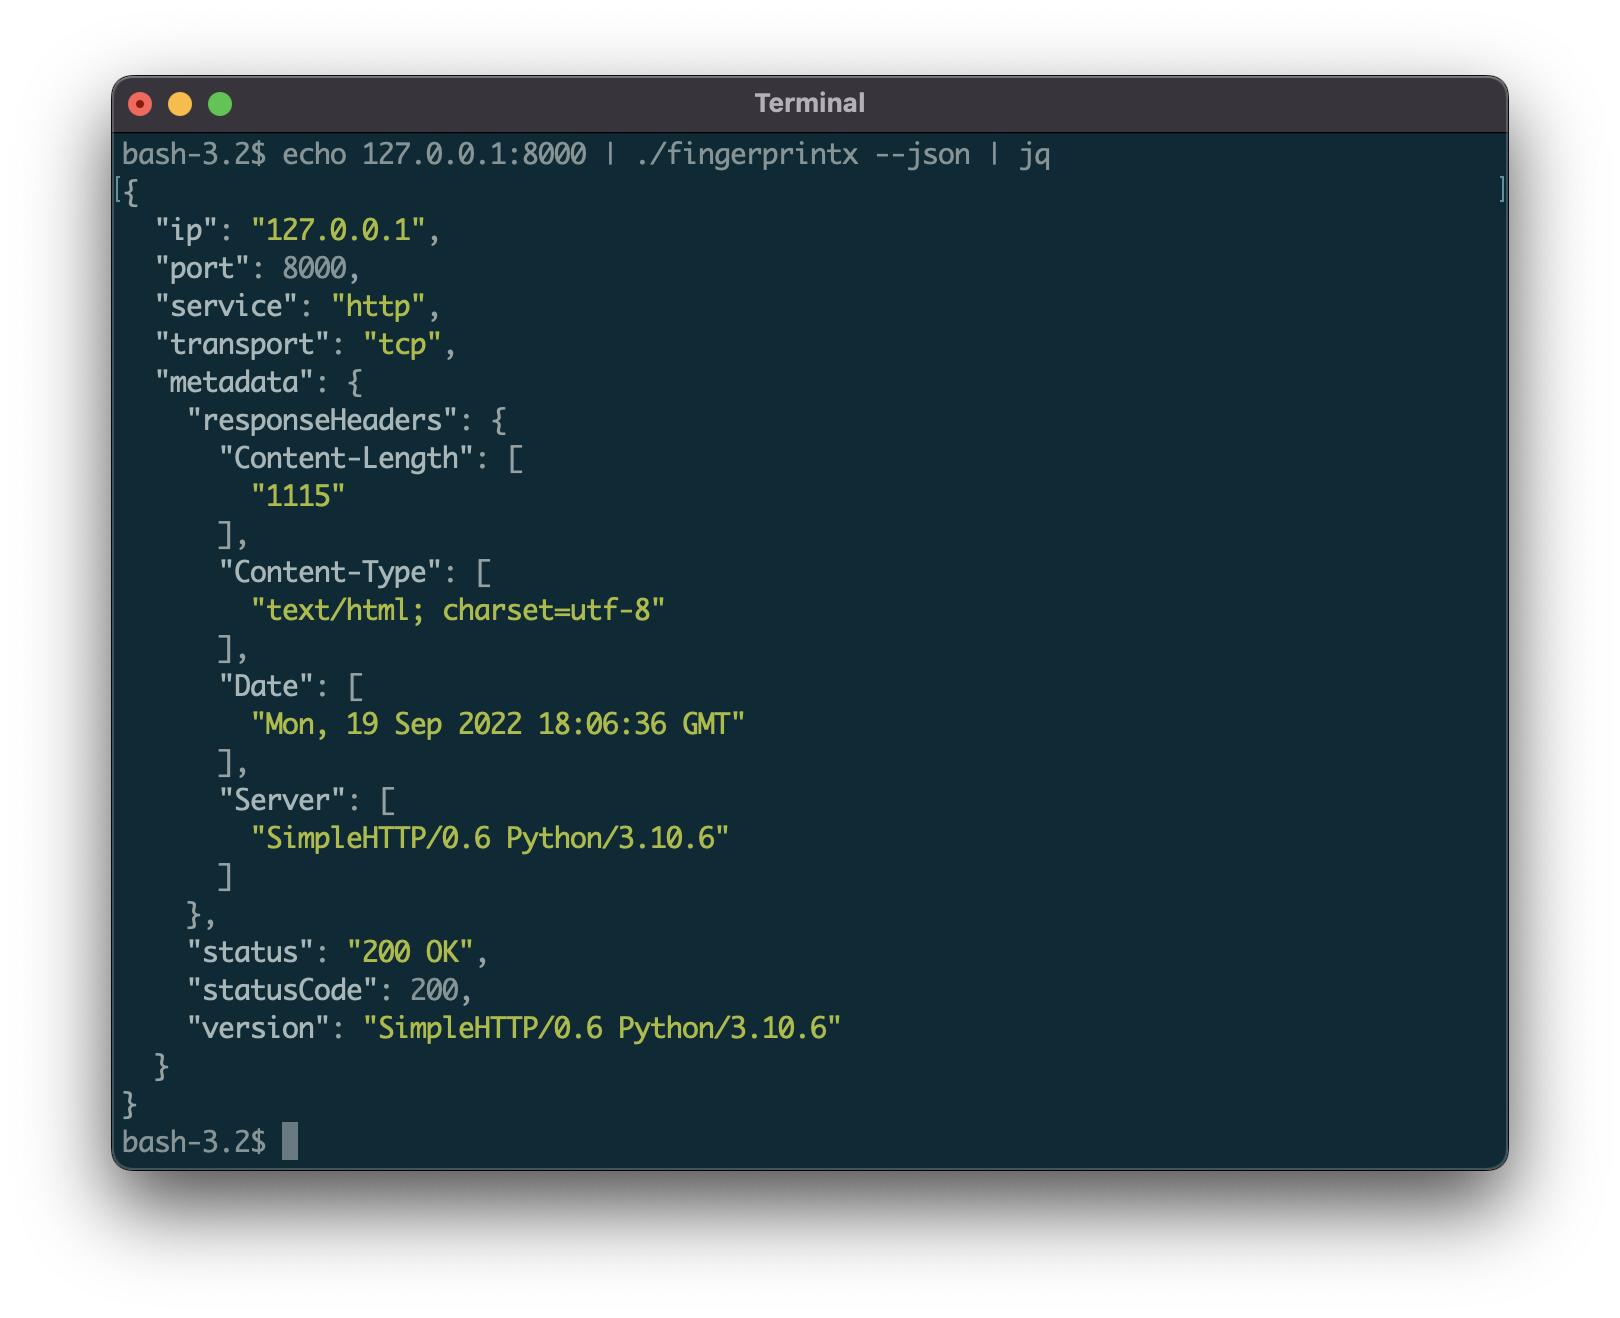 praetorian-inc/fingerprintx
Standalone utility for service discovery on open ports!
 nullt3r/jfscan
JF⚡can - Super fast port scanning & service discovery using Masscan and Nmap. Scan large networks with Masscan and use Nmap's scripting abilities to…






