
 #1
Penetration testing methodologies, frameworks, reporting, and automation tools.
Kitploit recommended

 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
 samyk/slipstream
NAT Slipstreaming allows an attacker to remotely access any TCP/UDP services bound to a victim machine, bypassing the victim’s NAT/firewall, just by…
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
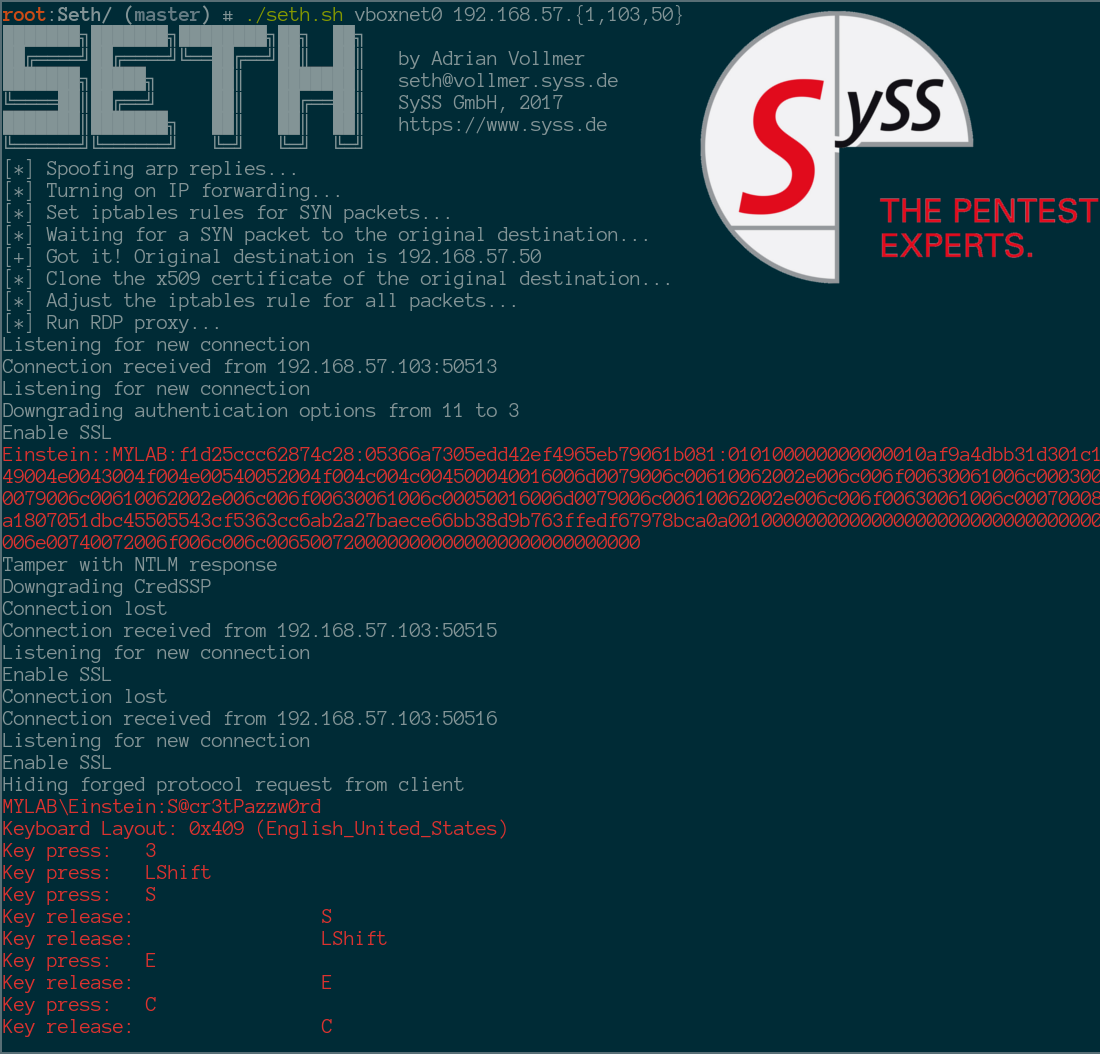 syss-research/seth
Perform a MitM attack and extract clear text credentials from RDP connections
 fortra/nanodump
The swiss army knife of LSASS dumping
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 lionsec/xerosploit
Efficient and advanced man in the middle framework
 ascotbe/kernelhub
:palm_tree:Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability…
 govolution/avet
AntiVirus Evasion Tool
 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 six2dez/onelistforall
Curated, categorized wordlist generator for web fuzzing, directory enumeration, and subdomain discovery. Automatically syncs 36+ sources, classifies…
 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 mandatoryprogrammer/xsshunter
The XSS Hunter service - a portable version of XSSHunter.com
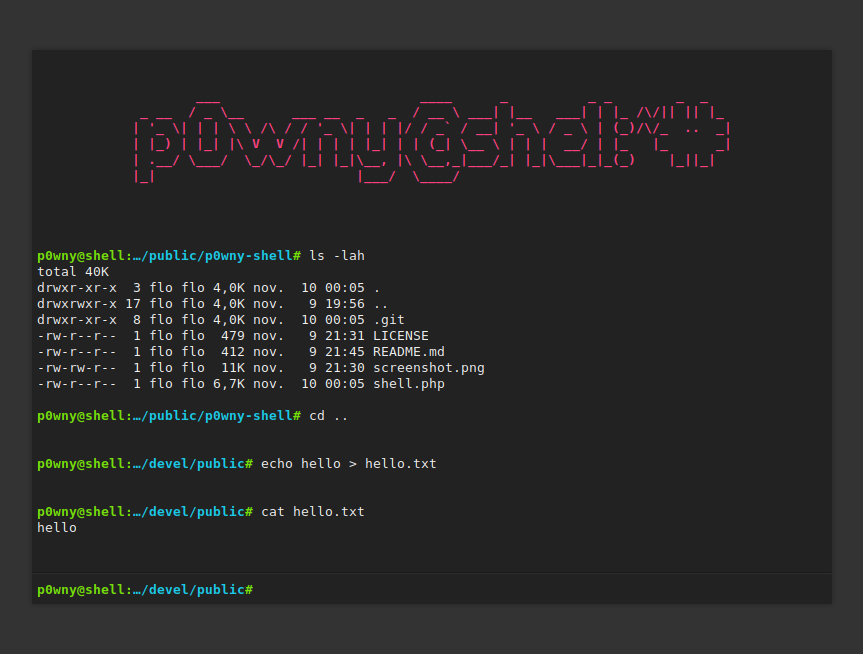 flozz/p0wny-shell
Single-file PHP shell
 enjoiz/xxeinjector
Tool for automatic exploitation of XXE vulnerability using direct and different out of band methods.








