
 #1
Penetration testing methodologies, frameworks, reporting, and automation tools.
Kitploit recommended
 eqstlab/cve-2026-109619
Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
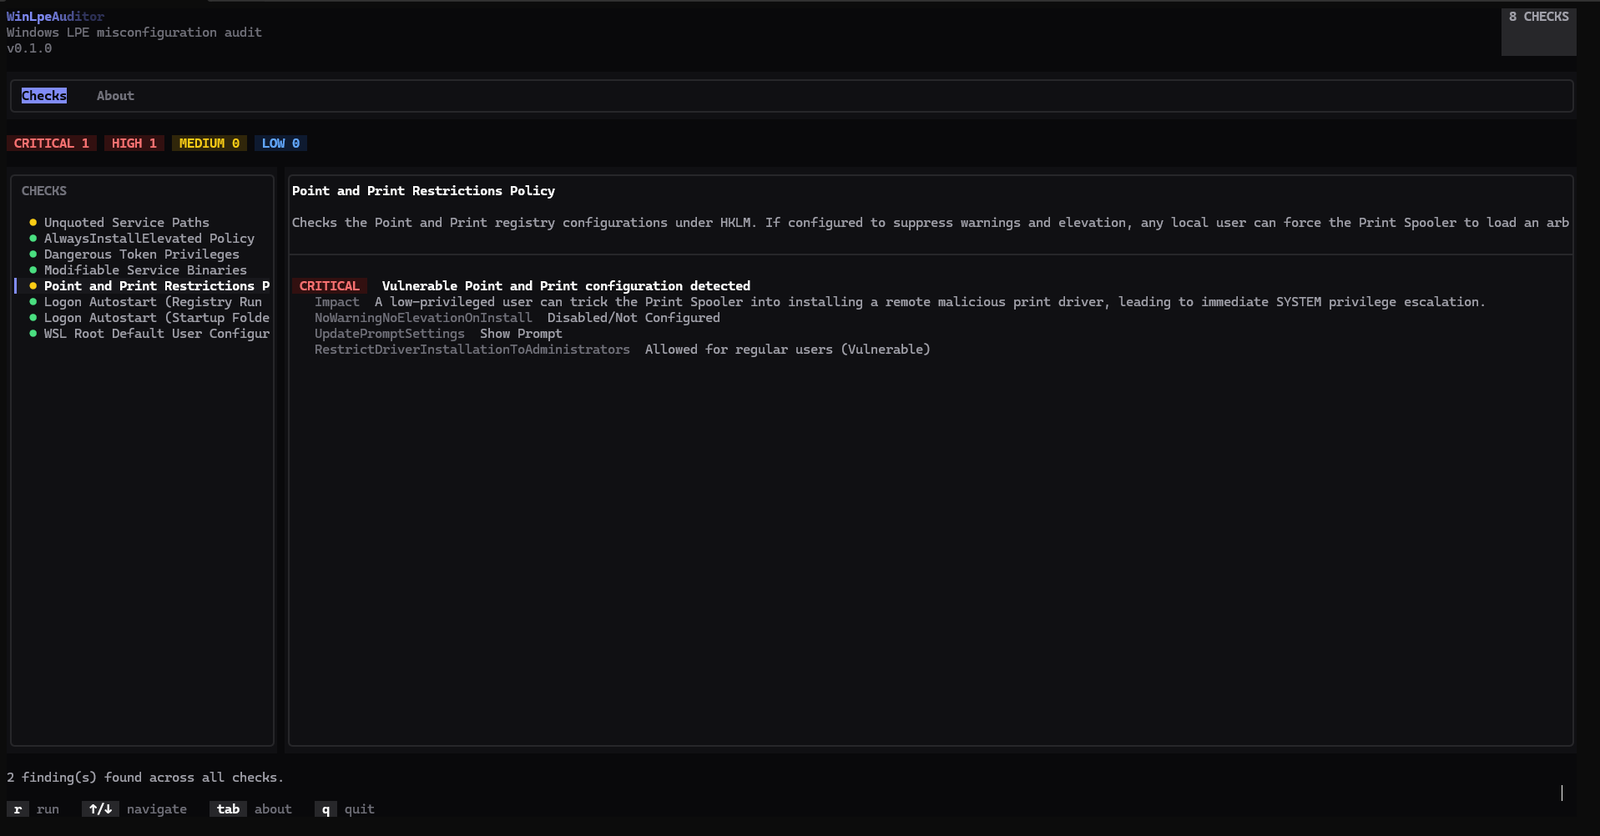 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
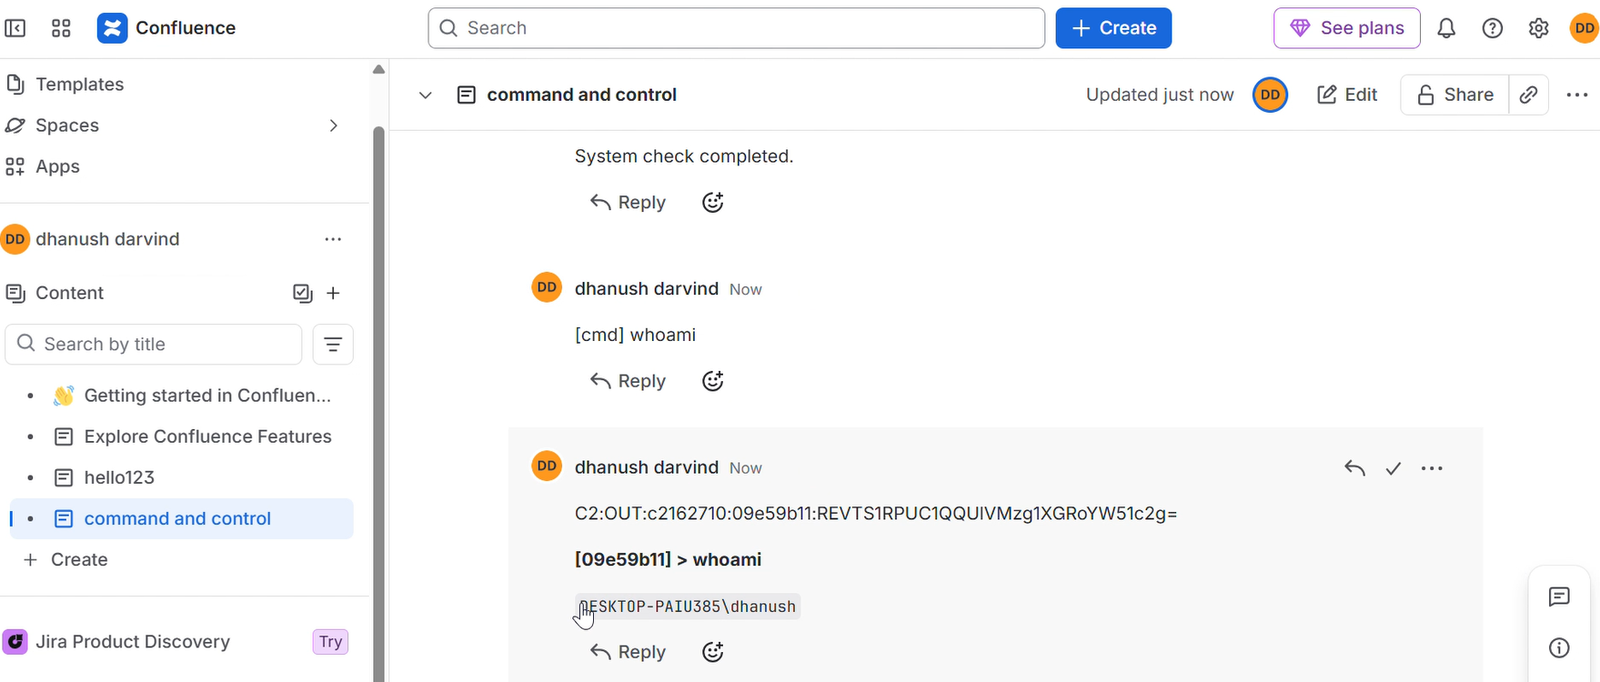 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 assetnote/php2shell-scanner
High fidelity scanner for php2shell (CVE-2026-109618 and CVE-2026-109619)
 eness/php2shell-cve-2026-109618-cve-2026-109619-poc
Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments.…
 david-alvarez-rosa/php-rce
Exploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
 ghxstsec/php2shell-poc
Python exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
 david-alvarez-rosa/php-rce
Exploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
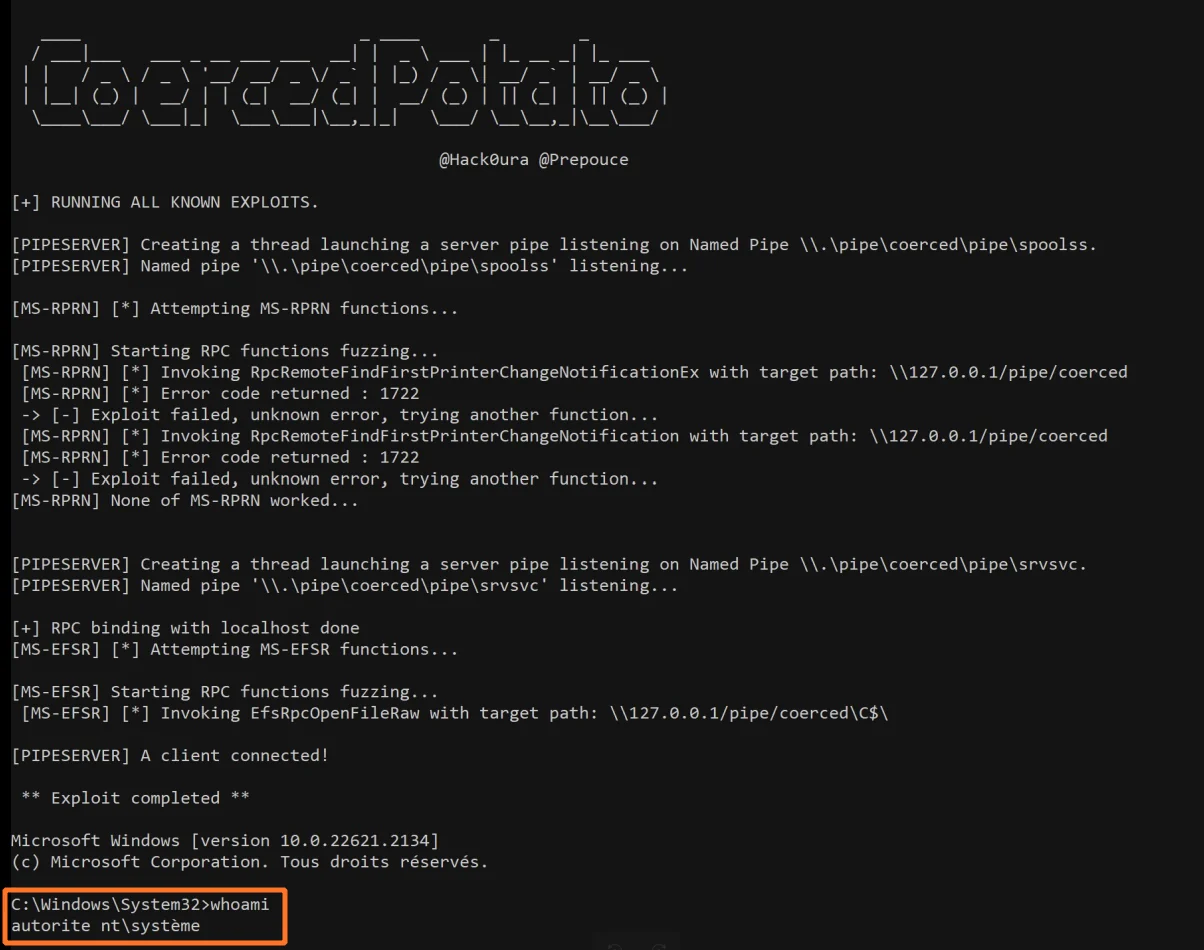 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 laremontada12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…








