
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 shelld3v/cve-2019-11580
A CVE-2019-11580 shell
 c5z54/cve-2026-62911-poc
CVE-2026-62911 — Exchange MRSProxy Pre-Auth RCE PoC | Scanner + Exploit | NTLM Relay → Webshell → SYSTEM
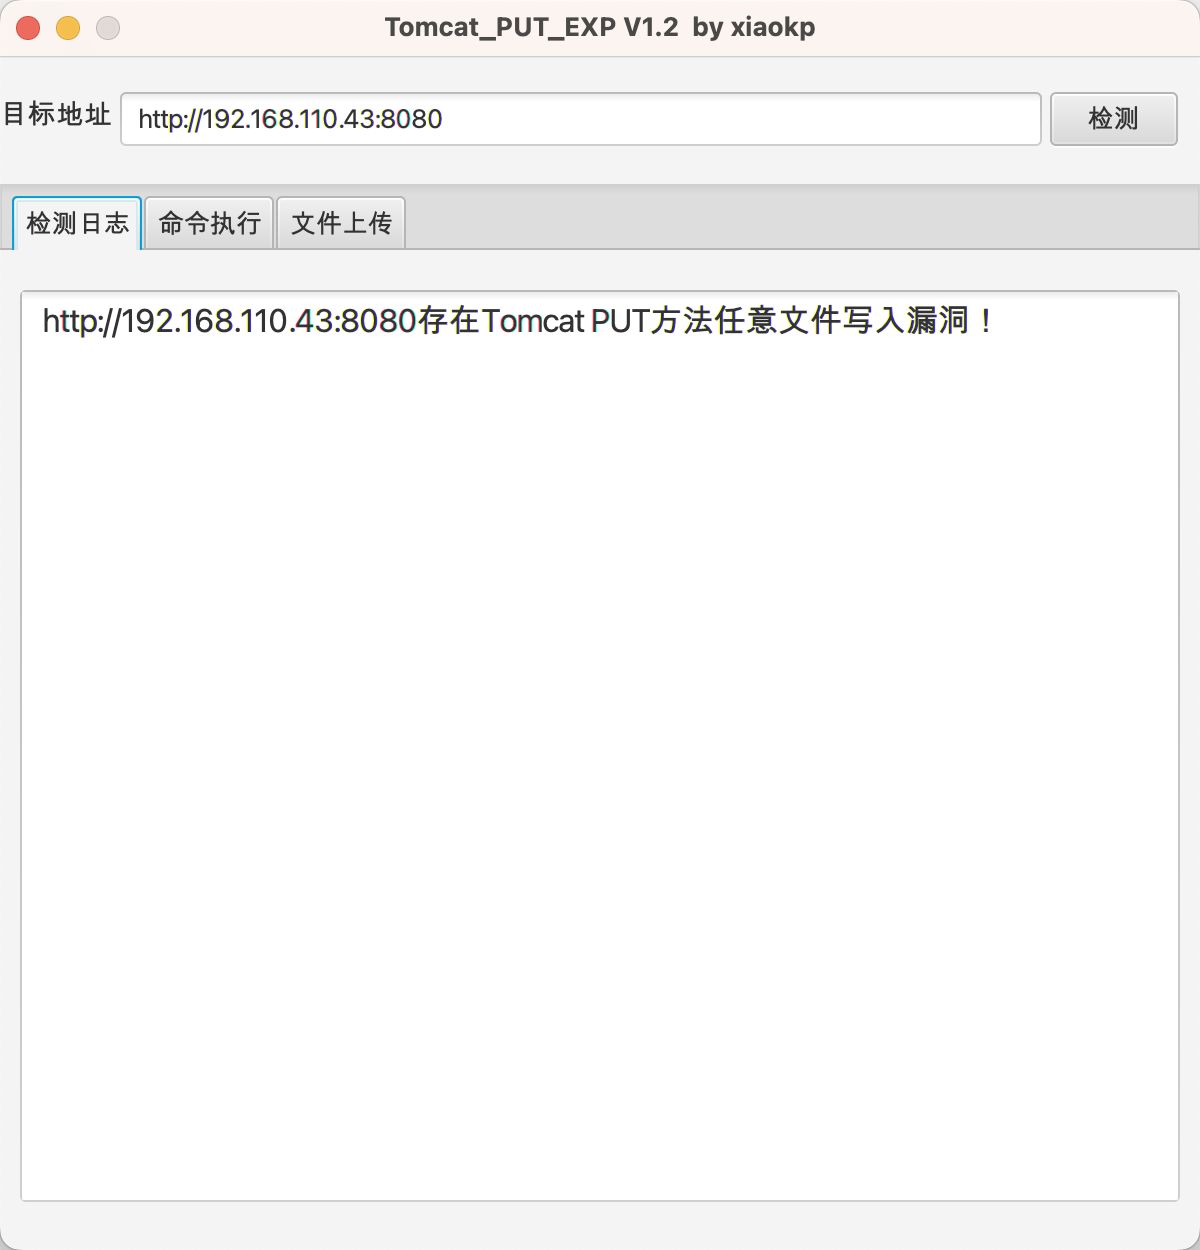 xiaokp7/tomcat_put_gui_exp
Tomcat PUT方法任意文件写入(CVE-2017-12615)exp
 donofly/cve-2025-22457-vulnserver-lab
Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 elitexspam/def4cer
A Secure Version of CVE-2026-53787 Amasty Order Attribute File Upload Exploit,with the modification of file upload of txt to html.
 nxploited/cve-2026-3891
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload
 tonixtoolkitofficial-afk/esp32-blue-ducky
ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.
 ktn1990/cve-2019-9978
Wordpress Social Warfare Remote Code Execution (AUTO UPLOAD SHELL)
 thau0x01/poc_proxylogon
Microsoft Exchange ProxyLogon PoC (CVE-2021-26855)
 gh0st0ne/weaponized-0604
Automated tool to exploit sharepoint CVE-2019-0604
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 zi0black/poc-cve-2017-12615-or-cve-2017-12717
CVE-2017-12617 and CVE-2017-12615 for tomcat server
 0x00-0x00/cve-2018-10517
CMS Made Simple 2.2.7 RCE exploit
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
 jimidk/better-cve-2022-29464
Proof-of-concept exploit for CVE-2022-29464 enabling unrestricted file upload and remote code execution on vulnerable WSO2 products, with a custom…
 z92g/cve-2021-31805
S2-061/S2-062 Struts2 远程命令执行漏洞 POC&EXP
 grimlockx/cve-2019-9978
Remote Code Execution in Social Warfare Plugin before 3.5.3 for Wordpress.








