
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended

 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 acheong08/cve-2025-55182-poc
Actual CVE-2025-55182 detection and exploit. No bullshit LLMs.
 ckkok/spring4shell-poc
Proof-of-concept exploit for Spring4Shell (CVE-2022-22965) that deploys a JSP webshell via crafted HTTP requests to vulnerable Spring Boot…
 0dayninja/cve-2021-3560
Polkit D-Bus Authentication Bypass Exploit
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 sunnyvale-it/cve-2021-44228-poc
CVE-2021-44228 (Log4Shell) Proof of Concept
 ianxtianxt/discuz-ml-rce
影响系统及版本:Discuz!ML V3.2-3.4 Discuz!x V3.2-3.4
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 zemarkhos/cve-2025-55315-poc-exploit
CVE-2025-55315 PoC Exploit
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
 ahmed-fa7im/cve-2023-38831-winrar-expoit-simple-poc
CVE-2023-38831 winrar exploit generator and get reverse shell
 immunityinc/log4j-jndiserver
This project will help to test the Log4j CVE-2021-44228 vulnerability.
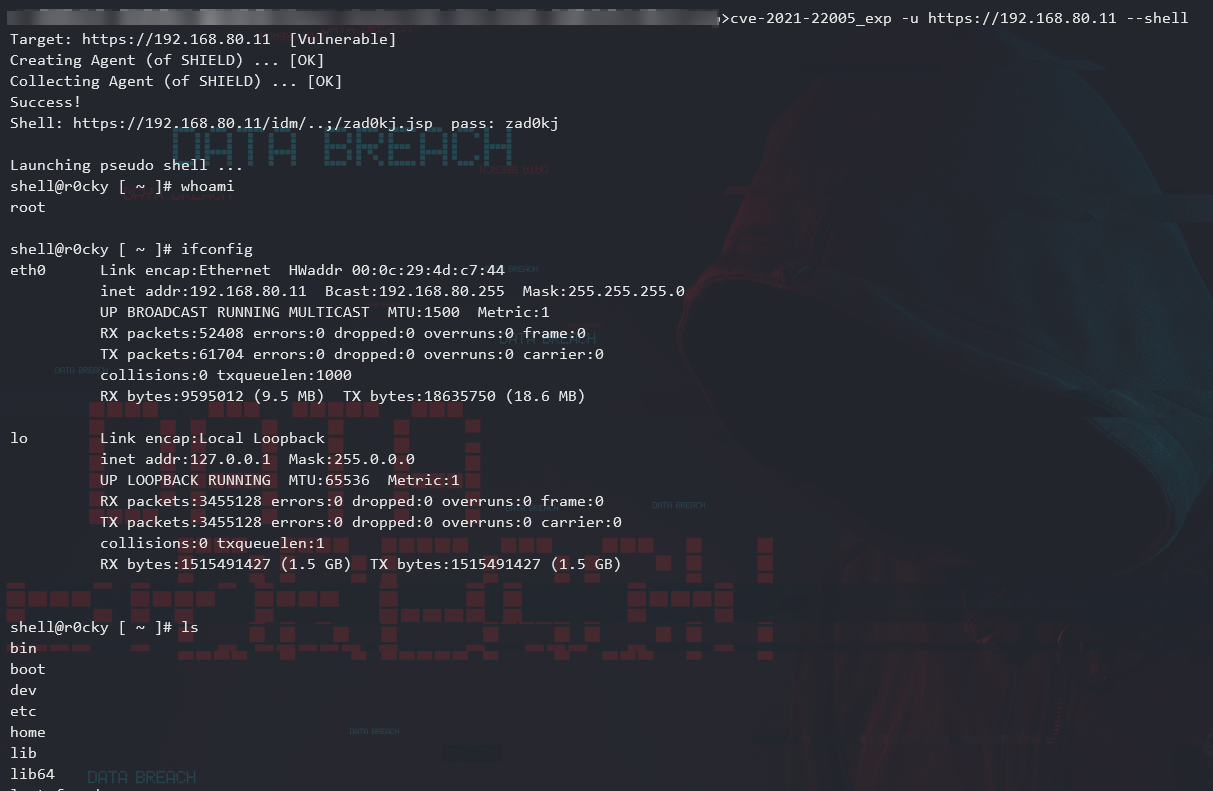 crackercat/cve-2021-22006
CVE-2021-22005 - VMWare vCenter Server File Upload to RCE
 momos1337/log4j-rce
Log4j RCE - (CVE-2021-44228)
 jaychouzzk/cve-2019-5475-nexus-repository-manager-
Exploit payload for CVE-2019-5475 in Nexus Repository Manager, enabling remote code execution via crafted Yum capability configuration.
 aslitsecurity/zimbra-cve-2022-30333
Zimbra unrar vulnerability. Now there are already POC available, it is safe to release our POC.
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…








