
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended

 drgreenthumb93/cve-2022-30190-follina
Proof-of-concept exploit for CVE-2022-30190 (Follina MSDT vulnerability). Generates a malicious Word document that executes a remote script via the…
 zombie-kaiser/cve-2024-4367-poc-fixed
PDF.js是由Mozilla维护的基于JavaScript的PDF查看器。此漏洞允许攻击者在打开恶意 PDF 文件后立即执行任意 JavaScript 代码。这会影响所有 Firefox 用户 (<126),因为 Firefox 使用 PDF.js 来显示 PDF 文件,但也严重影响了许多基于…
 learner330/fastjson-cve-2026-16723
Detailed CVE-2026-16723 analysis and exploit kit for Fastjson 1.2.83 RCE, covering vulnerable code paths, malicious JAR/bytecode generation, and a…
 likekabin/cve-2018-0802_cve-2017-11882
Proof-of-concept exploit generator for CVE-2017-11882 and CVE-2018-0802, crafting malicious RTF files to execute arbitrary commands on target systems…
 doudouhala/cve-2017-8464-exp-generator
this tool can generate a exp for cve-2017-8486, it is developed by python
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
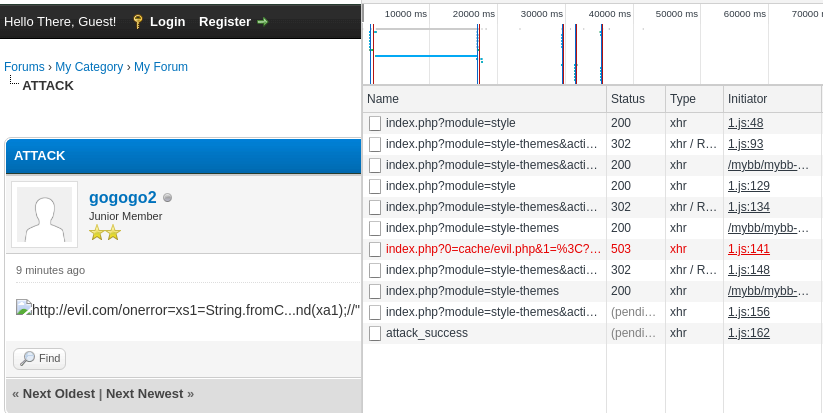 xiaopan233/mybb-xss_sql_rce-poc
Mybb associate CVE-2021-27890 & CVE-2021-27889 to RCE poc
 asaotomo/cve-2021-42013-apache-rce-poc-exp
Apache 远程代码执行 (CVE-2021-42013)批量检测工具:Apache HTTP Server是美国阿帕奇(Apache)基金会的一款开源网页服务器。该服务器具有快速、可靠且可通过简单的API进行扩充的特点,发现 Apache HTTP Server 2.4.50 中针对…
 kirinse/cve-2023-42115
Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.
 jas502n/drivelife-pstrojan
TrojanDropper/PS.Maloader.d
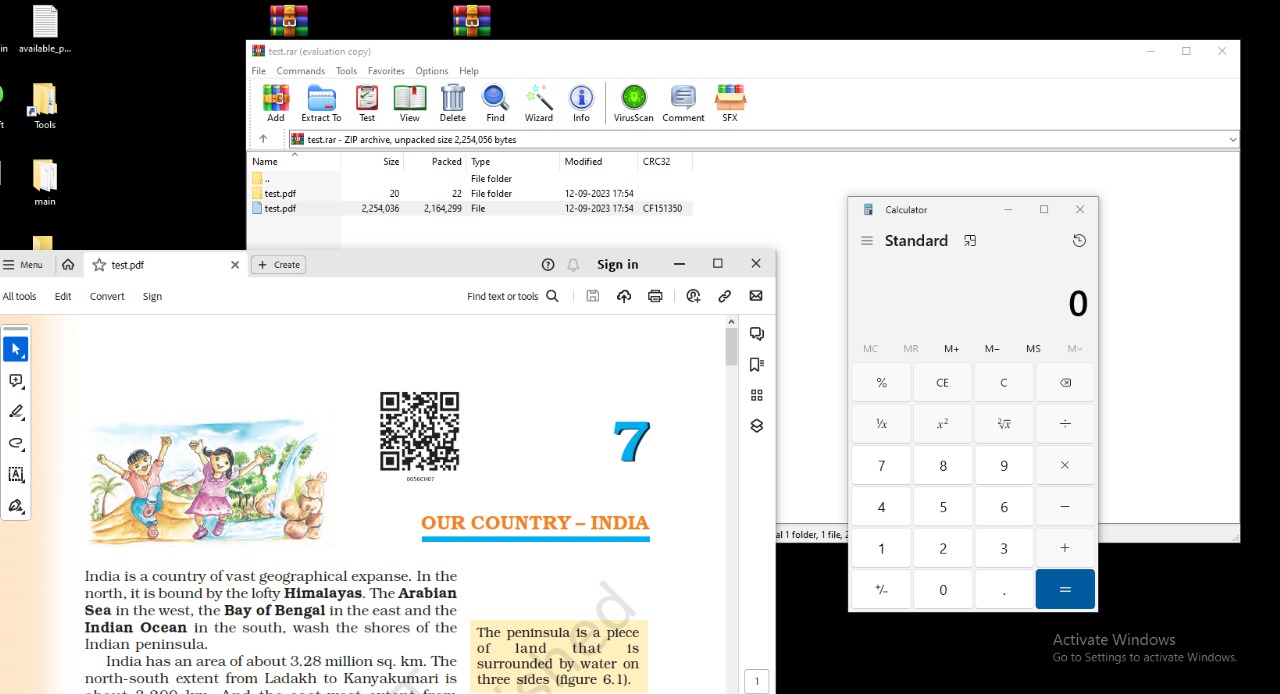 malwareman007/cve-2023-38831
CVE-2023-38831 WinRaR Exploit Generator
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 dr-iman/cve-2018-7600-drupal-0day-rce
Perl-based remote code execution exploit targeting CVE-2018-7600 in Drupal CMS, enabling payload upload and server compromise.
 marcourbano/cve-2021-44228
PoC for CVE-2021-44228.
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
 hydragyrum/evil-rmi-server
An evil RMI server that can launch an arbitrary command. May be useful for CVE-2021-44228
 0x7n6/cve-2022-24500
Standalone exploit for CVE-2022-24500 targeting Windows SMB, generating and executing shellcode to deliver a reverse Meterpreter payload.
 lighird/cve-2018-2628
CVE-2018-2628漏洞工具包








