
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 vysecurity/cve-2017-8759
CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
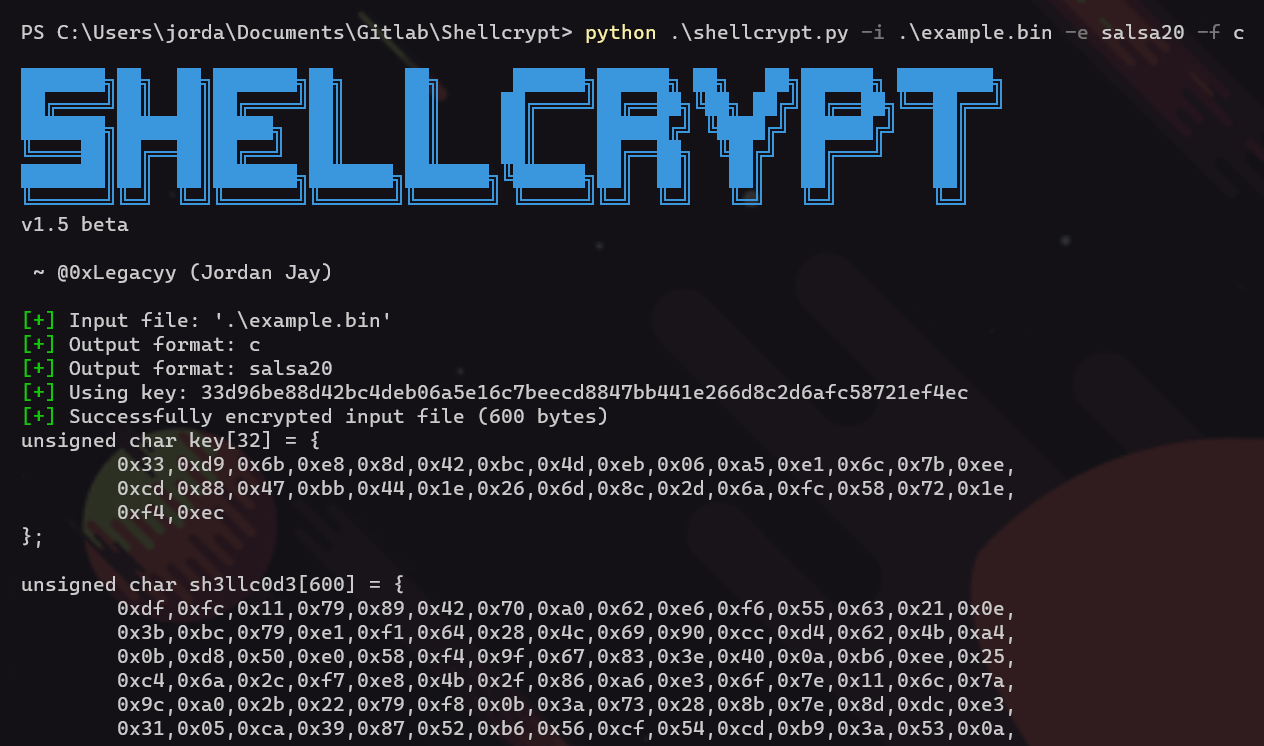 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 lloydlabs/wsb-detect
wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")
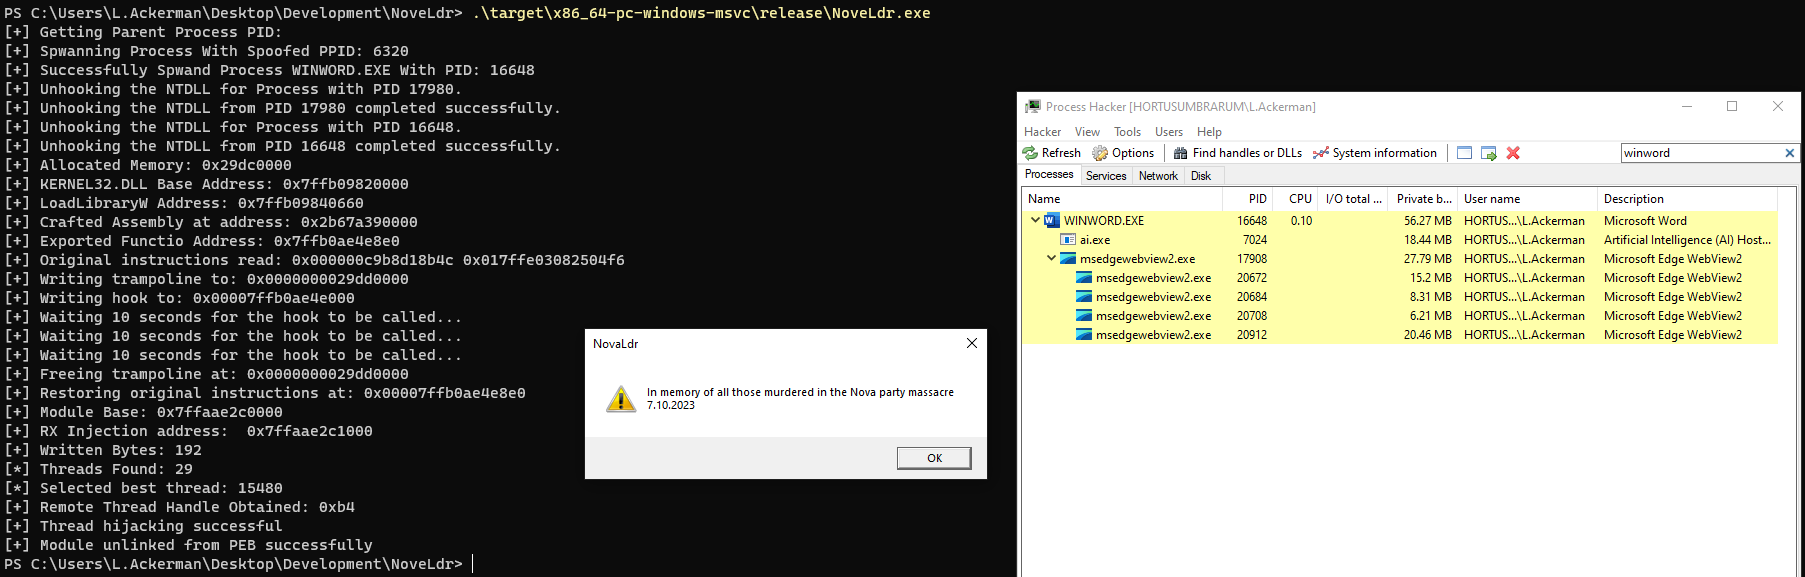 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
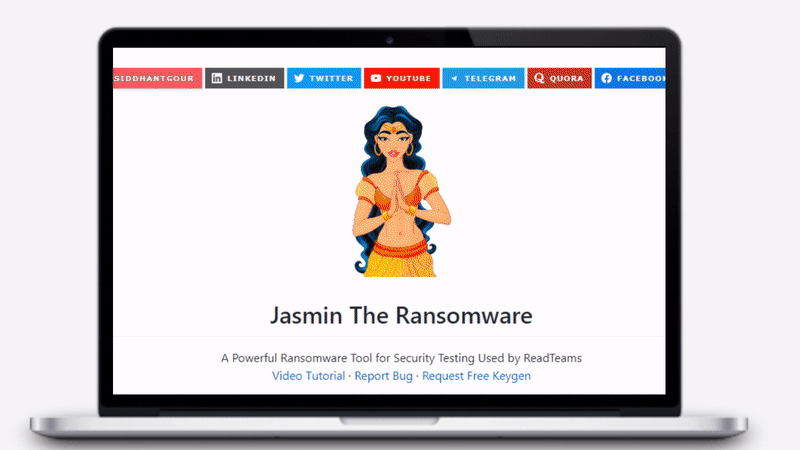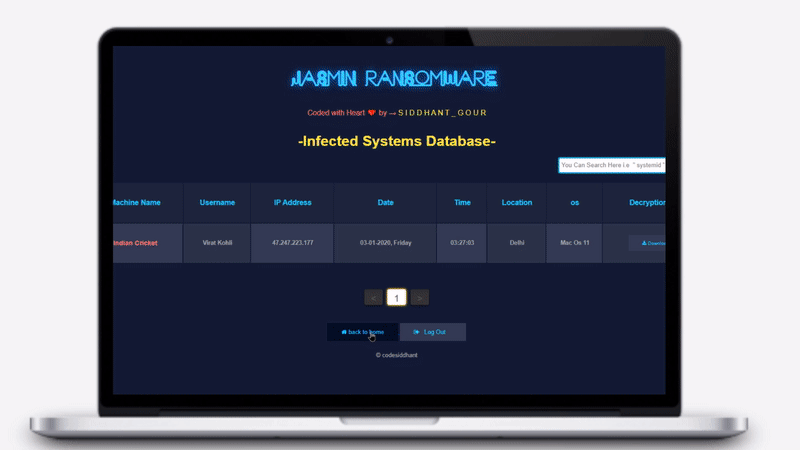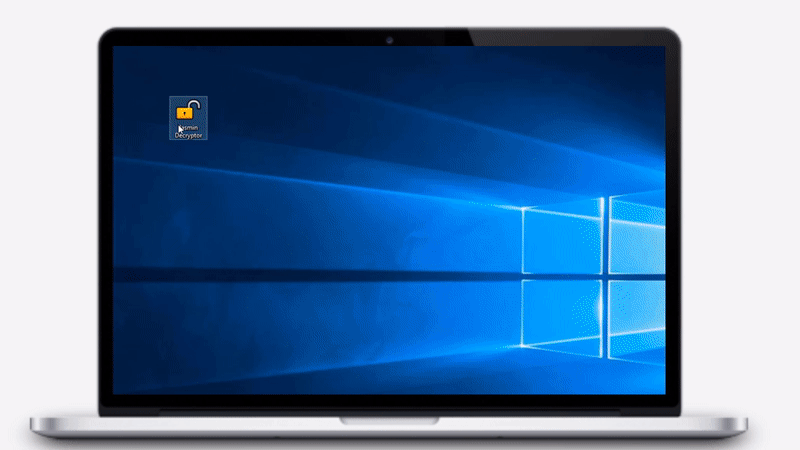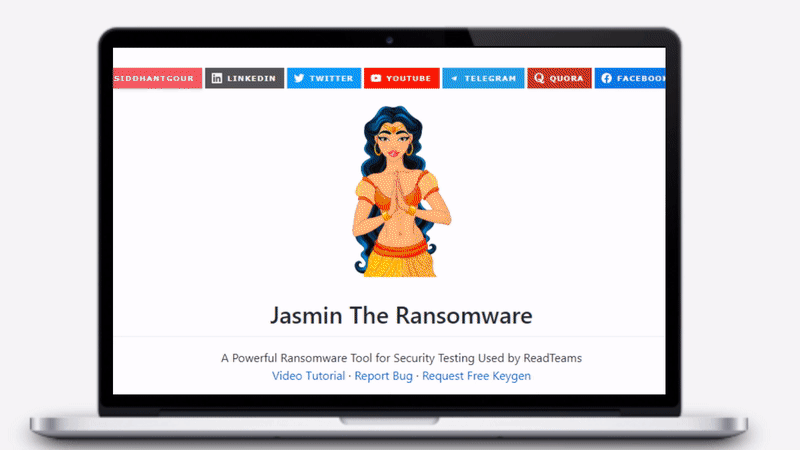 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 kozmic/laravel-poc-cve-2018-15133
PoC for CVE-2018-15133 (Laravel unserialize vulnerability)
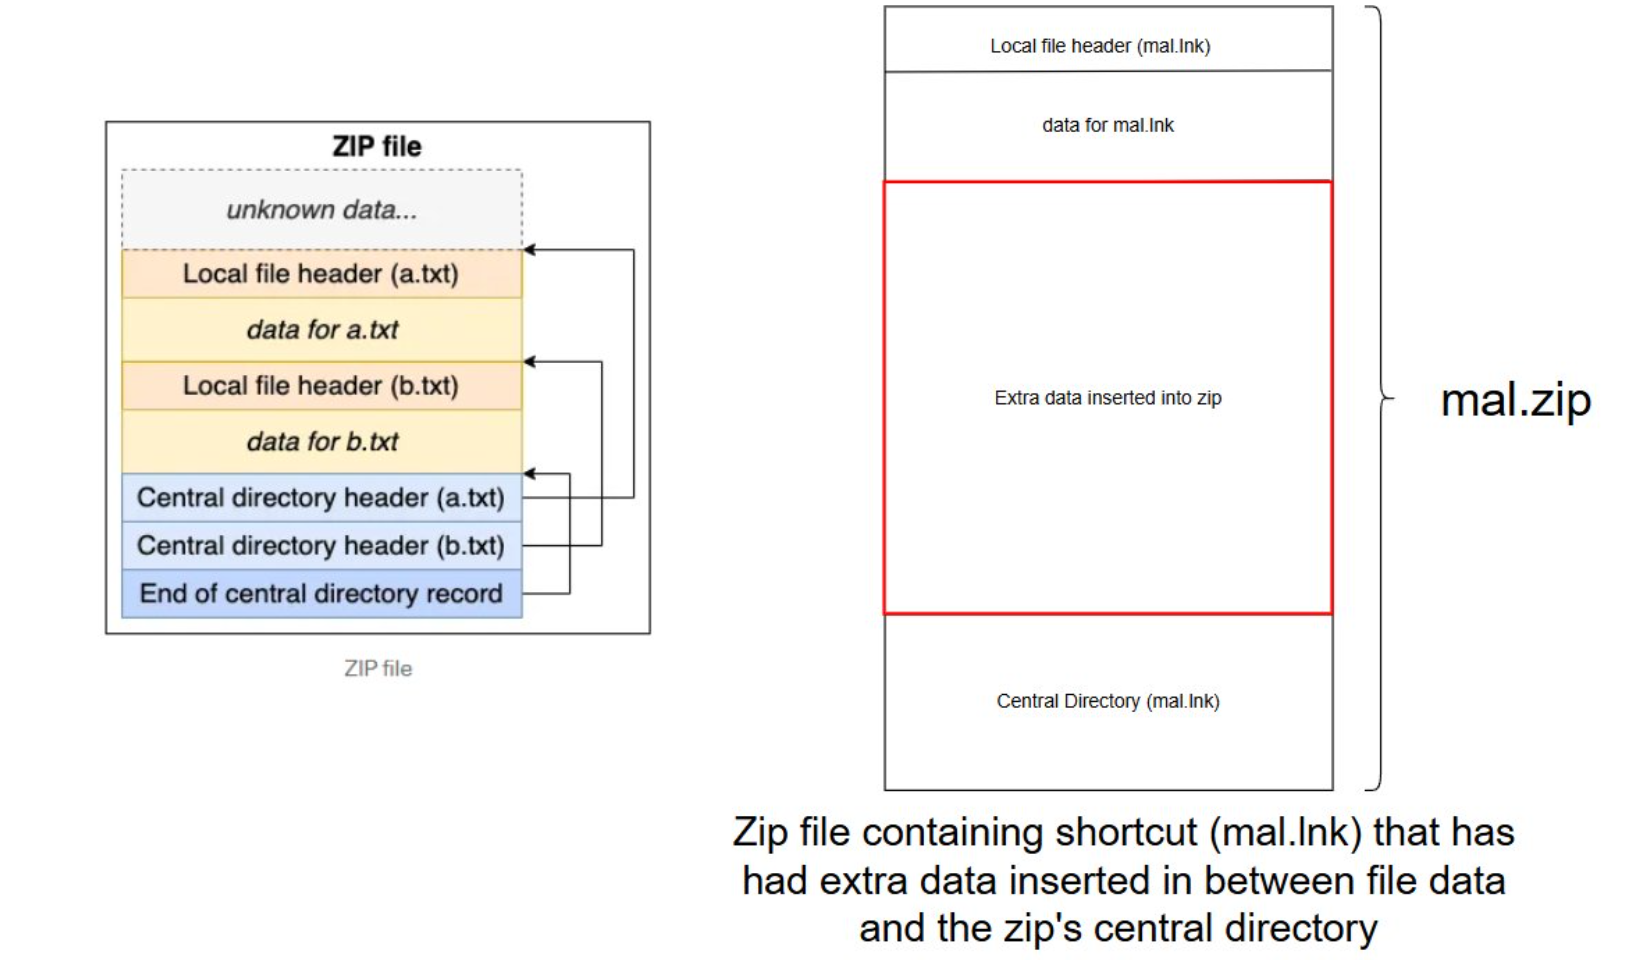 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 kudaes/split
Apply a divide and conquer approach to bypass EDRs








