
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 0xmrma/cve-2026-33146
A public share looked clean in the page tree, but the search endpoint told a different story. In Docmost, restricted child pages hidden from public…
 hohn/codeql-sample-polkit
All stages of exploring the polkit CVE-2021-4034 using codeql
 firstlax6t/cve-2026-36669-fengoffice
Detailed security advisory for CVE-2026-36669: unauthenticated arbitrary file upload in Feng Office, enabling stored XSS and session hijacking.…
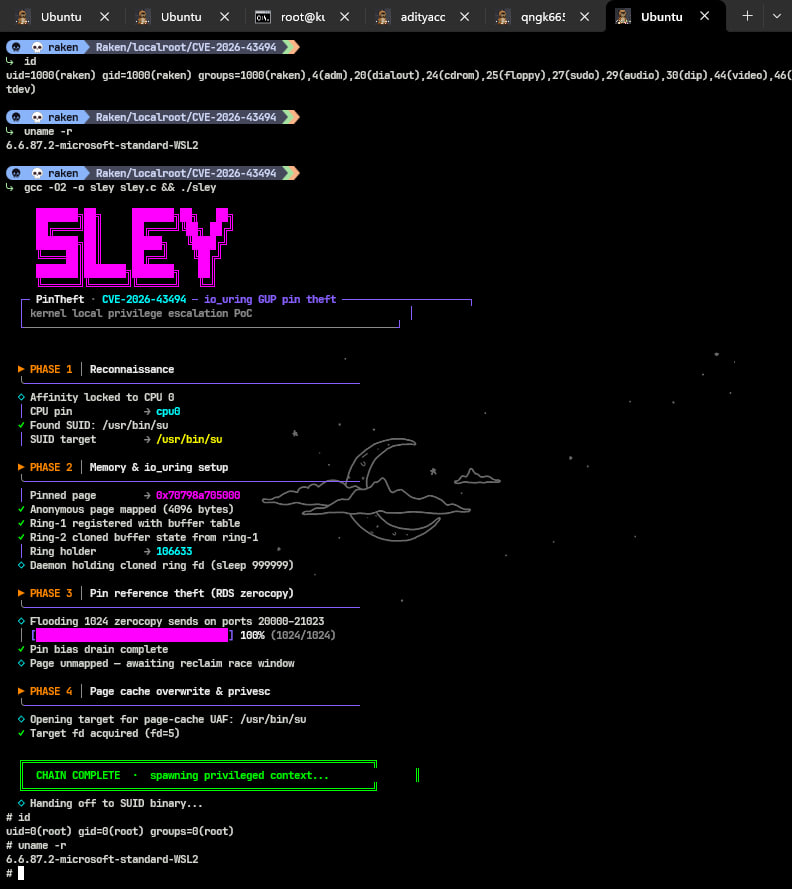 tanzz1337/cve-2026-43494-pintheft-poc
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux LPE via RDS zerocopy refcount bug + io_uring fixed buffers → SUID page-cache overwrite.…
 kryptoenix/cve-2025-47987_poc
Proof-of-concept exploit for CVE-2025-47987 with technical analysis and binary exploitation techniques for vulnerability verification and security…
 zvckster/cve-2025-63353
Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…
 zzzm0919/cve-2026-44648
Proof-of-concept exploit and advisory for CVE-2026-44648, demonstrating the vulnerability and providing technical details for assessment.
 mgtx2/cve-2026-39107
Detailed disclosure of a stored XSS vulnerability in Kimi AI v1.0's Preview tab, including attack scenario, PoC, and remediation guidance for…
 mrk336/cve-2024-3094
CVE-2024-3094 exposed a backdoor in the XZ compression library, allowing remote SSH access by bypassing authentication. It’s a major supply chain…
 dharmstm/cve-2026-30503-openkm-6.3.12-stored-xss
Detailed disclosure of CVE-2026-30503, a stored XSS vulnerability in OpenKM v6.3.12. Includes root cause analysis, PoC payloads, impact assessment,…
 anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…
 hawkeye-bd/cve-2025-43537
Cybersecurity Researcher | Apple Security Credit (CVE-2025-43537) | Vulnerability Research & Responsible Disclosure
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
 ktauchathuranga/cve-2025-70994
Passive RF signal analyzer for EV1527 fixed-code protocol, demonstrating CVE-2025-70994 replay vulnerability in Yadea T5 keyless entry systems.…
 john-jung/cve-2026-26903-poc
A PoC for demonstrating CVE-2026-26903
 ghostn4444/poc-cve-2025-6554
Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…
 h4zaz/cve-2025-60503
XSS vulnerability on ultimatefosters
 oscerd/cve-2026-40858
Reproducer for CVE-2026-40858 — Apache Camel camel-infinispan remote aggregation repository unsafe deserialization (RCE)








