
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 luisbuilds-data/cve-2024-1086-writeup
Root cause analysis and proof-of-concept exploit for CVE-2024-1086, a Linux kernel netfilter double-free vulnerability exploitable via heap spray for…
 born0monday/teamspeak3-vulnerabilities
Proof-of-concept exploits for CVE-2026-4390, CVE-2026-4391 and CVE-2026-4392 in TeamSpeak 3 server (3.13.7).
 tfawnies/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with tested versions and a technical…
 hunt-benito/zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri
Proof-of-concept exploit for CVE-2026-10672, an out-of-bounds read in Zephyr RTOS LwM2M firmware-update pull client. Includes standalone C…
 seqra/cve-2026-58138
Reproduction kit for CVE-2026-58138, an unauthenticated RCE in Conductor. Includes OpenTaint static analysis rules, isolated tests, SARIF results,…
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 0xmrma/cve-2026-34207
The SSRF filter checked hostname text, but the actual destination was decided later by DNS. That gap let attacker-controlled Webhook URLs reach…
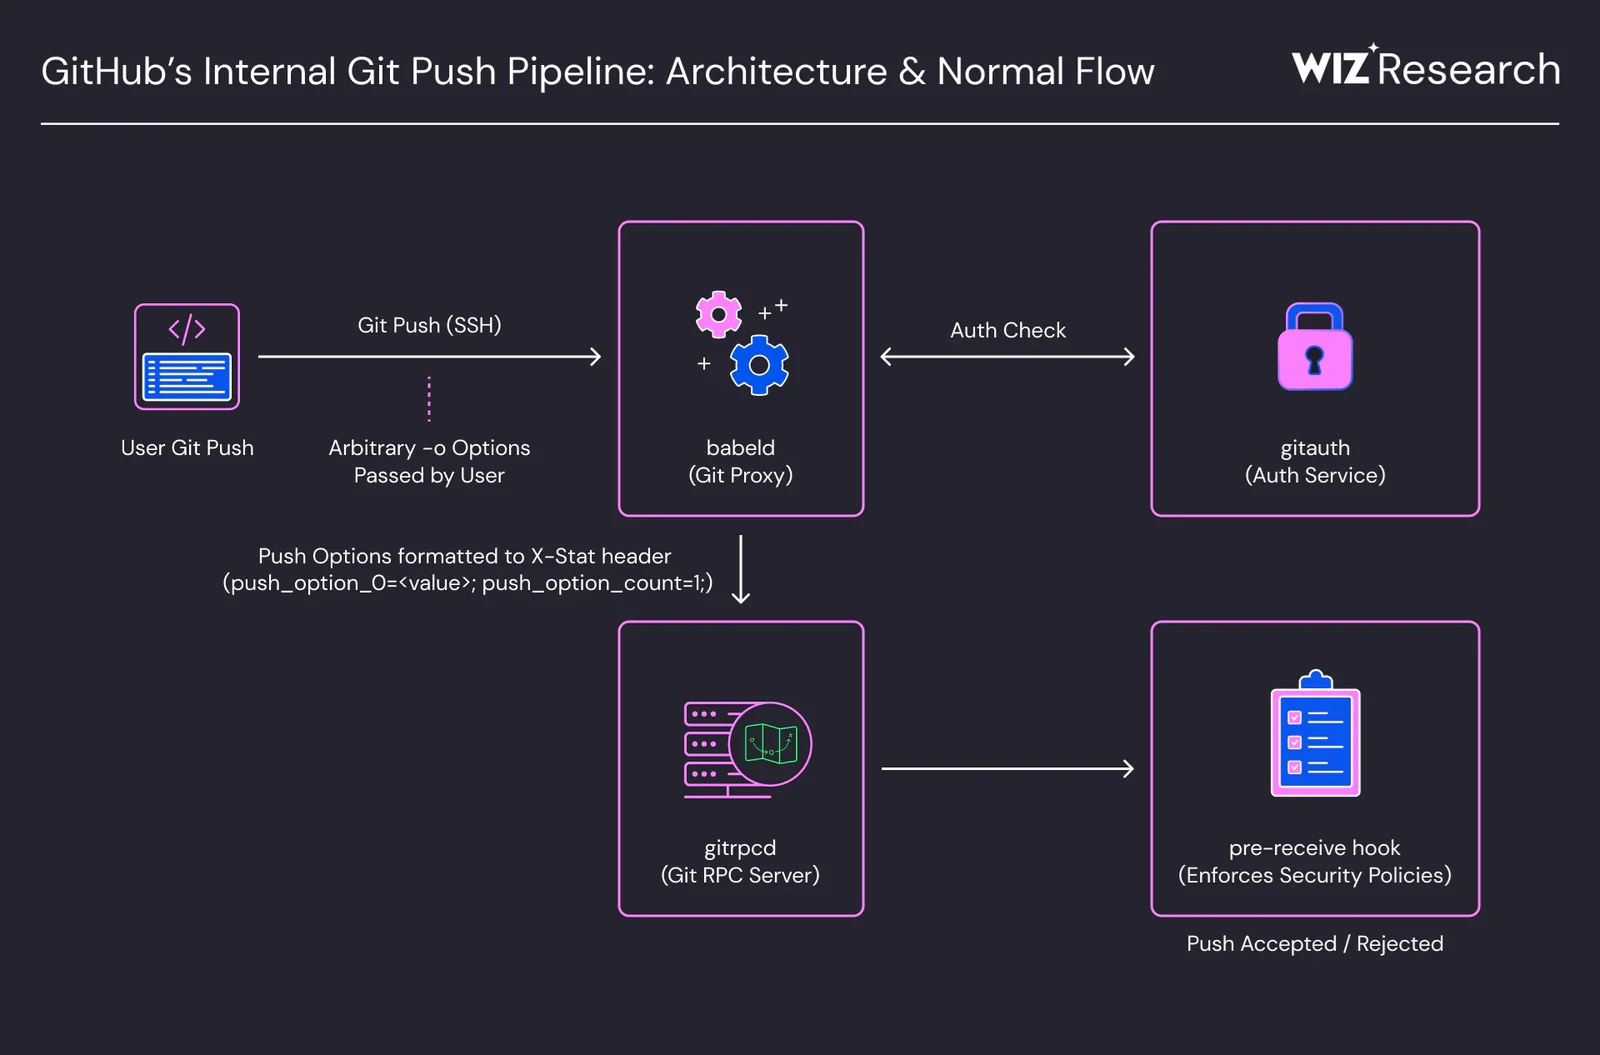 5kr1pt/cve-2026-3854
Technical breakdown of CVE-2026-3854, a GitHub RCE via header injection in git push, explaining the vulnerability, exploitation technique, and…
 rivaedoardo62-boop/cve-2024-23897-jenkins-poc
Self-contained Docker reproduction and analysis of CVE-2024-23897, the Jenkins CLI arbitrary file read via the args4j @-syntax argument expansion.
 kaleth4/cve-2026-55200
Technical analysis and proof-of-concept for CVE-2026-55200, a critical heap-based buffer overflow in libssh2 allowing pre-authentication RCE.…
 0xmrma/cve-2026-45806
Penpot's remote image import let an authenticated file editor turn a normal media convenience feature into backend-origin SSRF because…
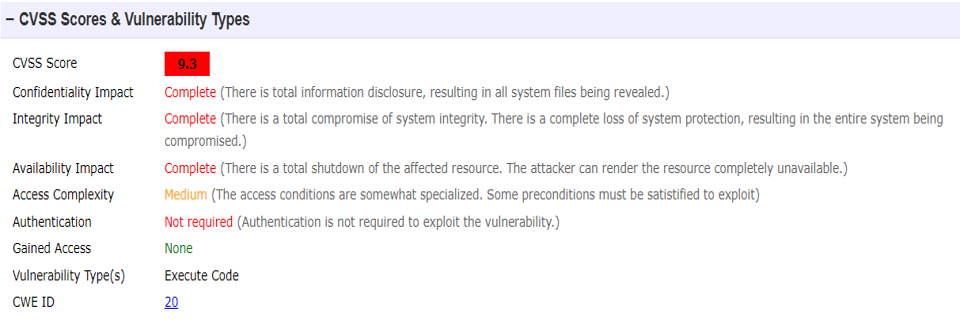 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
 muslimbek-0x/cve-2026-48030
Proof-of-concept exploit for CVE-2026-48030, a critical OS command injection in Pheditor 2.0.1-2.0.3. Includes vulnerable code analysis, PoC script,…
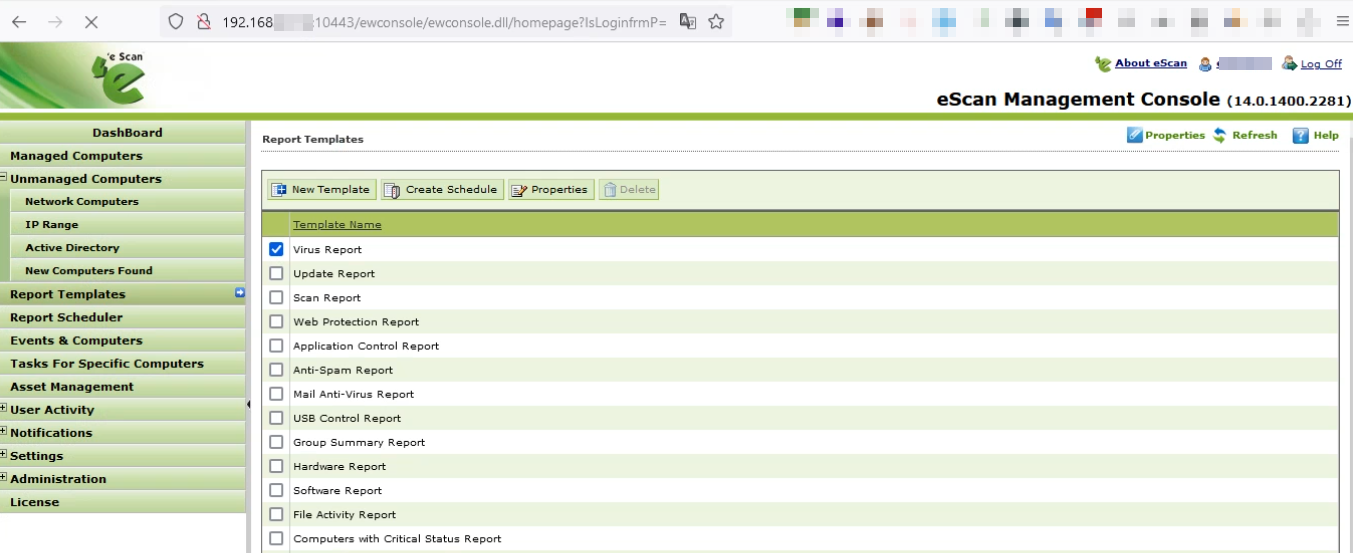 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
 mmionf/copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with a technical writeup and tested…
 mohabars/cve-2026-21986-virtualbox-dos
CVE-2026-21986: VirtualBox Shared Folders kernel memory exhaustion DoS
 0xmrma/cve-2026-34212
Docmost accepted a javascript: URL inside an attachment node, preserved it through storage and rendering, and turned it back into a clickable anchor…








