
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 clogan9019-dotcom/iohidfamily-poc-research
CVE-2026-28992 IOHIDFamily FastPathUserClient race condition PoC — security research
 kpatsakis/cve-2026-36834
Reproducible CVE-2026-36834 proof-of-concept demonstrating an out-of-bounds array read in LibRaw's Panasonic RW2 decoder, with mutation script and…
 grayxploit/cve-2026-48907
Proof-of-concept exploit and technical analysis for CVE-2026-48907, a CVSS 10.0 pre-authentication remote code execution vulnerability in the Joomla…
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 songg45/cve-2023-4683-test
CVE-2023-4683 - Test
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 shreyas-challa/cve-2026-46394-haxcms-git-command-injection
PoC and writeup for CVE-2026-46394: OS command injection in HAXcms Git.php (CWE-78). Authorized security research only.
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 0xmrma/cve-2026-34213
A low-privileged Docmost user could supply a victim attachmentId to the generic upload endpoint and overwrite another page's stored attachment inside…
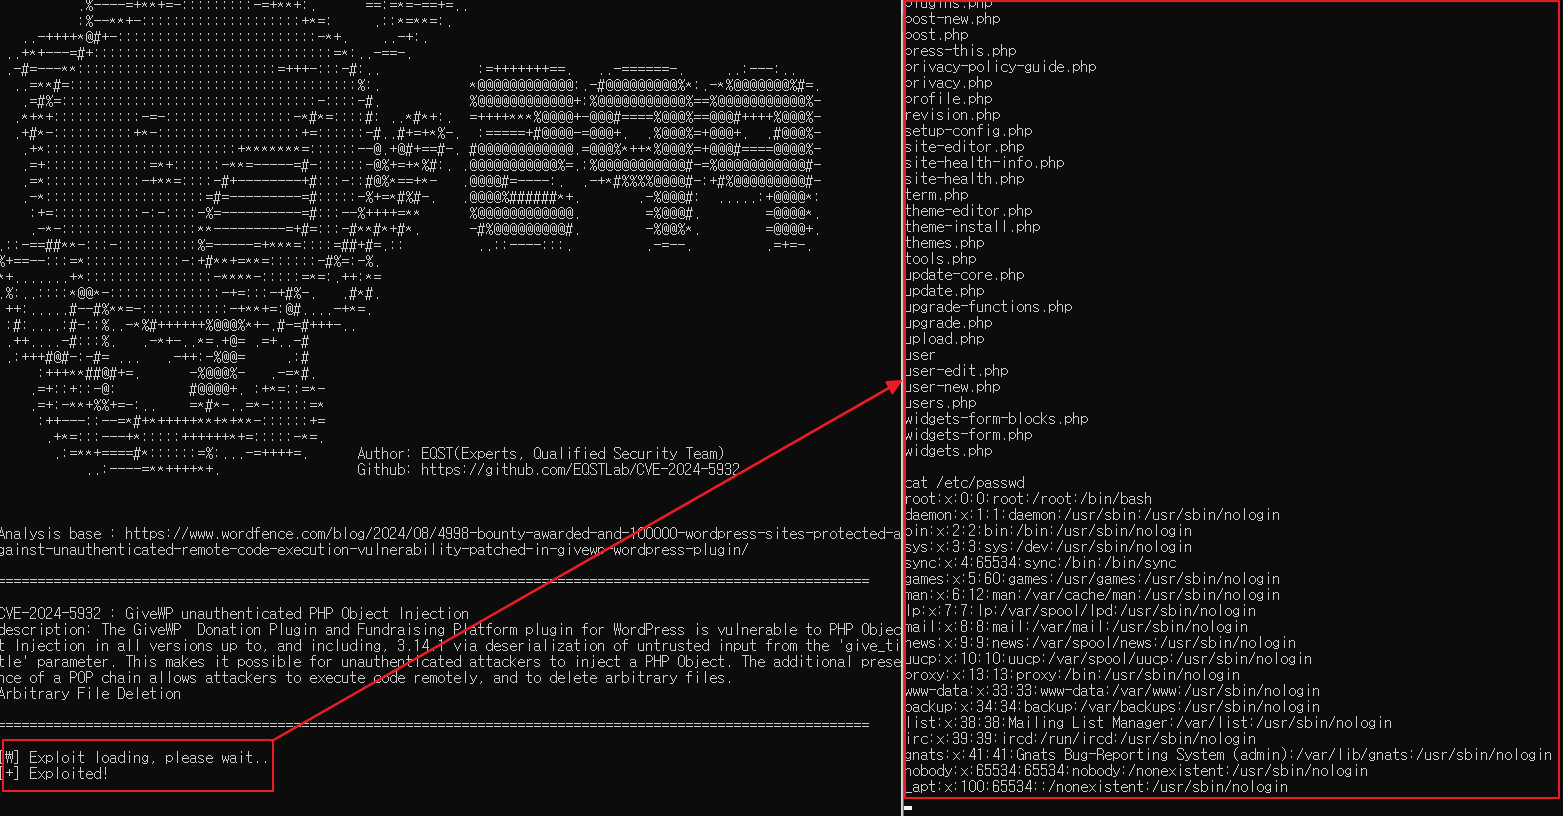 nishant-kumar-5173/cve-2024-5932
Proof-of-concept exploit for CVE-2024-5932, a PHP object injection vulnerability in the GiveWP WordPress plugin, enabling unauthenticated remote code…
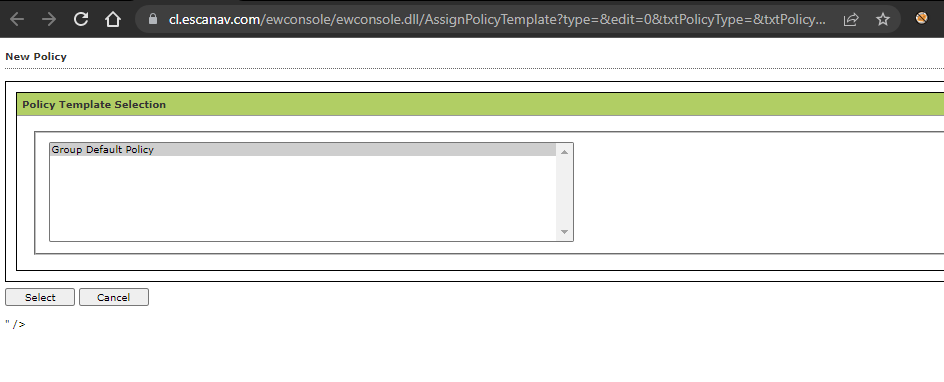 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 joakimbulow/cve-2026-48962
CVE-2026-48962 - IO::Compress - Code Execution
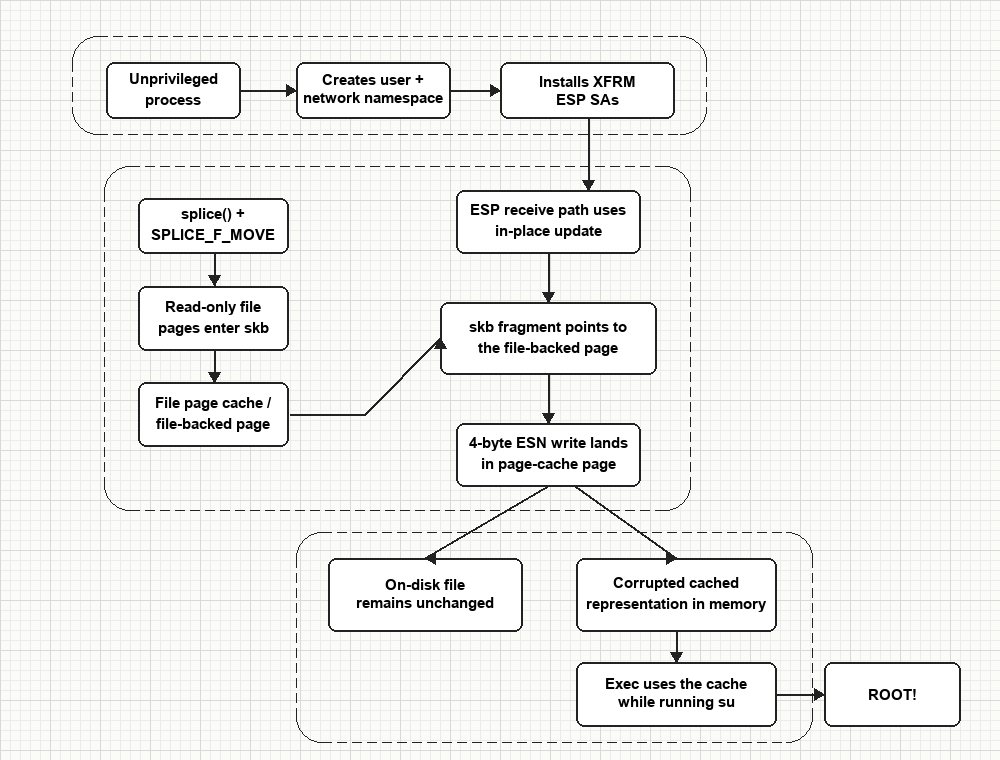 chernstepanov/dirtyfrag-for-dummies
Technical analysis and cleaned-up PoC for CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm-ESP vulnerability enabling page cache corruption via…
 syntaxsaiyan/cve-2026-36851
Walkthrough and PoC of File path traversal vulnerability(CVE-2026-36851) for UnPoller 2.33.0
 0xmrma/cve-2026-46558
Plane’s V2 asset subsystem trusted workspace slugs and asset UUIDs without enforcing the right membership checks, which let one authenticated user…
 mein-0/cve-2025-7771
Proof-of-concept exploit for CVE-2025-7771, a Windows kernel driver vulnerability in ThrottleStop.sys enabling arbitrary physical memory read/write…








