
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 jamezx32/cve-2026-85046
V8 inlined Array.prototype.sort elements-kind confusion - PoC + addrof (N-day research)
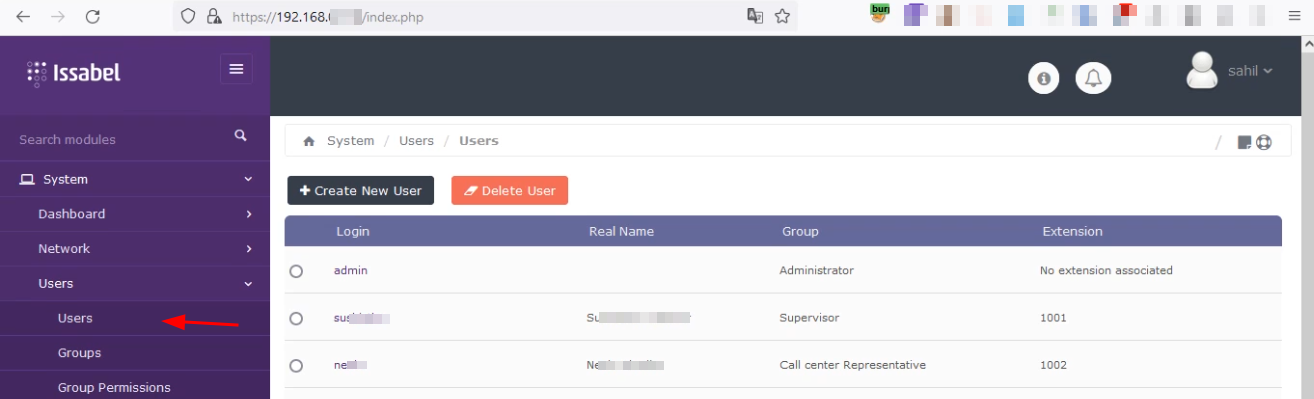 sahiloj/cve-2023-34839
CVE-2023-34839 is a Cross-Site Request Forgery (CSRF) vulnerability discovered in Issabel PBX version 4.0.0-6, a widely used open-source Unified…
 abraxas/pfsense-limiter-aqm
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - limiter AQM newline
 abraxas/sqlite-fts5-securedel
SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
 danielw98/zero-click-exploit-analysis
CVE-2025-55177 + CVE-2025-43300: reverse-engineering the WhatsApp-ImageIO zero-click iOS chain, with interactive labs.
 undacmic/heartbleed-proof-of-concept
Proof of concept for exploiting the Heartbeat Extension bug detailed in the CVE-2014-0160. :old_key: :unlock:
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 abraxas/pfsense-dyndns-cache-path
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - File write - DynDNS cache path
 horkimhab/cve-2026-59265
Proof-of-concept and research material for CVE-2026-59265, a LibreOffice and OpenOffice vulnerability, intended for authorized lab testing and…
 ammarkrblt/cve-2026-78818-cyberpanel-phpselection-rce
CVE-2026-78818 - CyberPanel <= 2.4.7 authenticated root RCE via phpSelection command injection + cloudAPI WAF bypass
 malhyuk/cve-2026-98180
Proof-of-concept and KASAN-confirmed KUnit reproducer for CVE-2026-98180, a drm/msm use-after-free of scheduler-containing ring and VM objects…
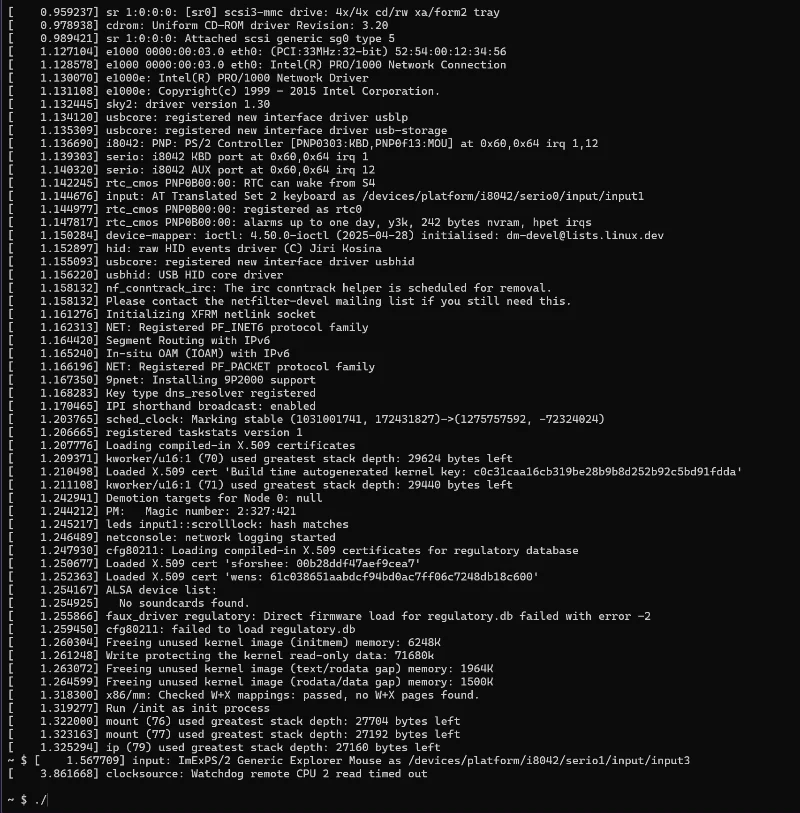 imkidz0/poc-cve-2026-98258
Proof-of-concept demonstrating CVE-2026-98258, a Linux kernel posix-cpu-timers flaw where a queued timer is freed on the expiry list, with a working…
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 abraxas/proftpd-site-copy-dest-follow
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SITE COPY dest follows symlink
 abraxas/proftpd-sftp-copy-file-write
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SFTP copy-file skips dest WRITE
 bombobombone/cve-2026-103585
Sanitized report and loopback-only PoC script demonstrating stored XSS via javascript: license URLs in MediaSearch QuickView (CVE-2026-103585).
 abraxas/pfsense-uploadconfig
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - hidden uploadconfig








