
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
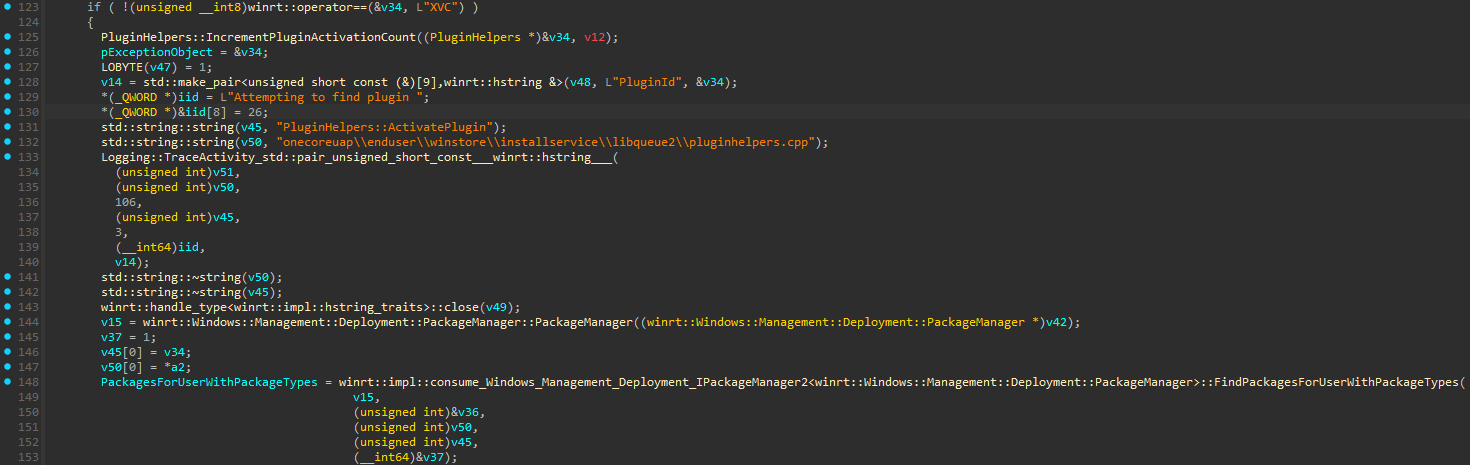
 karollooool/cve-2026-119987-writeup
CVE-2026-119987: Windows App Store Elevation of Privilege
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 peach-research-lab/authorizationbench
[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team
 n0kovo/awesome-password-cracking
A curated list of awesome tools, research, papers and other projects related to password cracking and password security.
 zeetee1235/cve-2026-126497
Proof-of-concept and analysis for CVE-2026-126497, a heap out-of-bounds write in LibreCAD/libdxfrw R2004 DWG section-page parsing, with ASan…
 akil-x/r00tlib-catalog
A community-curated knowledge hub and catalog for computer science, cybersecurity & software engineering books
 rudsarkar/ghsa-673q-mjm6-r5xr
Dockerized proof-of-concept for GHSA-673q-mjm6-r5xr: a single unauthenticated request achieves RCE in Next.js use cache / React Flight, with a…
 owasp/mosaic
Coordination structure for AI security standards and guidelines, reducing fragmentation and providing clear guidance for securing AI systems across…
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 xca-attacks/mior
Proof-of-concept kernel patch and research artifacts for MIOR, a data fabric rerouting attack exploiting an uninitialized Reverse Map Table…
 agnuxo1/openclaw-p2p
Decentralized Autonomous Research Collective. Lean 4-verified, IPFS-backed, agent-native. Production paper: arXiv:2604.19792. Live at p2pclaw.com.
 douglasmun/cve-2026-123158_sshole_lab
Secure-coding laboratory: Docker reproduction of CVE-2026-123158 (sshole) — OpenSSH password-auth bypass on musl/no-PAM, why the default is safe, and…
 slowmist/knowledge-base
Curated knowledge base of blockchain security research, audit reports, guides, and translations covering smart contracts, cryptography, and AI…
 suruurism/cve-writeups-and-pocs
CVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
 risc0/zirgen
Domain-specific language compiler for creating arithmetic circuits targeting the RISC Zero zero-knowledge proof system, enabling custom accelerators…
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 michalbednarski/thelastbundlemismatch
Writeup and exploit for CVE-2023-45777, bypass for Intent validation inside AccountManagerService on Android 13 despite "Lazy Bundle" mitigation








