
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 lirantal/cve-2024-21532-poc-ggit
Proof-of-concept exploit for CVE-2024-21532, a command injection vulnerability in the ggit npm package's fetchTags API, demonstrating unsafe exec()…
 shokribardiya/cve-2025-14847-mongobleed
CVE-2025-14847 mongobleed python file
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 0xblackash/cve-2026-45447
CVE-2026-45447
 danielossai12/aisecplus-week01-danielossai
AISec Plus Week 1 threat write-up — EchoLeak (CVE-2025-32711), zero-click indirect prompt injection in Microsoft 365 Copilot.
 minc-nice-100/http2-bomb-analysis-paper
HTTP/2 Bomb: HPACK indexed-reference amplification + flow-control stall. A high school student's full protocol analysis (LaTeX). CVE-2026-49975,…
 pavanvootla-sec/cve-2026-37196
Stored XSS vulnerability disclosure for nirix traq v3.9.0 with PoC, root cause analysis, and mitigation guidance for security researchers and…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 siyuanli00/intact
Research code reproducing multi-turn LLM jailbreak experiments (FITD, MRCJ, ActorAttack, X-Teaming) from the SoK intent-oriented systematization…
 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
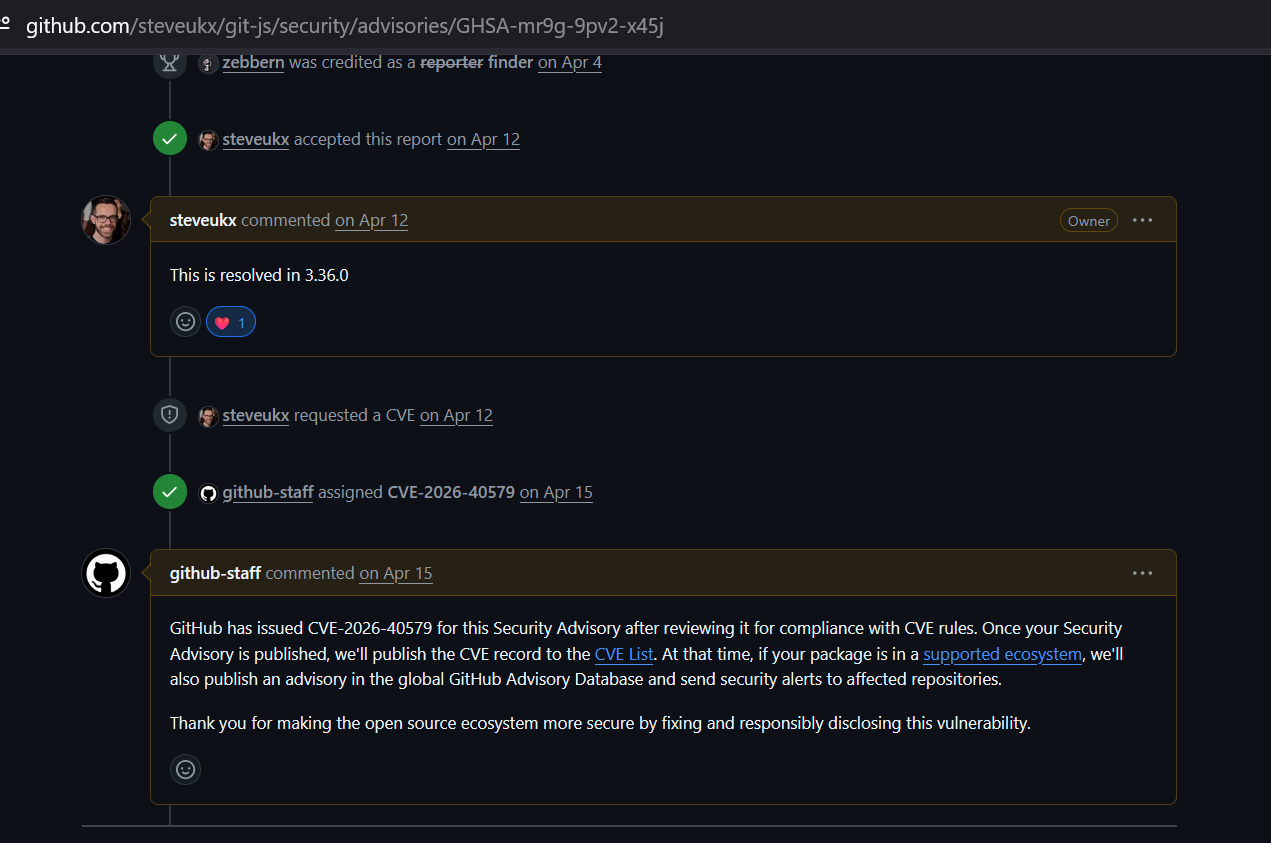 zebberncve/cve-2026-40579
Advisory for git-js ⌯⌲ 11 mill weekly downloads
 ad3210/cve-2024-2887-report
POC available soon
 wsu-cyber-security-lab-ai/clipguard
Adversarial image perturbation tool that uses SAM segmentation and CLIP models to evade AI-based scam image classifiers for security research.
 murdok1982/exploit-poc-para-cve-2024-30085
Exploit en Python diseñado para aprovechar la vulnerabilidad de elevación de privilegios CVE-2024-30085
 mauricioportela/cve-2026-31431-analysis
Relatório de Análise Técnica: Exploração de Falha de Isolamento no Kernel Linux (CVE-2026-31431)
 nst/spyphone
This project shows the kind of data a rogue iPhone application can collect.
 joakimbulow/cve-2026-48962
CVE-2026-48962 - IO::Compress - Code Execution
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…








