 0xblackash/cve-2026-45447
CVE-2026-45447

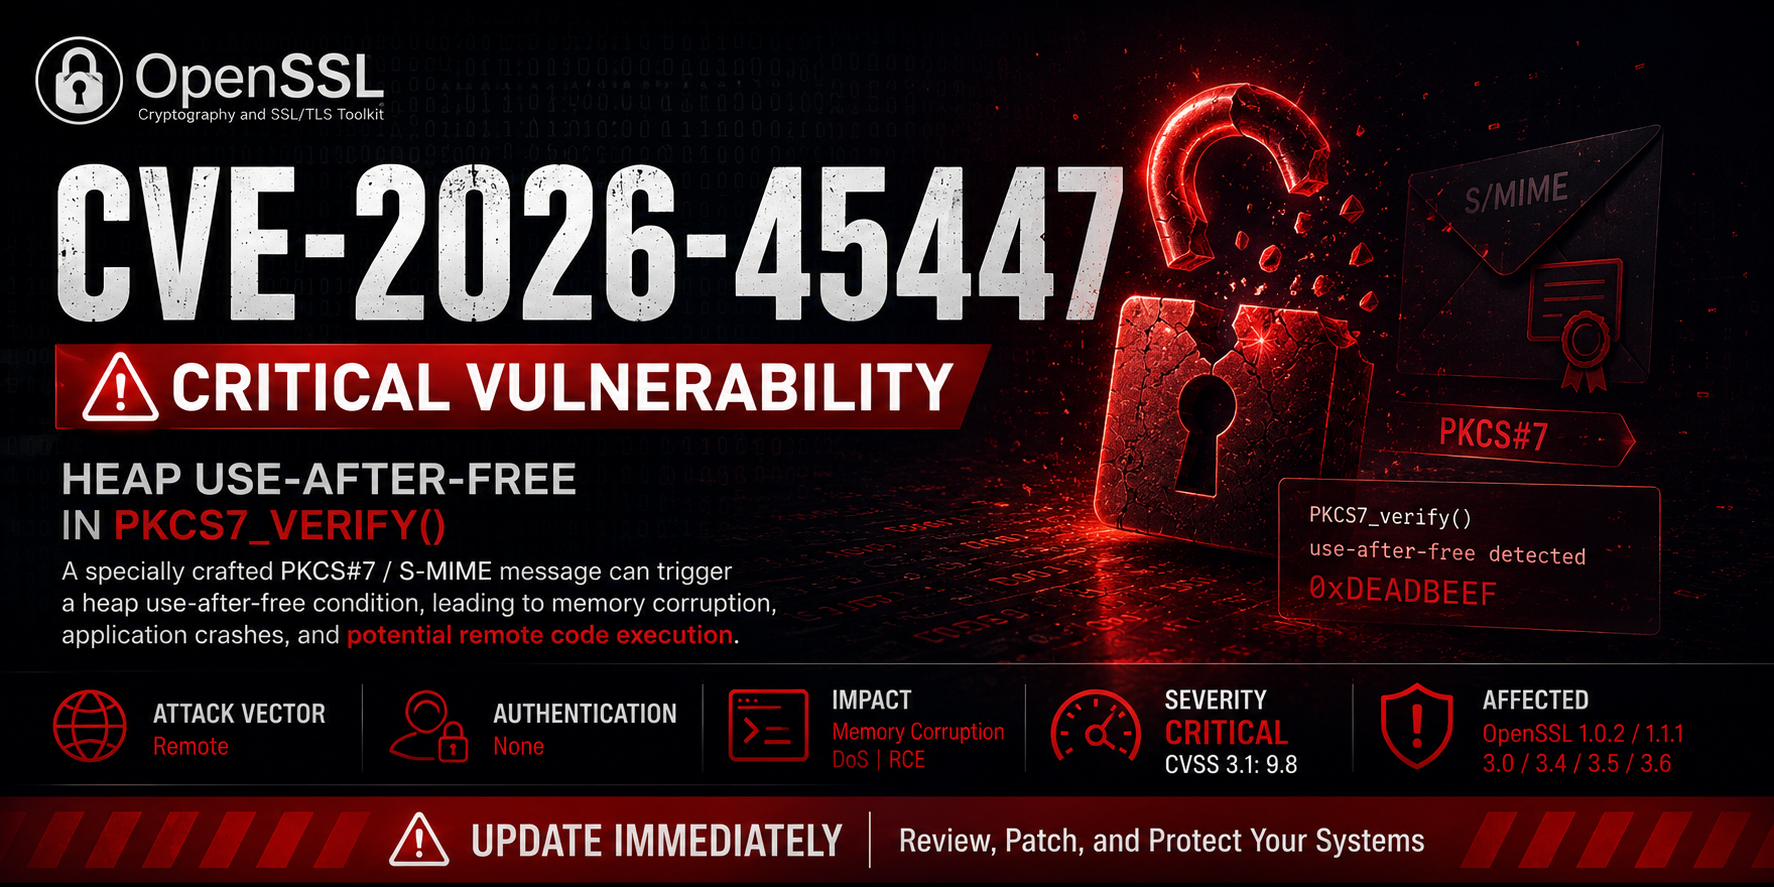

Heap Use-After-Free in PKCS7_verify() allowing memory corruption, crashes, and potential remote code execution.
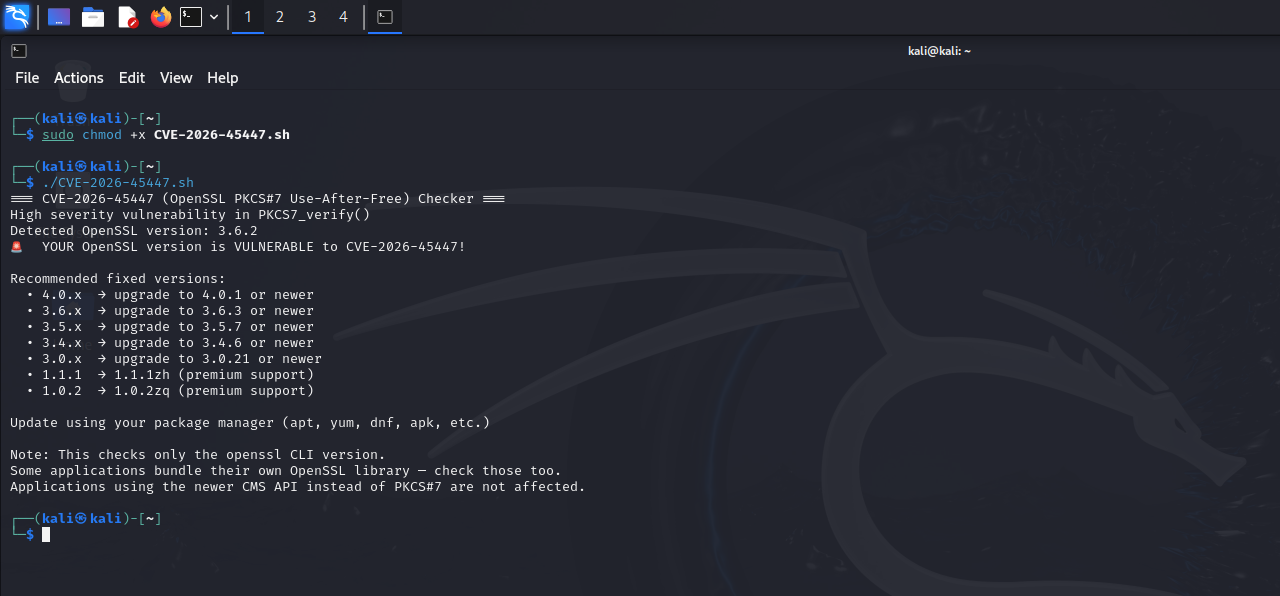
CVE-2026-45447 is a critical vulnerability in OpenSSL's PKCS#7 verification functionality.
The flaw exists within the PKCS7_verify() code path and can be triggered through a specially crafted PKCS#7 or S/MIME signed message containing a malformed ASN.1 structure.
Successful exploitation may result in:
| Property | Value |
|---|---|
| CVE | CVE-2026-45447 |
| Vendor | OpenSSL |
| Severity | Critical |
| CVSS v3.1 | 9.8 |
| CWE | CWE-416 |
| Vulnerability Type | Use-After-Free |
| Attack Vector | Remote |
| User Interaction | Required (message processing) |
| Authentication | None |
| Affected Component | PKCS7_verify() |
A malicious actor can craft a specially formed:
containing an empty ASN.1 SET inside:
SignedData.digestAlgorithms
During verification, OpenSSL incorrectly frees a BIO object while ownership is still assumed by the calling application.
Subsequent access results in a classic:
Heap Use-After-Free
condition.
Attacker
    │
    ▼
Crafted PKCS#7 / S-MIME Message
    │
    ▼
Target Application
    │
    ▼
PKCS7_verify()
    │
    ▼
Unexpected BIO Free
    │
    ▼
Use-After-Free Triggered
    │
    ├── Application Crash
    ├── Memory Corruption
    └── Potential RCE
Potential disclosure of sensitive memory contents.
Heap corruption may allow attacker-controlled memory manipulation.
Application crashes and denial-of-service conditions.
Possible depending on:
- Application architecture
- Heap layout
- Mitigations
- Exploitation primitives
| Branch | Status |
|---|---|
| OpenSSL 1.0.2 | Affected |
| OpenSSL 1.1.1 | Affected |
| OpenSSL 3.0.x | Affected |
| OpenSSL 3.4.x | Affected |
| OpenSSL 3.5.x | Affected |
| OpenSSL 3.6.x | Affected |
Upgrade to vendor-patched releases provided by:
Always verify package versions from your operating system vendor.
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H
| Metric | Value |
|---|---|
| Attack Vector | Network |
| Attack Complexity | Low |
| Privileges Required | None |
| User Interaction | Required |
| Scope | Unchanged |
| Confidentiality | High |
| Integrity | High |
| Availability | High |
Applications using OpenSSL's PKCS#7 verification APIs:
Any software directly invoking:
PKCS7_verify()
Segmentation fault
SIGSEGV
SIGABRT
Double free
Heap corruption
journalctl -xe
dmesg | grep segfault
grep -Ri "openssl" /var/log/
Look for:
PKCS7_verify failed
BIO error
ASN1 parsing failure
SMIME verification failure
Heap corruption detected
1. Create malformed PKCS#7 structure
2. Embed empty ASN.1 SET
3. Deliver to target application
4. Trigger PKCS7_verify()
5. Observe heap corruption
⚠️ This repository intentionally excludes weaponized exploit code.
OpenSSL is one of the most widely deployed cryptographic libraries worldwide.
A vulnerability affecting signature validation routines may impact:
CVE-2026-45447/
│
├── README.md
│
├── assets/
│   ├── CVE-2026-45447.png
│   └── screenshots/
│
├── advisory/
│   ├── technical-analysis.md
│   ├── timeline.md
│   └── impact-assessment.md
│
├── detection/
│   ├── sigma/
│   ├── yara/
│   └── hunting-guide.md
│
├── iocs/
│   └── indicators.md
│
└── references/
    └── links.md
This repository is intended exclusively for:
The information contained herein must be used only in authorized environments and in accordance with applicable laws and regulations.
OpenSSL • Use-After-Free • Critical Severity