
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 rimbadirgantara/opac-fast-automation
automation untuk CVE-2025-65862
 sagittarius-a/cve-2022-21658
POC for cve-2022-21658
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 rkrakesh524/oob_entry
oob_entry tfp0 kernel exploit for armv7 iOS (iOS 3.0–10.3.4), using CVE-2023-32434. We will publish a write-up detailing the methods in the coming…
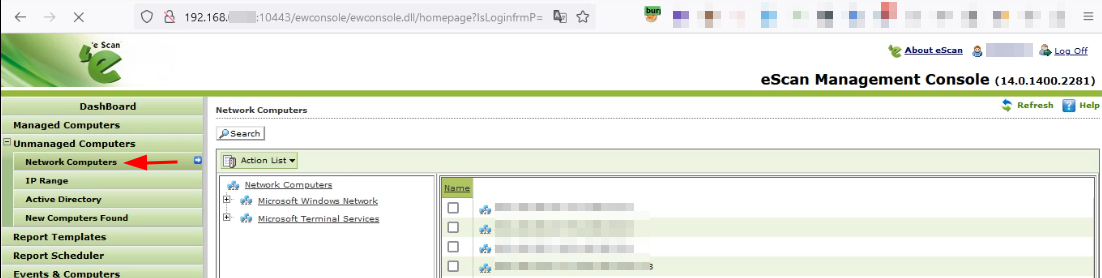 sahiloj/cve-2023-34837
CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
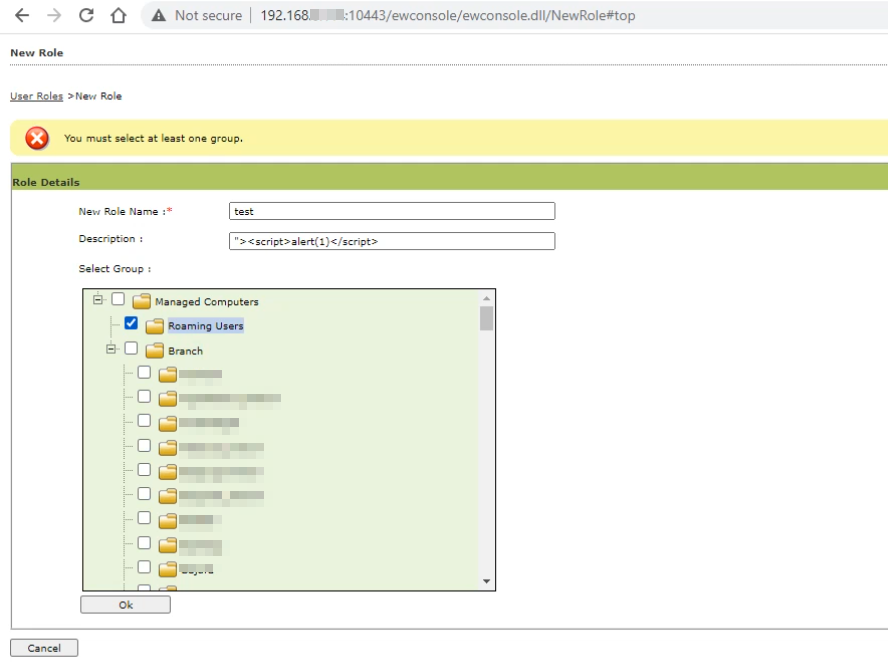 sahiloj/cve-2023-34838
Microworld Technologies eScan Management Console version 14.0.1400.2281 is vulnerable to a Stored Cross-Site Scripting (XSS) attack.
 sahiloj/cve-2023-34839
CVE-2023-34839 is a Cross-Site Request Forgery (CSRF) vulnerability discovered in Issabel PBX version 4.0.0-6, a widely used open-source Unified…
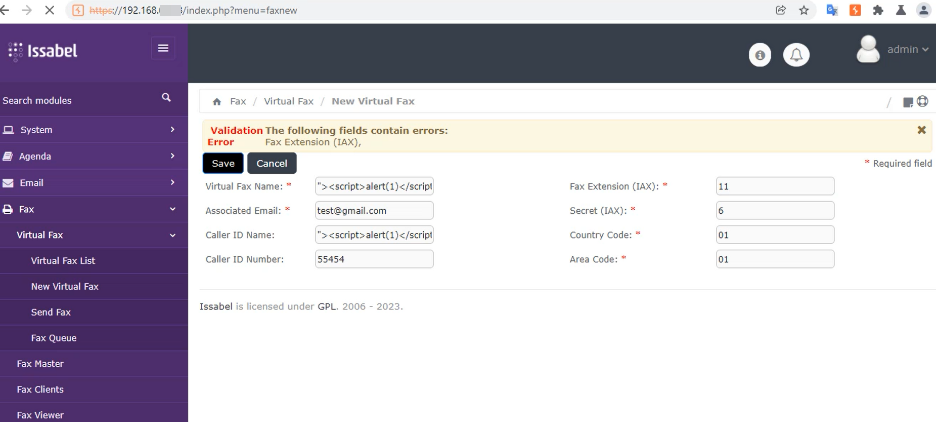 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 xyddnljydd/cve-2020-1066
Exploit code for CVE-2020-1066 with accompanying blog analysis, demonstrating a specific Windows privilege escalation vulnerability.
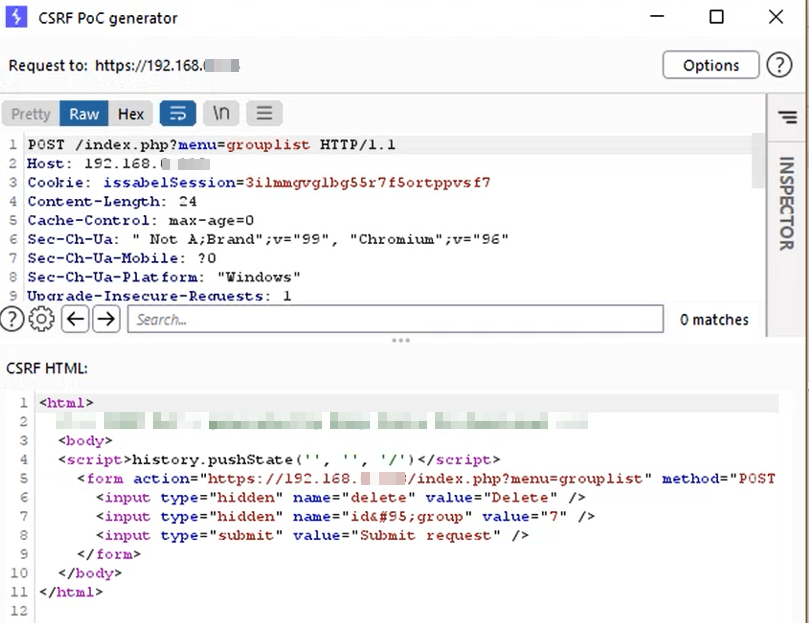 sahiloj/cve-2023-37597
Issabel-pbx v 4.0.0-6 contains a Cross-Site Request Forgery (CSRF) vulnerability in its user group management functionality.
 sahiloj/cve-2023-37599
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.
 vino-theva/cve-2021-44228
Apache Log4j is a logging tool written in Java. This paper focuses on what is Log4j and log4shell vulnerability and how it works, how it affects the…
 jeromeyoung/cve-2021-43141
Information about CVE-2021-43141, a reflected XSS in the plan_application section.
 sudaiv/cve-2021-41081
N-DAY VULNERABILITY RESEARCH (FROM PATCH TO EXPLOIT ANALYSIS OF CVE-2021-41081)

 edubr2020/cve-2021-40444--cabless
Modified code so that we don´t need to rely on CAB archives
 immersive-labs-sec/cve-2021-40444-analysis
Deobfuscated exploit code for CVE-2021-40444 with detailed analysis and supporting blog article documenting the attack vector and recovery process.
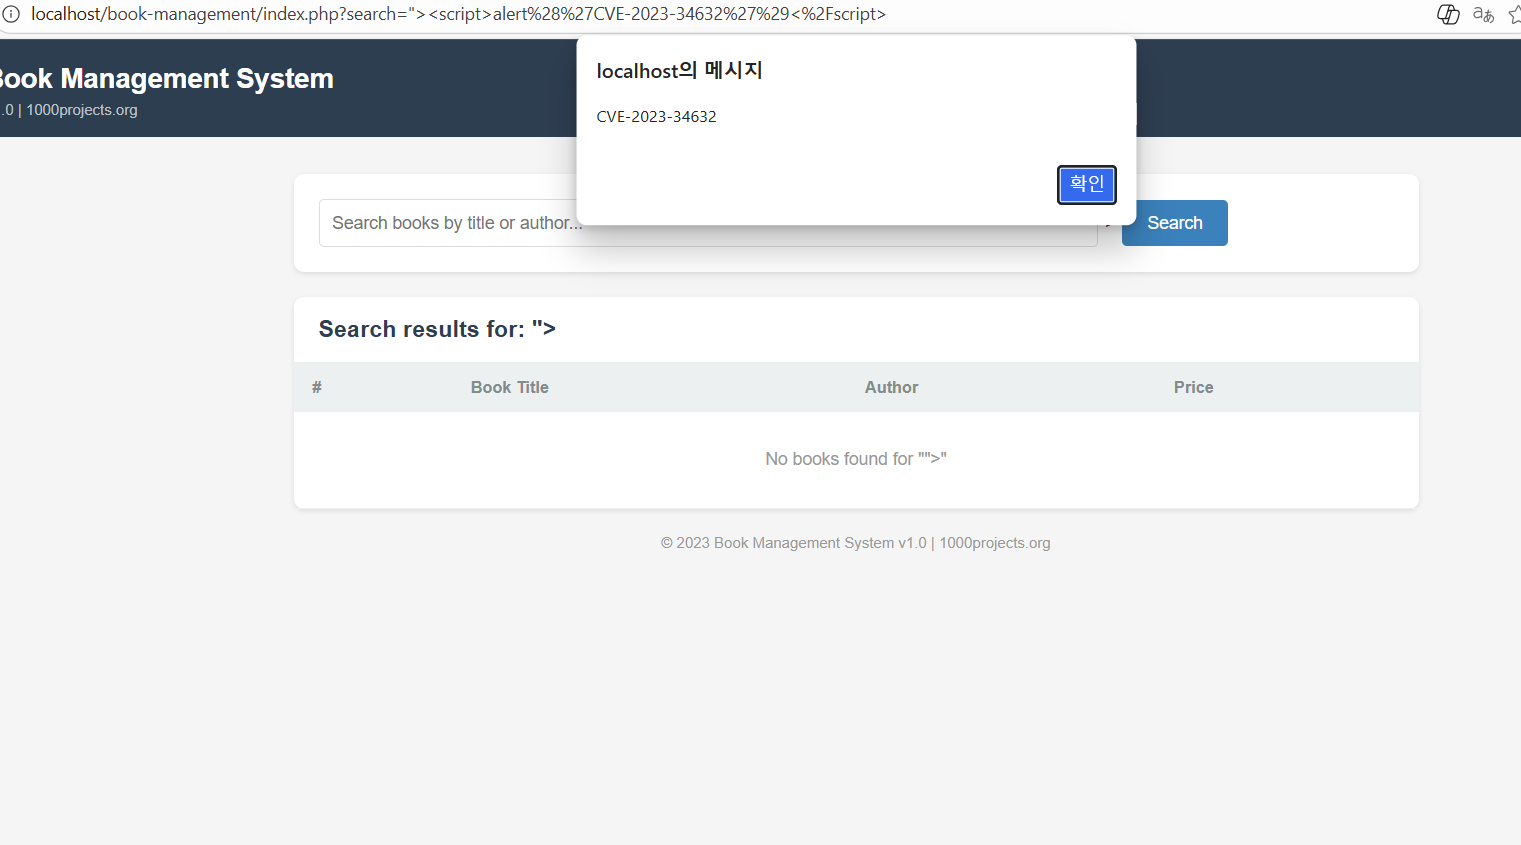 ssophiz/cve-2023-34632
Reflected XSS in 1000projects Book Management System 1.0









