
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 alucard0x1/cve-2026-98432
Proof-only PoC for CVE-2026-98432, a Linux IPv4/TCP ireq_opt use-after-free: race trigger and heap-reuse oracle that confirms the UAF without code…
 offline-ant/tcp2kaslr
CVE-2026-98432: a plain IPv4 TCP server is vulnerable, MPTCP is not the trigger. Bug trigger, evidence and analysis.
 alvaroguzmancode/cve-2026-98432
Rust detector and local lab for CVE-2026-98432, a Linux IPv4 TCP use-after-free in inet_opt/ireq_opt: static ELF analysis, kprobe reachability…
 raahilmw/synipopt
IPv4 SYN with IP options, one lab target per run, for CVE-2026-98432 research. Header-offset parser, regression tests, and a postmortem of a broken…
 googlesky/cve-2026-98432
KASAN-verified proof-of-concept reproducing CVE-2026-98432, a Linux kernel IPv4 TCP inet_opt/ireq_opt use-after-free, with cross-CPU race harness and…
 4onurdemir/tcl-androidtv-root-attempts
Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…
 janewas/cve-2026-98260-vivo-gki-research
Research notes: porting CVE-2026-98260 to vivo/iQOO GKI 6.6.127 (no exploit code; coordinated disclosure planned)
 jadedfella/lpe-study-notes
A slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)
 nanoturtle1145/cve-2026-98260-uaf
CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…
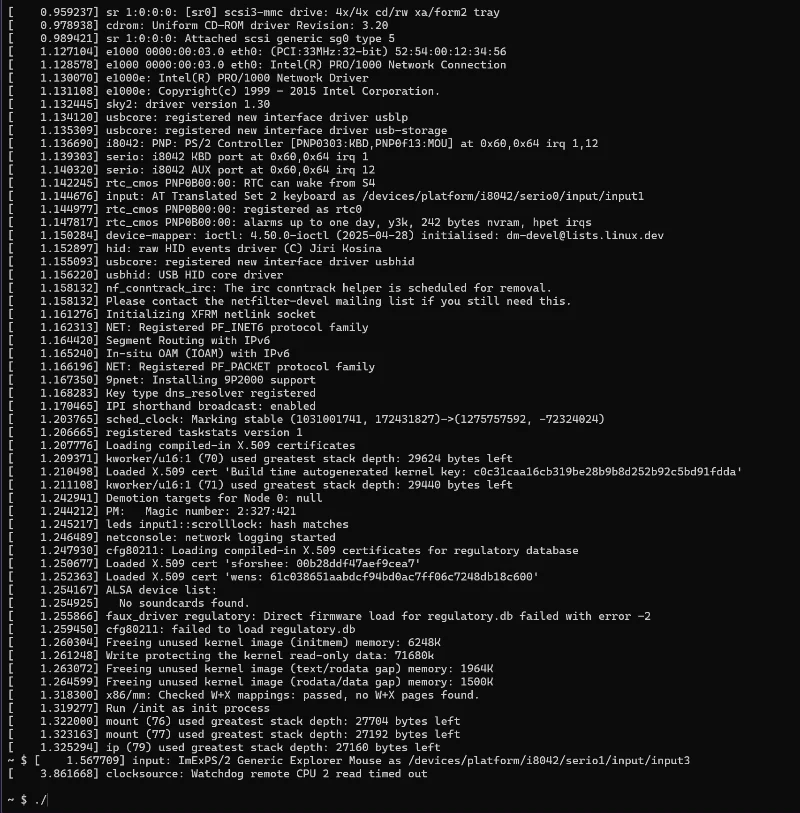 imkidz0/poc-cve-2026-98258
Proof-of-concept demonstrating CVE-2026-98258, a Linux kernel posix-cpu-timers flaw where a queued timer is freed on the expiry list, with a working…
 malhyuk/cve-2026-98180
Proof-of-concept and KASAN-confirmed KUnit reproducer for CVE-2026-98180, a drm/msm use-after-free of scheduler-containing ring and VM objects…
 ahiamaduuche-sys/cve-2026-97859-analysis
Cybersecurity assignment on CVE-2026-97859, severity analysis, patching, and the Cyber Kill Chain.
 ahiamaduuche-sys/cve-2026-97859-cybersecurity-analysis
Cybersecurity assignment on CVE-2026-97859, severity analysis, patching, and the Cyber Kill Chain.
 ahiamaduuche-sys/cve-2026-97859-cyb-analysis
Cybersecurity assignment on CVE-2026-97859, severity analysis, patching, and the Cyber Kill Chain.
 phinode-labs/nginx-cve-2026-97629
Proof-of-concept exploit, root-cause analysis and one-line patch for CVE-2026-97629, an nginx TLS session-ticket forgery that bypasses…
 woshigenm/cve-2026-97555
Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…
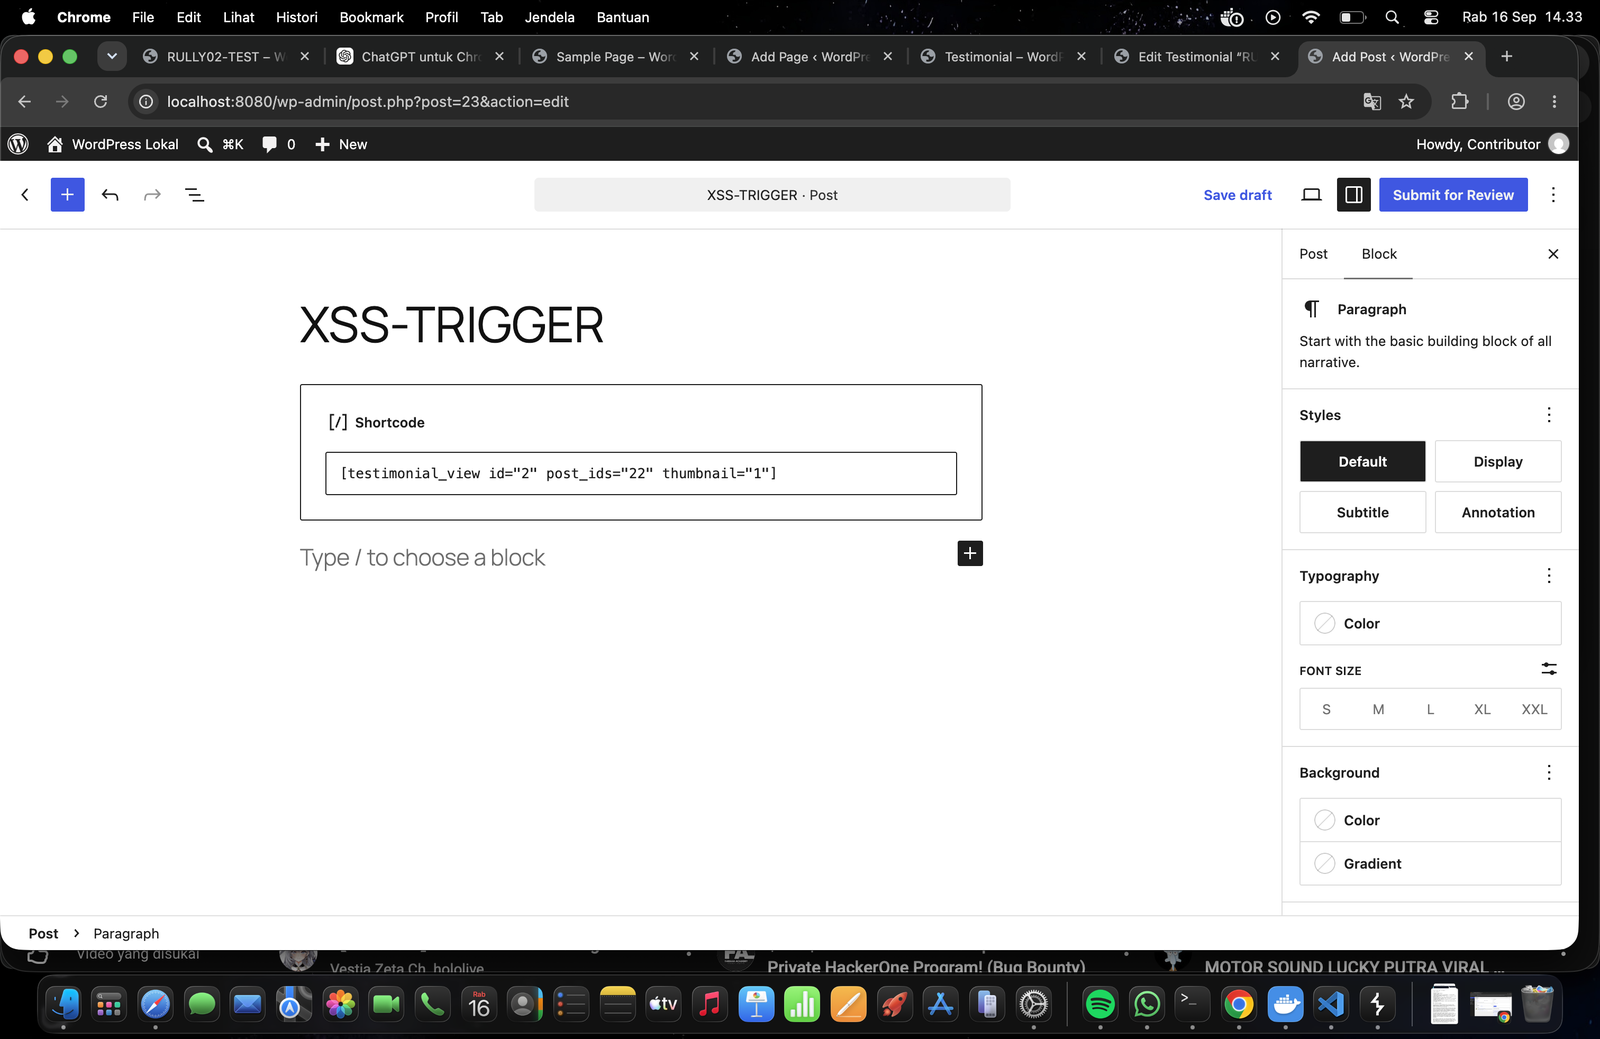 rully2212/cve-2026-97286
Technical advisory and proof of concept for CVE-2026-97286, an authenticated stored XSS in the WordPress Strong Testimonials plugin, with attack…
 ampedwastaken/cve-2026-97229-gitlab-ci-cd-regex-compiler-rce
Technical investigation of CVE-2026-97229 (GitLab CI/CD regex RCE): local patched GitLab lab, CI Lint API checks, version auditing, and defensive…








