
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 0xblackash/cve-2026-55200
CVE-2026-55200
 imfht/cve-2023-38545
😄 CVE-2023-38545堆溢出的POC和分析文章
 ixtal23/spectrescope
The demo of the speculative execution attack Spectre (CVE-2017-5753, CVE-2017-5715).
 hyeonjun17/cve-2022-2590-analysis
In-depth analysis of CVE-2022-2590, a Linux kernel race condition in shared memory (shmem) enabling arbitrary write to read-only pages via…
 arttnba3/cve-2022-0847
my personal exploit of CVE-2022-0847(dirty pipe)
 vettrivel007/cve-disclosures
A repository documenting security vulnerabilities discovered in Free and Open Source Software (FOSS) by VETTRIVEL U
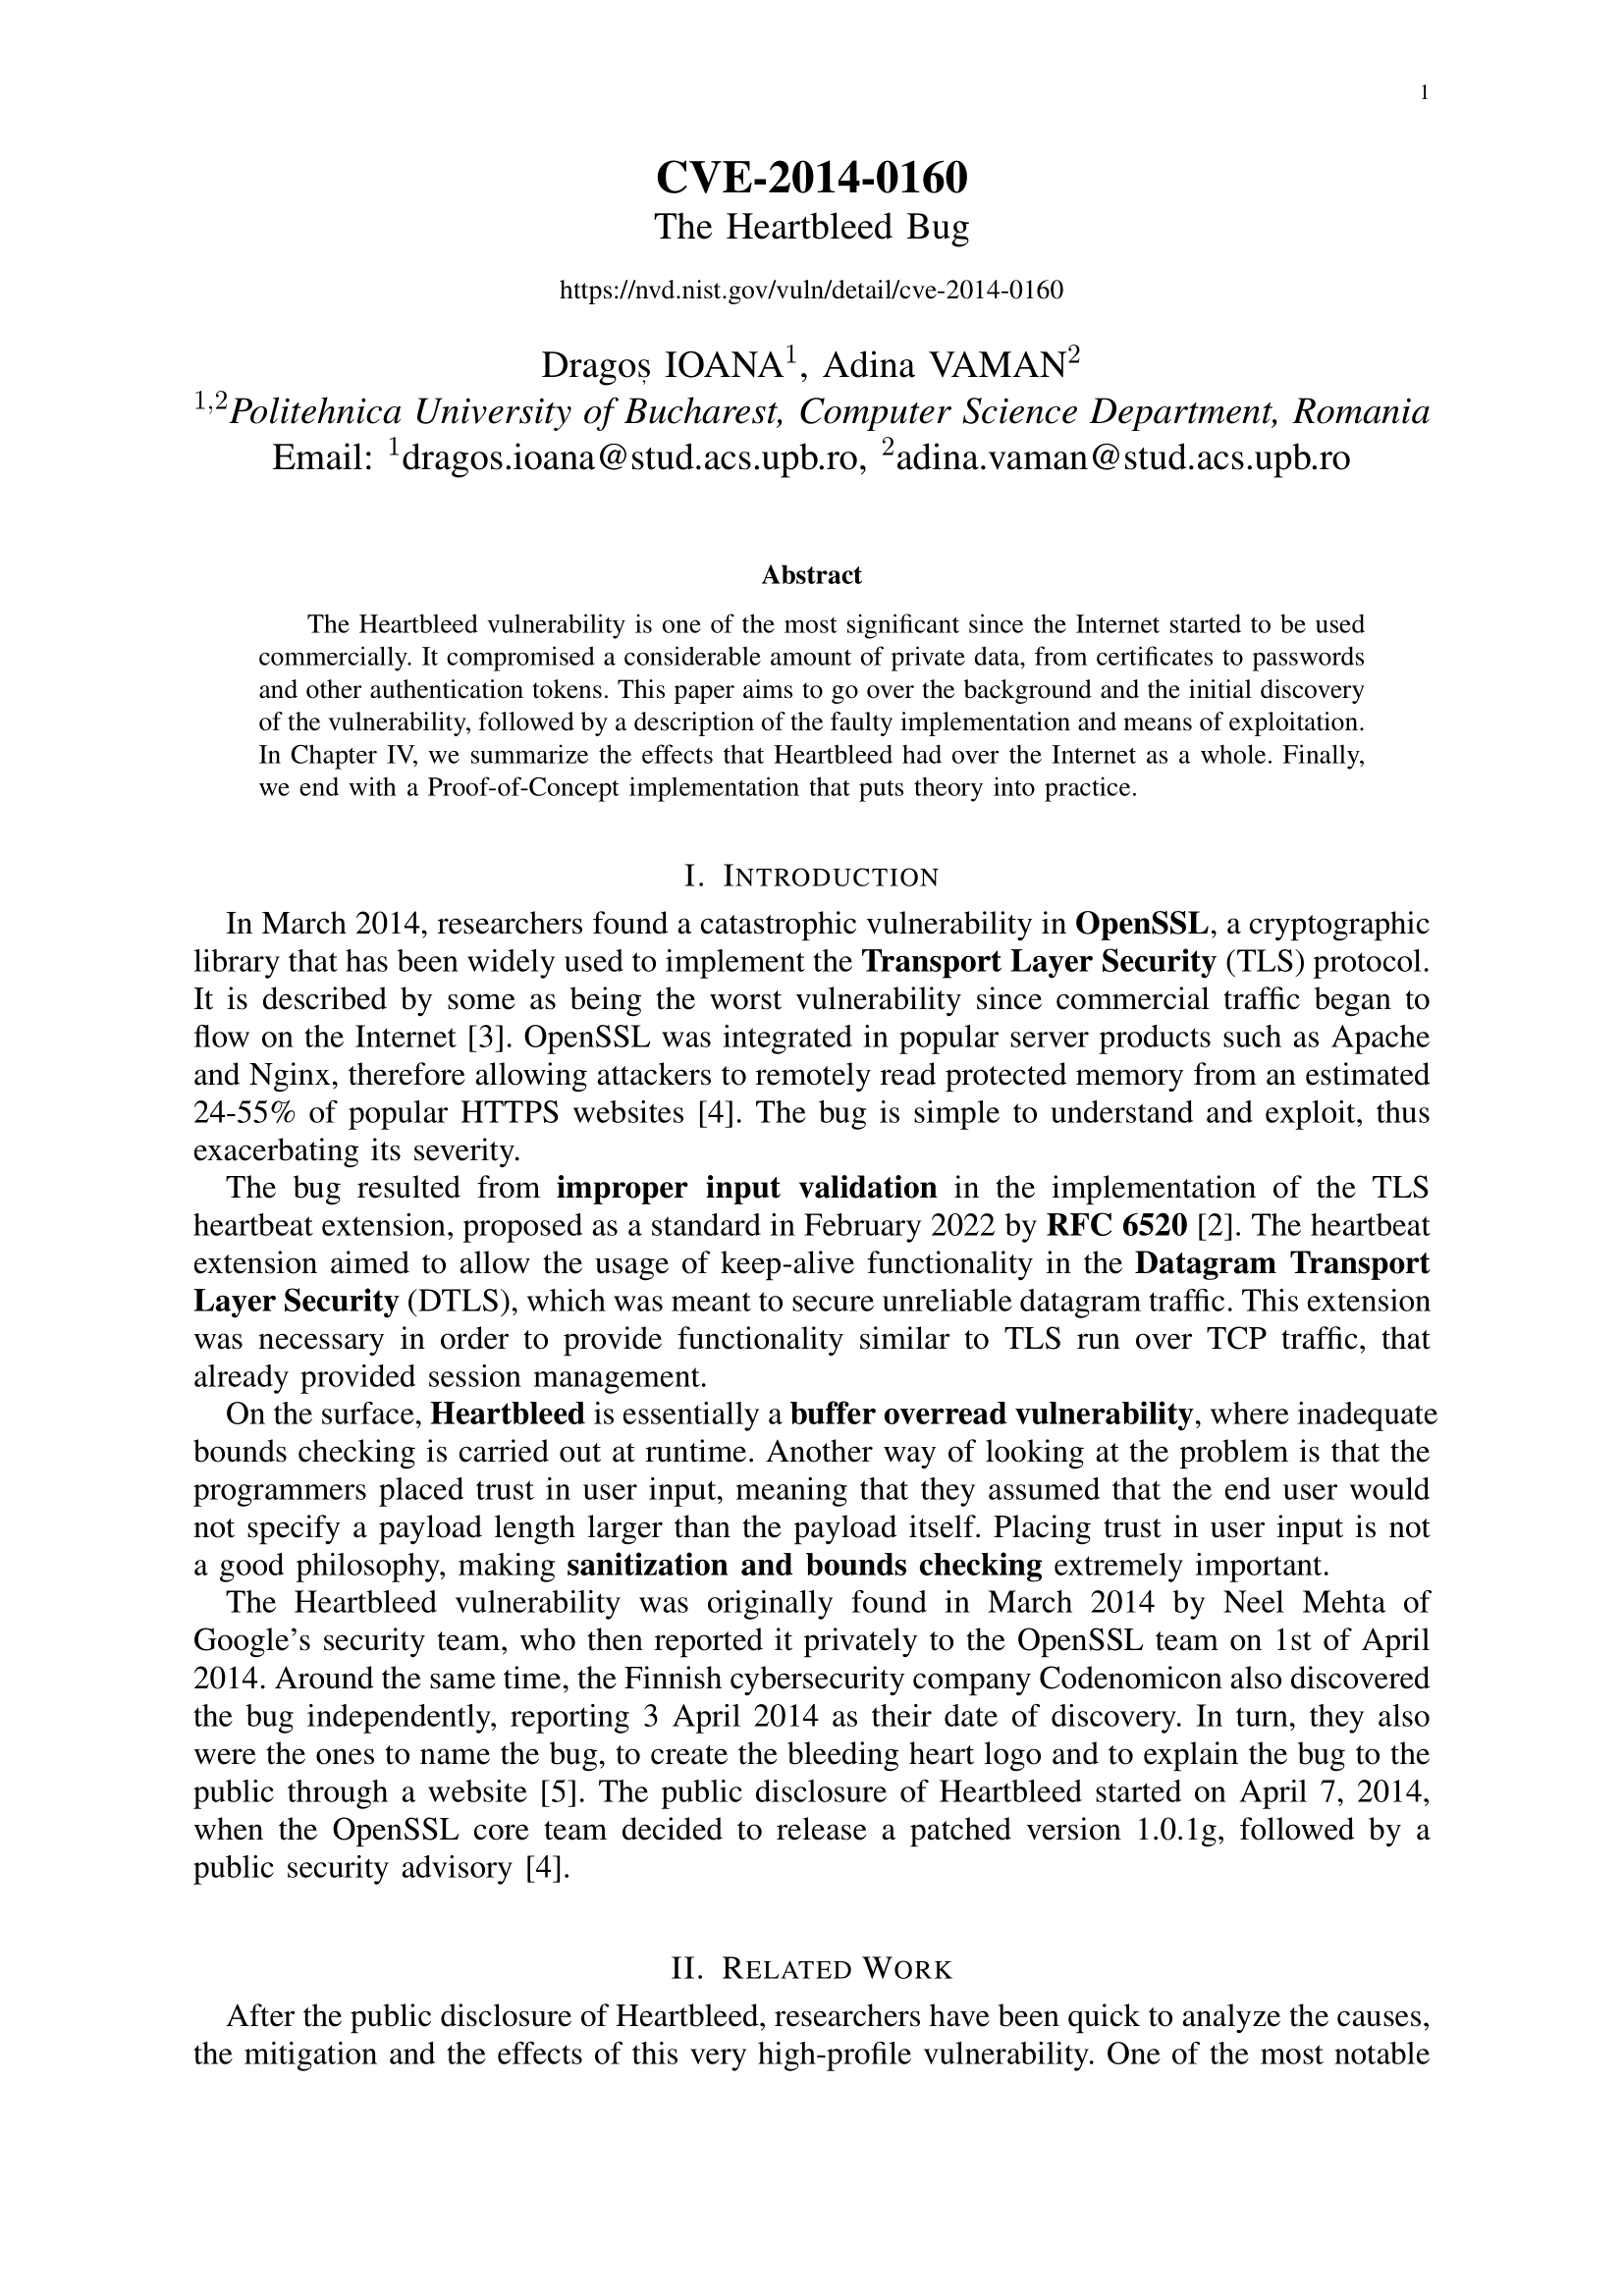 undacmic/heartbleed-proof-of-concept
Proof of concept for exploiting the Heartbeat Extension bug detailed in the CVE-2014-0160. :old_key: :unlock:
 giwon9977/cve-2021-33739_poc_analysis
Analysis and proof-of-concept exploit for CVE-2021-33739, a Windows kernel privilege escalation vulnerability, with educational resources for…
 gal-nagli/cve-2021-26832
Cross Site Scripting (XSS) at the "Reset Password" page form of Priority Enterprise Management System v8.00 allows attackers to execute javascript on…
 digamma-ai/cve-2020-8835-verification
Coq-based formal verification of a Linux kernel eBPF verifier vulnerability (CVE-2020-8835) with reproducible build environment and proof artifacts.
 ibm/pgp-client-checker-cve-2021-33560
Tool to check whether a PGP client is affected by CVE-2021-33560
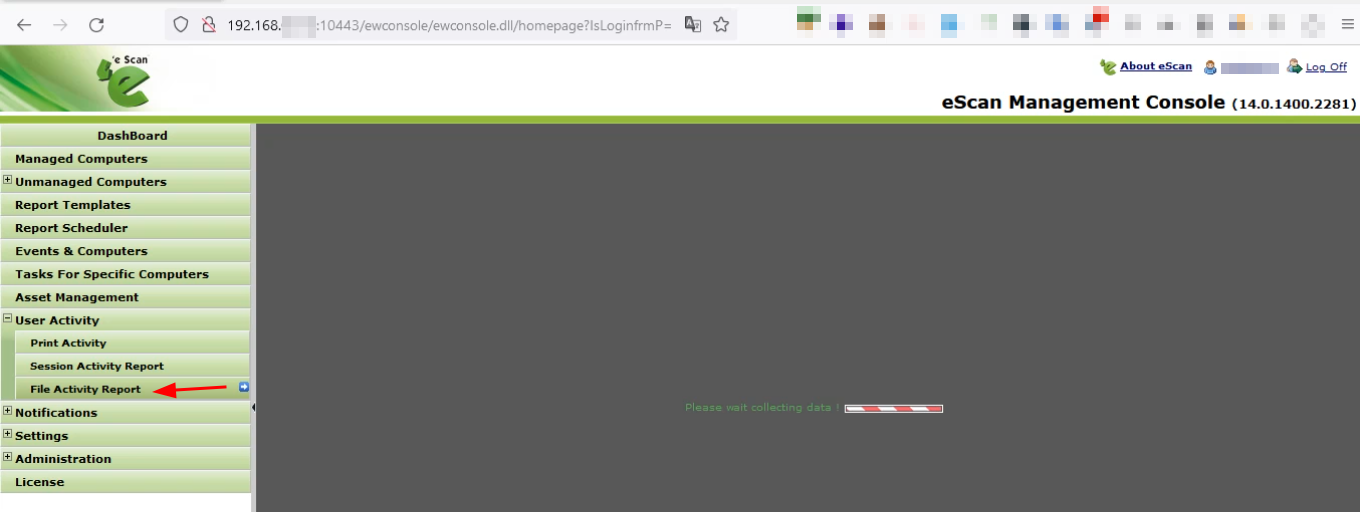 sahiloj/cve-2023-34836
A Reflected Cross-Site Scripting (XSS) vulnerability exists in Microworld Technologies eScan Management Console v14.0.1400.2281. The vulnerable…
 karlemilnikka/cve-2024-0710
Unauthenticated Form Submission Unique ID Modification
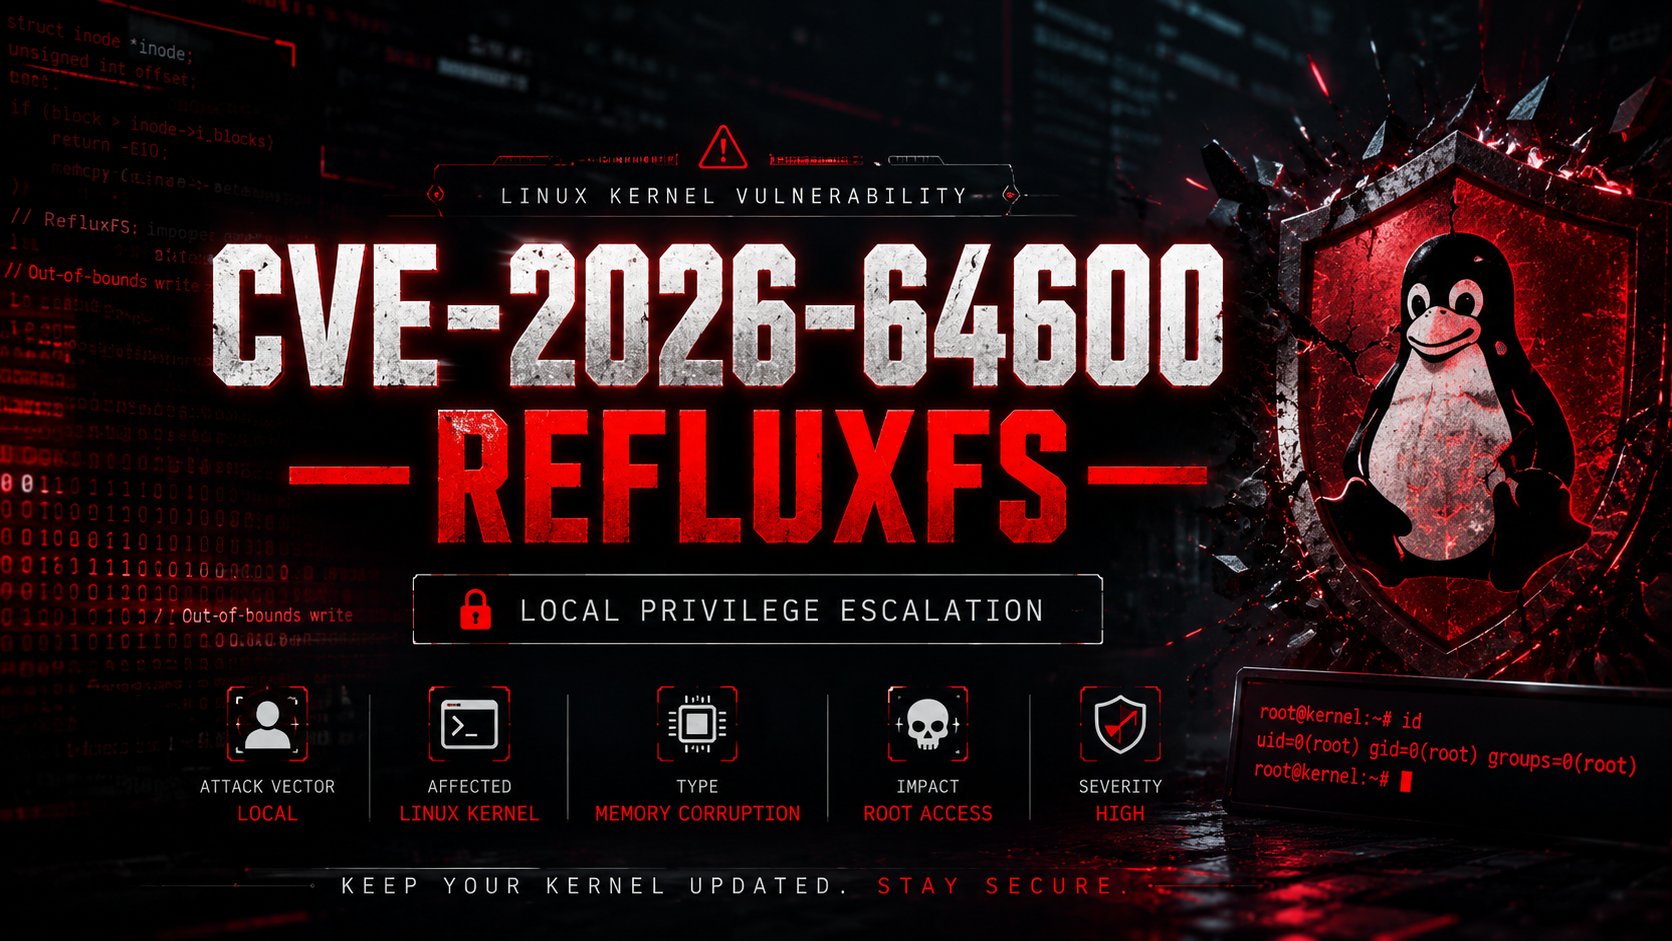 letsr00t/refluxfs_cve-2026-64600
Technical analysis of CVE-2026-64600, a Linux kernel local privilege escalation in RefluxFS via memory corruption, with mitigation and references for…
 mbadanoiu/wso2-2020-0731
WSO2-2020-0731: XXE and XSS vulnerabilities in WSO2 Carbon
 chrissub08/cve-2026-33910_sqlinjectionvulnerabilityopenemr8.0.0.2
CVE-2026-33910: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 nu11secur1ty/rtfm
Comprehensive book on penetration testing and red teaming operations, covering exploitation, post-exploitation, and adversary simulation techniques…
 nastycrow/cve-2025-27893
Detailed disclosure of CVE-2025-27893: an authenticated web parameter manipulation vulnerability in Archer Platform 6.x allowing unauthorized…








