
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 tandasat/hello-vt-rp
A simple hypervisor demonstrating the use of the Intel VT-rp (redirect protection) technology.
 horkimhab/cve-2026-93485
Educational security research repository for learning and testing CVE-2026-93485 concepts in isolated, authorized lab environments.
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 horkimhab/cve-2026-77179
Educational CVE-2026-77179 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated…
 horkimhab/cve-2026-65374
Educational CVE-2026-65374 research repository with lab setup guidance for authorized vulnerability testing and defensive security study.
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 shinycolumn/cve-2025-56801
AES-CFB IV Generation Vulnerability in Reolink Desktop Application
 kyaw-tun/blue-team-capstone
CVSS v3.1 assessment of CVE-2009-0658 (Adobe Acrobat Buffer Overflow), including Base, Temporal, and Environmental scoring and remediation…
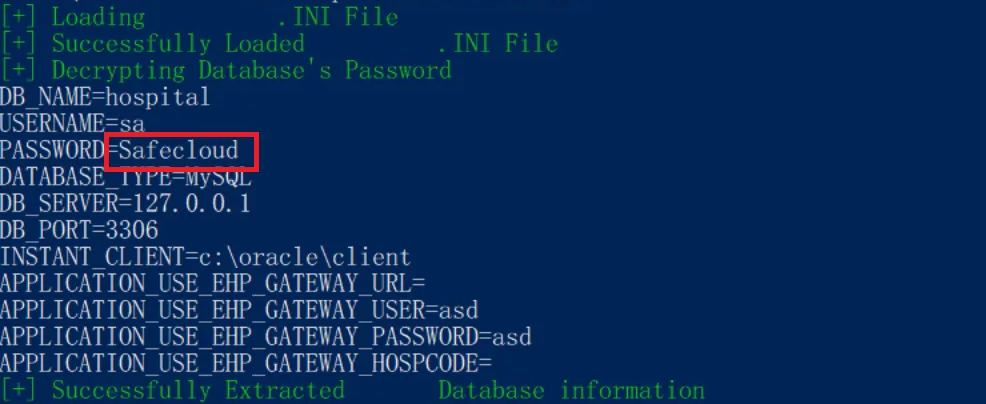 safecloudth/cve-2024-53522
Proof-of-concept exploit for CVE-2024-53522, demonstrating decryption of HOSxP XE database credentials using a static hard-coded private key-IV.
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 bjrjk/cve-2022-4262
Full Chain Analysis of CVE-2022-4262, a non-trivial feedback slot type confusion in V8.
 seanwrightsec/cve-2022-42889-poc
Proof of Concept for the Apache commons-text vulnerability CVE-2022-42889.
 signal-sfop/sfop
Segmentation Fault-Oriented Programming exploitation technique
 vincentbernat/cve-2015-3456
Experiments related to CVE-2015-3456
 ndmalc/cve-2021-20323
Proof-of-concept and analysis for CVE-2021-20323, a reflected XSS vulnerability in Keycloak's clients-registrations endpoint, with exploitation…
 ffri/xprtestsuite
A collection of scripts and documents to help future XProtect Remediator (XPR) research
 mmxsrup/cve-2019-5489
Page Cache Side Channel Attacks (CVE-2019-5489) proof of concept for Linux
 0xblackash/cve-2026-55200
CVE-2026-55200








