
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 halcy0nic/cve-2022-36752
Proof of concept for CVE-2022-36752
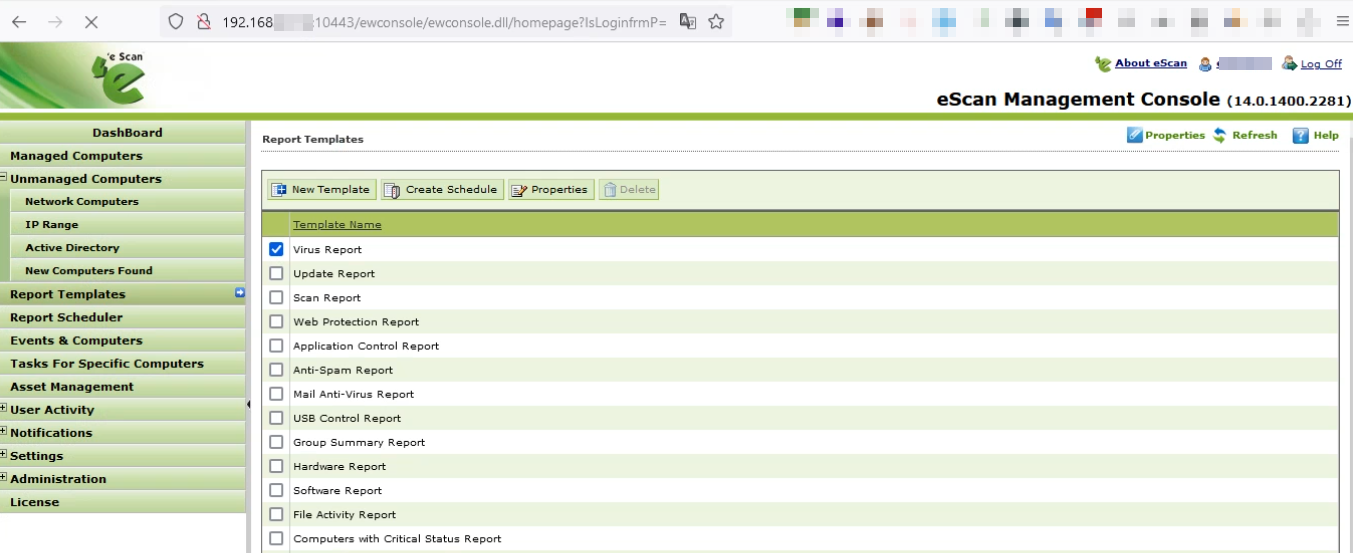 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
 v0idnetwork/cve-2026-46331
pedit COW
 themehackers/cve-2026-34038
CVE-2026-34038: Authenticated Remote Command Injection in Coolify
 snorlyd/https-nj.gov---cve-2020-11023
Vulnearability Report of the New Jersey official site
 ant1sec-ops/cve-2024-33453
Sensitive Data exposure
 at190510-cuong/cve-2025-65482-xxe-
CVE-2025-65482 (XXE)
 0x00phantom-hat/hoverfly-1.11.3-rce-cve-2025-54123-exploit
Exploit for CVE-2025-54123, an authenticated OS command injection in Hoverfly's middleware API, providing check-only, single-command, interactive…
 popy21/security-research
Vulnerability research write-ups — CVE-2026-12478 (libsoup), Apple WebKit, Google VRP
 gabrielha12/termix-research
CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
 0xblackash/cve-2026-33017
CVE-2026-33017
 lukasz-rybak/cve-2026-27621
CVE-2026-27621 - TypiCMS Core has Stored Cross-Site Scripting (XSS) via SVG File Upload
 nick-yin12/106362522
針對近期微軟公布修補遭駭客攻擊的Exchange Server漏洞問題,台灣DEVCORE表示早在1月5日便已發現安全漏洞後,並且向微軟通報此項編號命名為「CVE-2021-26855 」,以及「CVE-2021-27065」的零日漏洞,同時也將此項漏洞稱為「ProxyLogon」。 …
 dharan10/cve-2025-67730
A public disclourse of CVE-2025-67730 in Frape lms By dharan ragunathan
 walidriouah/cve-2026-30691
CVE-2026-30691: Stored Cross-Site Scripting (XSS) in @cyntler/react-doc-viewer
 vnchk1/sec_review_cve-2024-3094
Security review уязвимости CVE-2024-3094 с открытым исходным кодом
 rishavand1/cve-2025-65791
CVE-2025-65791 — Command Injection in ZoneMinder
 git0xlai/react2shellpoc
This repository provides a proof-of-concept for CVE-2025-55182 (React2Shell), a remote code execution vulnerability in React Server Components. It…








