
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 n0kovo/awesome-password-cracking
A curated list of awesome tools, research, papers and other projects related to password cracking and password security.
 binarygolf/bggp
Annual small file competition repository with binary golf challenges across themes like polyglots, crashes, self-replication, and downloads,…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 wang-yanting/agentwatcher
Causal context attribution and rule-based monitor LLM defense against indirect prompt injection in LLM agents, achieving state-of-art performance on…
 shurikgo/cve-2026-25262-sm8450-research
CVE-2026-25262 applicability to Snapdragon 8 Gen 1 — experimental results

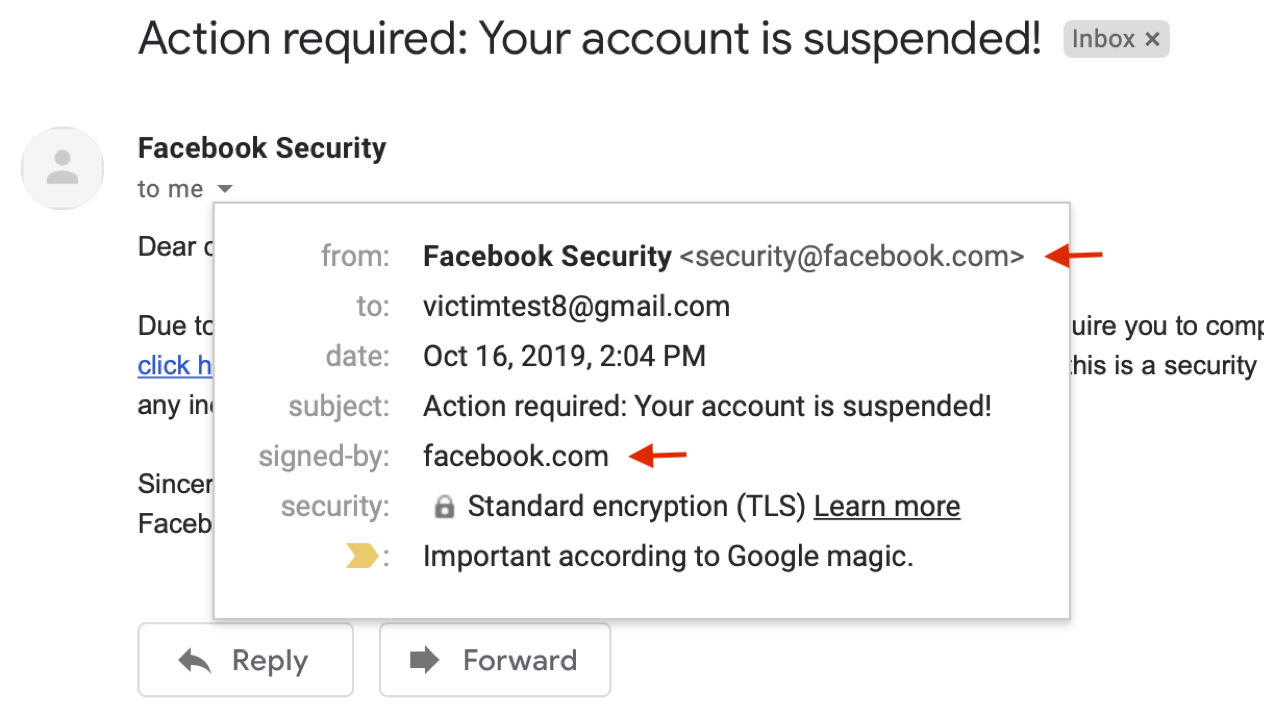 chenjj/espoofer
An email spoofing testing tool that aims to bypass SPF/DKIM/DMARC and forge DKIM signatures.🍻
 hellboy3110/cve-2026-16219-croogo-lab
Safely demonstrates CVE-2026-16219 path traversal in Croogo CMS with a loopback-only PoC, technical analysis, remediation guidance, and standalone…
 cookiengineer/actual-php2shell
:robot: (Vibecoded prototype) NO, There is an easy way to exploit this vulnerability!
 wwwiesel/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 gkrishnan724/cve-2021-38297
A Proof of concept scenario for exploitation of CVE2021-38297 GO WASM buffer-overflow
 nicpwns/cve-2026-62183
Apache Syncope: User self-service privilege escalation
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
 siyuanli00/intact
Research code reproducing multi-turn LLM jailbreak experiments (FITD, MRCJ, ActorAttack, X-Teaming) from the SoK intent-oriented systematization…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 xhowenma/rope
Defense framework enforcing routed origin policy to prevent indirect prompt injection in tool-using LLM agents, with deterministic origin checks and…









