
 #1
Tools for capturing, inspecting, and analyzing network traffic in real-time or from capture files.
Kitploit recommended
 sahilmgandhi/iotshark
IotShark - Monitoring and Analyzing IoT Traffic
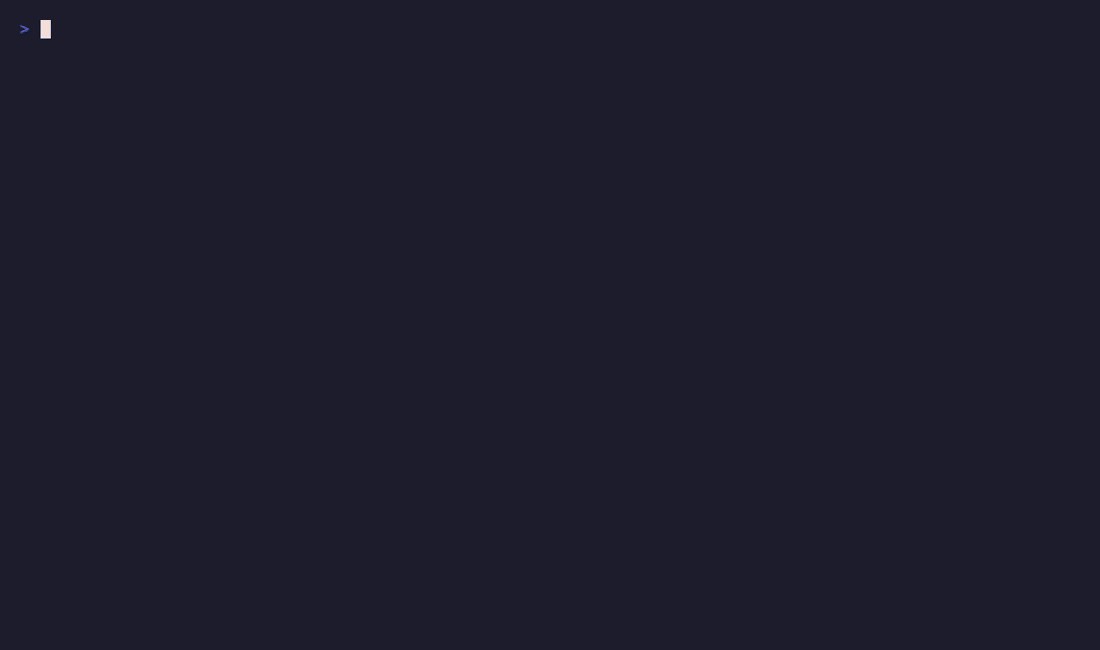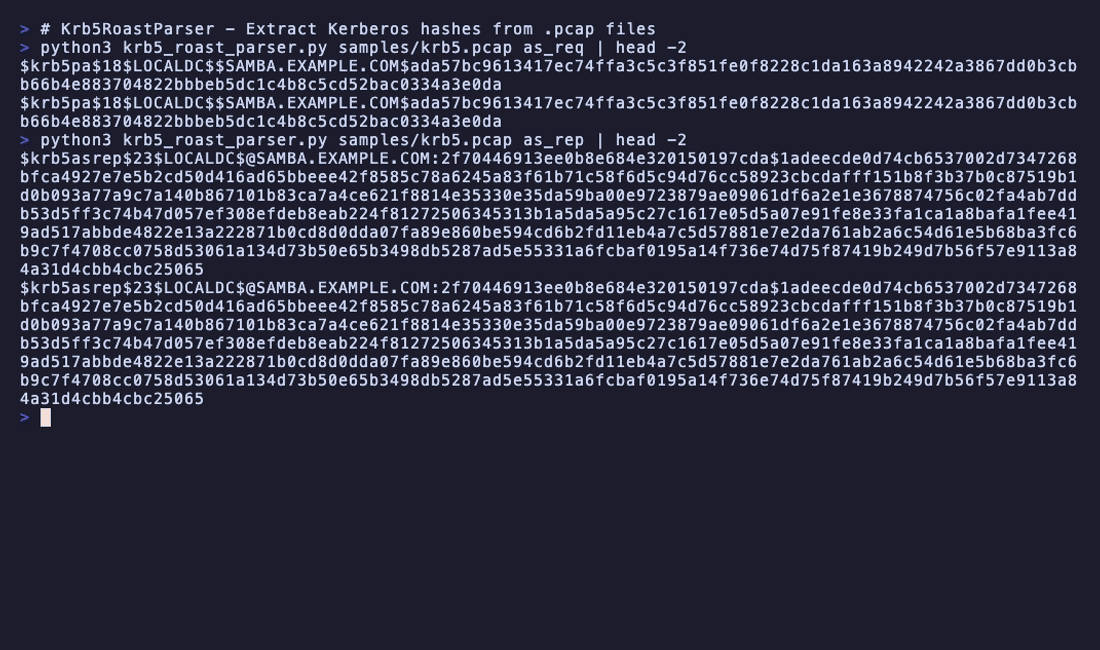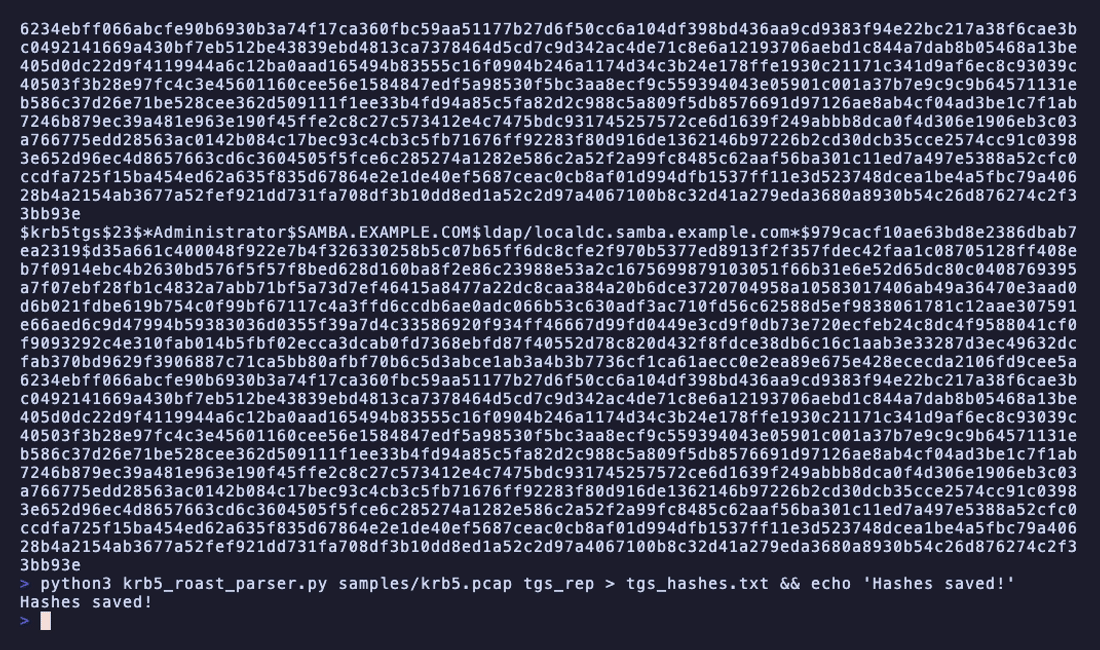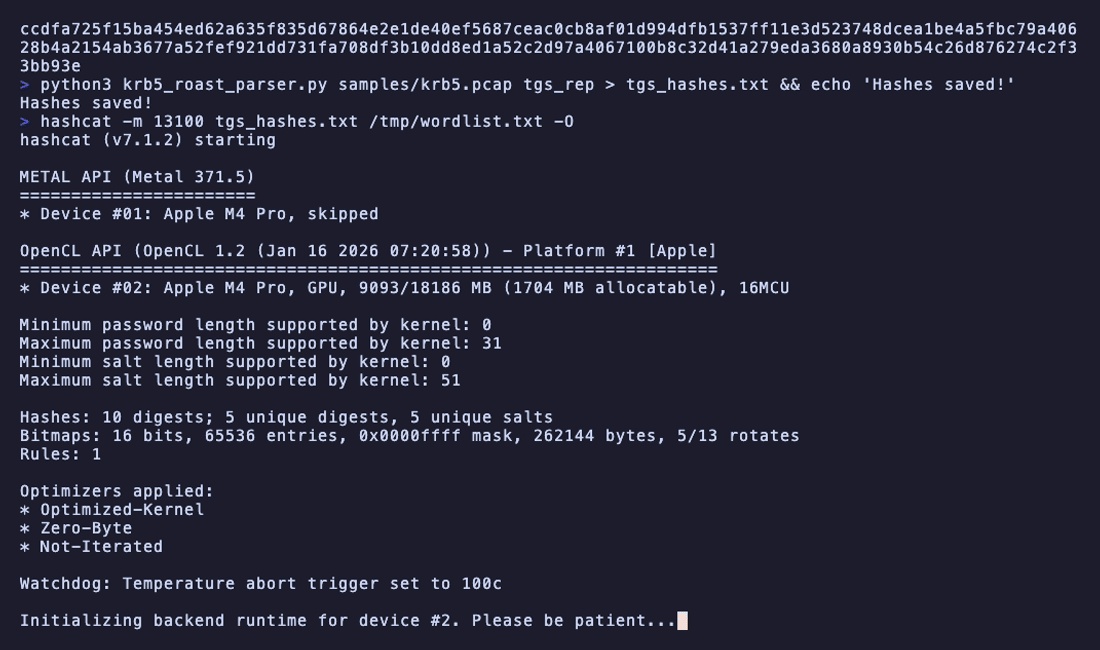 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
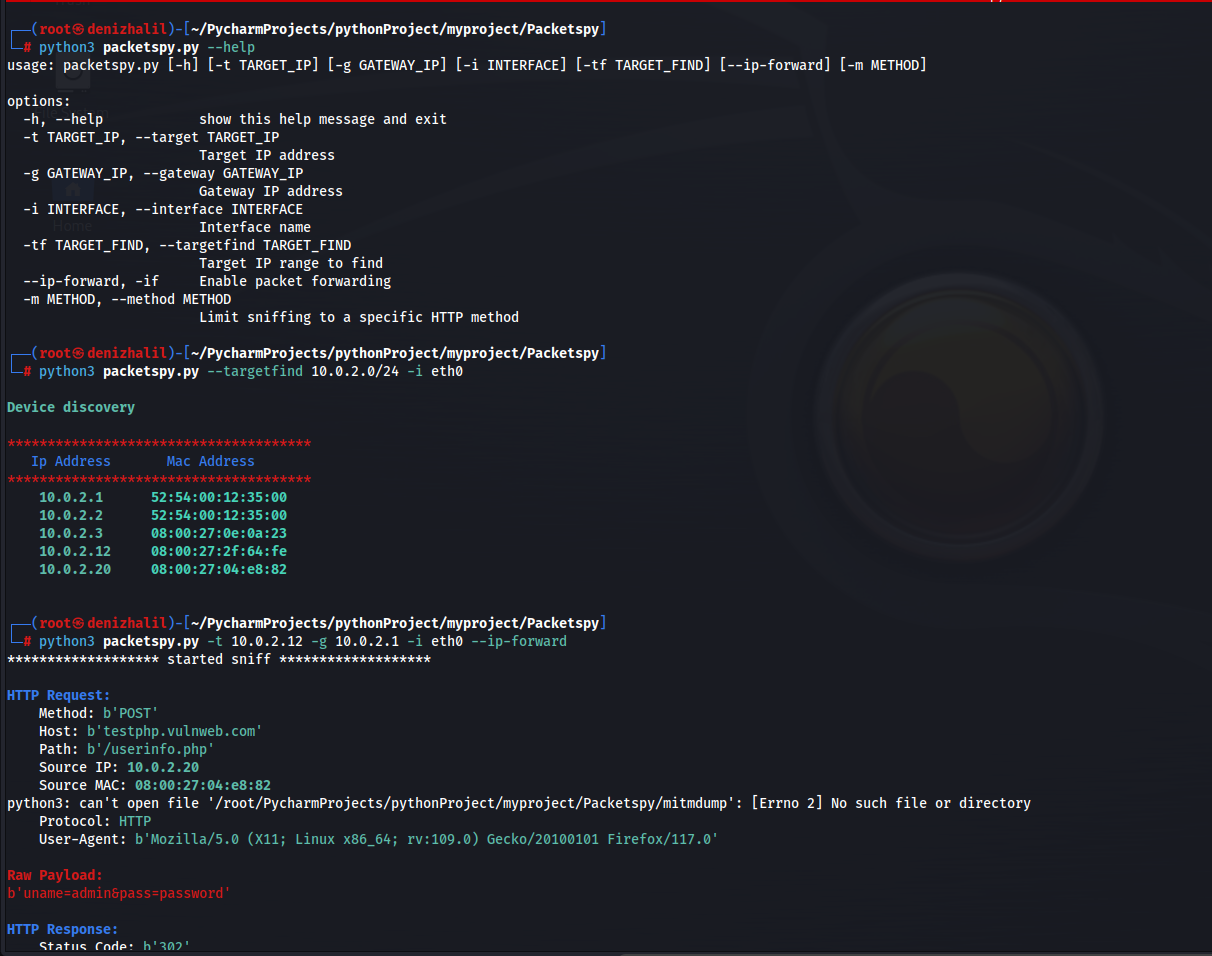 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
 codepr/creak
Poison, reset, spoof, redirect MITM script
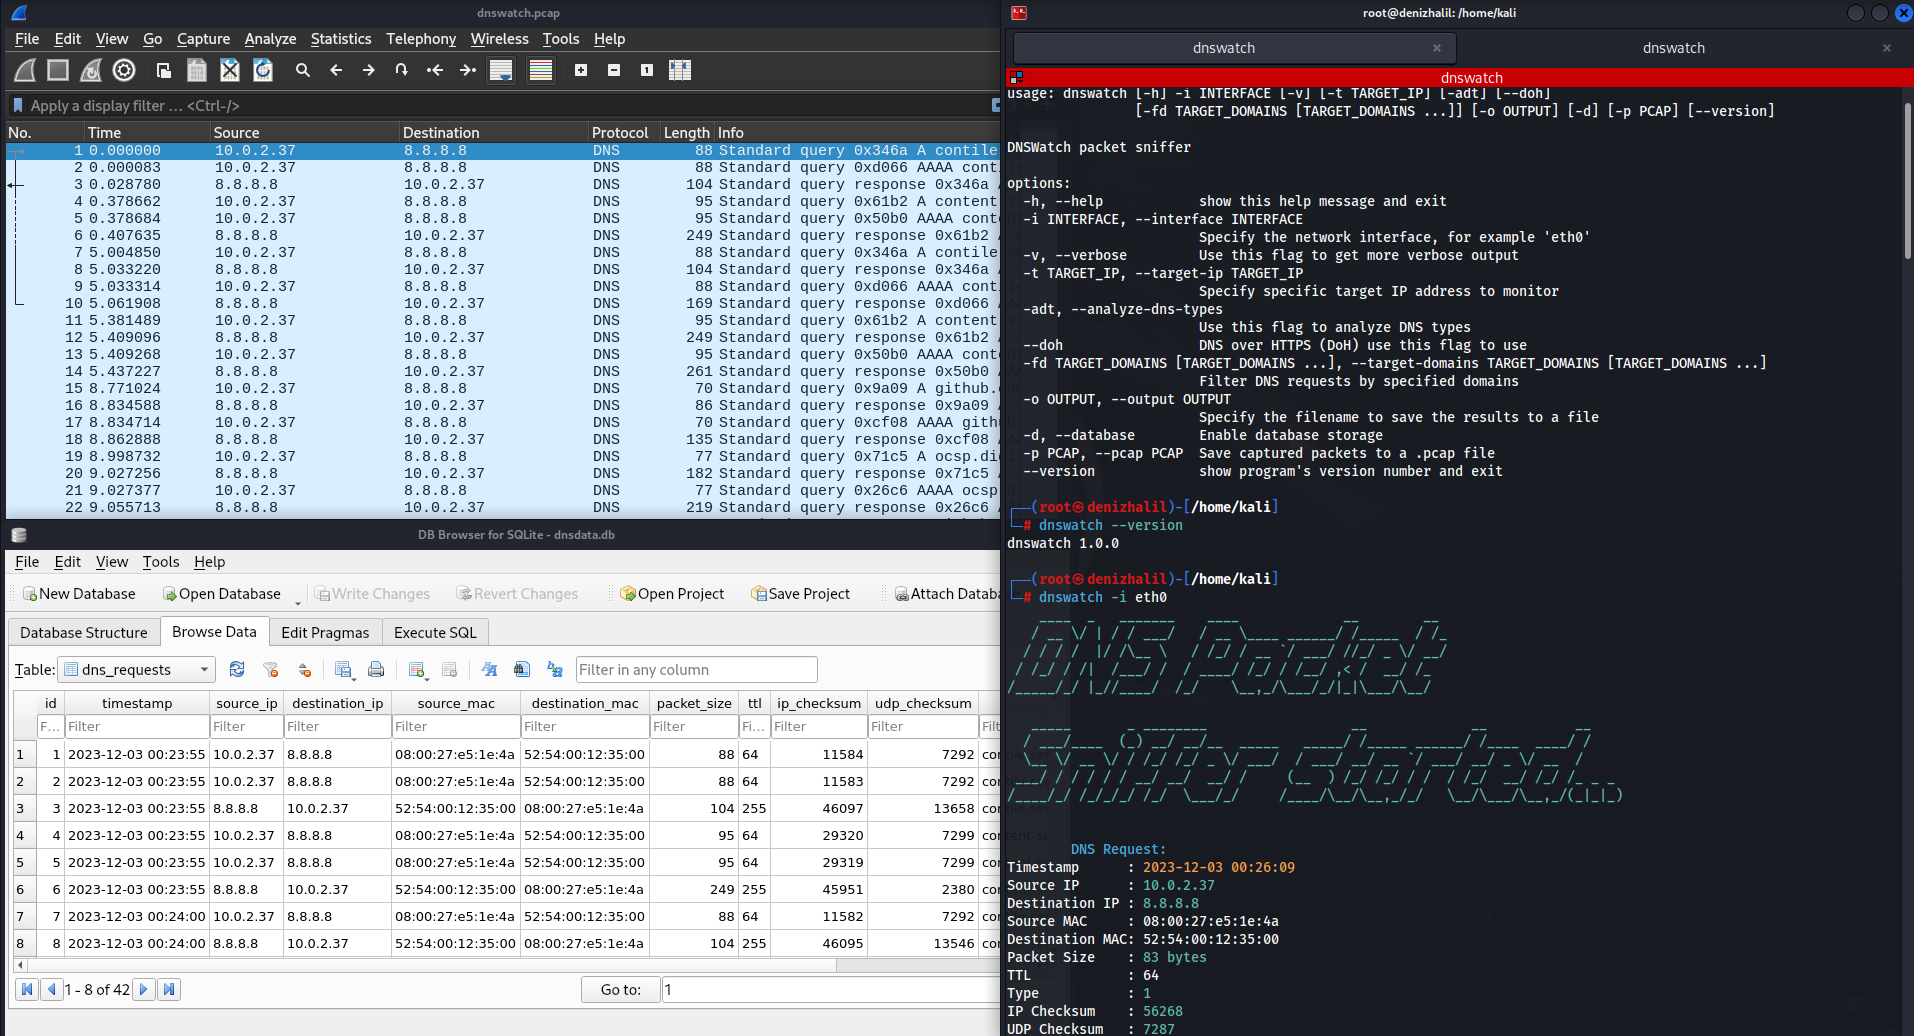 halildeniz/dnswatch
DNS traffic sniffer and analyzer for monitoring, filtering, and detecting anomalies in DNS queries. Features include PCAP export, DoH support, and a…
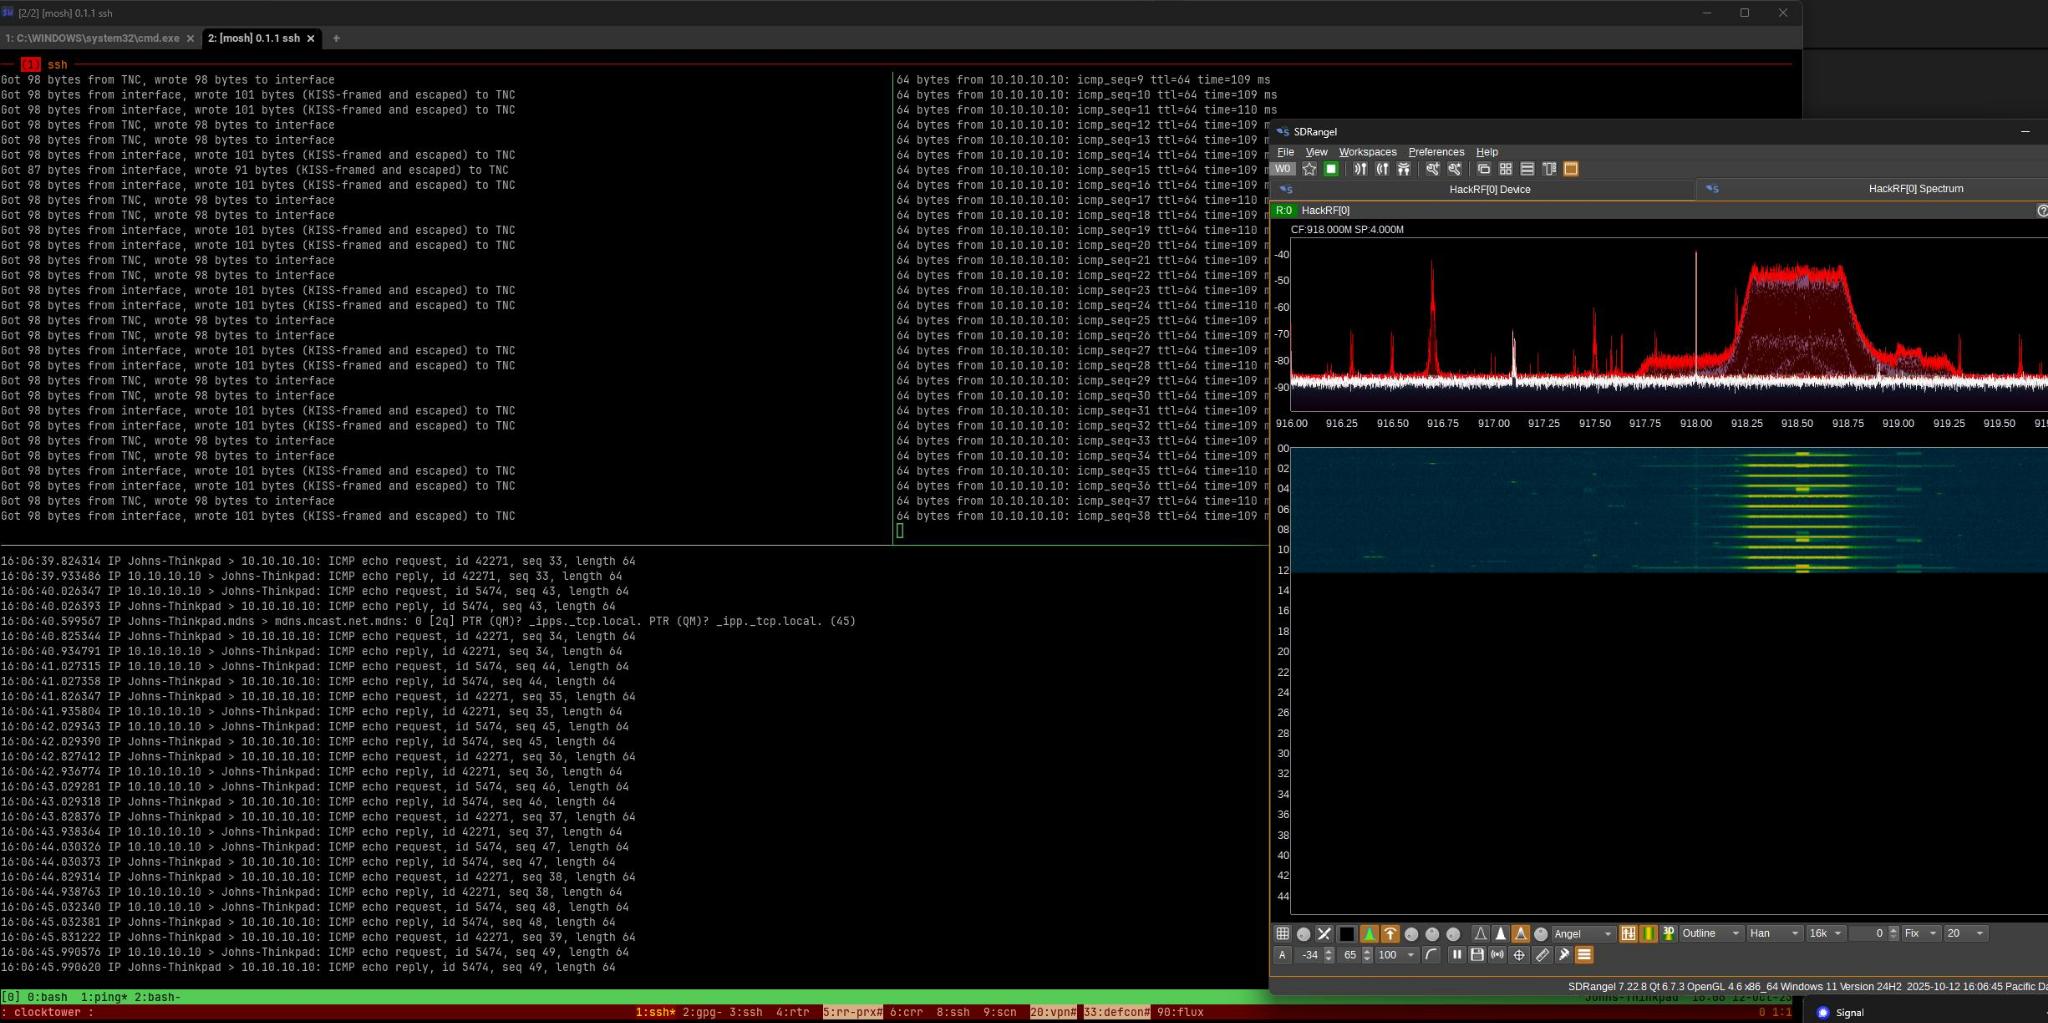 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 nccgroup/pcap-burp
Pcap importer for Burp
 quarkslab/peetch
eBPF-based toolkit for sniffing network traffic, extracting OpenSSL TLS keys, and intercepting/decrypting TLS 1.2 connections in real time using…
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 nccgroup/ebpf
eBPF - extended Berkeley Packet Filter tooling
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
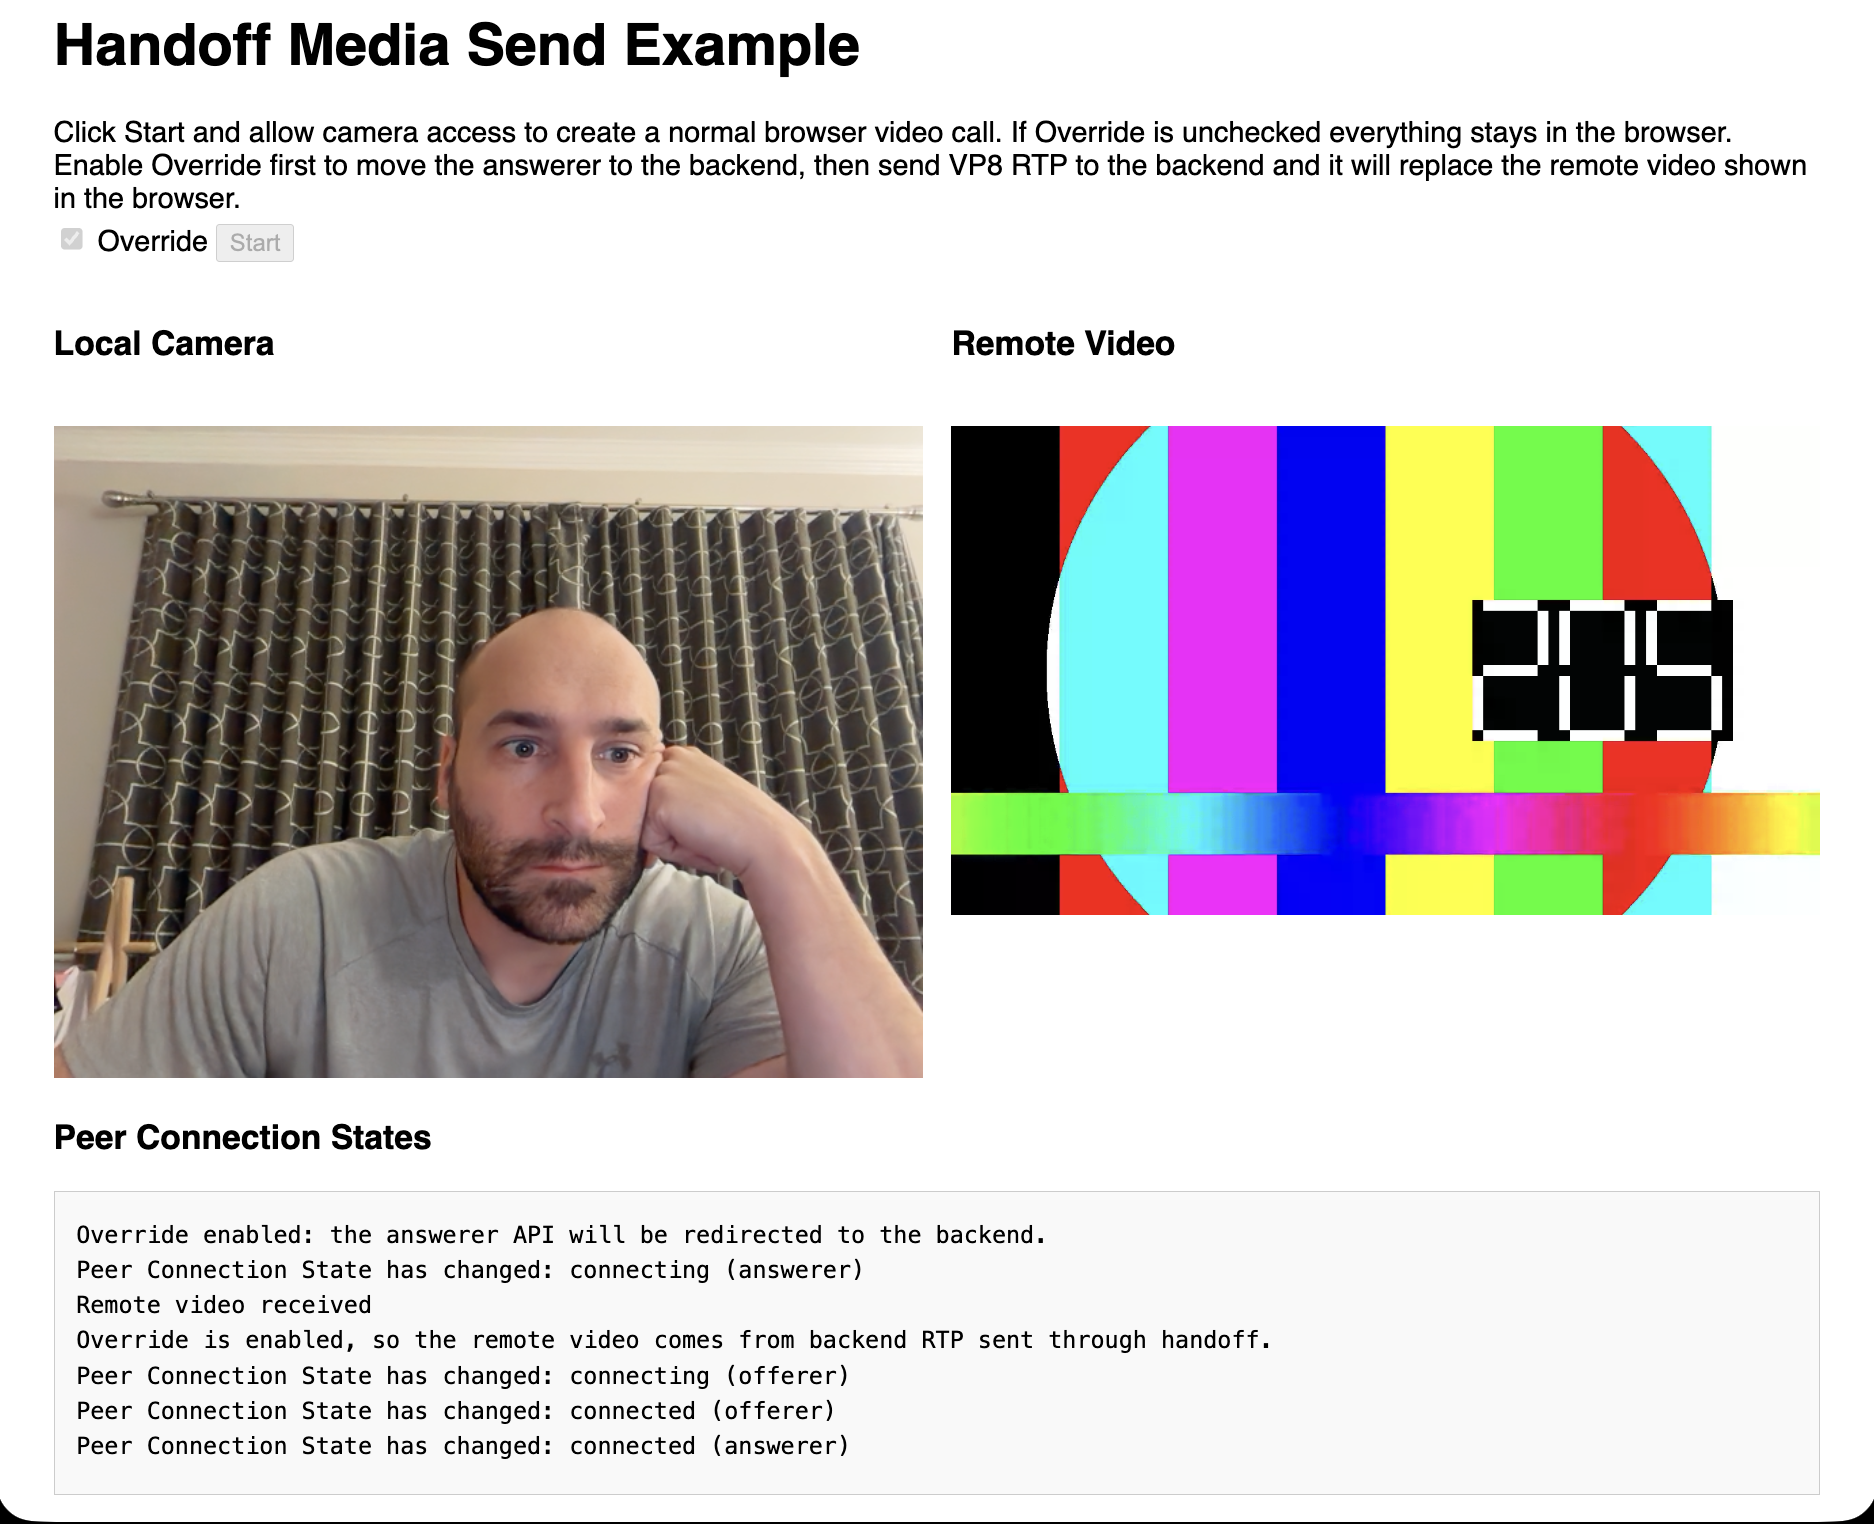 pion/handoff
Start WebRTC in the browser—run it somewhere else
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
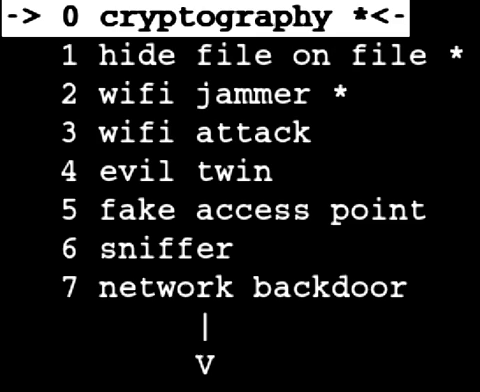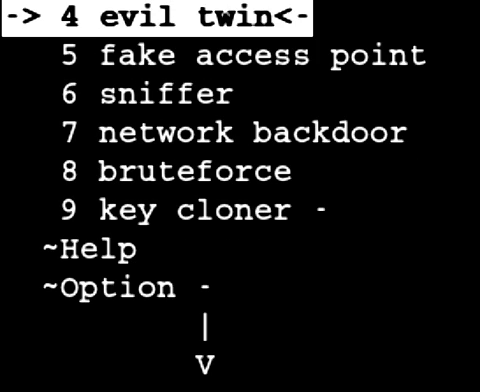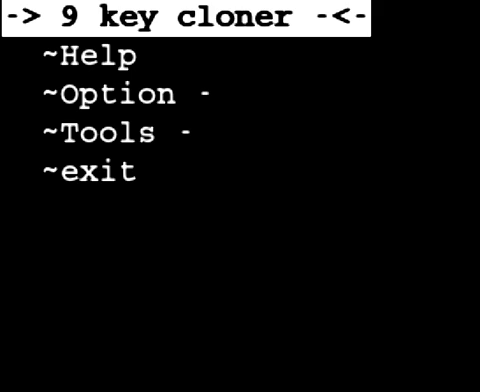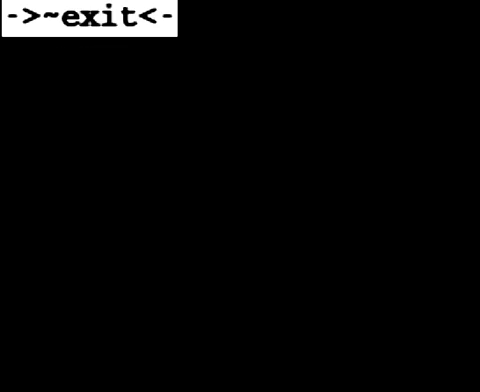 marcrowproject/bramble
Bramble is a hacking Open source suite.
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…








