
 #1
Tools for capturing, inspecting, and analyzing network traffic in real-time or from capture files.
Kitploit recommended
 decrypto-org/rupture
A framework for BREACH and other compression-based crypto attacks
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 awakecoding/wireshark-rdp
Wireshark RDP resources
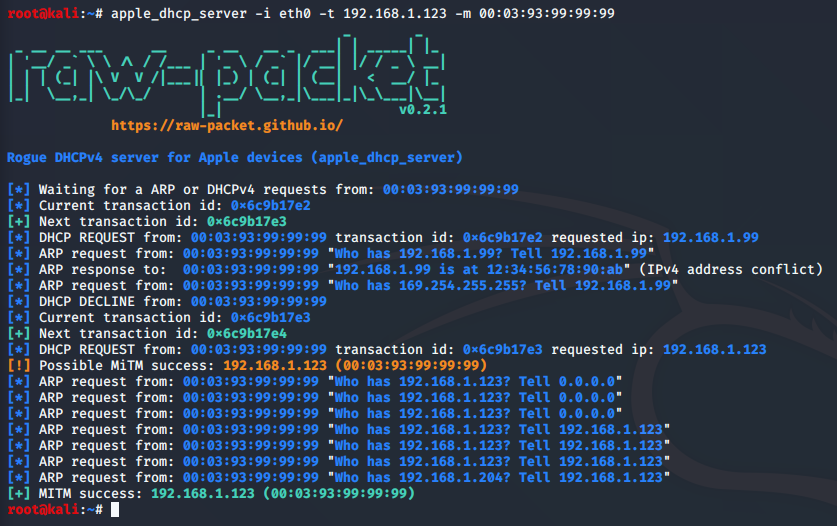 raw-packet/raw-packet
Raw-packet Project
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 niloofarkheirkhah/nili
Nili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
 androguide/dsploit
dSploit - The most complete and advanced IT security professional toolkit on Android.
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 galkan/flashlight
Pentesters spend too much time during information gathering phase. Flashlight (Fener) provides services to scan network/ports and gather information…
 ntrippar/arpwner
ARP spoofing and network packet manipulation tool for man-in-the-middle attacks, traffic interception, and LAN reconnaissance using Python and pcap.
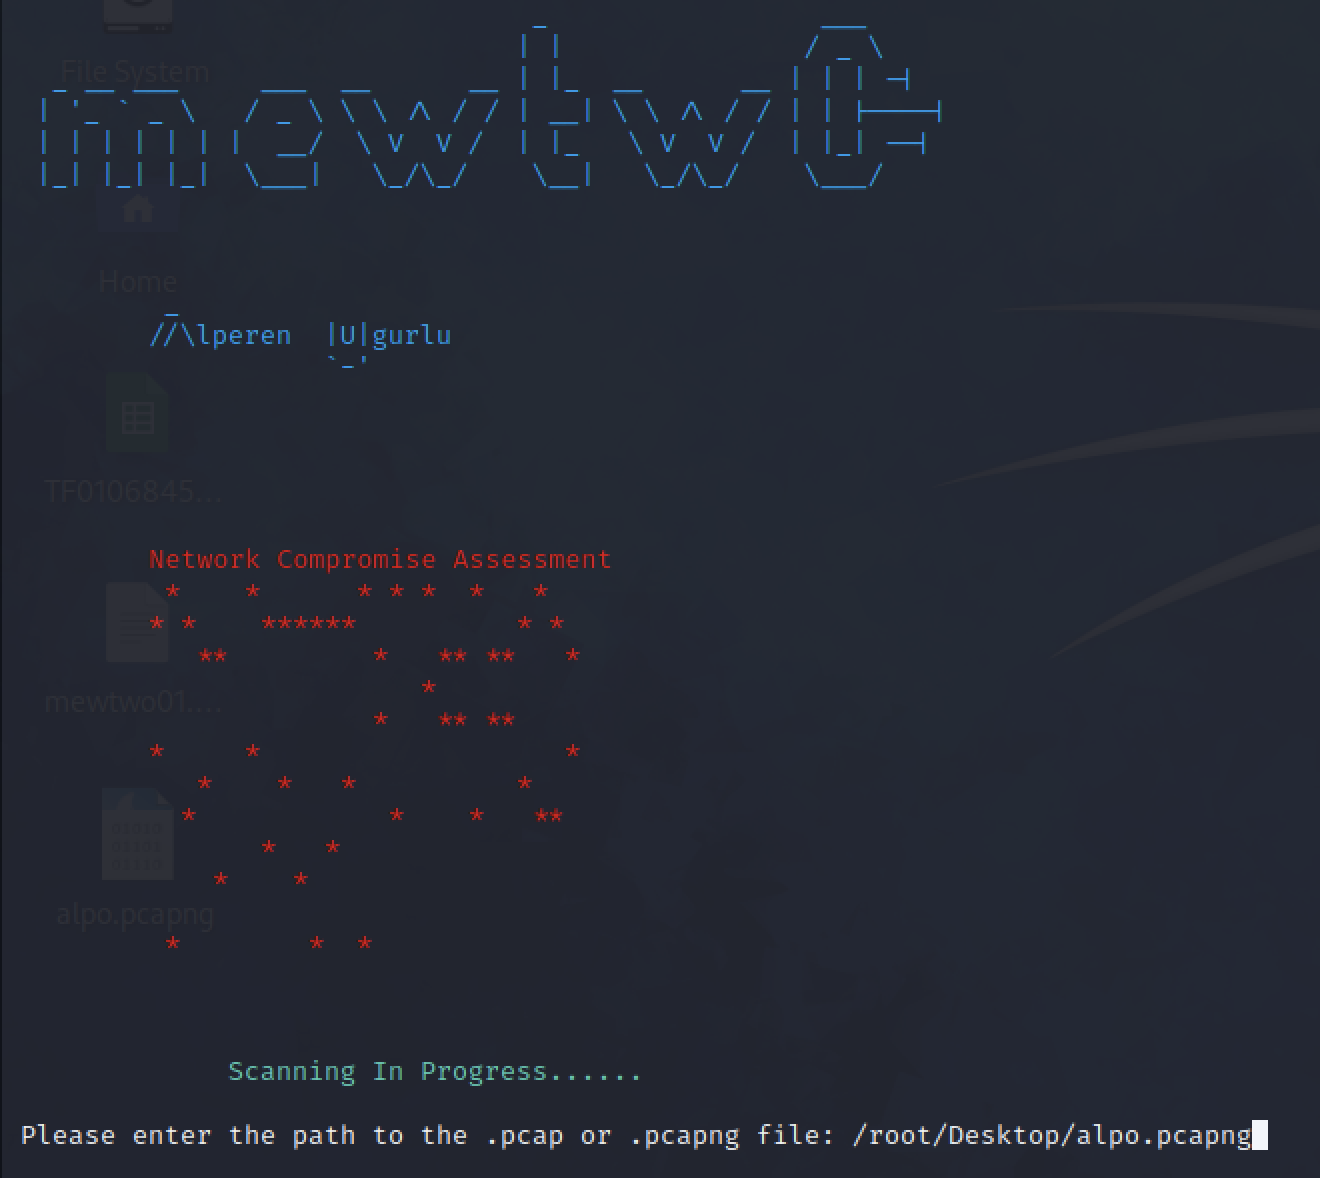 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 mhils/honeyproxy
This project is now part of @mitmproxy.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…








