
 #1
Tools for capturing, inspecting, and analyzing network traffic in real-time or from capture files.
Kitploit recommended
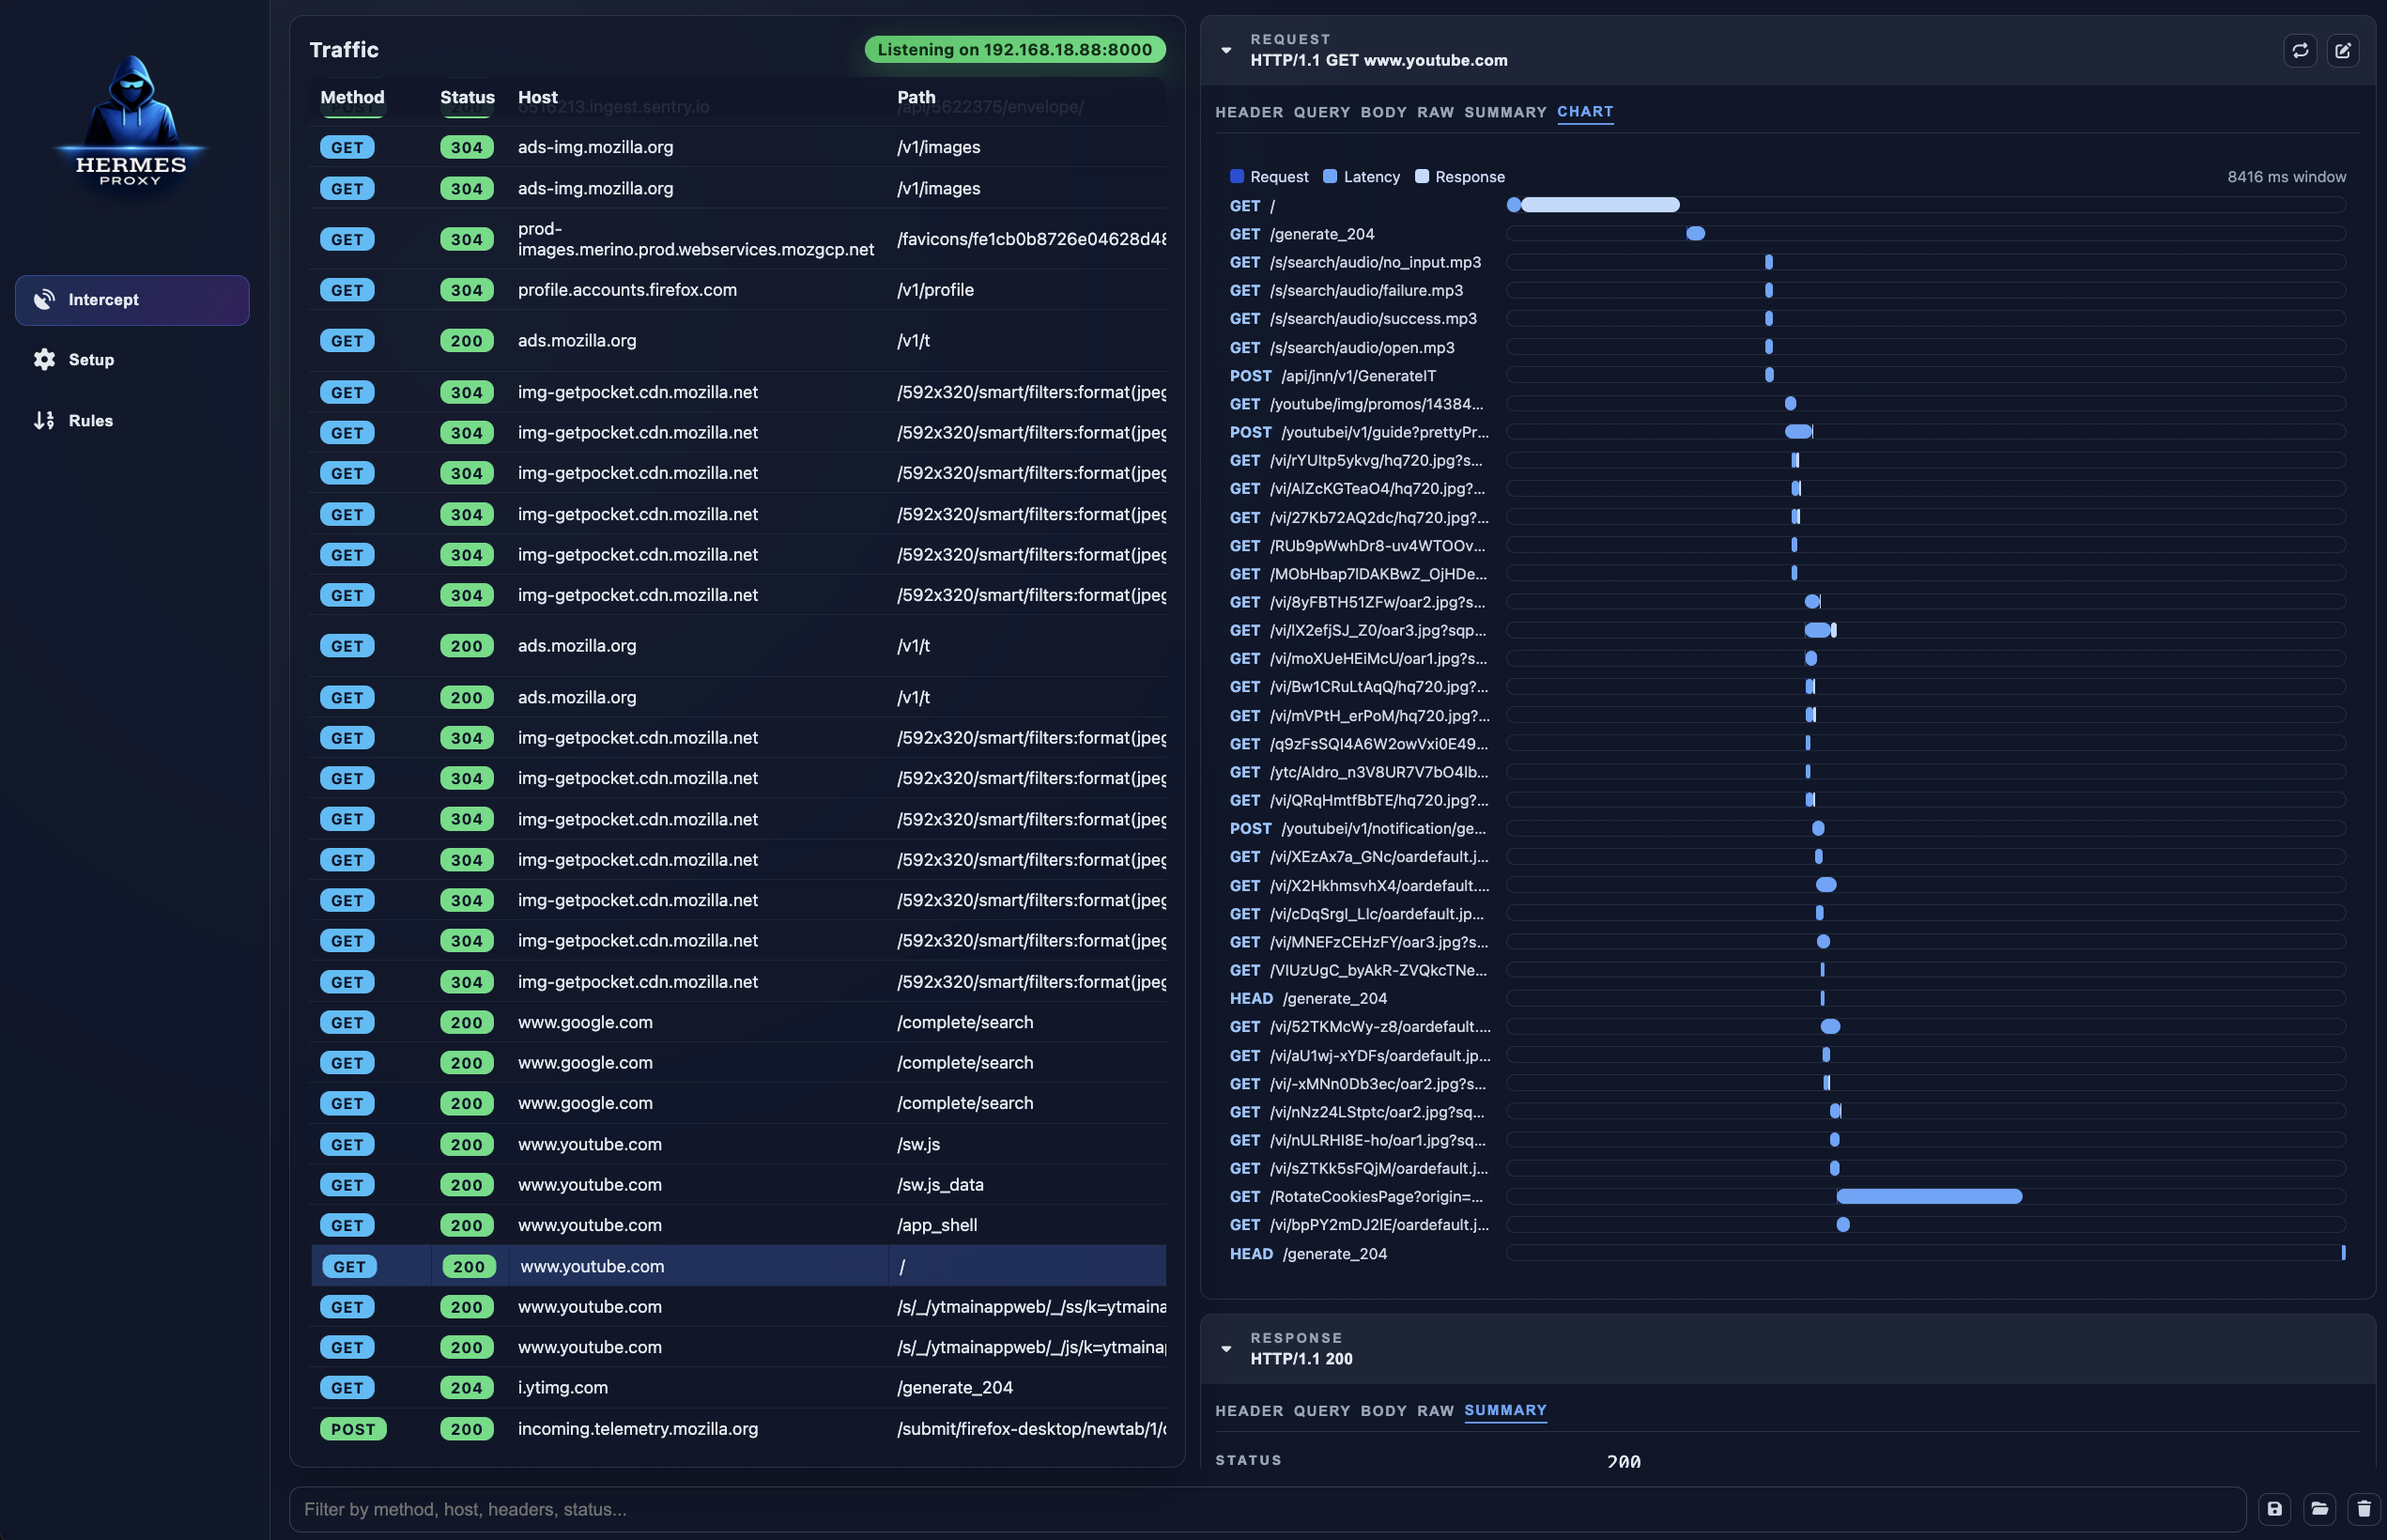
 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 mike01/pypacker
:package: The fastest and simplest packet manipulation lib for Python
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 offensive-hub/black-widow
GUI based offensive penetration testing tool (Open Source)
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
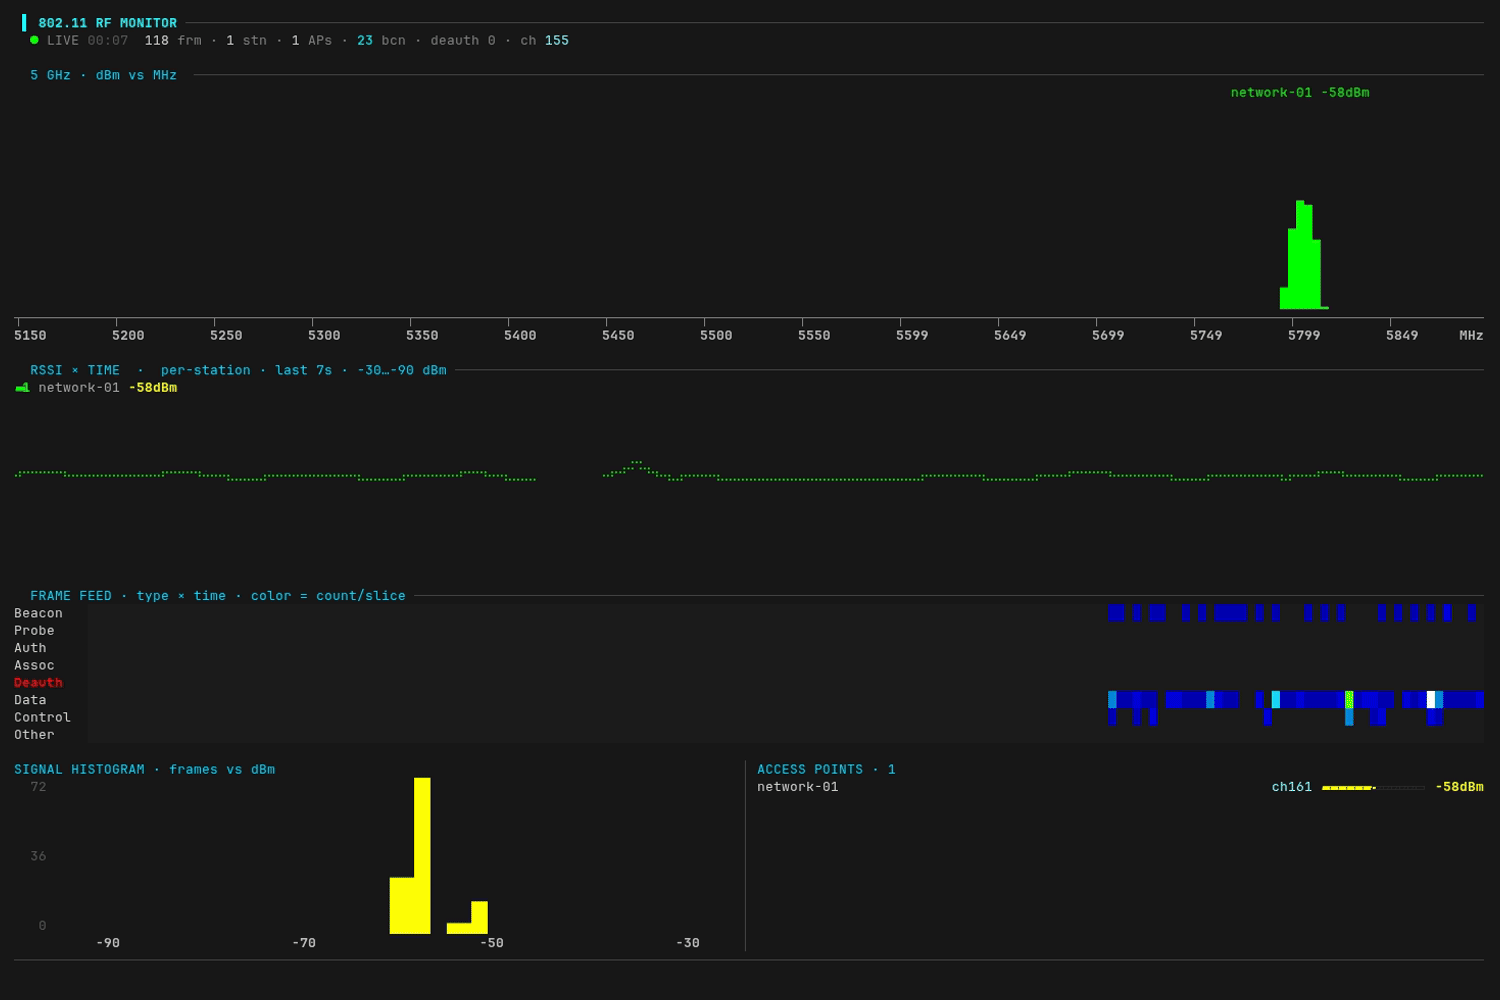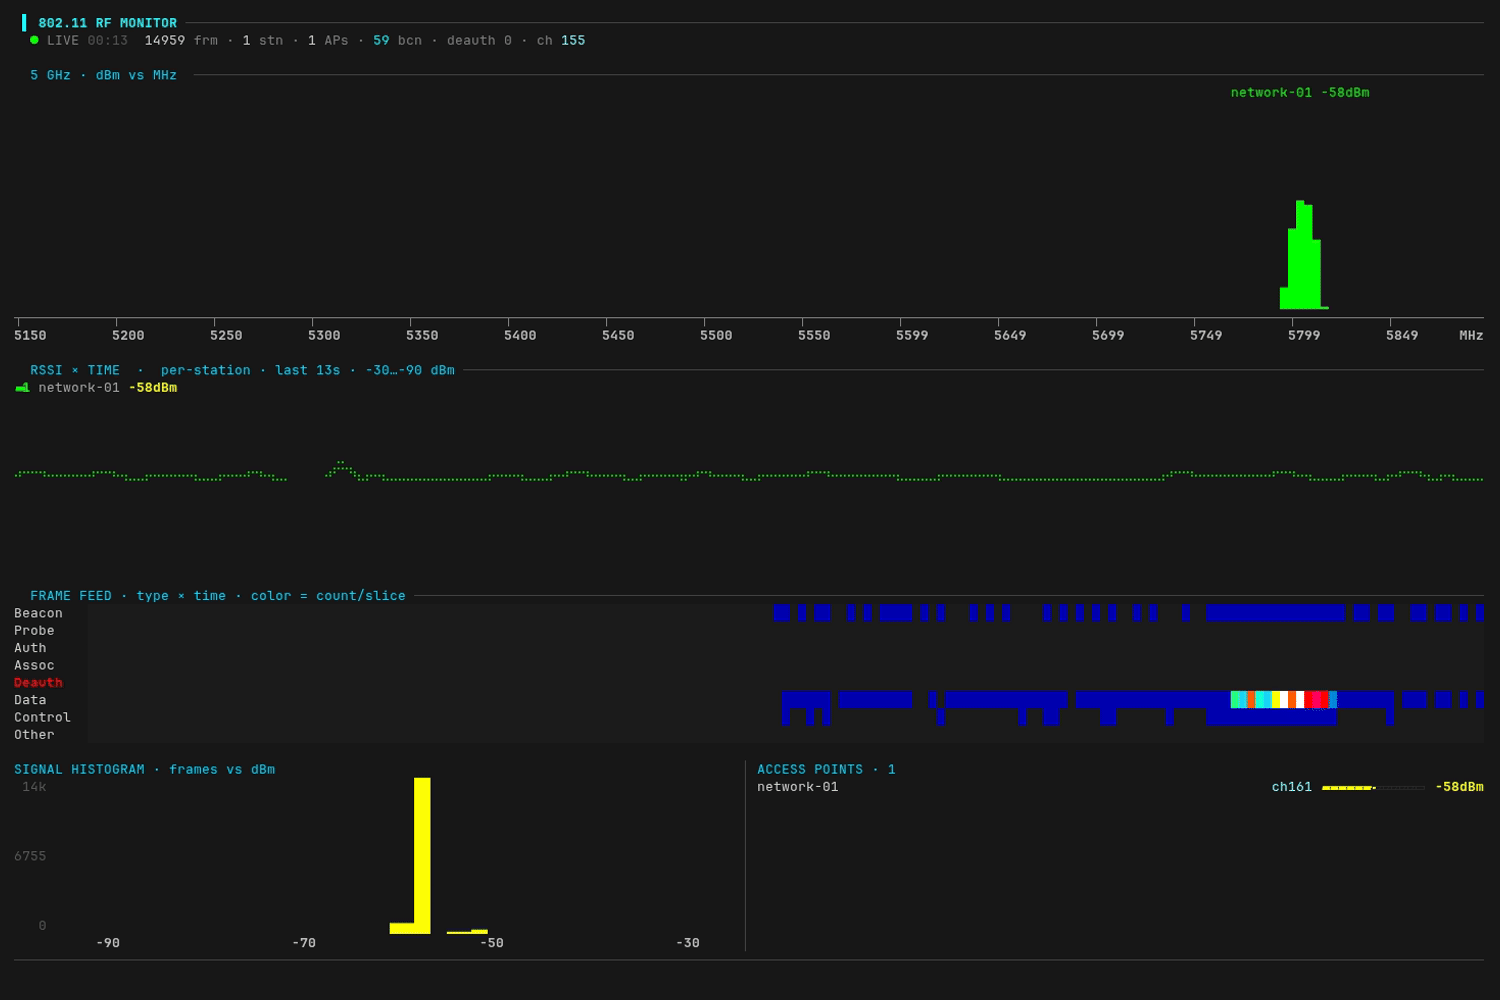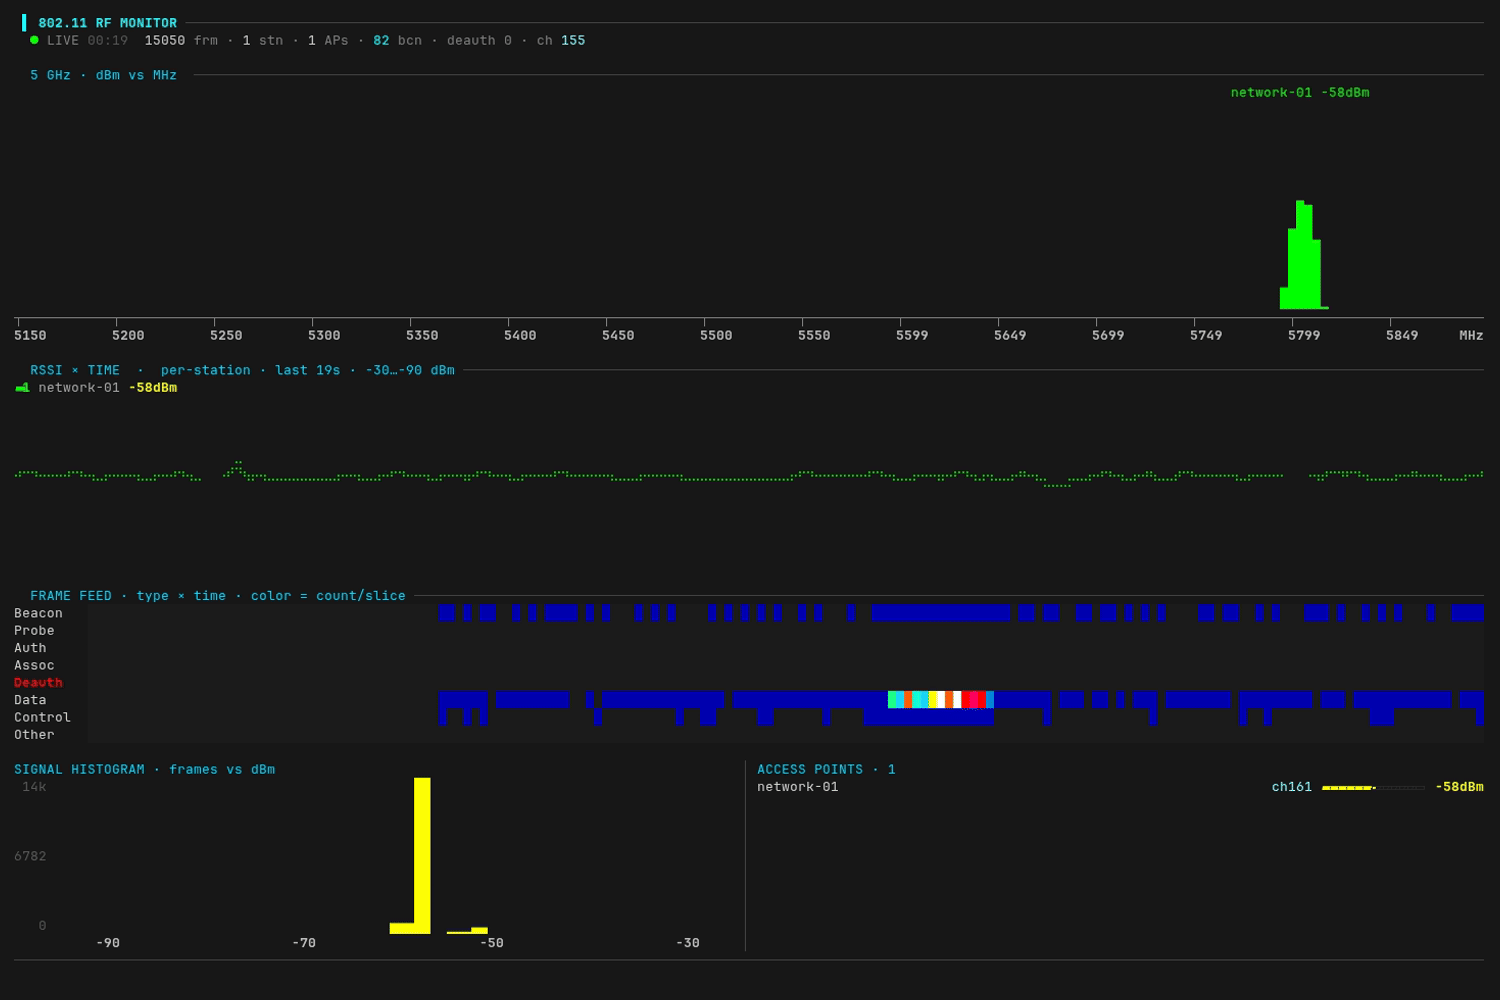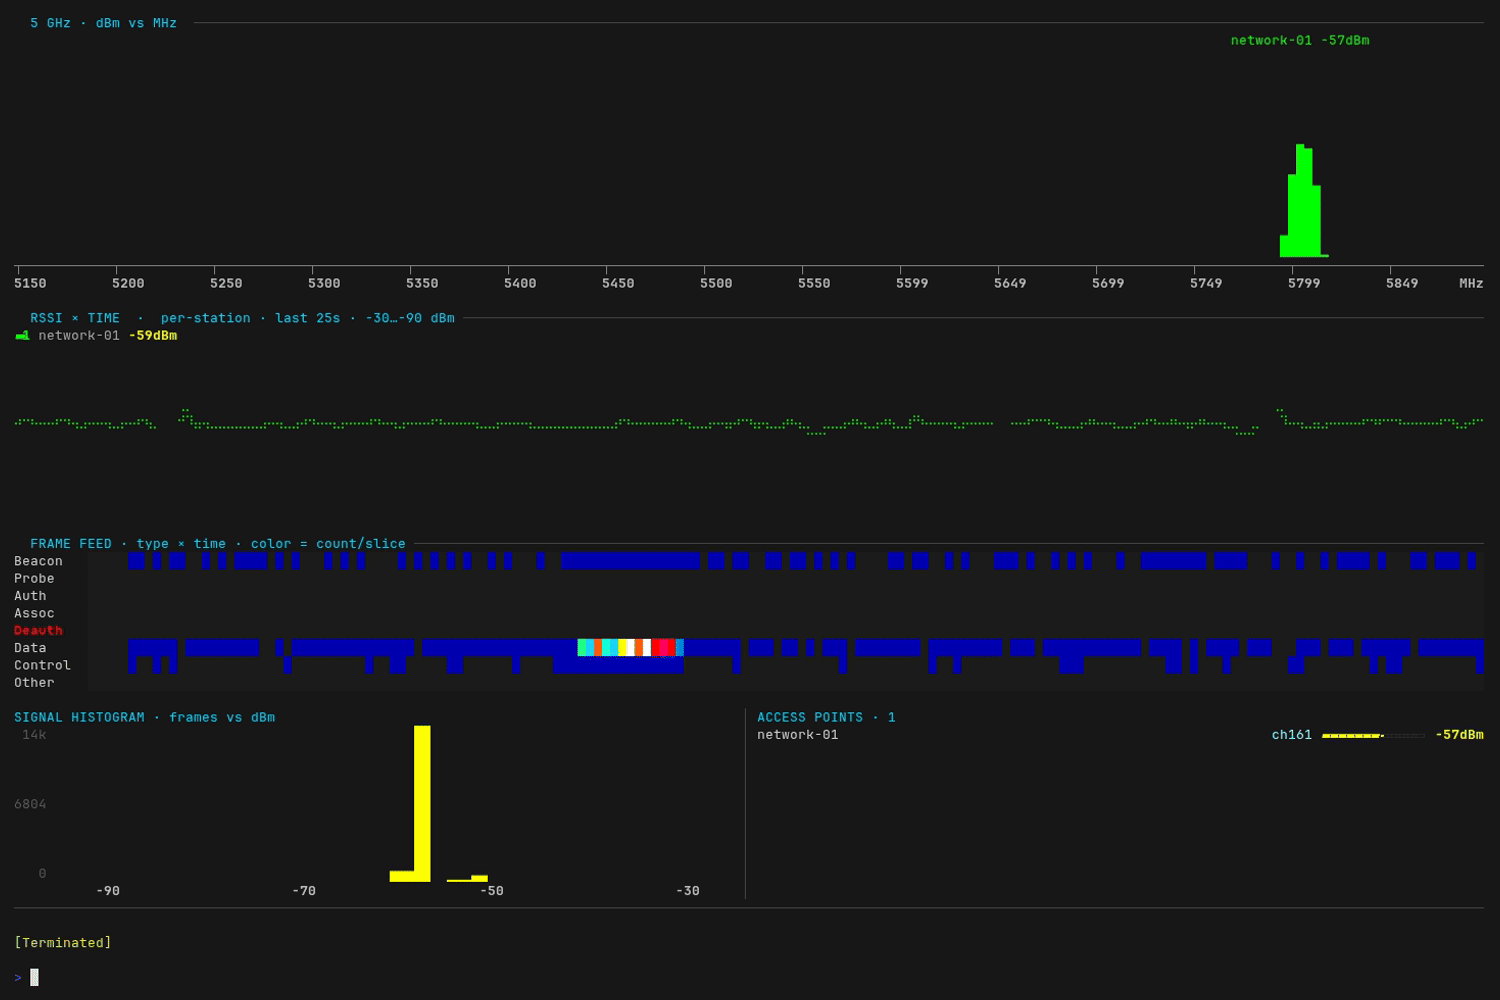 yeet-src/airtop
htop for the airwaves — a live 802.11 (Wi-Fi) RF dashboard in your terminal
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
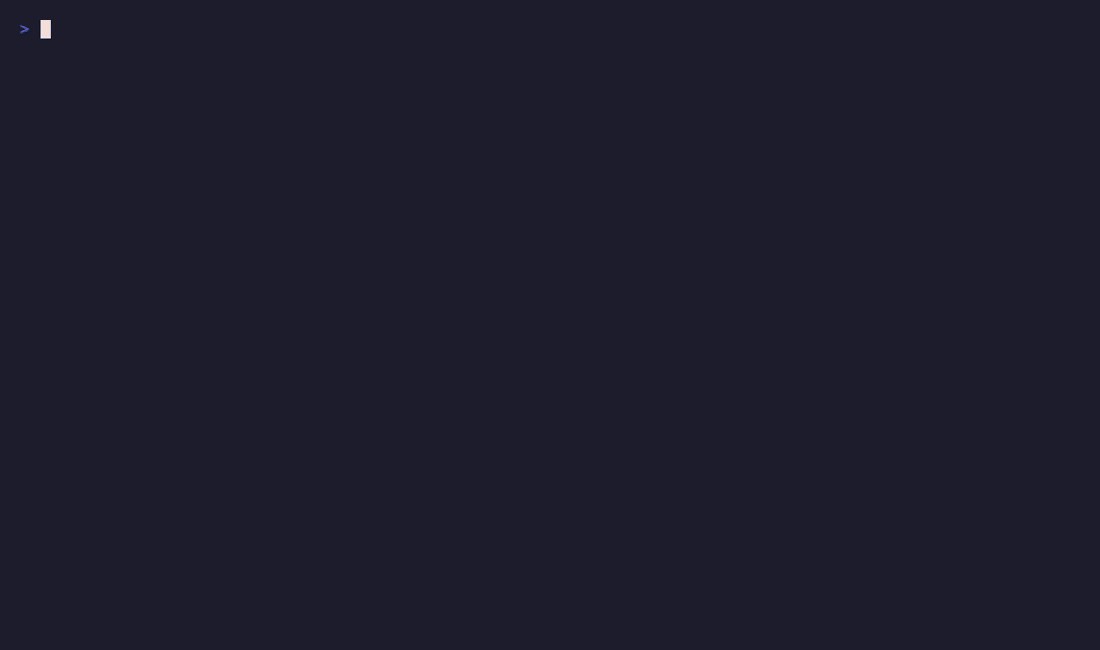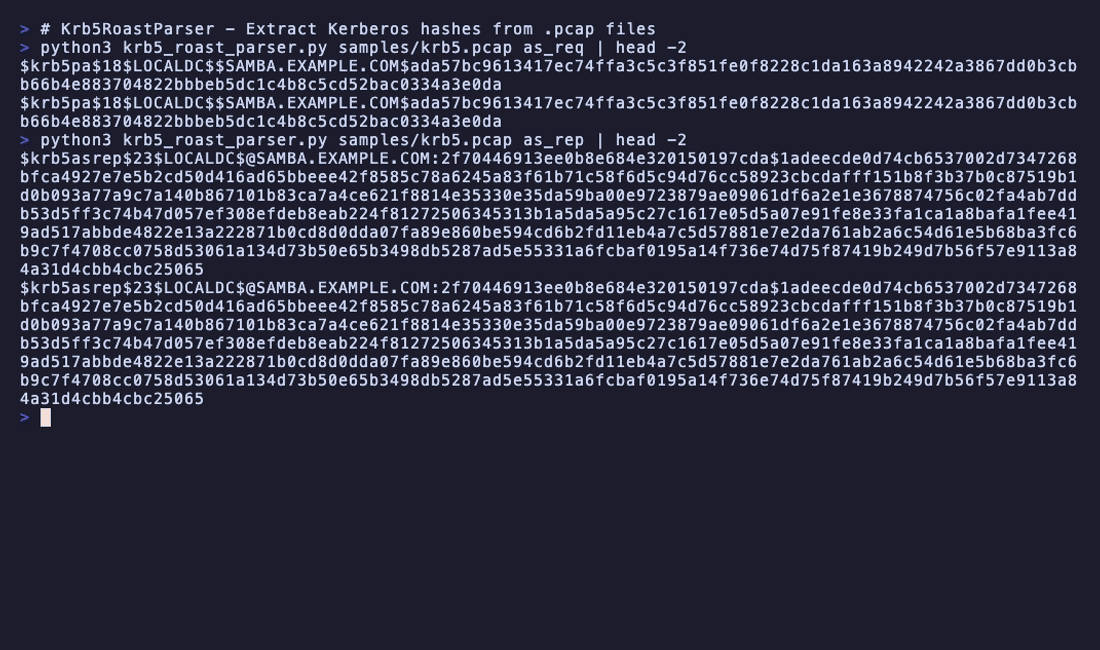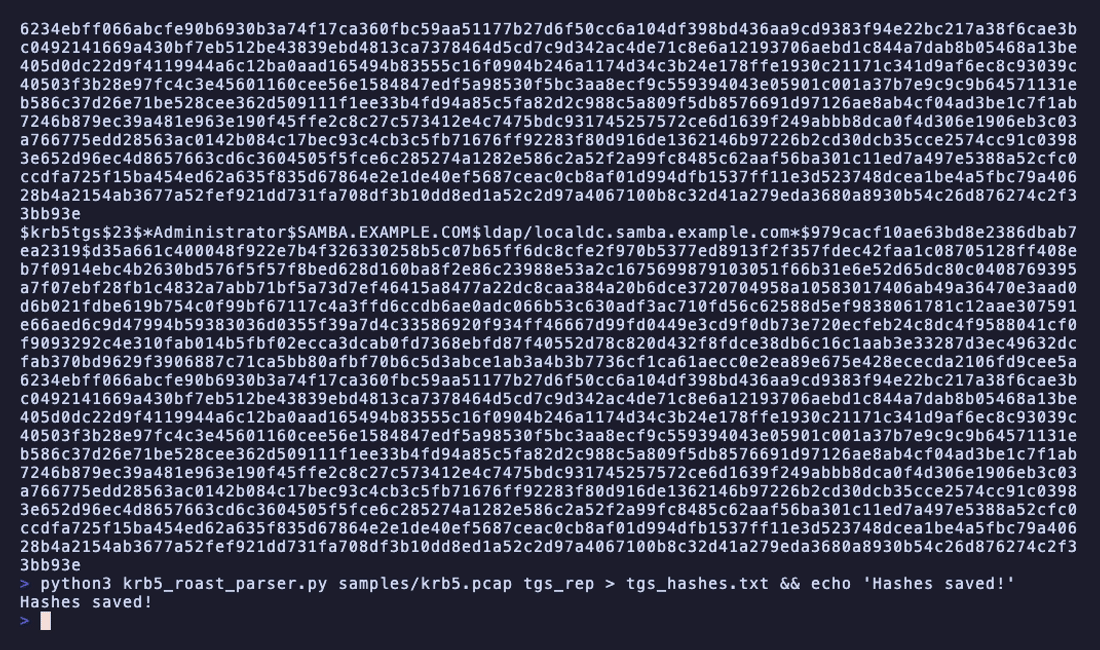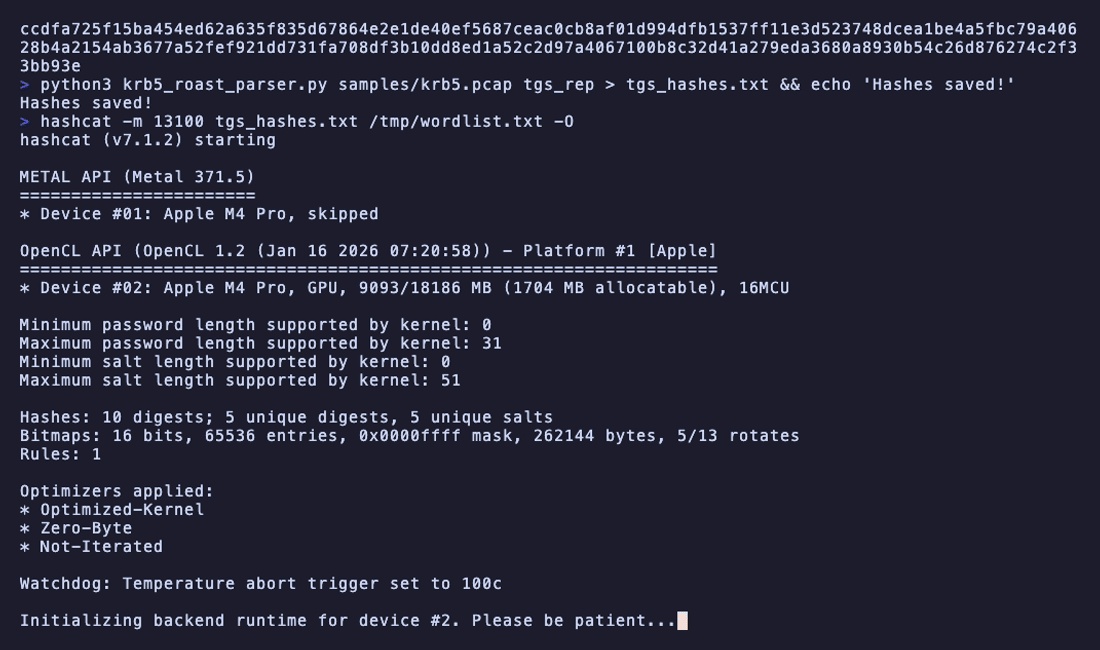 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 appneta/tcpreplay
Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
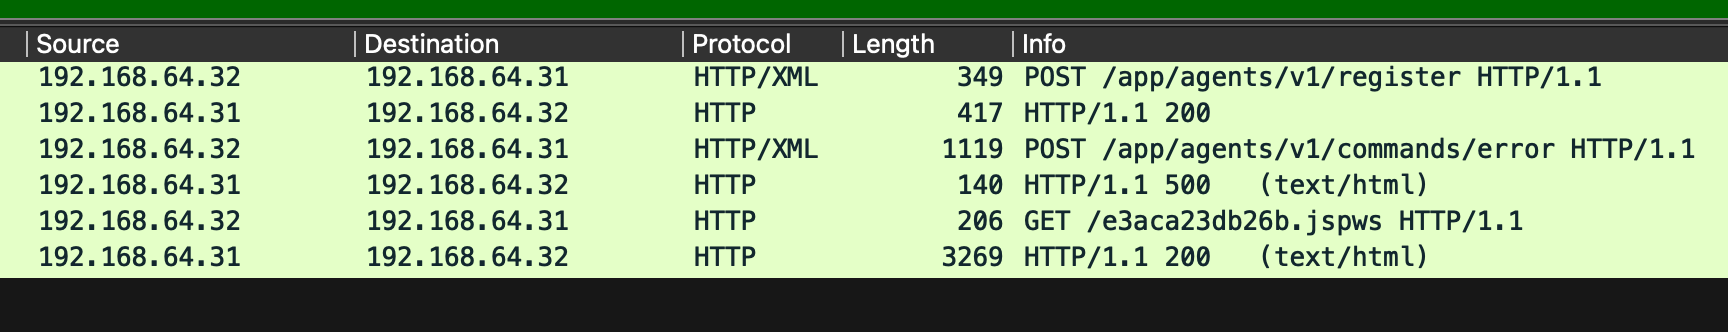 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap







