
 #1
Tools for collecting and analyzing publicly available information from online sources.
Kitploit recommended
 90n45-d3v/dbmonster
A Multitool For Tracking And Locating Nearby Devices Via Their RF Activities.
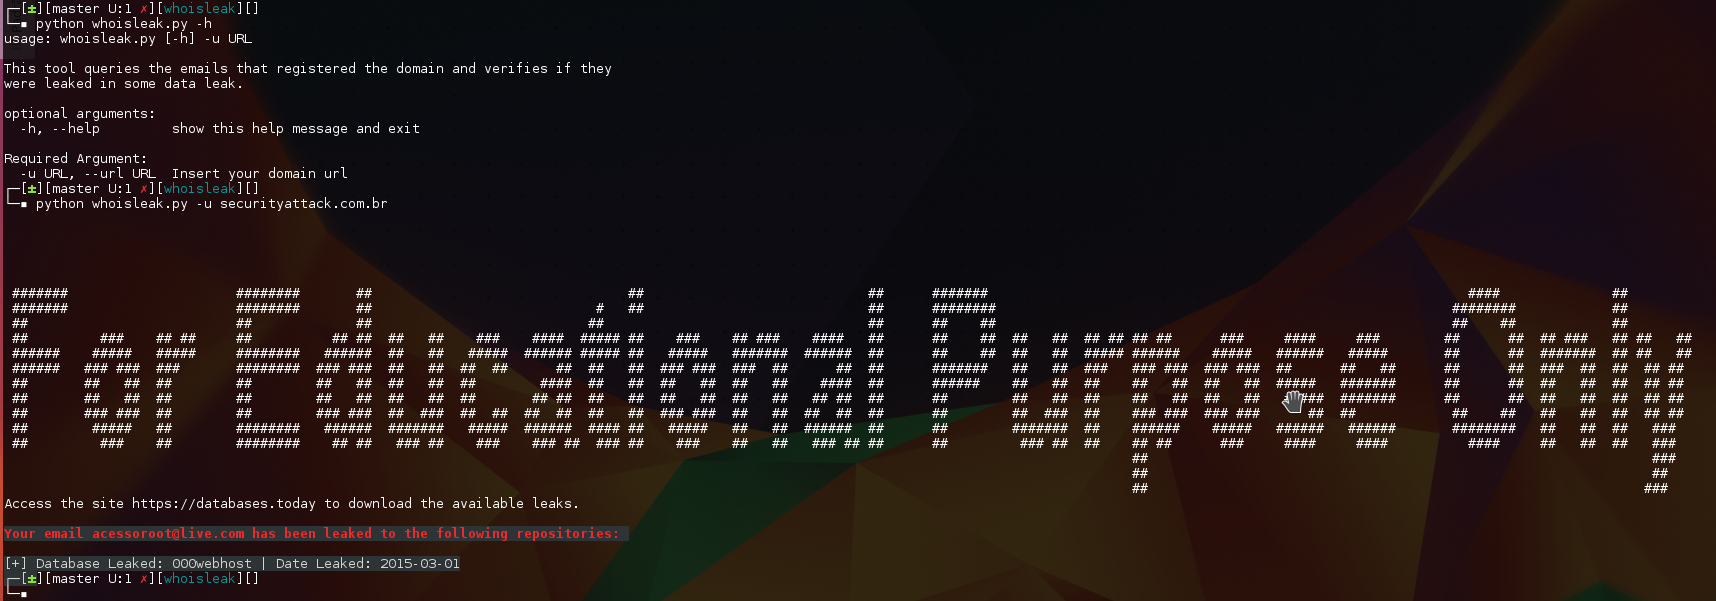 warflop/whoisleak
This tool queries the emails that registered the domain and verifies if they were leaked in some data leak.
 two06/linkedintel
LinkedIn recon the easy way
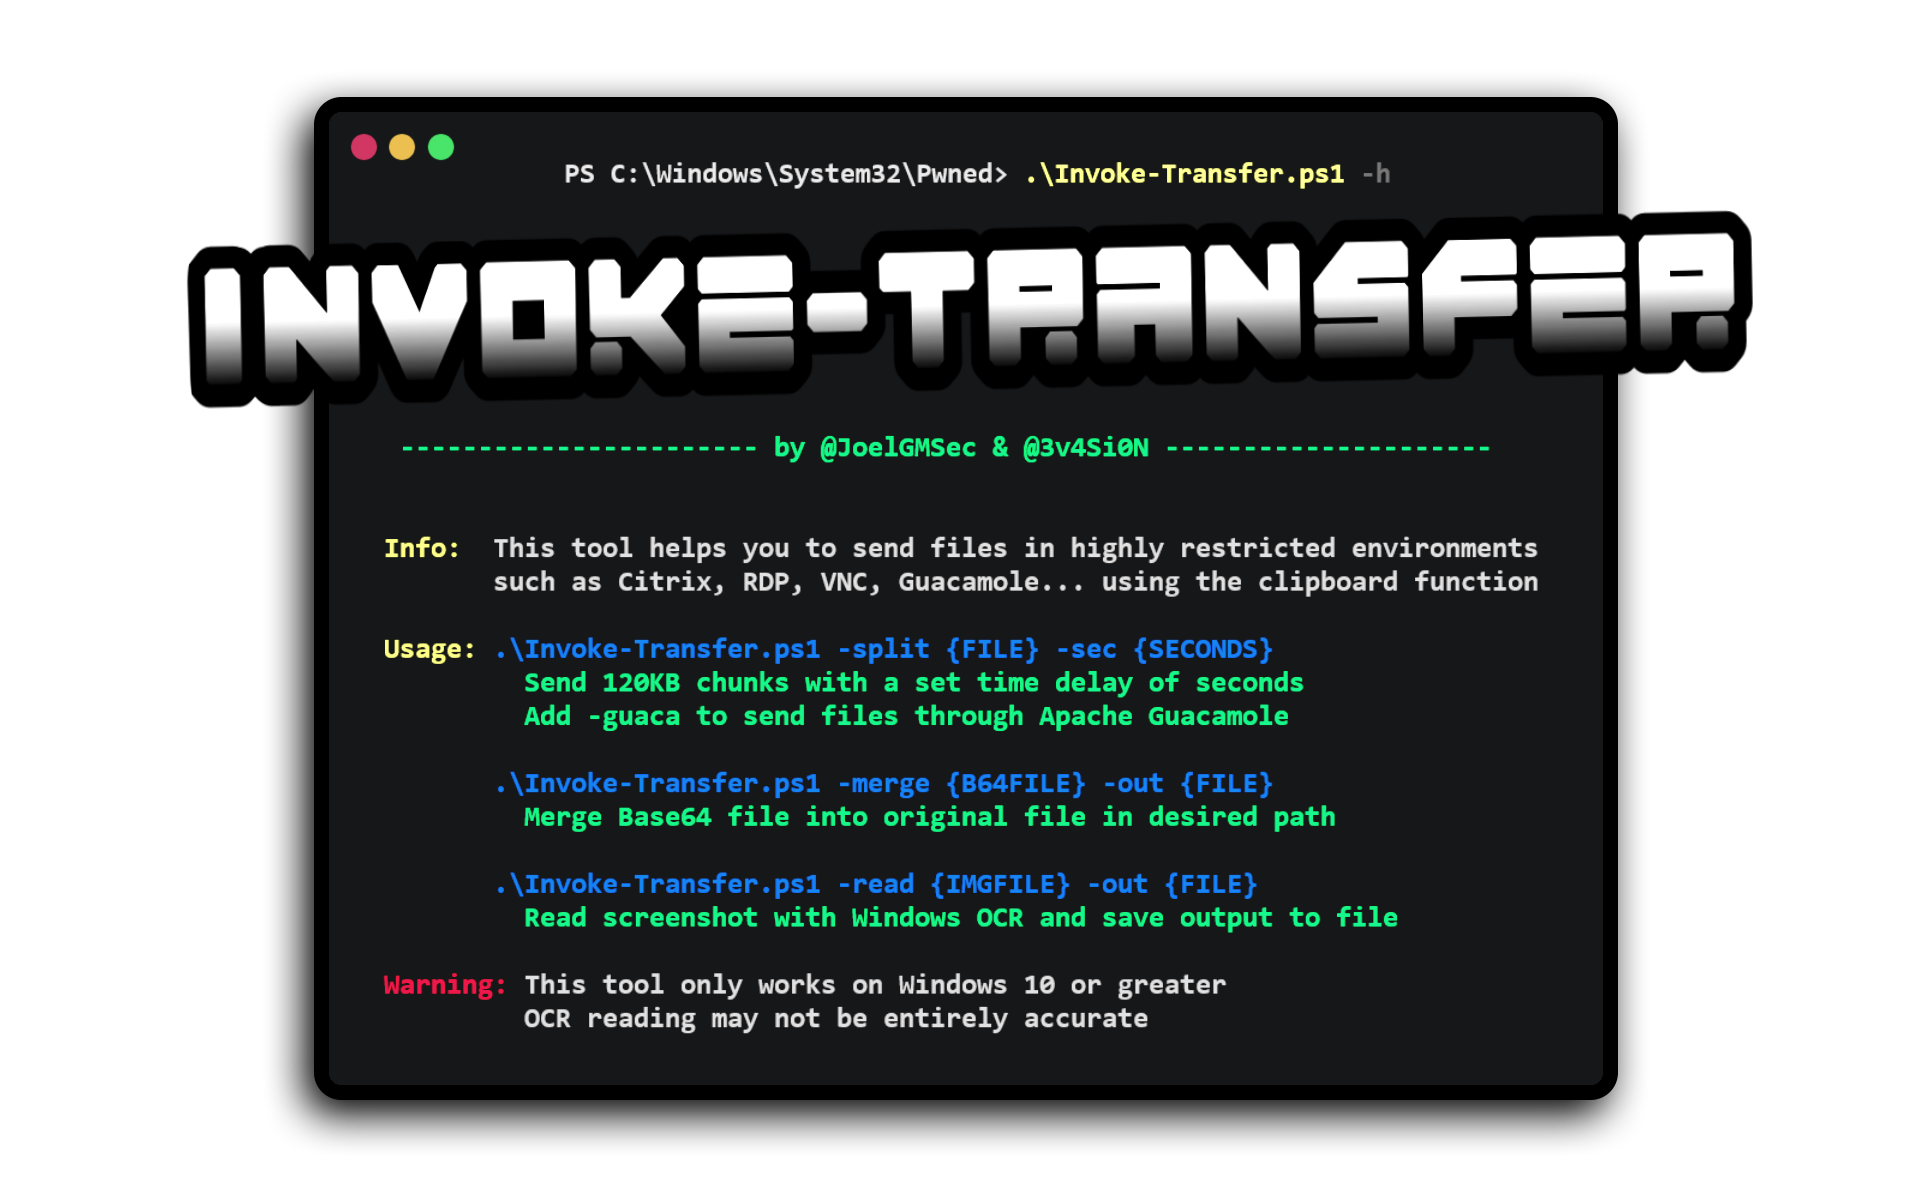 joelgmsec/invoke-transfer
PowerShell tool for transferring files in restricted environments (Citrix, RDP, VNC, Guacamole) via clipboard, Base64 chunks, keystrokes, or OCR…
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
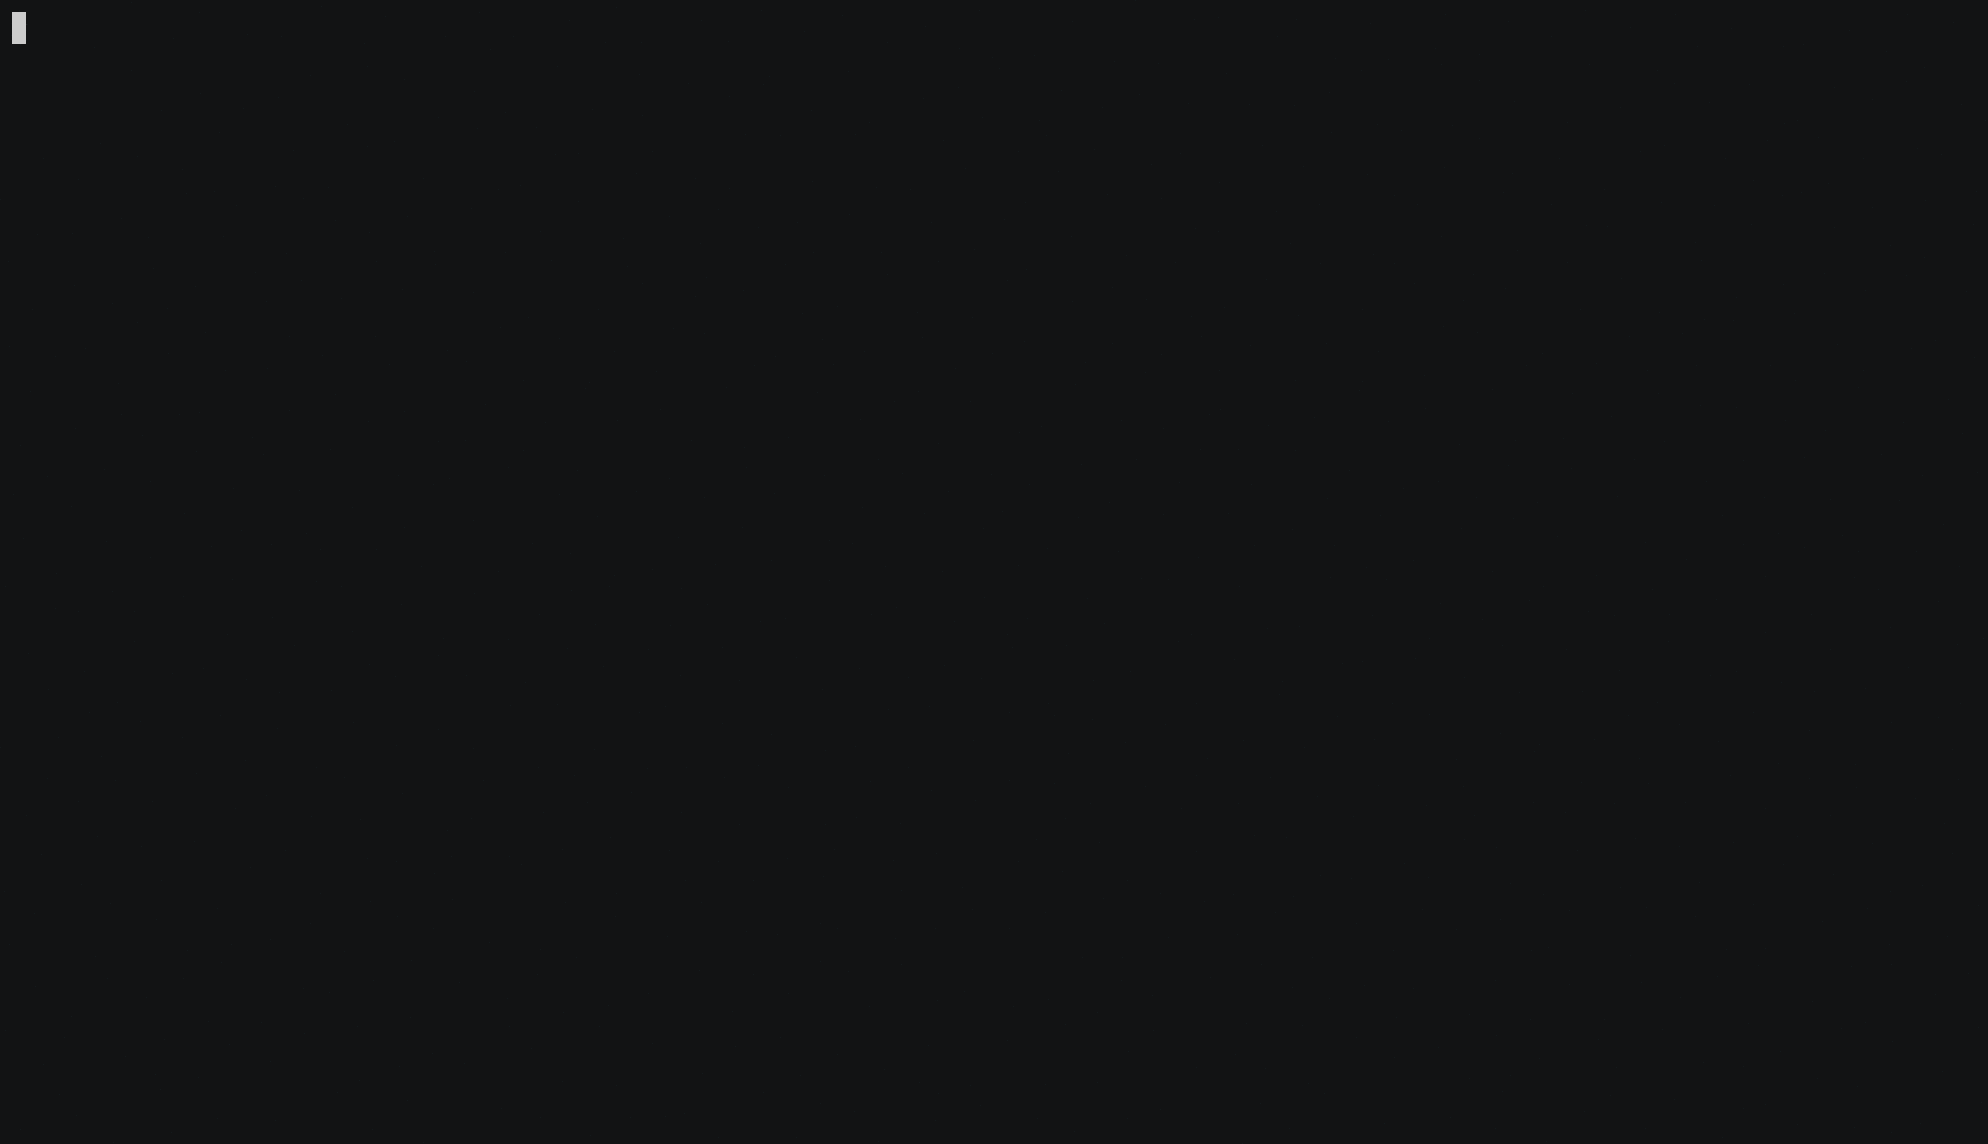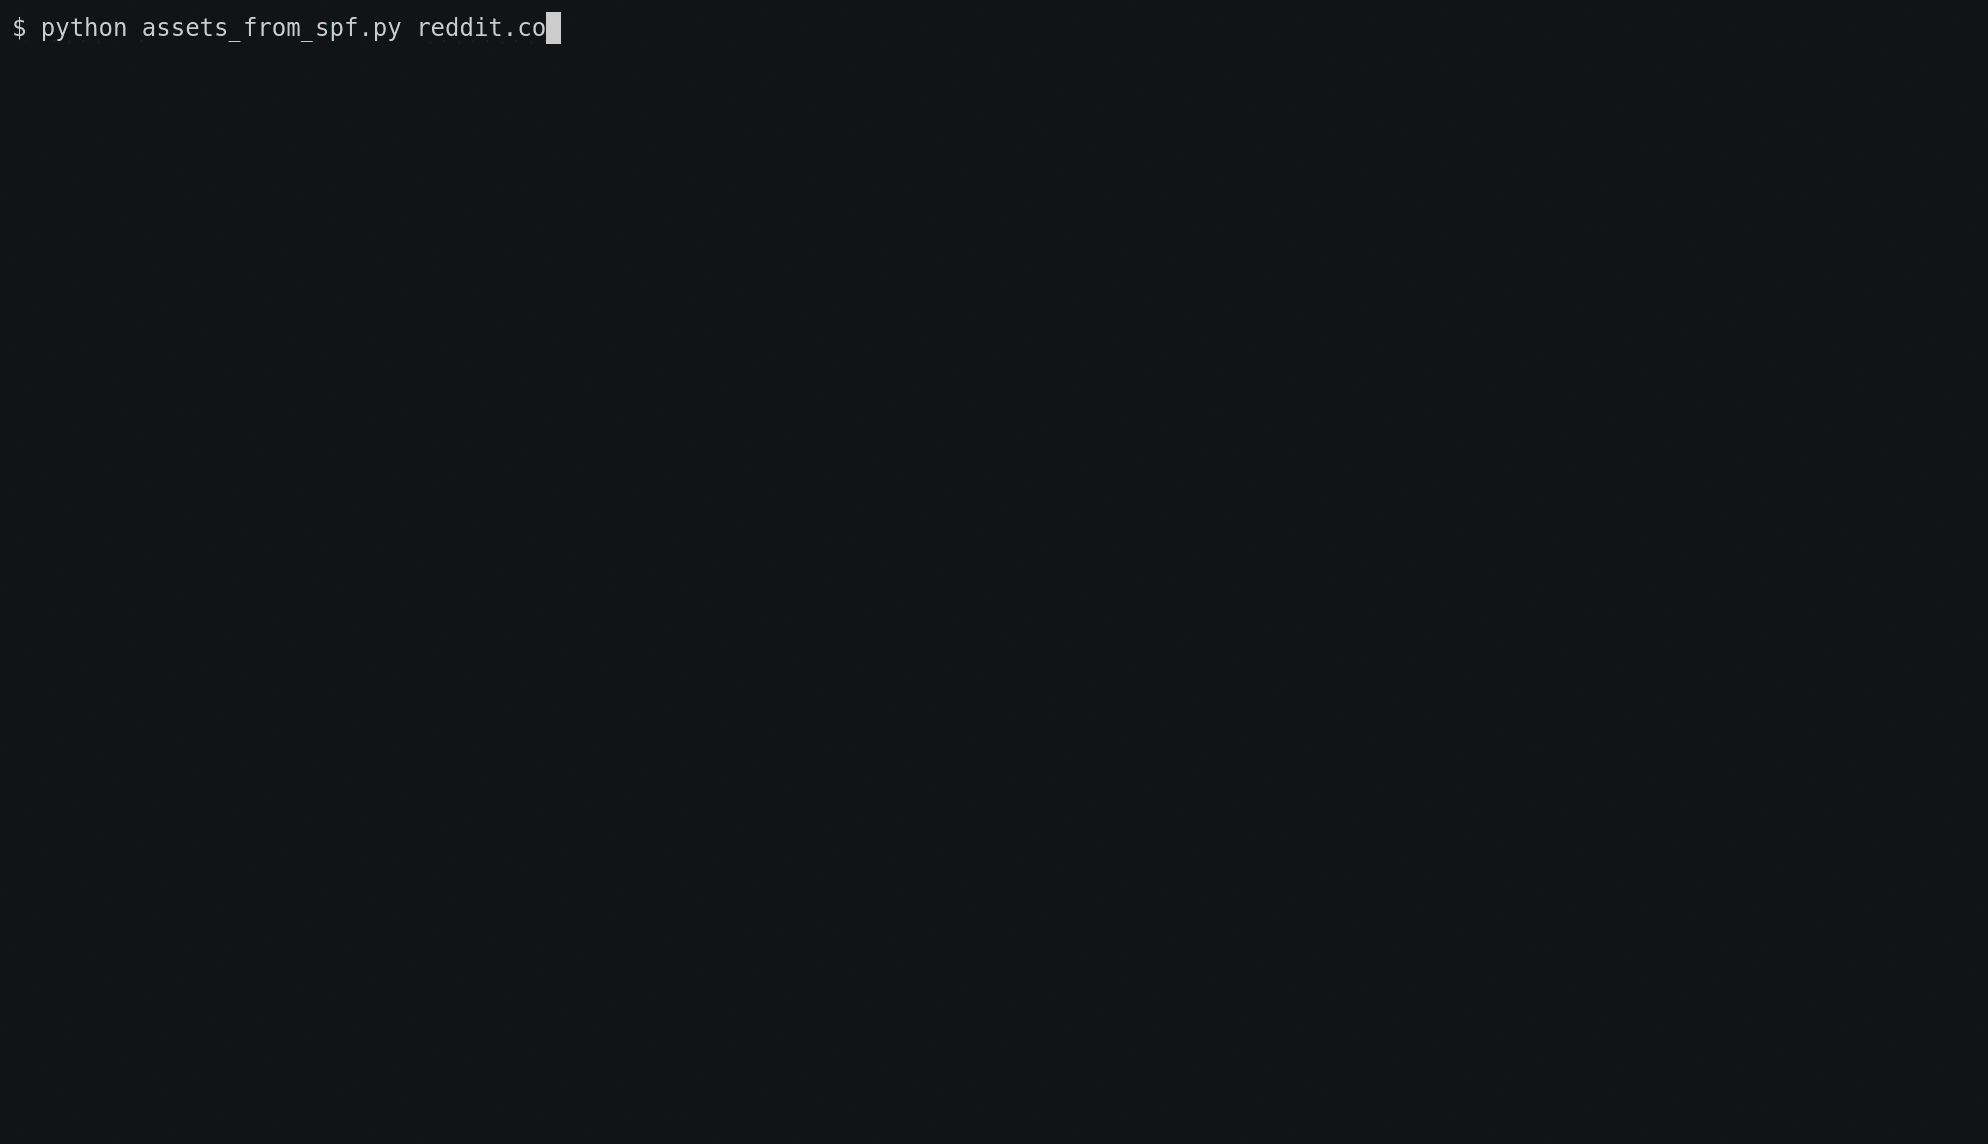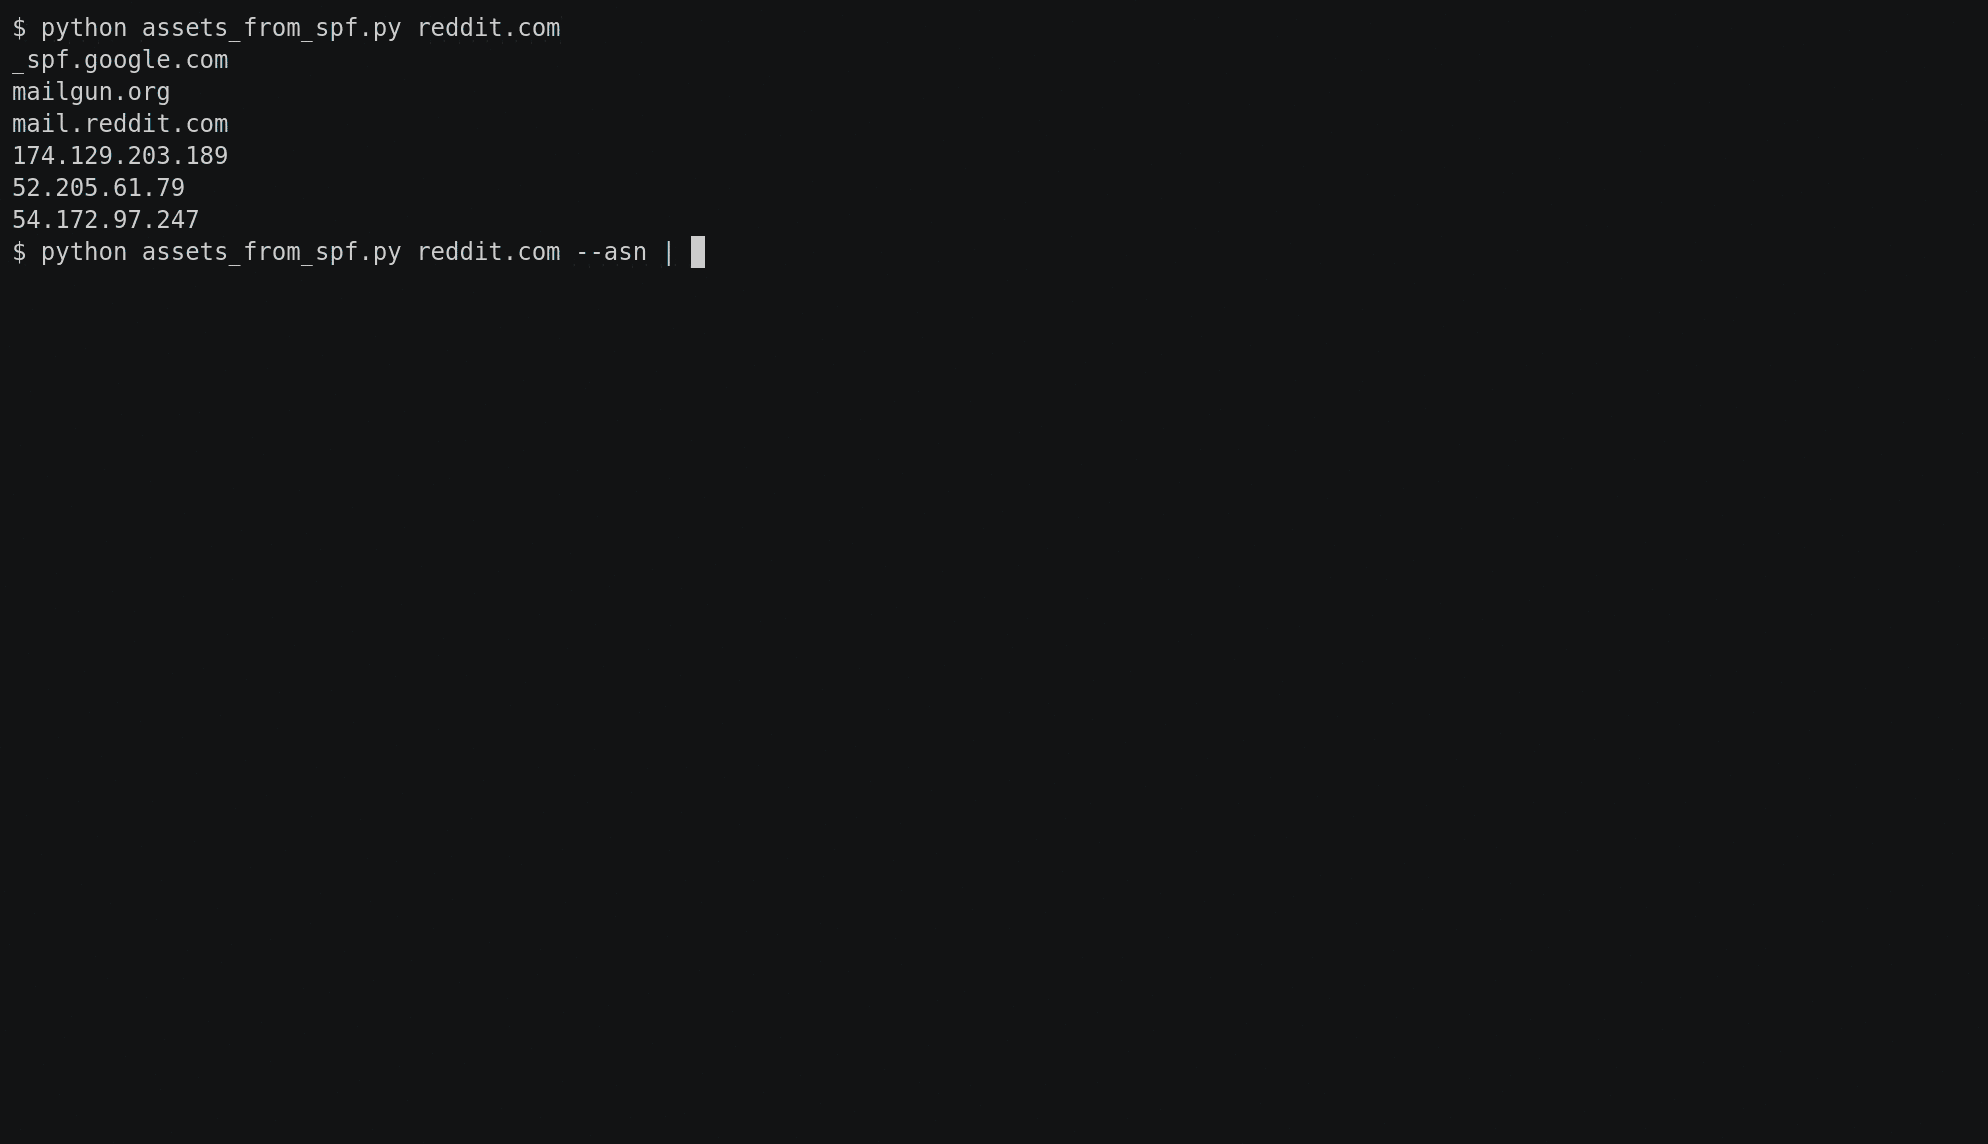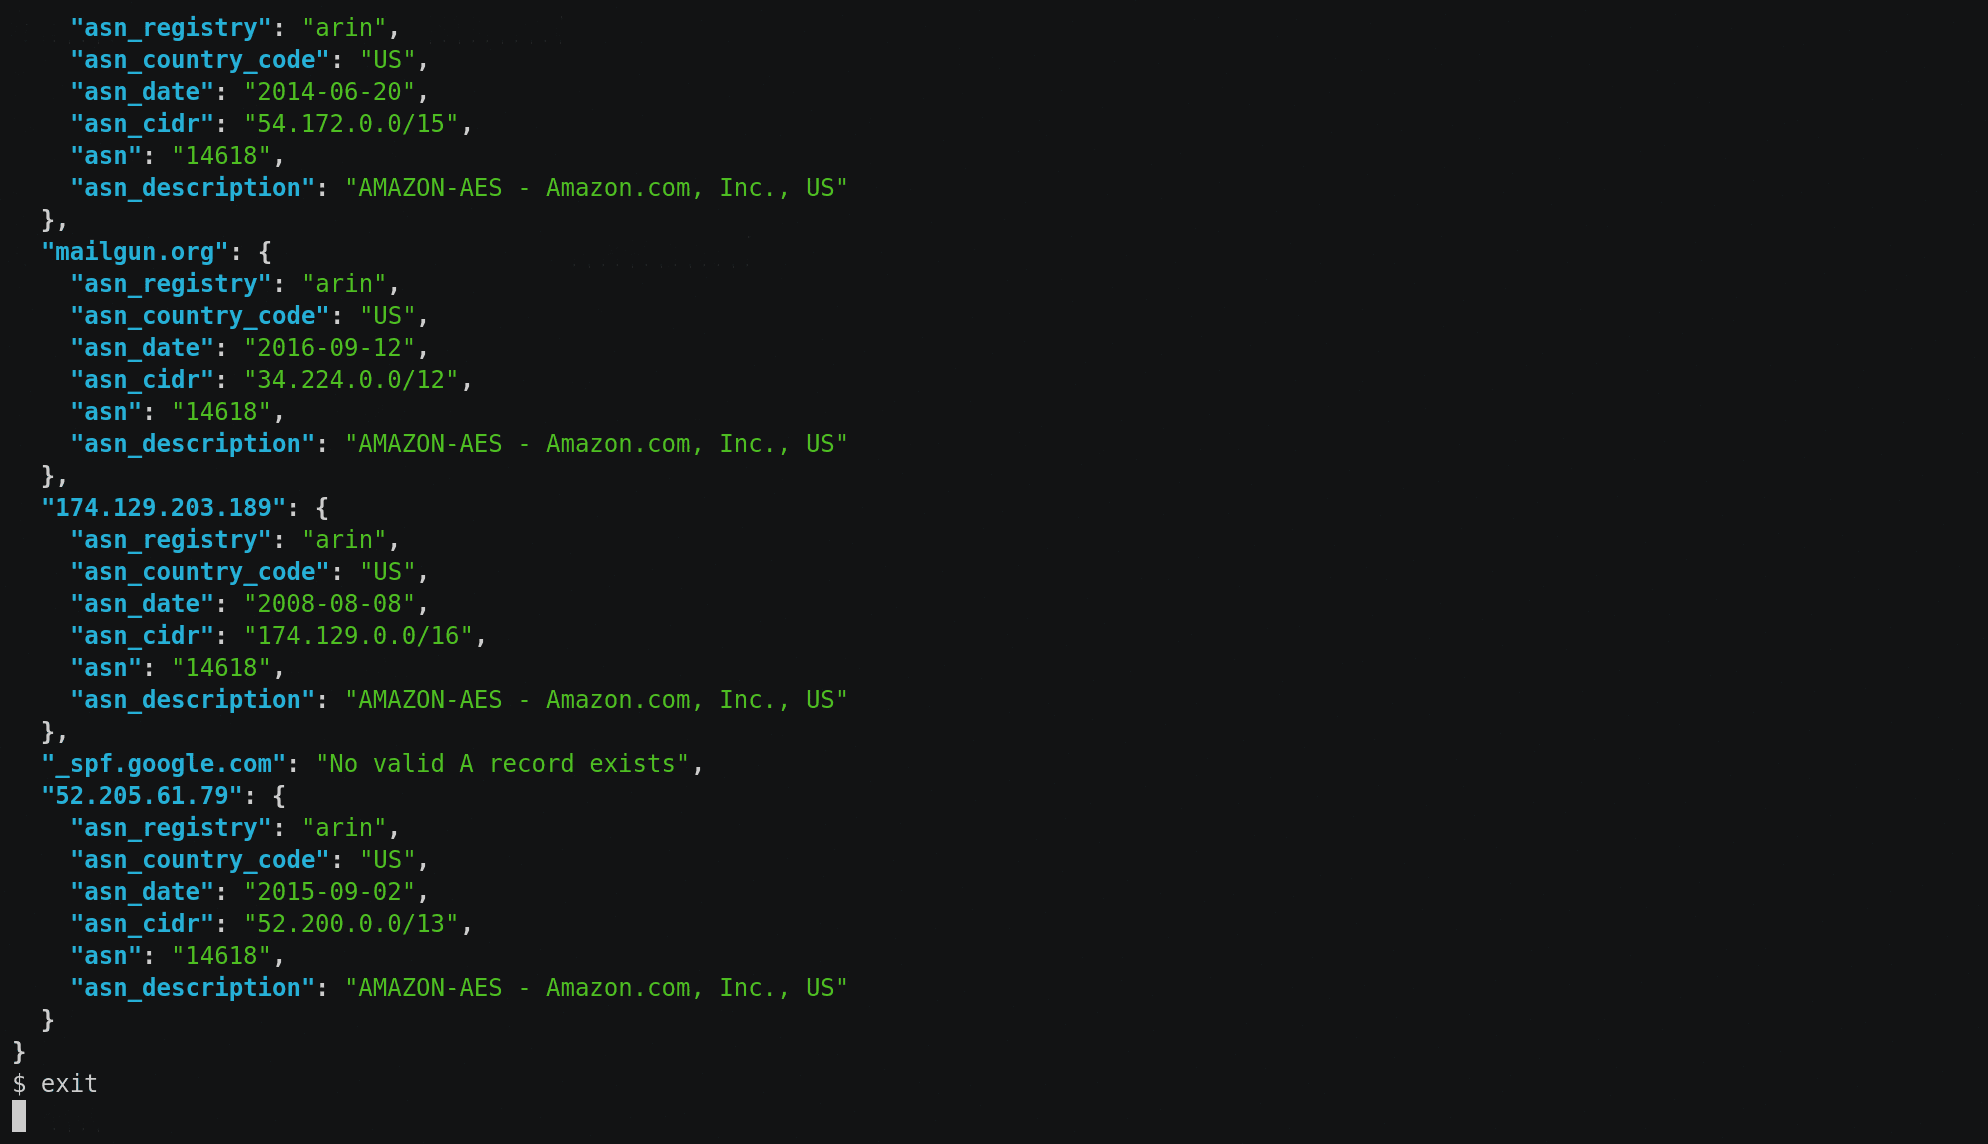 0xbharath/assets-from-spf
A Python script to parse net blocks & domain names from SPF record
 offxec/samurai
Bash-based email discovery framework that extracts email addresses using Google dork queries, company names, or domain names for OSINT reconnaissance.
 gtgalaxi/quick-lookup-ptrun
PowerToys Run plugin for instant IP, domain, and hash lookups across multiple threat intelligence platforms like Shodan, VirusTotal, and GreyNoise.
 0xbharath/slurp-old
A tool to enumerate S3 buckets manually or via certstream
 fetchfox/fetchfox
AI-powered web scraping and data extraction library that extracts structured information from any webpage using natural language instructions, with…
 coderpirata/xpl-search
Search exploits in multiple exploit databases!
 n4xh4ck5/n4xd0rk
Listing subdomains about a main domain
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 crypt0p3g/adnullenum
One-pass anonymous Active Directory enumeration over SAMR and LSARPC — null session, no credentials, with structured reusable output.
 samhaxr/sxdork
A powerful tool that utilizes the technique of google dorking to search for specific information on the internet.
 halildeniz/networksherlock
Multi-threaded port scanner with TCP/UDP support, banner grabbing, and Shodan integration for enhanced network reconnaissance and vulnerability…
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…








