
 #1
Tools for analyzing network traffic and communication logs to investigate security incidents.
Kitploit recommended
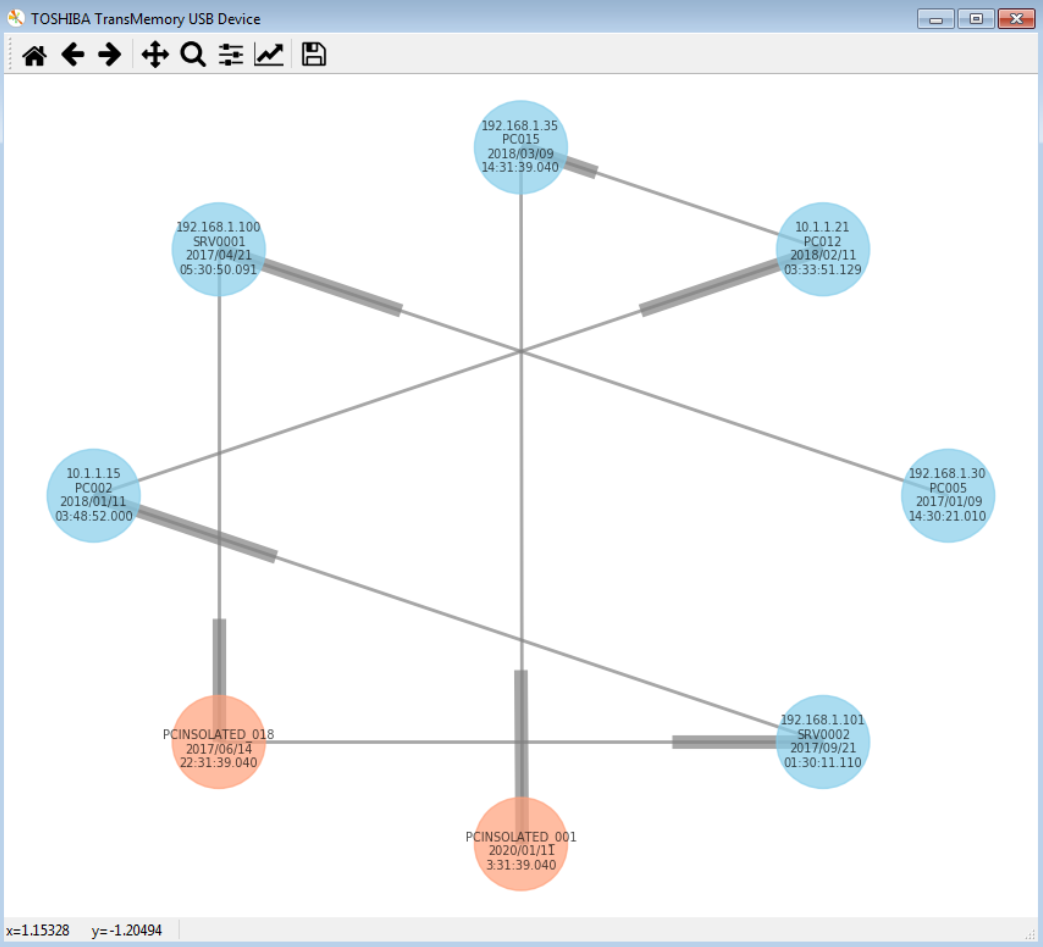
 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 cristianzsh/forensictools
Collection of forensic tools
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management








