Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Network Forensics

Tools for analyzing network traffic and communication logs to investigate security incidents.

Kitploit recommended
Top tools

10 selected
wireshark preview#1

wireshark

GitHubwireshark/wireshark
9.9k19 hours ago
zeek preview#2

zeek

GitHubzeek/zeek
7.8k3 days ago
arkime preview#3

arkime

GitHubarkime/arkime
7.4k21h 32m ago
Malcolm preview#4

Malcolm

GitHubcisagov/malcolm
2.5k1 month ago
suricata preview#5

suricata

GitHuboisf/suricata
6.5k6 days ago
ntopng preview#7

ntopng

GitHubntop/ntopng
8.1k18h 12m ago
scapy preview#8

scapy

GitHubsecdev/scapy
12.5k1 day ago
etl2pcapng preview#10

etl2pcapng

GitHubmicrosoft/etl2pcapng
7351 year ago
netsniff-ng preview#11

netsniff-ng

GitHubnetsniff-ng/netsniff-ng
1.4k1 year ago
gopacket preview#13

gopacket

GitHubgoogle/gopacket
6.8k1 year ago
NewestRelevanceMost popularRecently updated
140 results
pyshark preview

pyshark

GitHubkiminewt/pyshark

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
packet-sniffing-analysiswi-fi-auditingencryption-decryption-tools+5
2.5k6 months ago
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
packet-sniffing-analysisnetwork-forensicsthreat-intelligence
6844 years ago
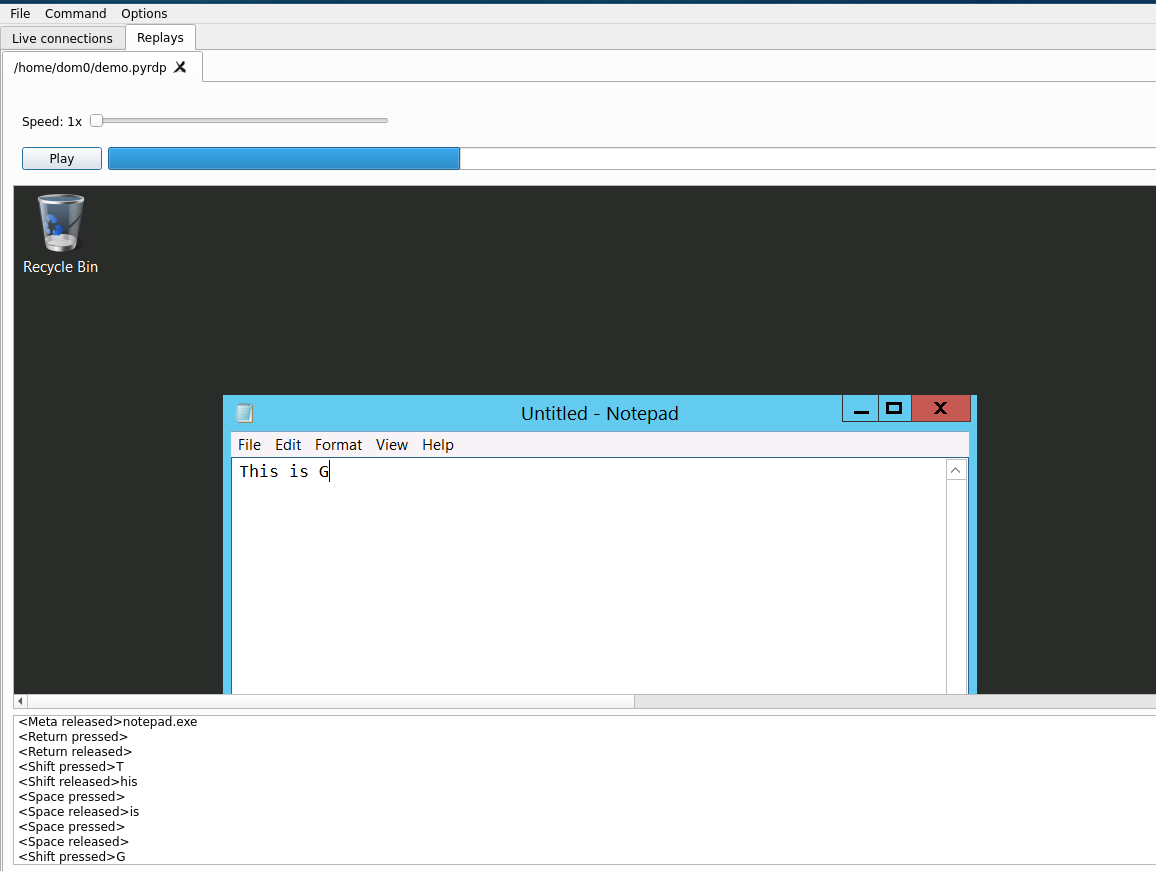
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact

exploitationnetwork-forensicsinformation-gathering+9
1.8k4 months ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
defensive-toolspacket-sniffing-analysisnetwork-mapping+14
7.8k3 days ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

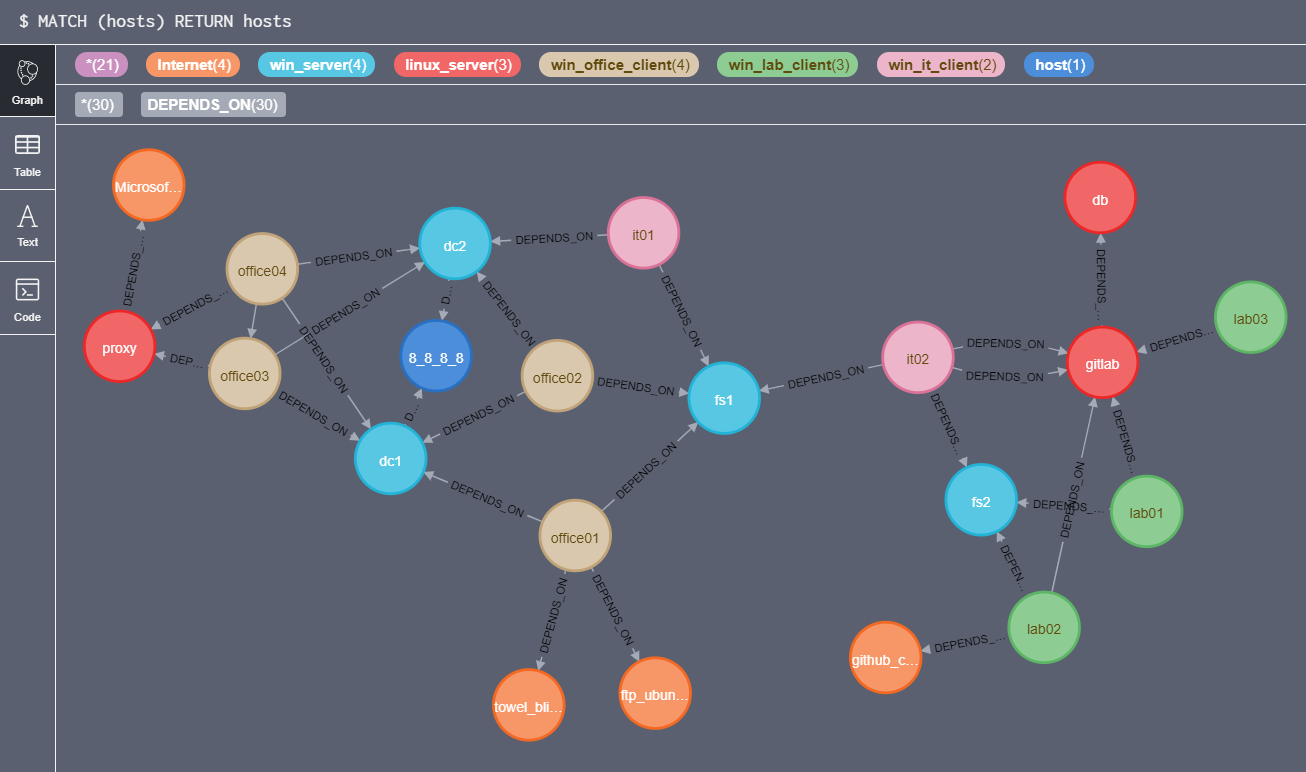
create cypher create statements for neo4j out of netstat files from multiple machines
network-forensicsinformation-gatheringlog-analysis
415 years ago
pcapinator preview

pcapinator

GitHubmspicer/pcapinator

A tool for processing a lot of pcaps using tshark

packet-sniffing-analysiswi-fi-auditingnetwork-forensics+2
1552 years ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
packet-sniffing-analysisnetwork-forensicsforensics+2
7351 year ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
disk-forensicsosintdynamic-analysis-sandboxing+7
232 months ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

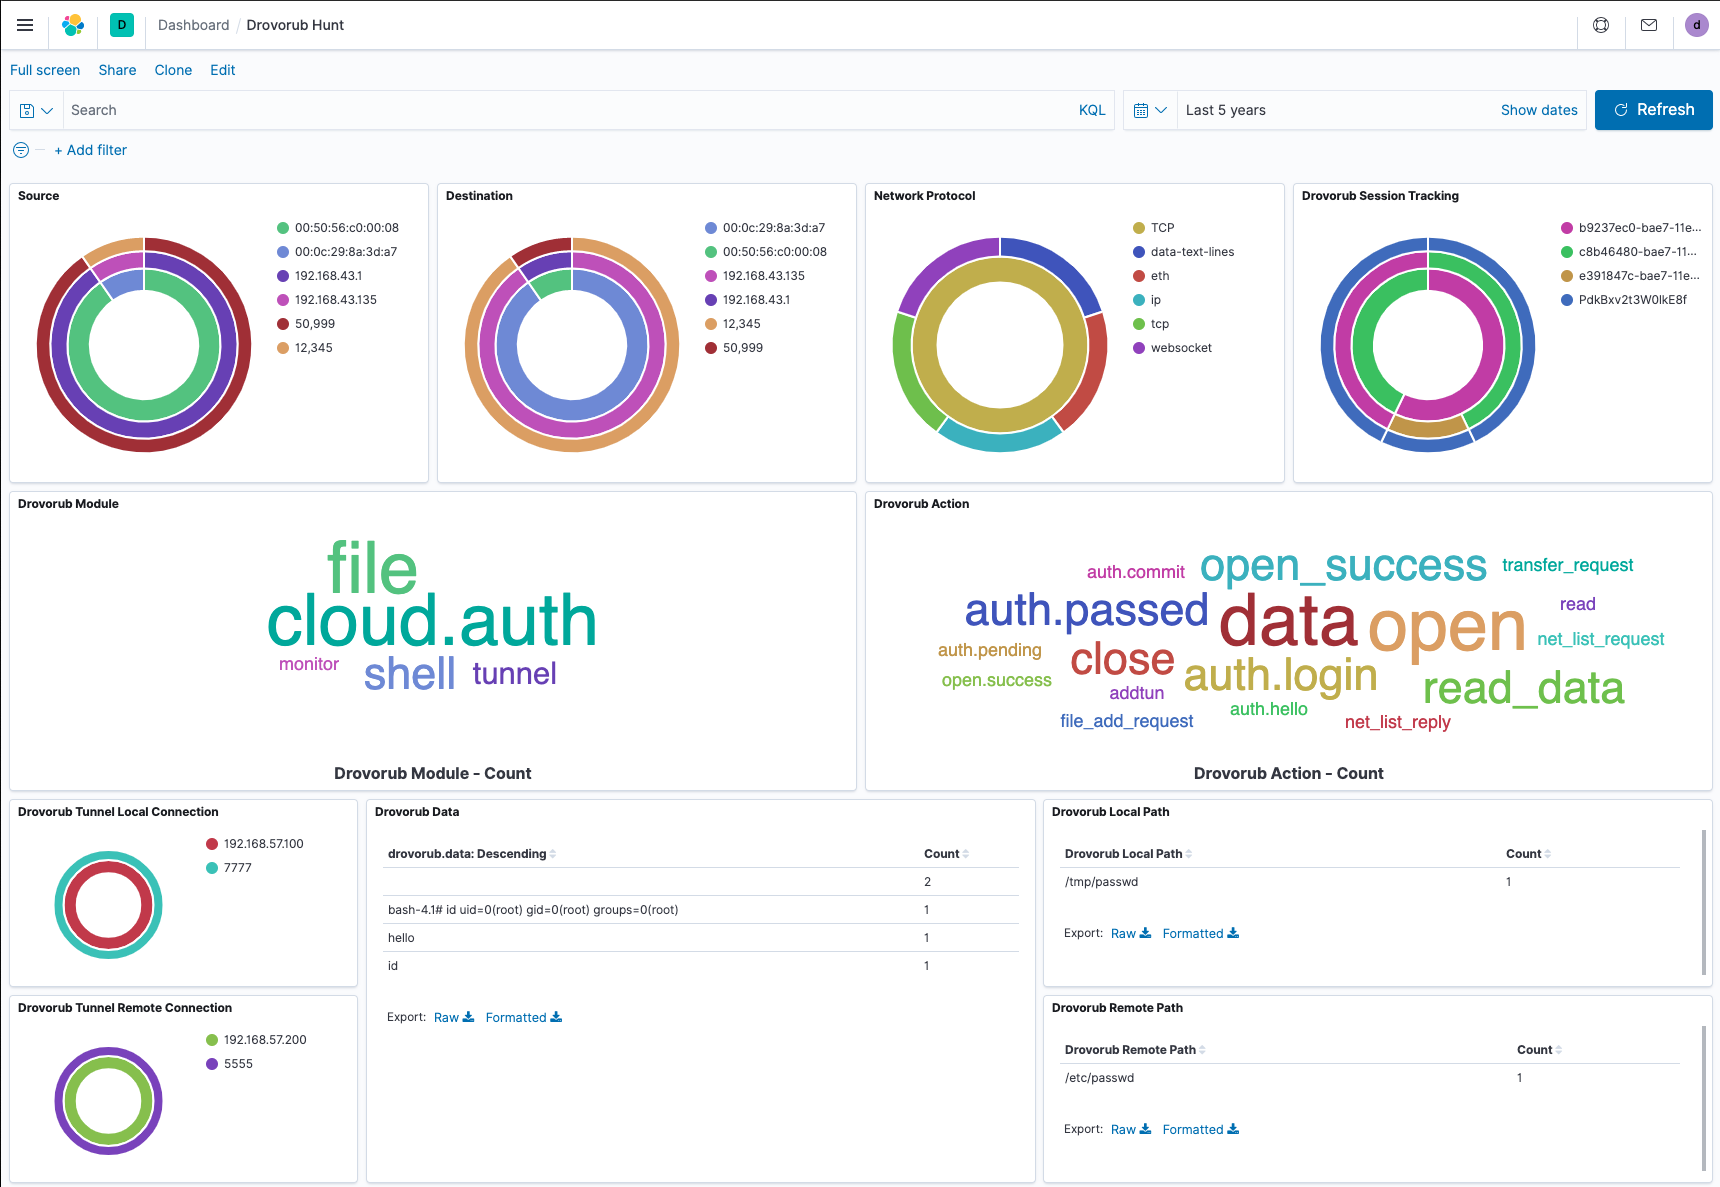
A tool to assist with network-based hunting for GRU's Drovorub malware c2

threat-feeds-aggregatorsnetwork-forensicsmalware-analysis+3
256 years ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

defensive-toolsdisk-forensicsmemory-forensics+8
4.2k14h 37m ago
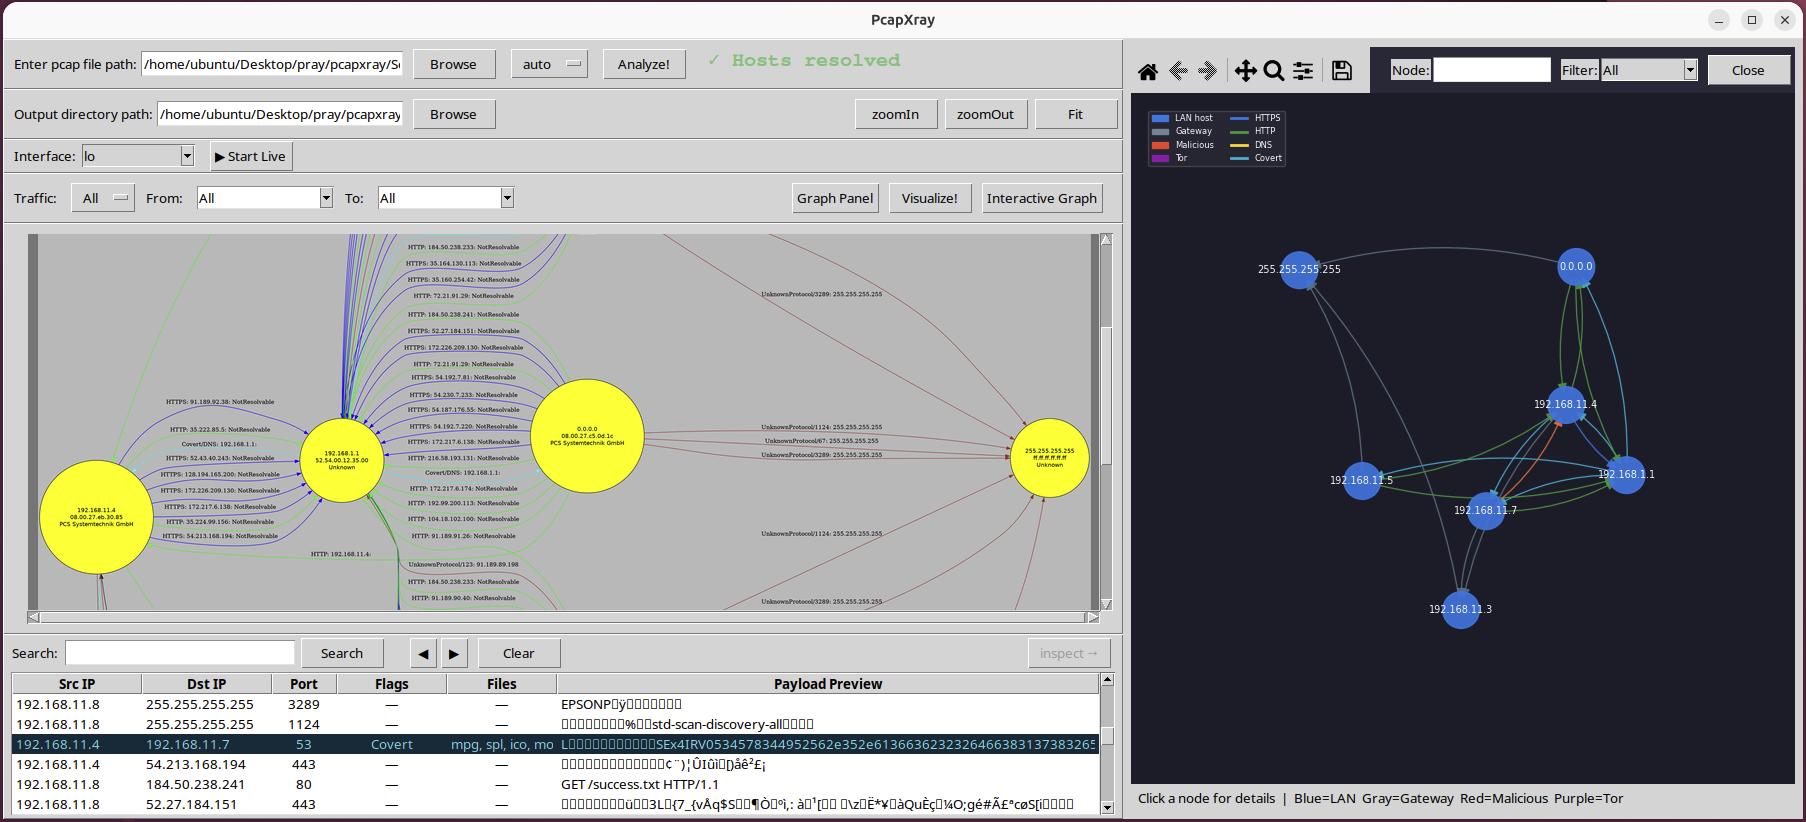
PcapXray preview

PcapXray

GitHubsrixivas/pcapxray

❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
osintpacket-sniffing-analysisnetwork-mapping+7
1.9k5 months ago
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

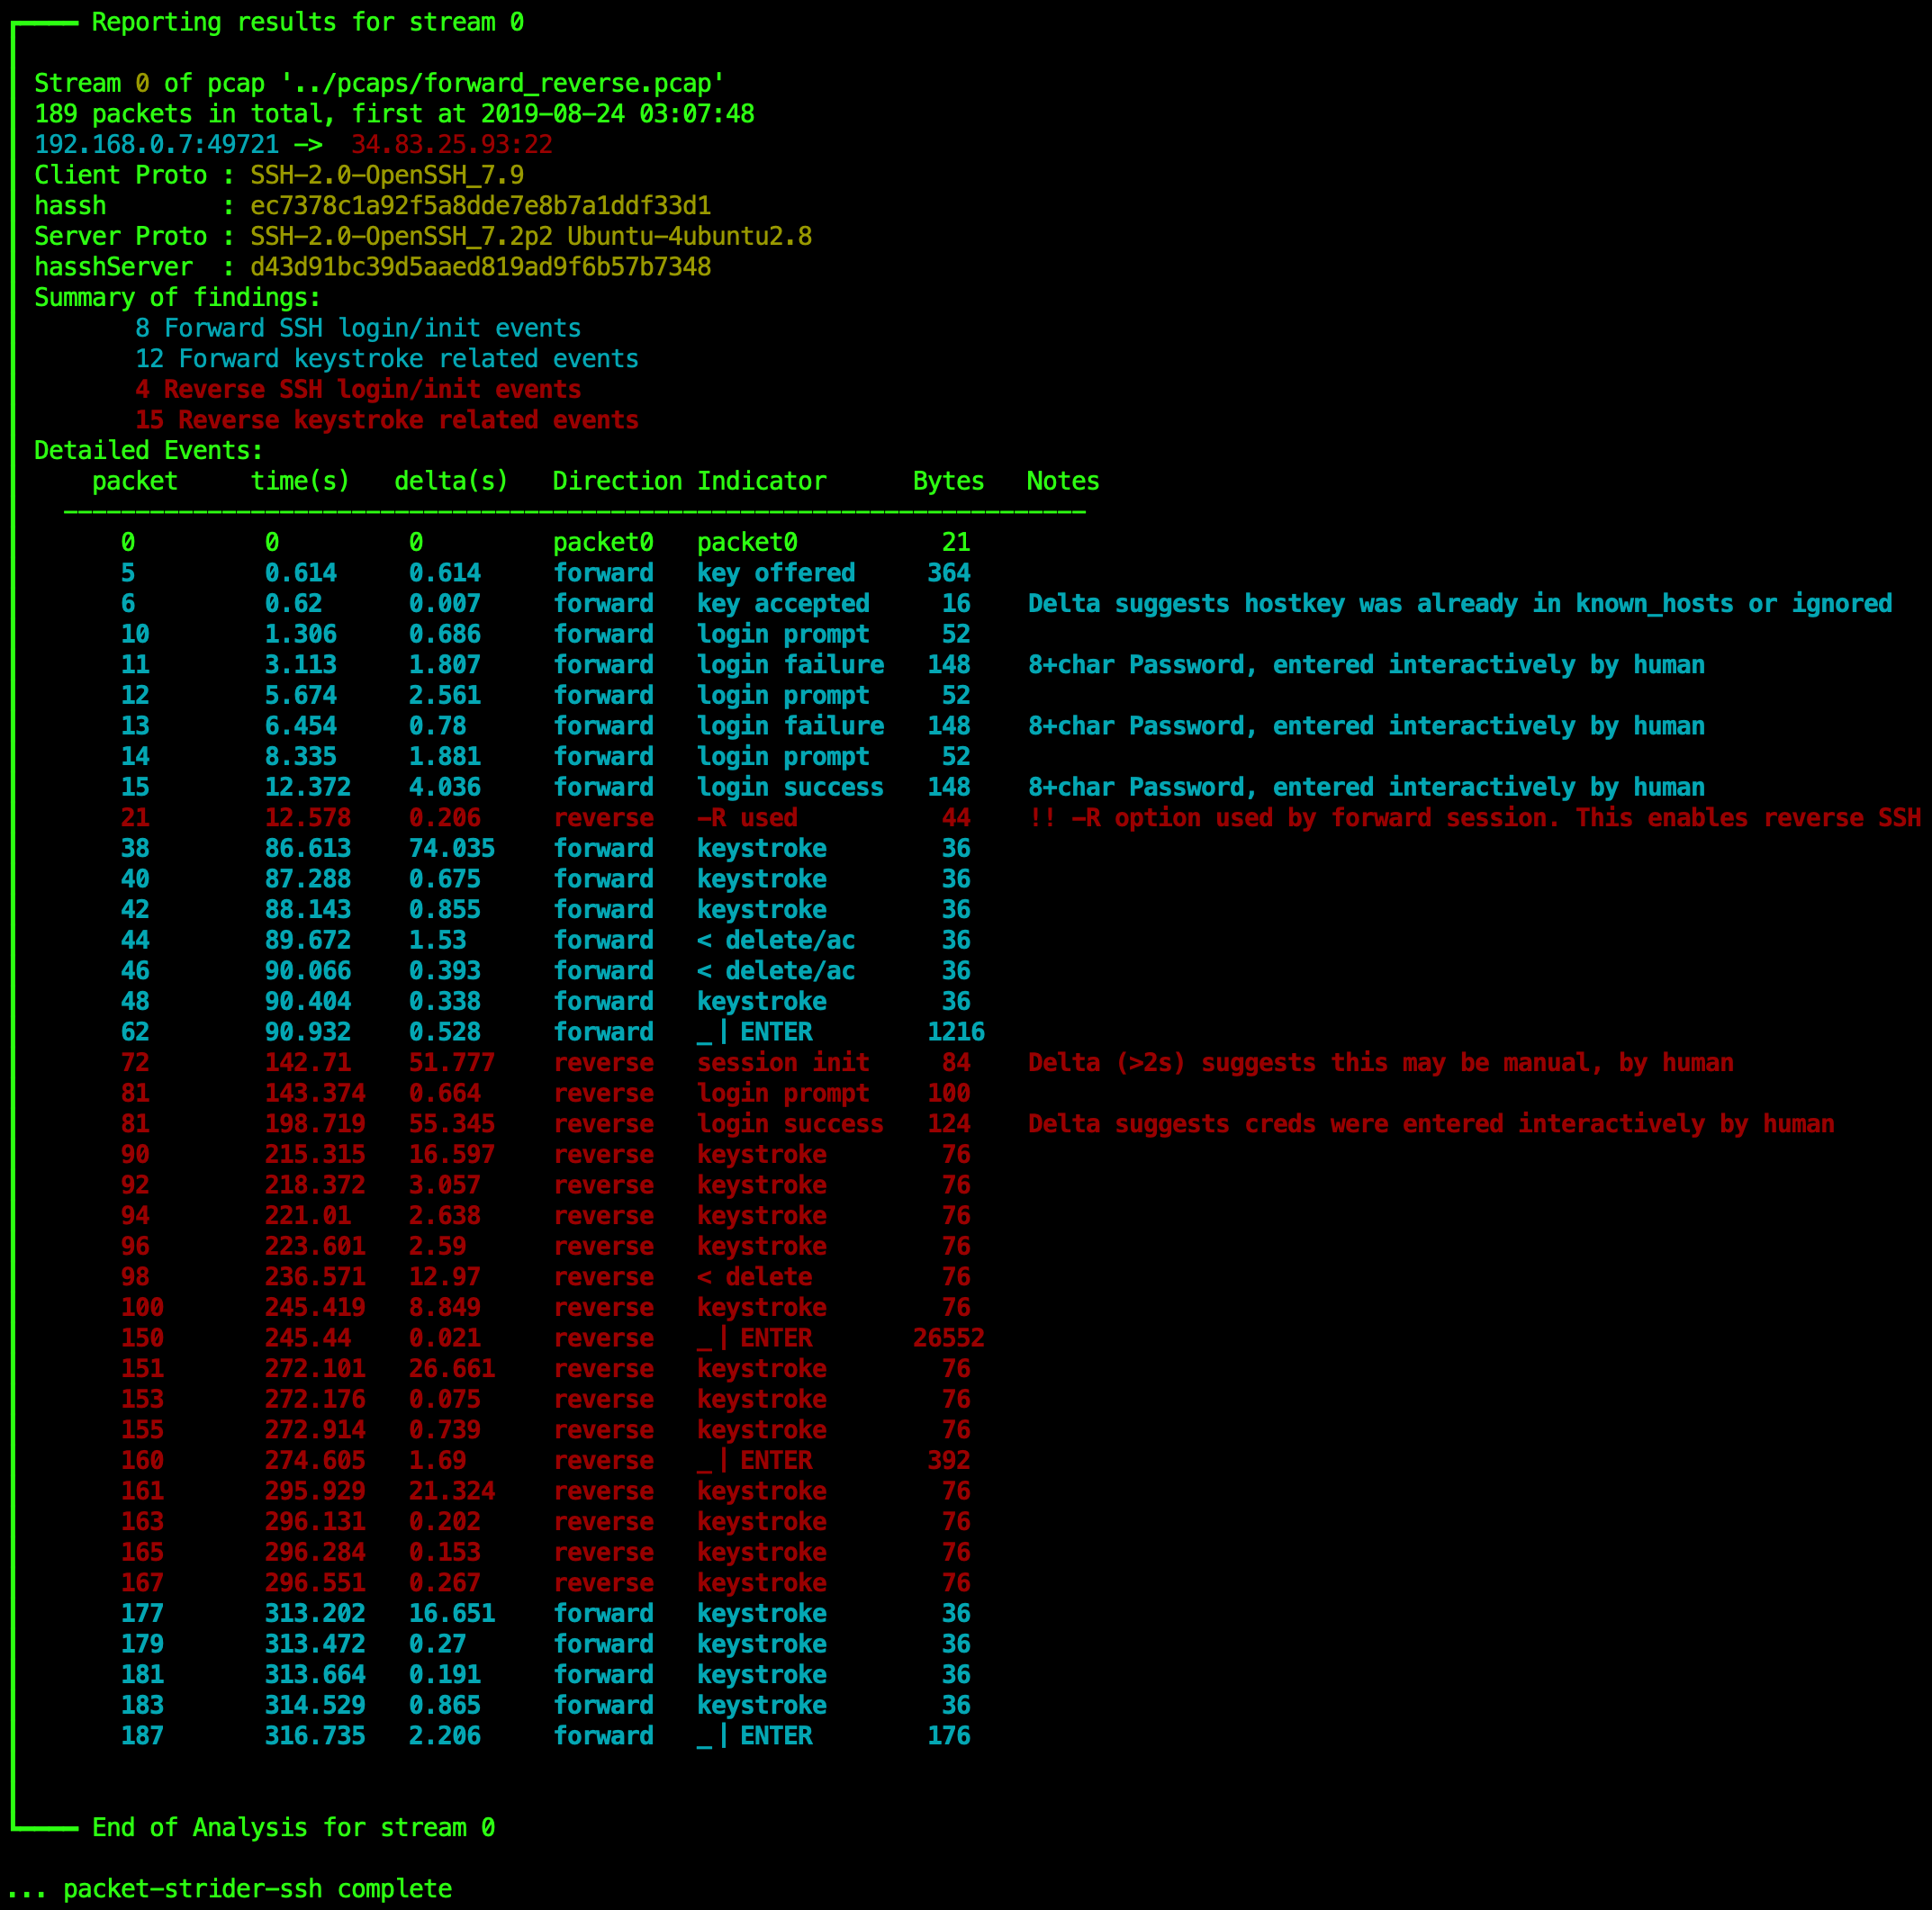
A network packet forensics tool for SSH

packet-sniffing-analysisnetwork-forensicsforensics+5
2546 years ago
caronte preview

caronte

GitHubeciavatta/caronte

A tool to analyze the network flow during attack/defence Capture the Flag competitions
packet-sniffing-analysisnetwork-forensicsforensics+1
6514 years ago
pyWhat preview

pyWhat

GitHubbee-san/pywhat

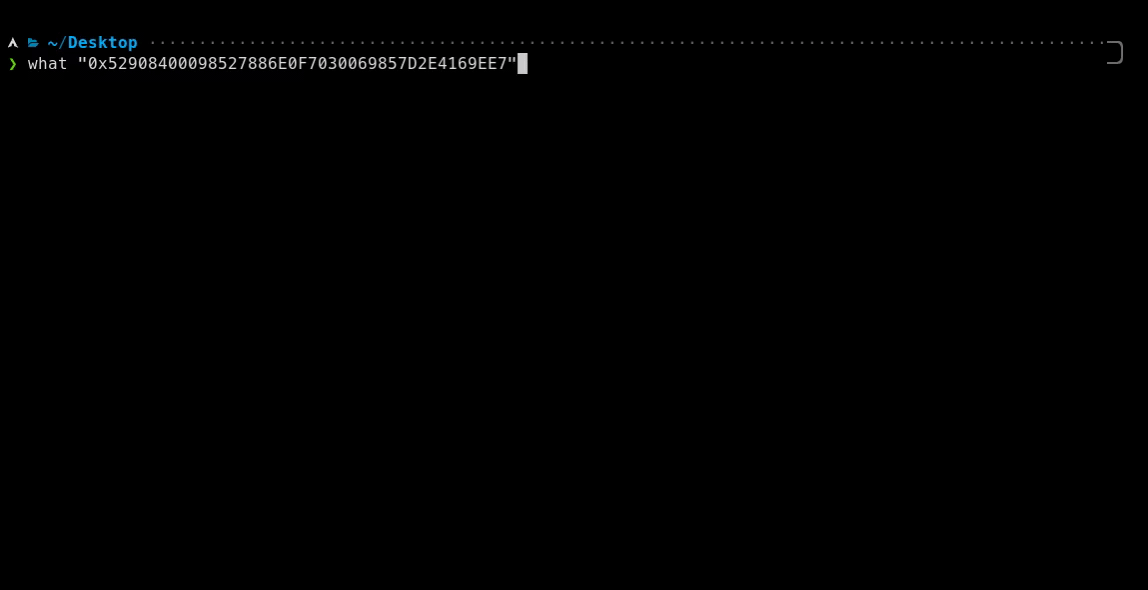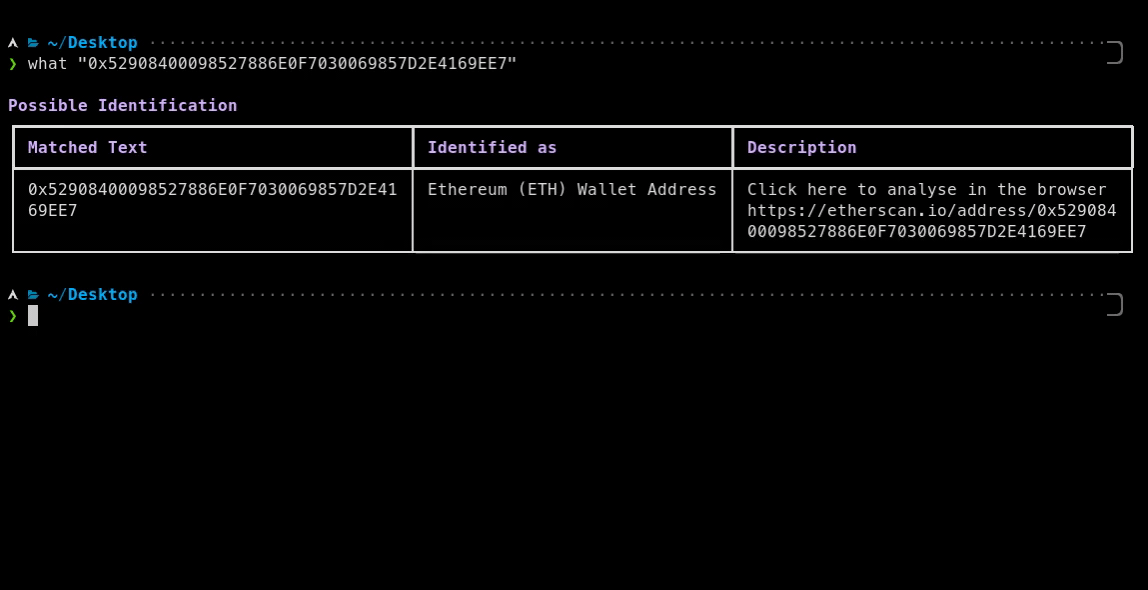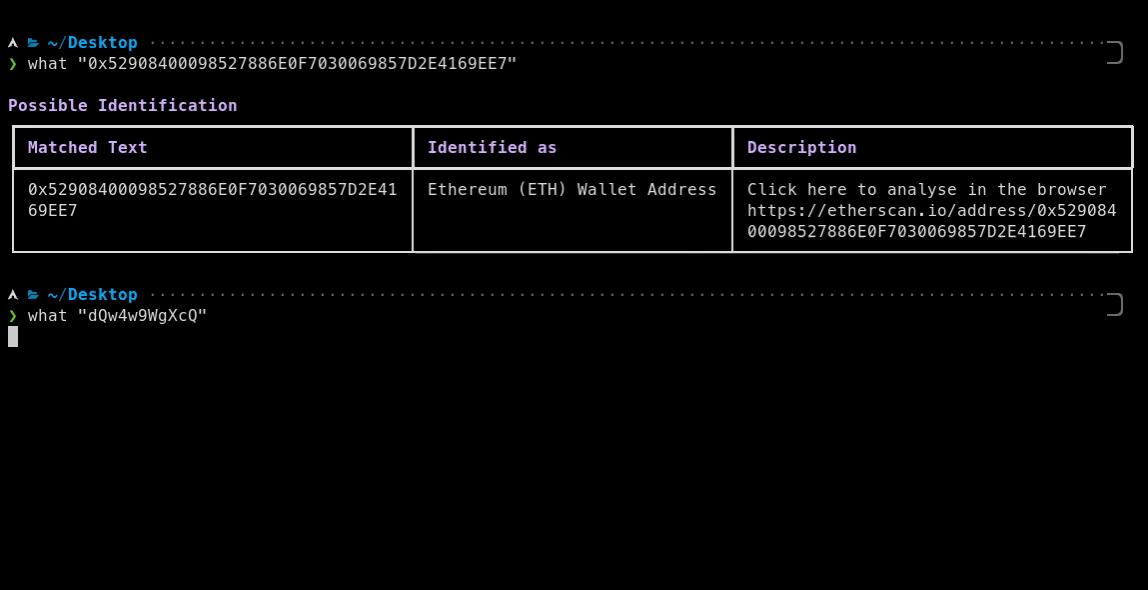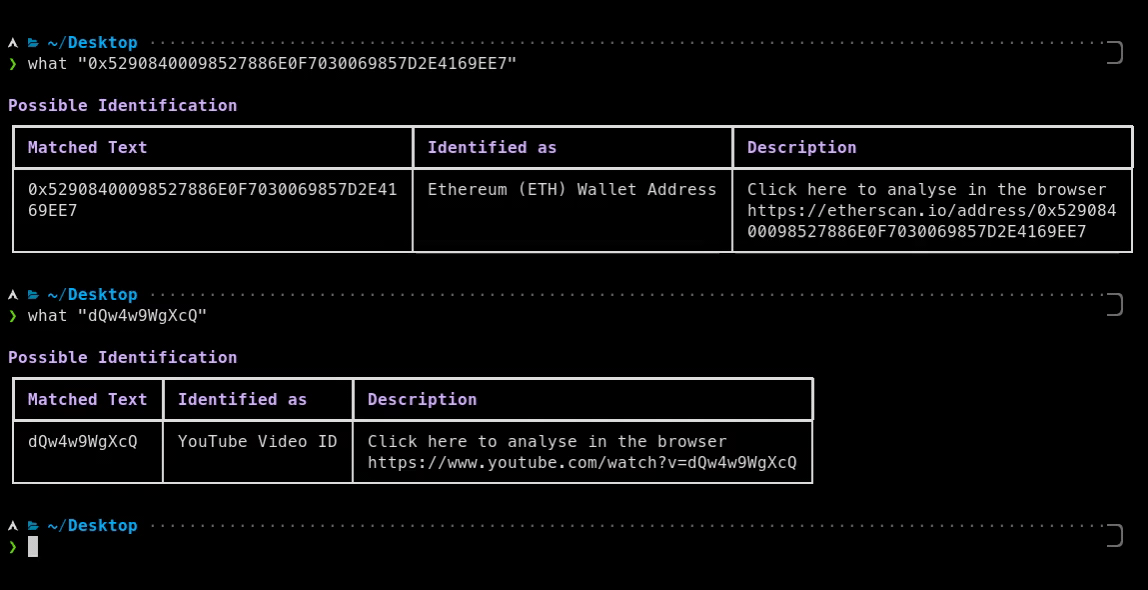
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
osintreconnaissancevulnerability-analysis+7
7.3k3 years ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

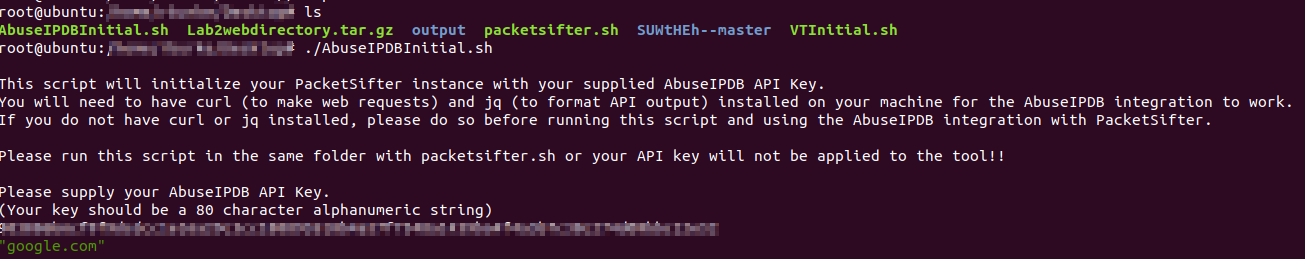
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsioc-managementpacket-sniffing-analysis+5
935 years ago
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

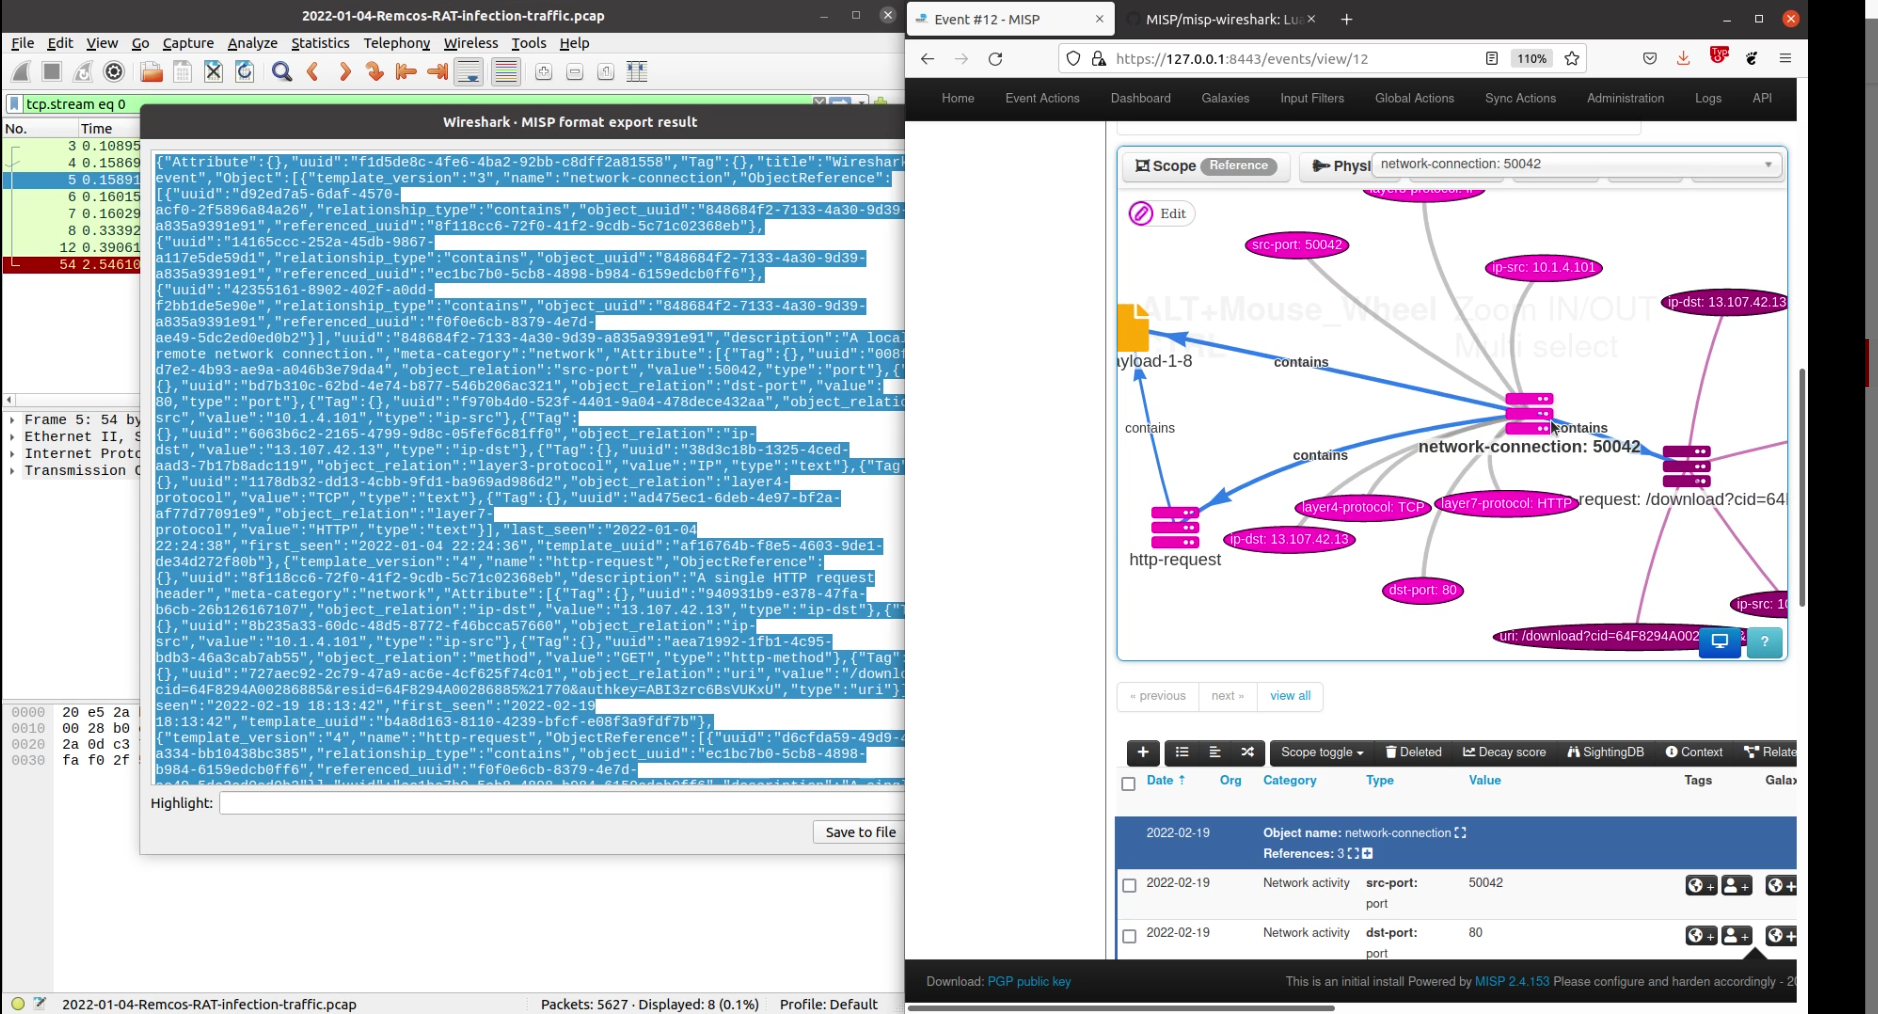
Lua plugin to extract data from Wireshark and convert it into MISP format

packet-sniffing-analysisnetwork-forensicsforensics+2
502 years ago
Qu1cksc0pe preview

Qu1cksc0pe

GitHubcyb3rmx/qu1cksc0pe

All-in-One malware analysis tool.

android-securitystatic-analysisdynamic-analysis-sandboxing+4
2.0k10 days ago
IpGeo preview

IpGeo

GitHubz4l4mi/ipgeo

Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.


osintreconnaissancenetwork-forensics+1
1323 years ago
Previous1…678Next