
 #1
Tools for analyzing network traffic and communication logs to investigate security incidents.
Kitploit recommended
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 awakecoding/wireshark-rdp
Wireshark RDP resources
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
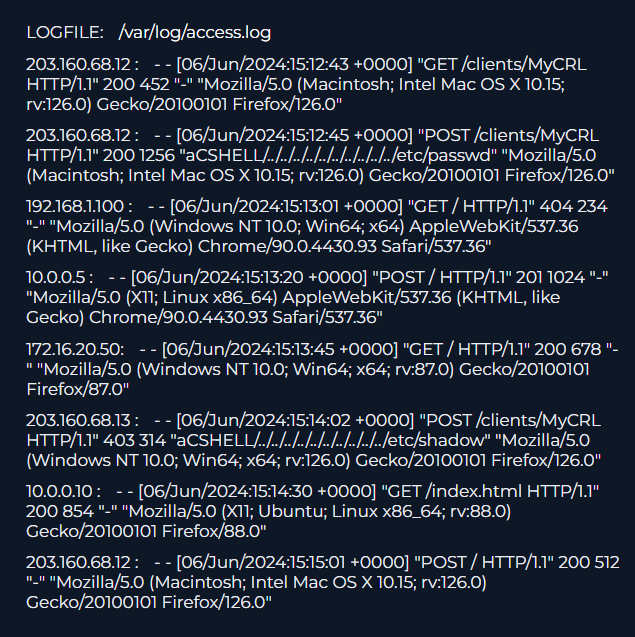 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…

 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 nccgroup/pcap-burp
Pcap importer for Burp
 synacktiv/pcapan
A pcap capture analysis helper
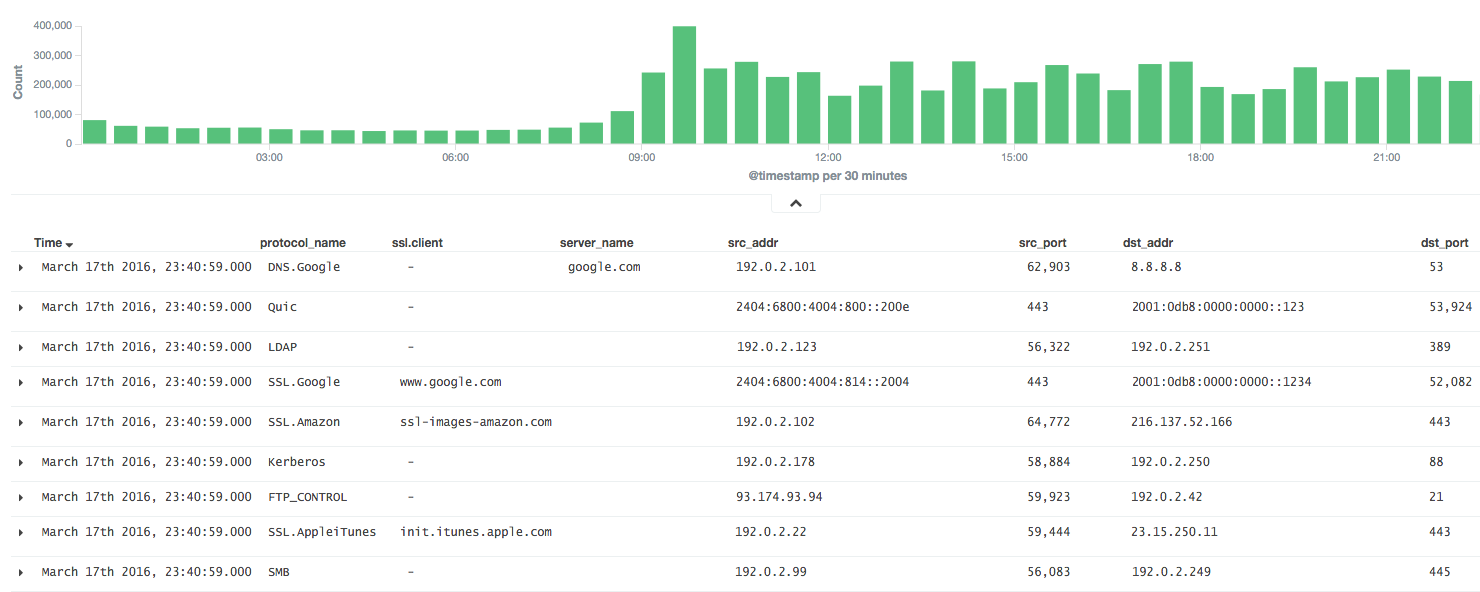 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection







