
 #1
Configuration auditing, compliance scanning, hardening benchmarks, and drift detection tools.
Kitploit recommended

 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
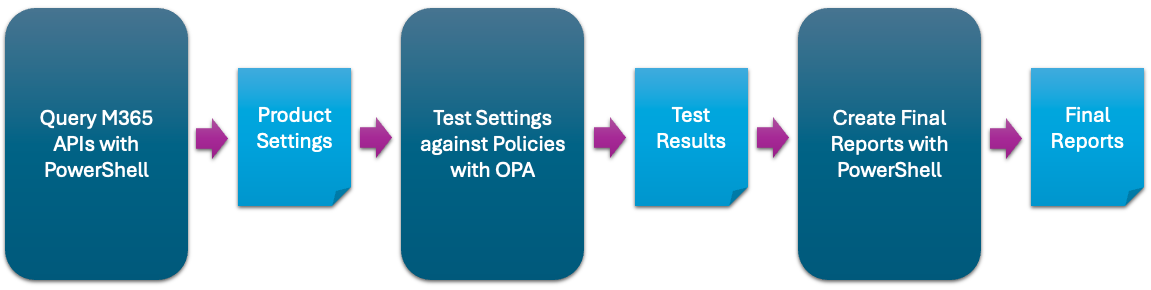 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 yandex/gixy
Nginx configuration static analyzer
 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 0x6d69636b/windows_hardening
HardeningKitty and Windows Hardening Settings
 aquasecurity/tfsec
Tfsec is now part of Trivy
 m0rtem/cloudfail
Utilize misconfigured DNS and old database records to find hidden IP's behind the CloudFlare network
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 ine-labs/awsgoat
AWSGoat : A Damn Vulnerable AWS Infrastructure
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.






