
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Log Analysis — Page 36 | Kitploit
Categories

Log Analysis

Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.

Kitploit recommended

Top tools

10 selected
wazuh preview#1

wazuh

GitHubwazuh/wazuh
16.5k14h 5m ago
graylog2-server preview#2

graylog2-server

GitHubgraylog2/graylog2-server
8.2k4h 45m ago
loki preview#3

loki

GitHubgrafana/loki
29.0k2h 58m ago
osquery preview#7

osquery

GitHubosquery/osquery
23.4k16h 37m ago
securityonion preview#8

securityonion

GitHubsecurity-onion-solutions/securityonion
4.9k1 month ago
zeek preview#9

zeek

GitHubzeek/zeek
7.8k14h 17m ago
suricata preview#10

suricata

GitHuboisf/suricata
6.5k5 days ago
sigma preview#11

sigma

GitHubsigmahq/sigma
10.9k1 day ago
detection-rules preview#12

detection-rules

GitHubelastic/detection-rules
2.7k1 day ago
logparser preview#13

logparser

GitHublogpai/logparser
2.0k1 year ago
NewestRelevanceMost popularRecently updated
684 results
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
forensicsthreat-intelligenceincident-response+1
8412 days ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems

forensicsinformation-gatheringdigital-forensics+3
2202 years ago
S1EM preview

S1EM

GitHubv1d1an/s1em

This project is a SIEM with SIRP and Threat Intel, all in one.
vulnerability-scannersforensicsnetwork-security+6
4621 year ago
epagneul preview

epagneul

GitHubjurelou/epagneul

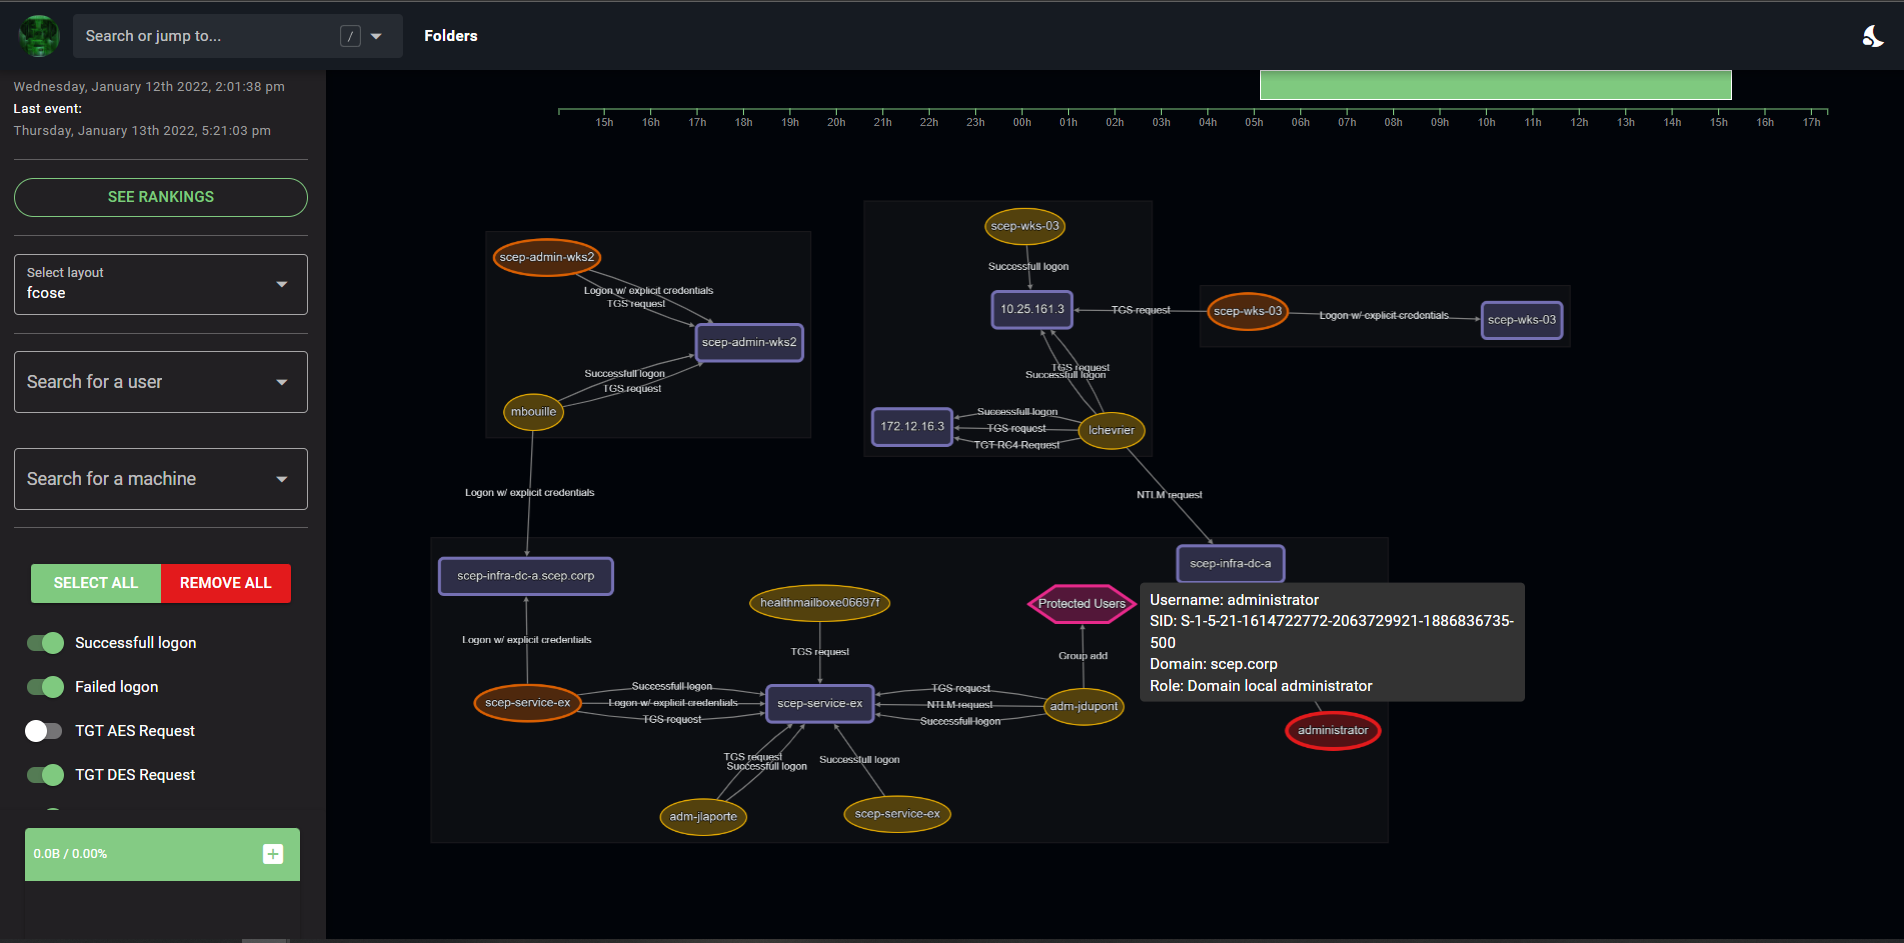
Graph Visualization for windows event logs

forensicslog-analysis
2511 year ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
forensicsdigital-forensicsthreat-intelligence+2
3.3k1 day ago
SuricataLog preview

SuricataLog

GitHubjosevnz/suricatalog

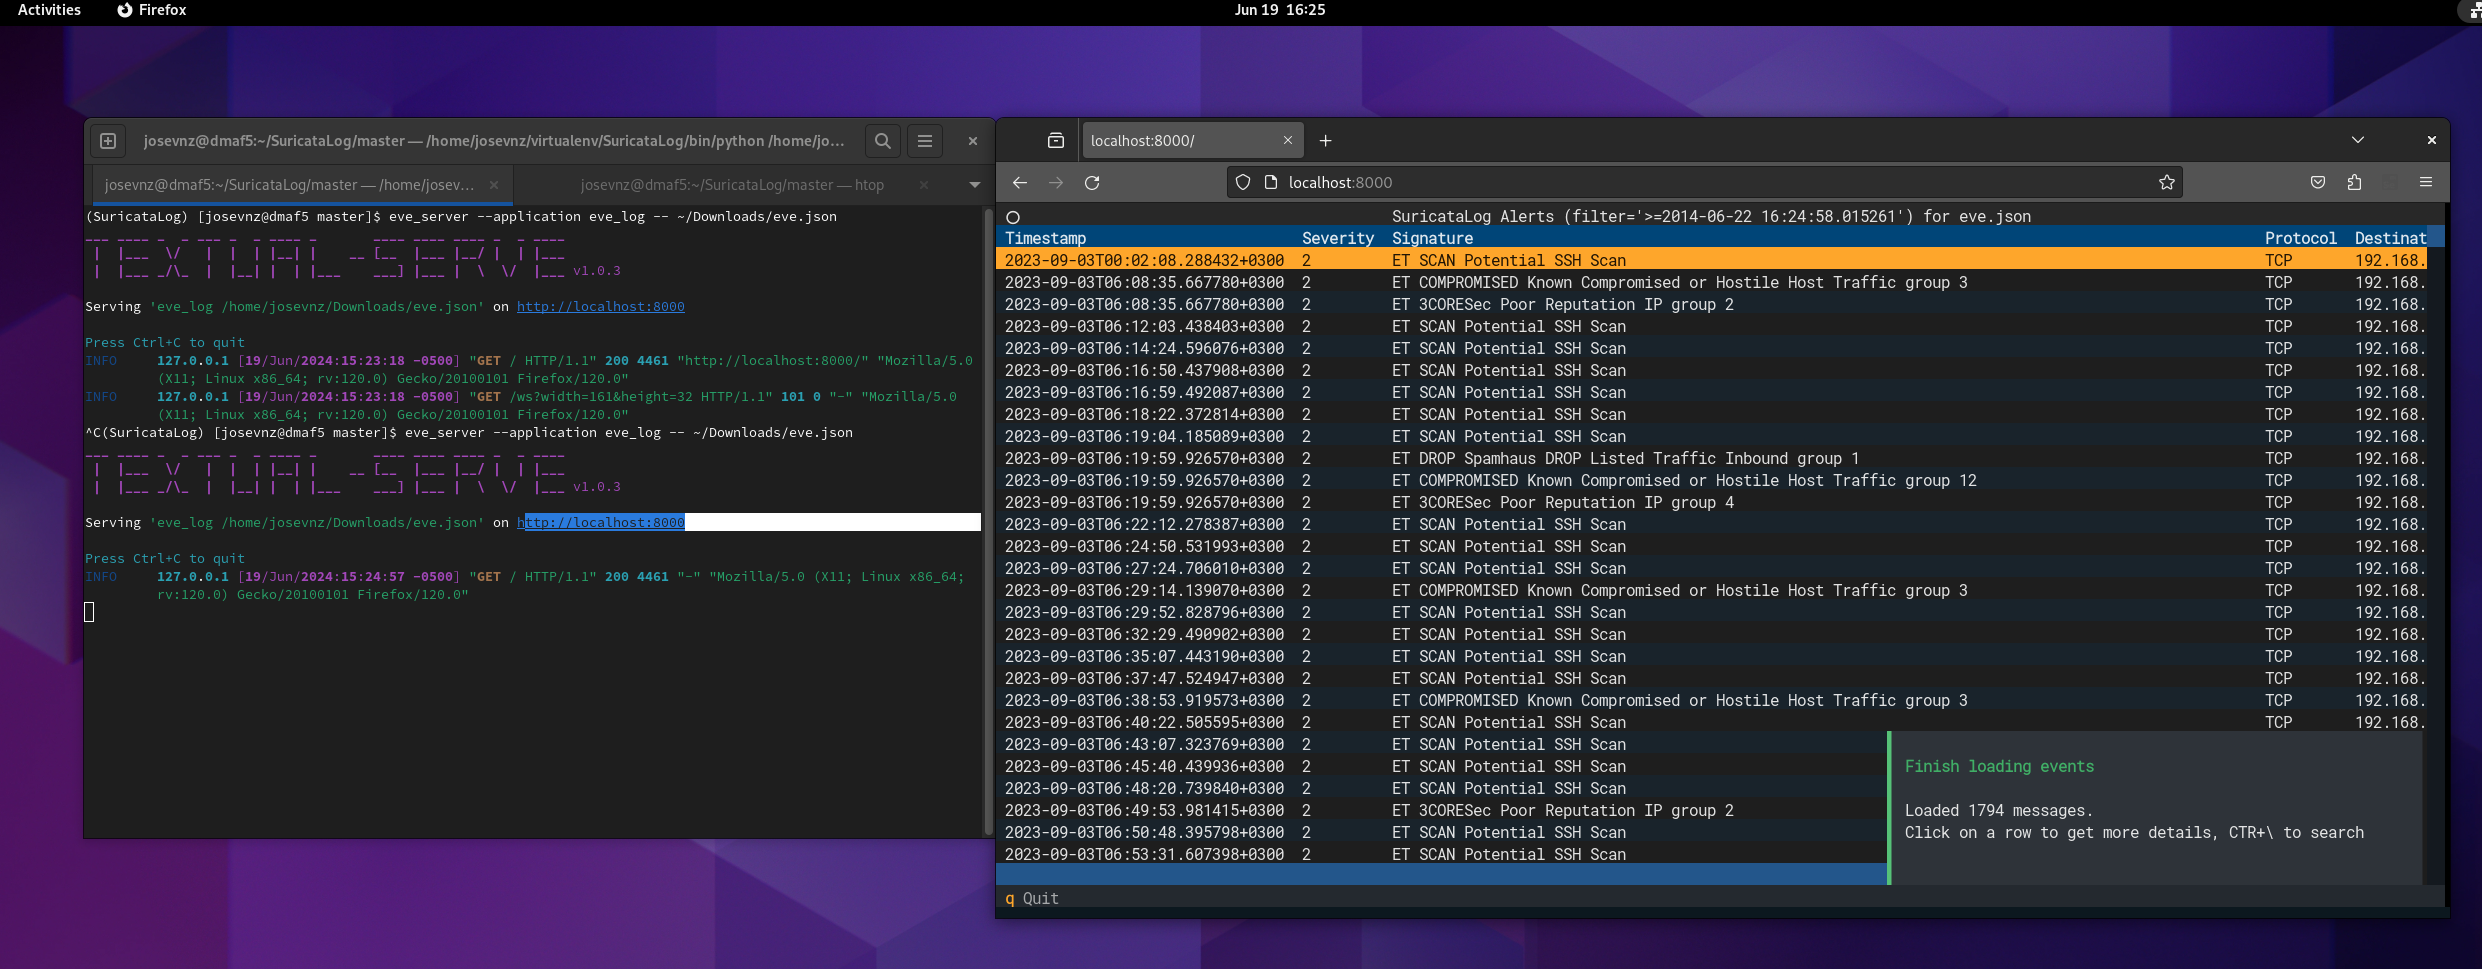
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
network-securityintrusion-detectioneducation+1
2715 days ago
L3MON preview

L3MON

GitHubd3vl/l3mon

Web-based network monitoring system providing real-time bandwidth tracking, server performance metrics, and customizable alerts for proactive network…

network-mappingnetwork-securitylog-analysis
2863 years ago
DetectionLabELK preview

DetectionLabELK

GitHubcyberdefenders/detectionlabelk

DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
defensive-toolsosintconfiguration-auditing+7
5755 years ago
SnitchDNS preview

SnitchDNS

GitHubctxis/snitchdns

Database Driven DNS Server with a Web UI
phishing-toolsdata-exfiltrationinformation-gathering+7
2442 years ago
DFIR-O365RC preview

DFIR-O365RC

GitHubanssi-fr/dfir-o365rc

PowerShell module for Office 365 and Azure log collection

forensicsdigital-forensicscloud-security+2
2821 year ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
disk-forensicsioc-managementvulnerability-analysis+8
856 months ago
hawk preview

hawk

GitHubt0pcyber/hawk

Powershell Based tool for gathering information related to O365 intrusions and potential Breaches

cloud-infrastructure-securityinformation-gatheringdigital-forensics+3
9491 year ago
Cowrie and Grafana Honeypot using Terraform on DigitalOcean preview

Cowrie and Grafana Honeypot using Terraform on DigitalOcean

GitLaboseguera12/cowrie-honeypot-digitalocean

Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
cloud-infrastructure-securitynetwork-securitydevsecops+2
126 days ago
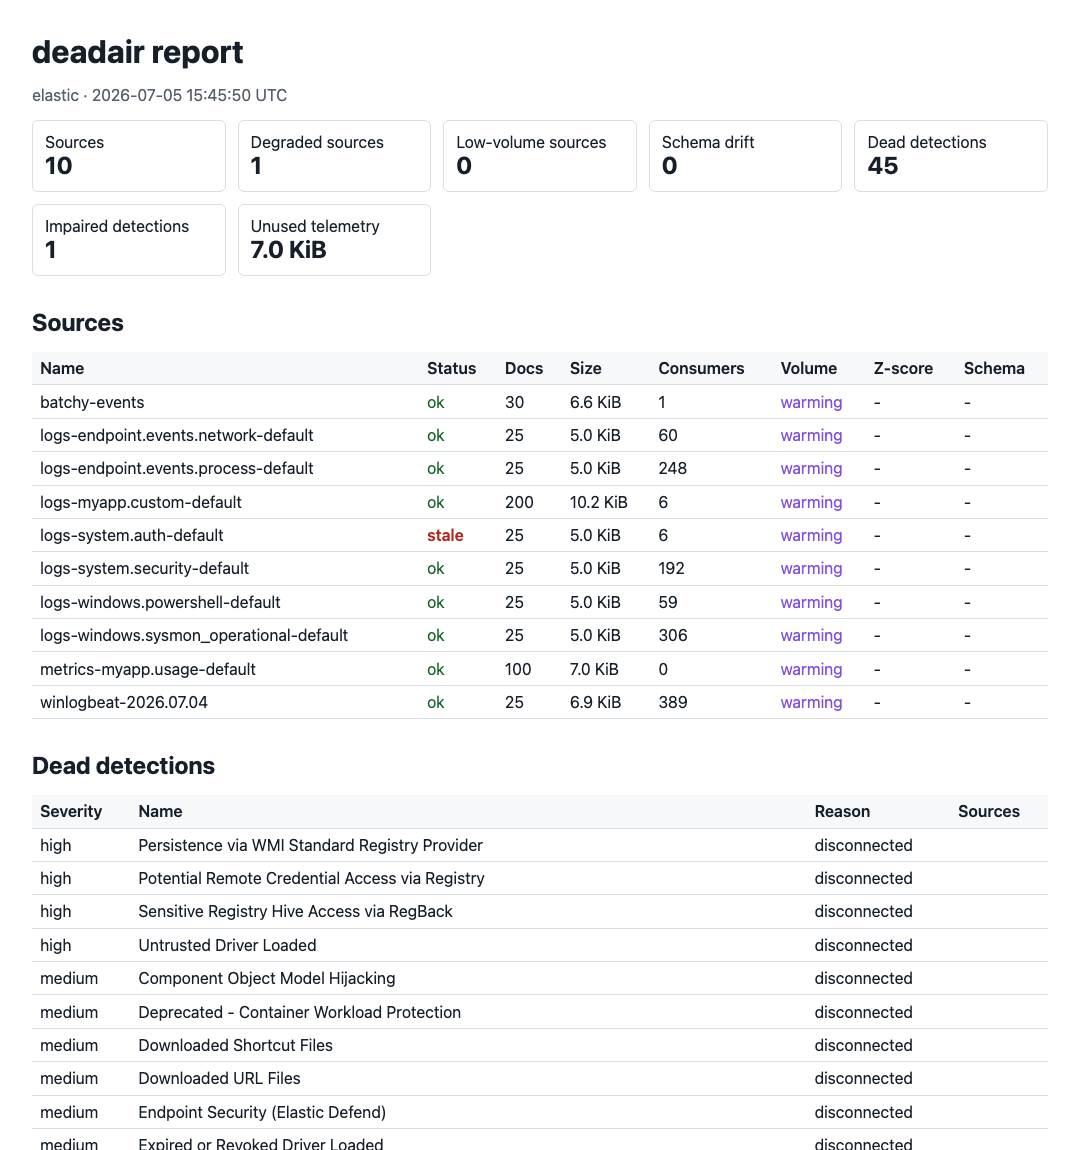
deadair preview

deadair

GitHubbig-comfy/deadair

Finds the detection rules in your SIEM that are running blind

vulnerability-analysisconfiguration-auditinglog-analysis
61 month ago
tirreno preview

tirreno

GitHubtirrenotechnologies/tirreno

Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…

threat-intelligenceincident-responseapi-security+3
1.5k15 days ago
How-To-Secure-A-Linux-Server preview

How-To-Secure-A-Linux-Server

GitHubimthenachoman/how-to-secure-a-linux-server

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

vulnerability-scannersconfiguration-auditingnetwork-security+7
30.3k1 month ago
kippo-g0tmi1k preview
Archived

kippo-g0tmi1k

GitHubg0tmi1k/kippo-g0tmi1k

Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…

defensive-toolspassword-attacksinformation-gathering+4
1312 years ago
dfir-toolkit preview
Archived

dfir-toolkit

GitHubdfir-dd/dfir-toolkit

CLI tools for forensic investigation of Windows artifacts

disk-forensicsforensicsdigital-forensics+2
3551 year ago
Previous1…35363738Next









