
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended

 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 canonical/ubuntu-security-notices
Ubuntu vulnerability dataset publishing USN/LSN security notices in OSV and OpenVEX JSON formats for automated vulnerability and VEX-aware dependency…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
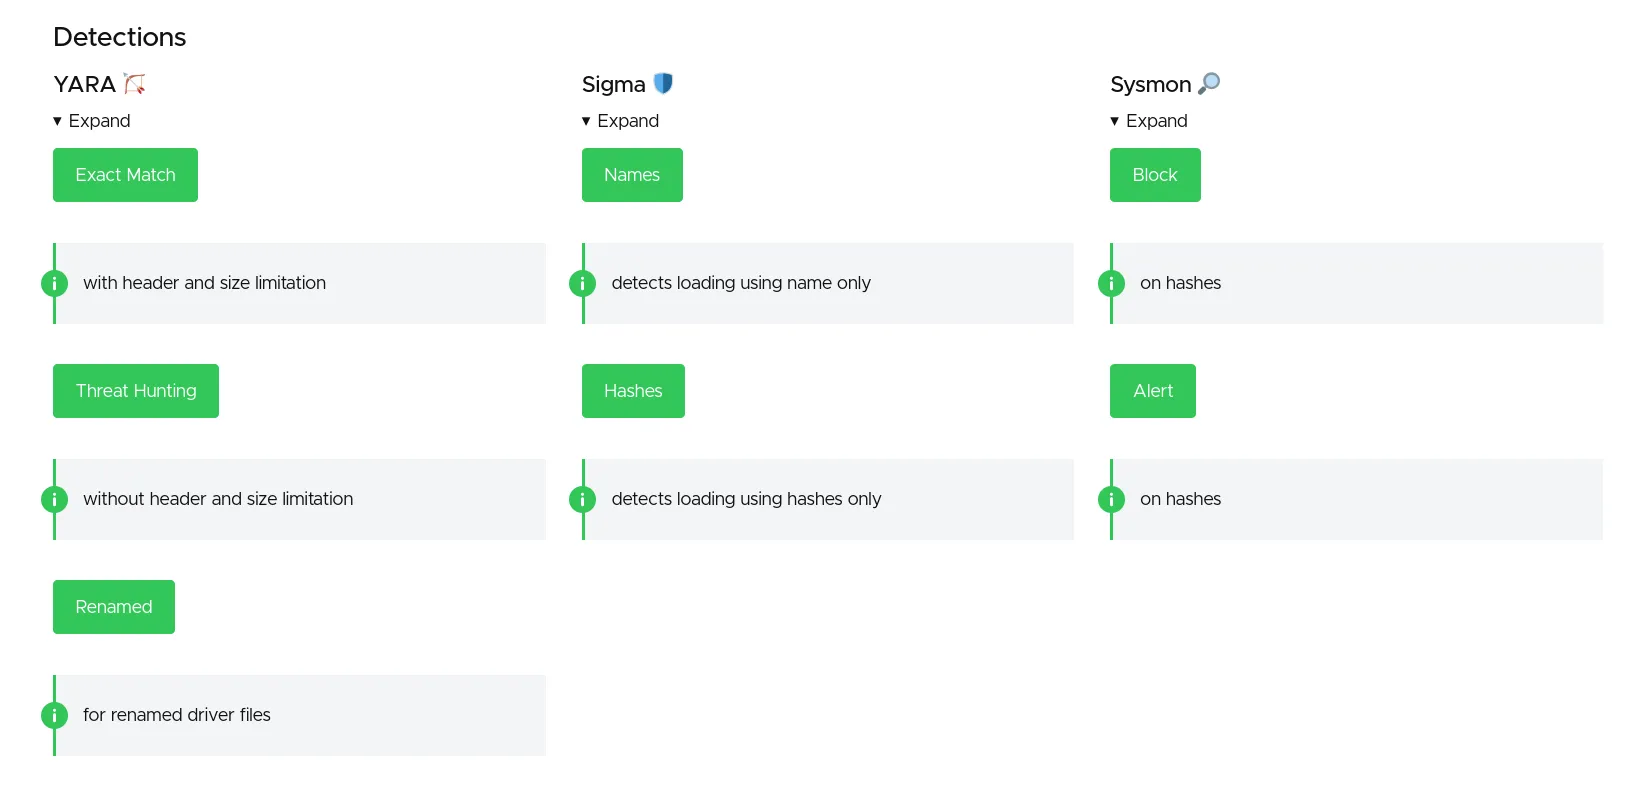 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 paloaltonetworks/unit42-timely-threat-intel
A collection of files with indicators supporting social media posts from Palo Alto Network's Unit 42 team to disseminate timely threat intelligence.
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
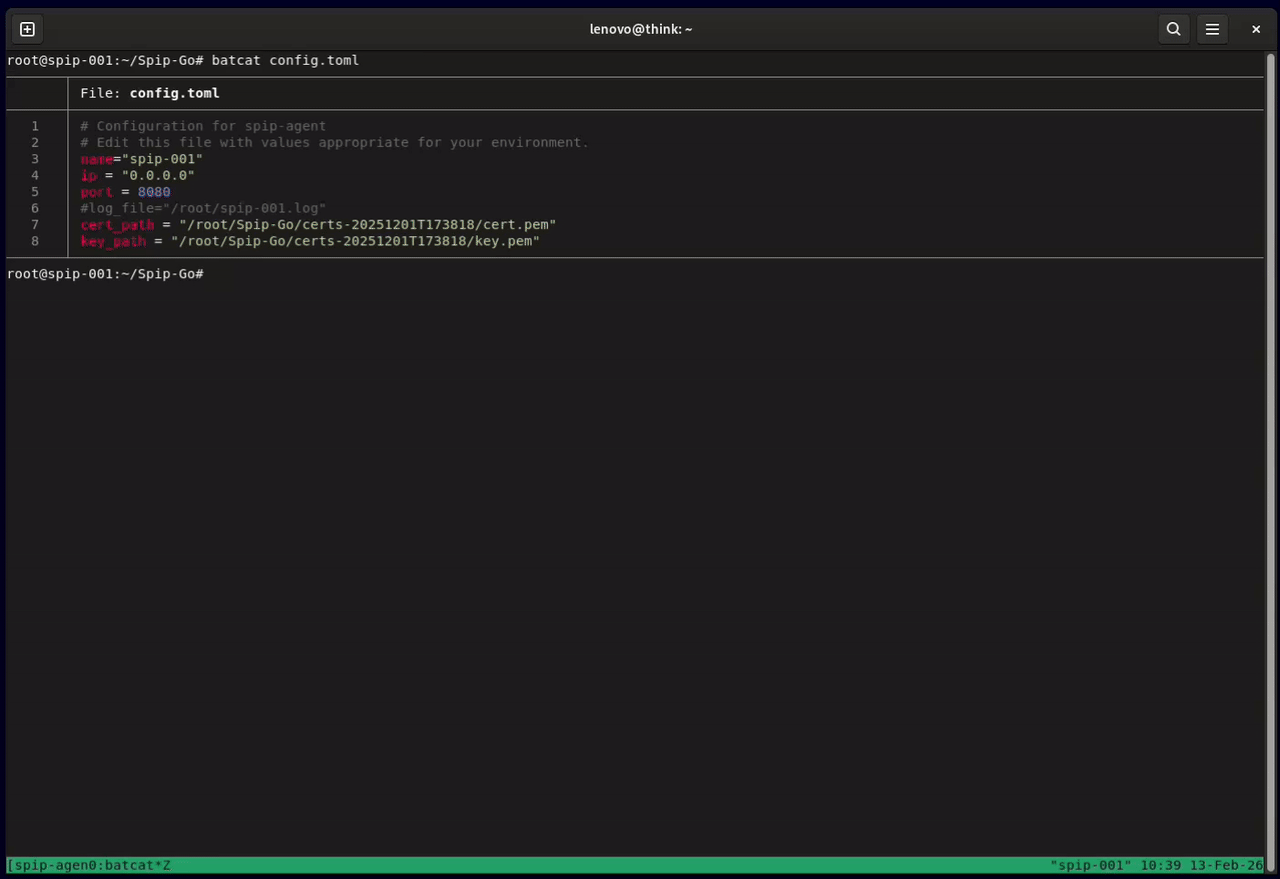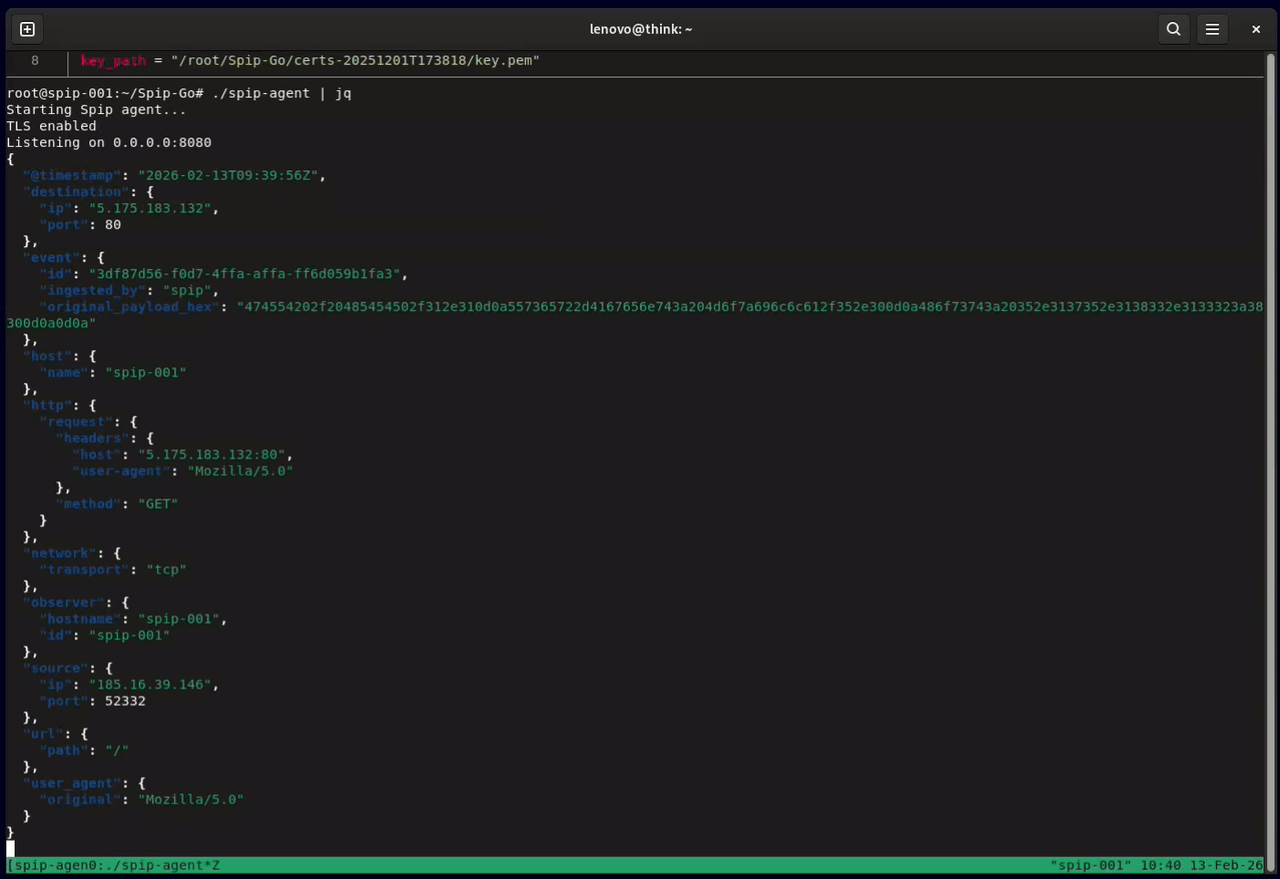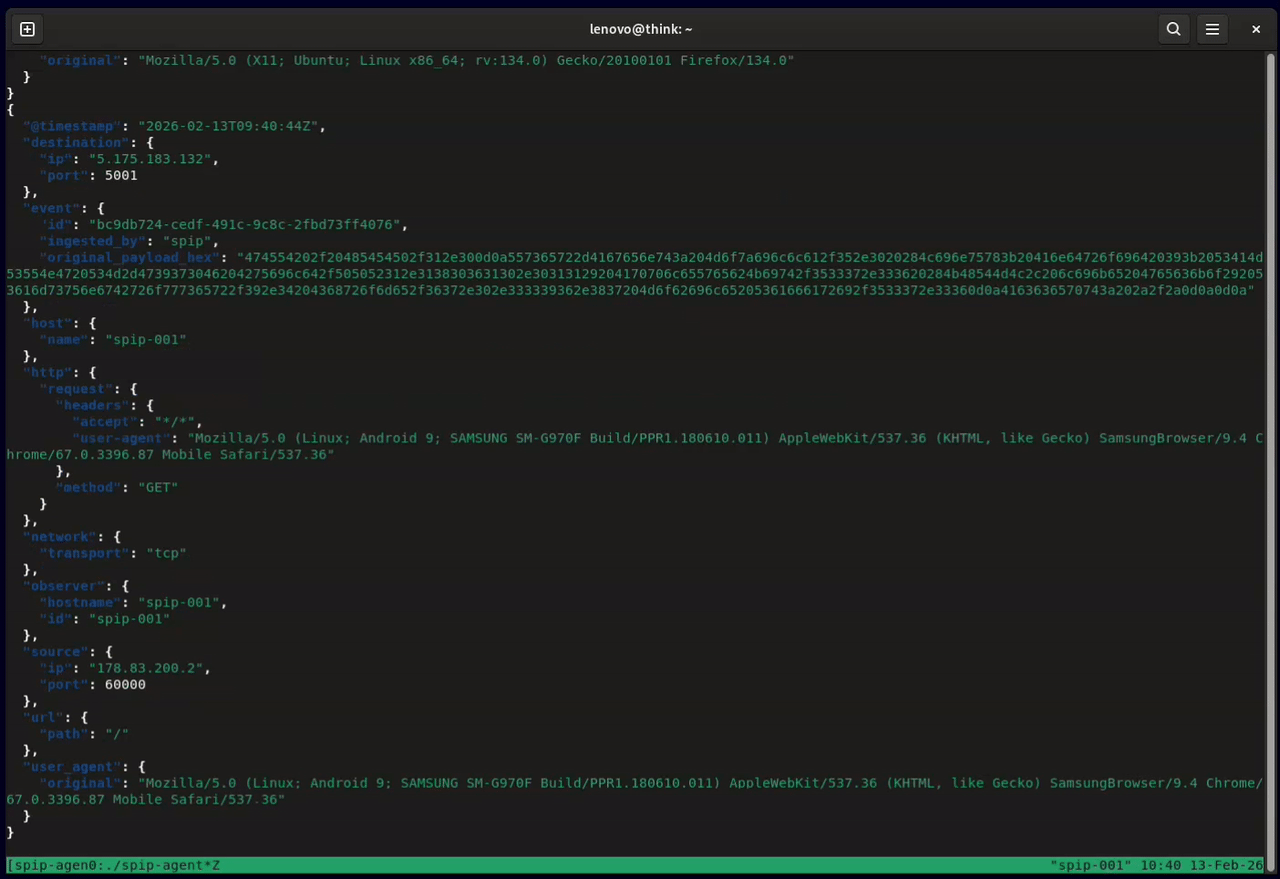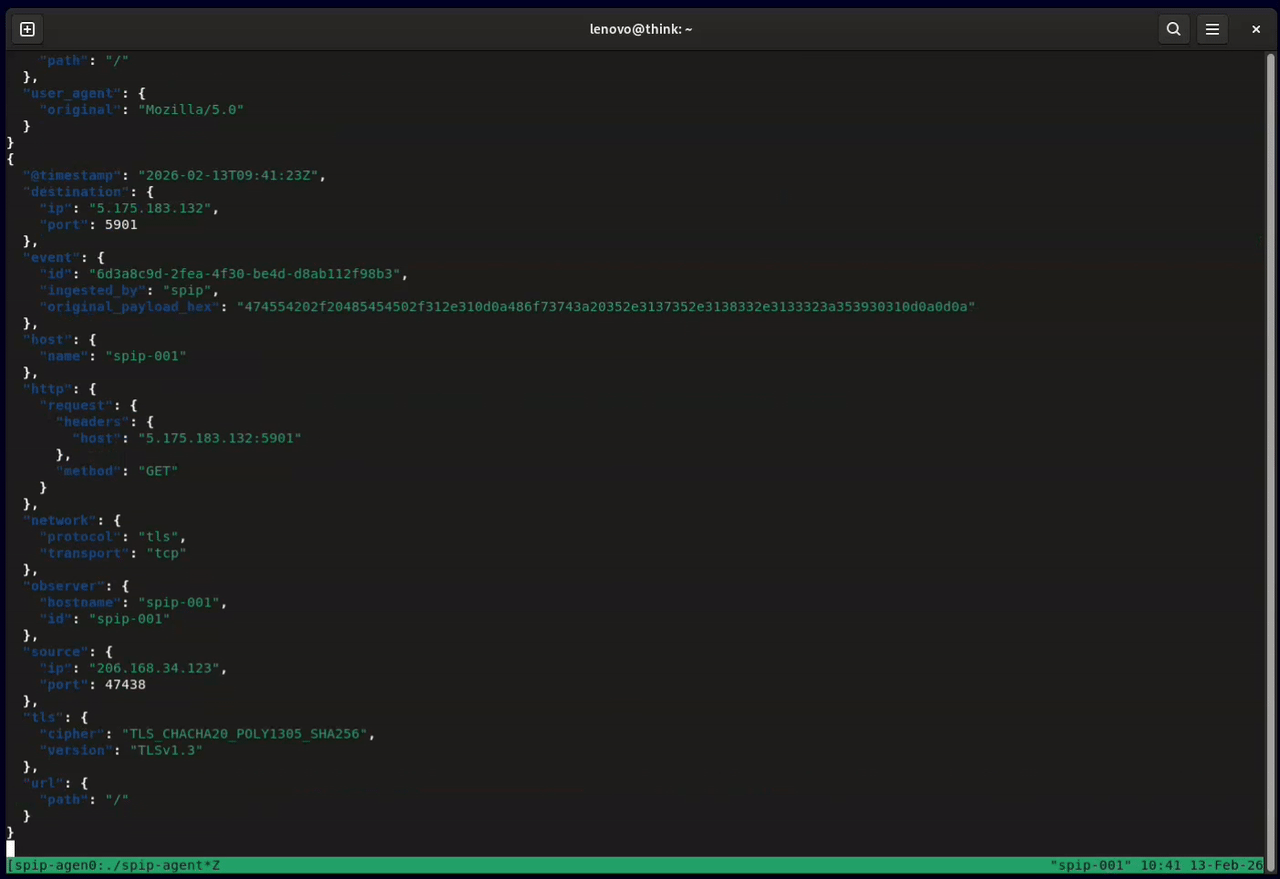 honeylabshq/spip-go
Spip network sensor written in Go
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 vahpem/rust-deobf
Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…







