#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
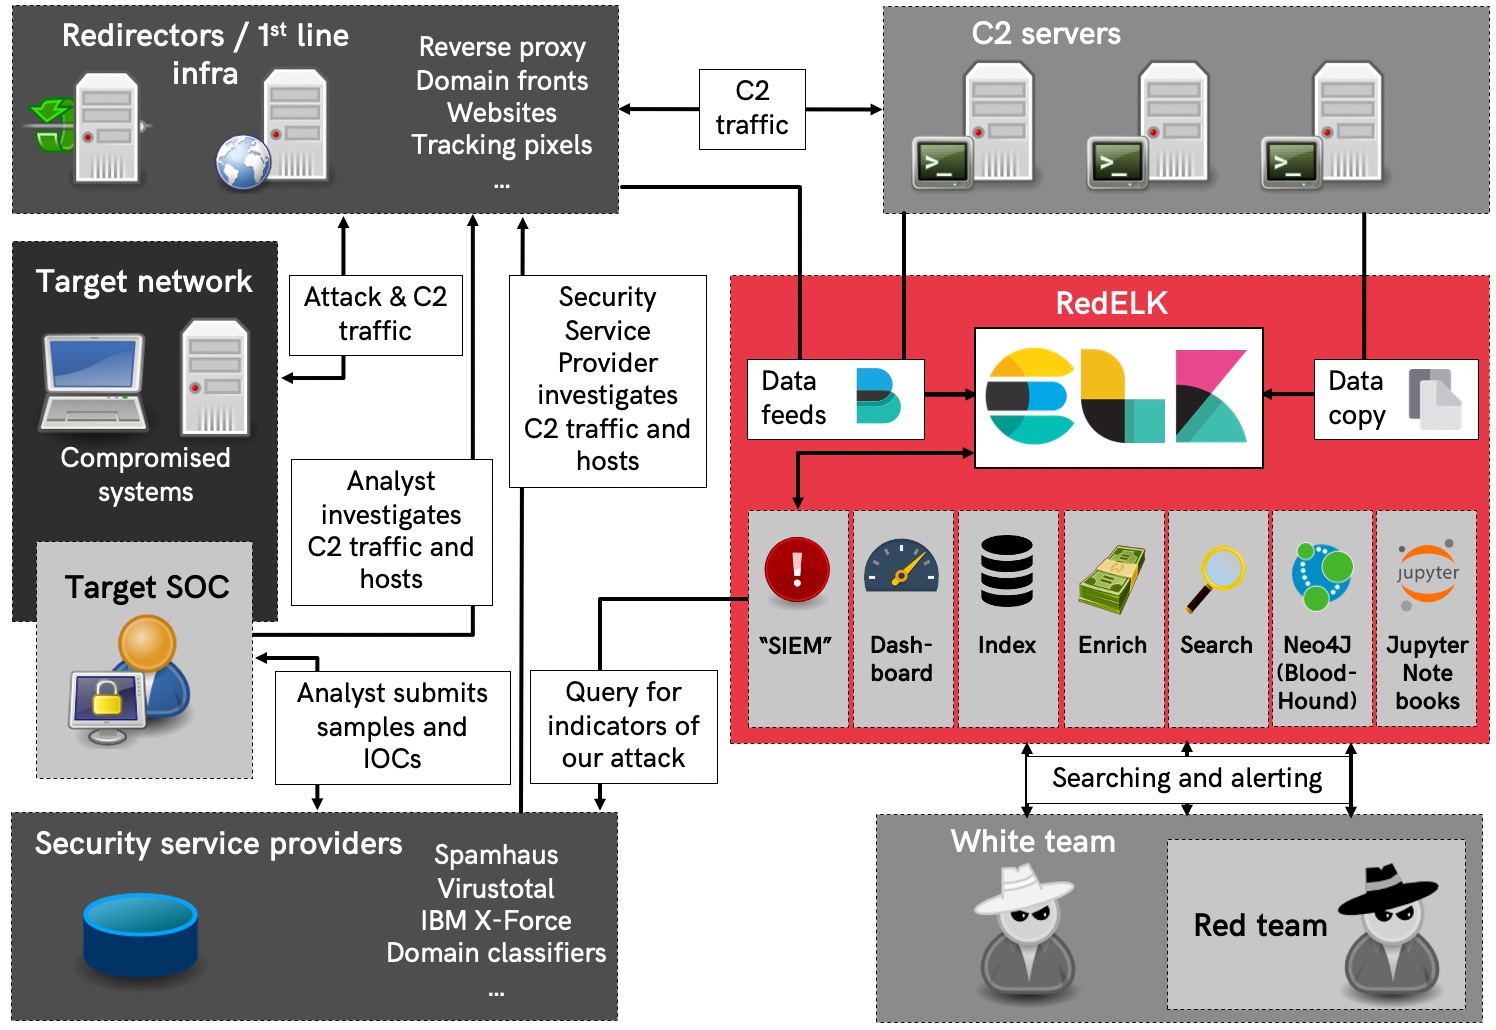
 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
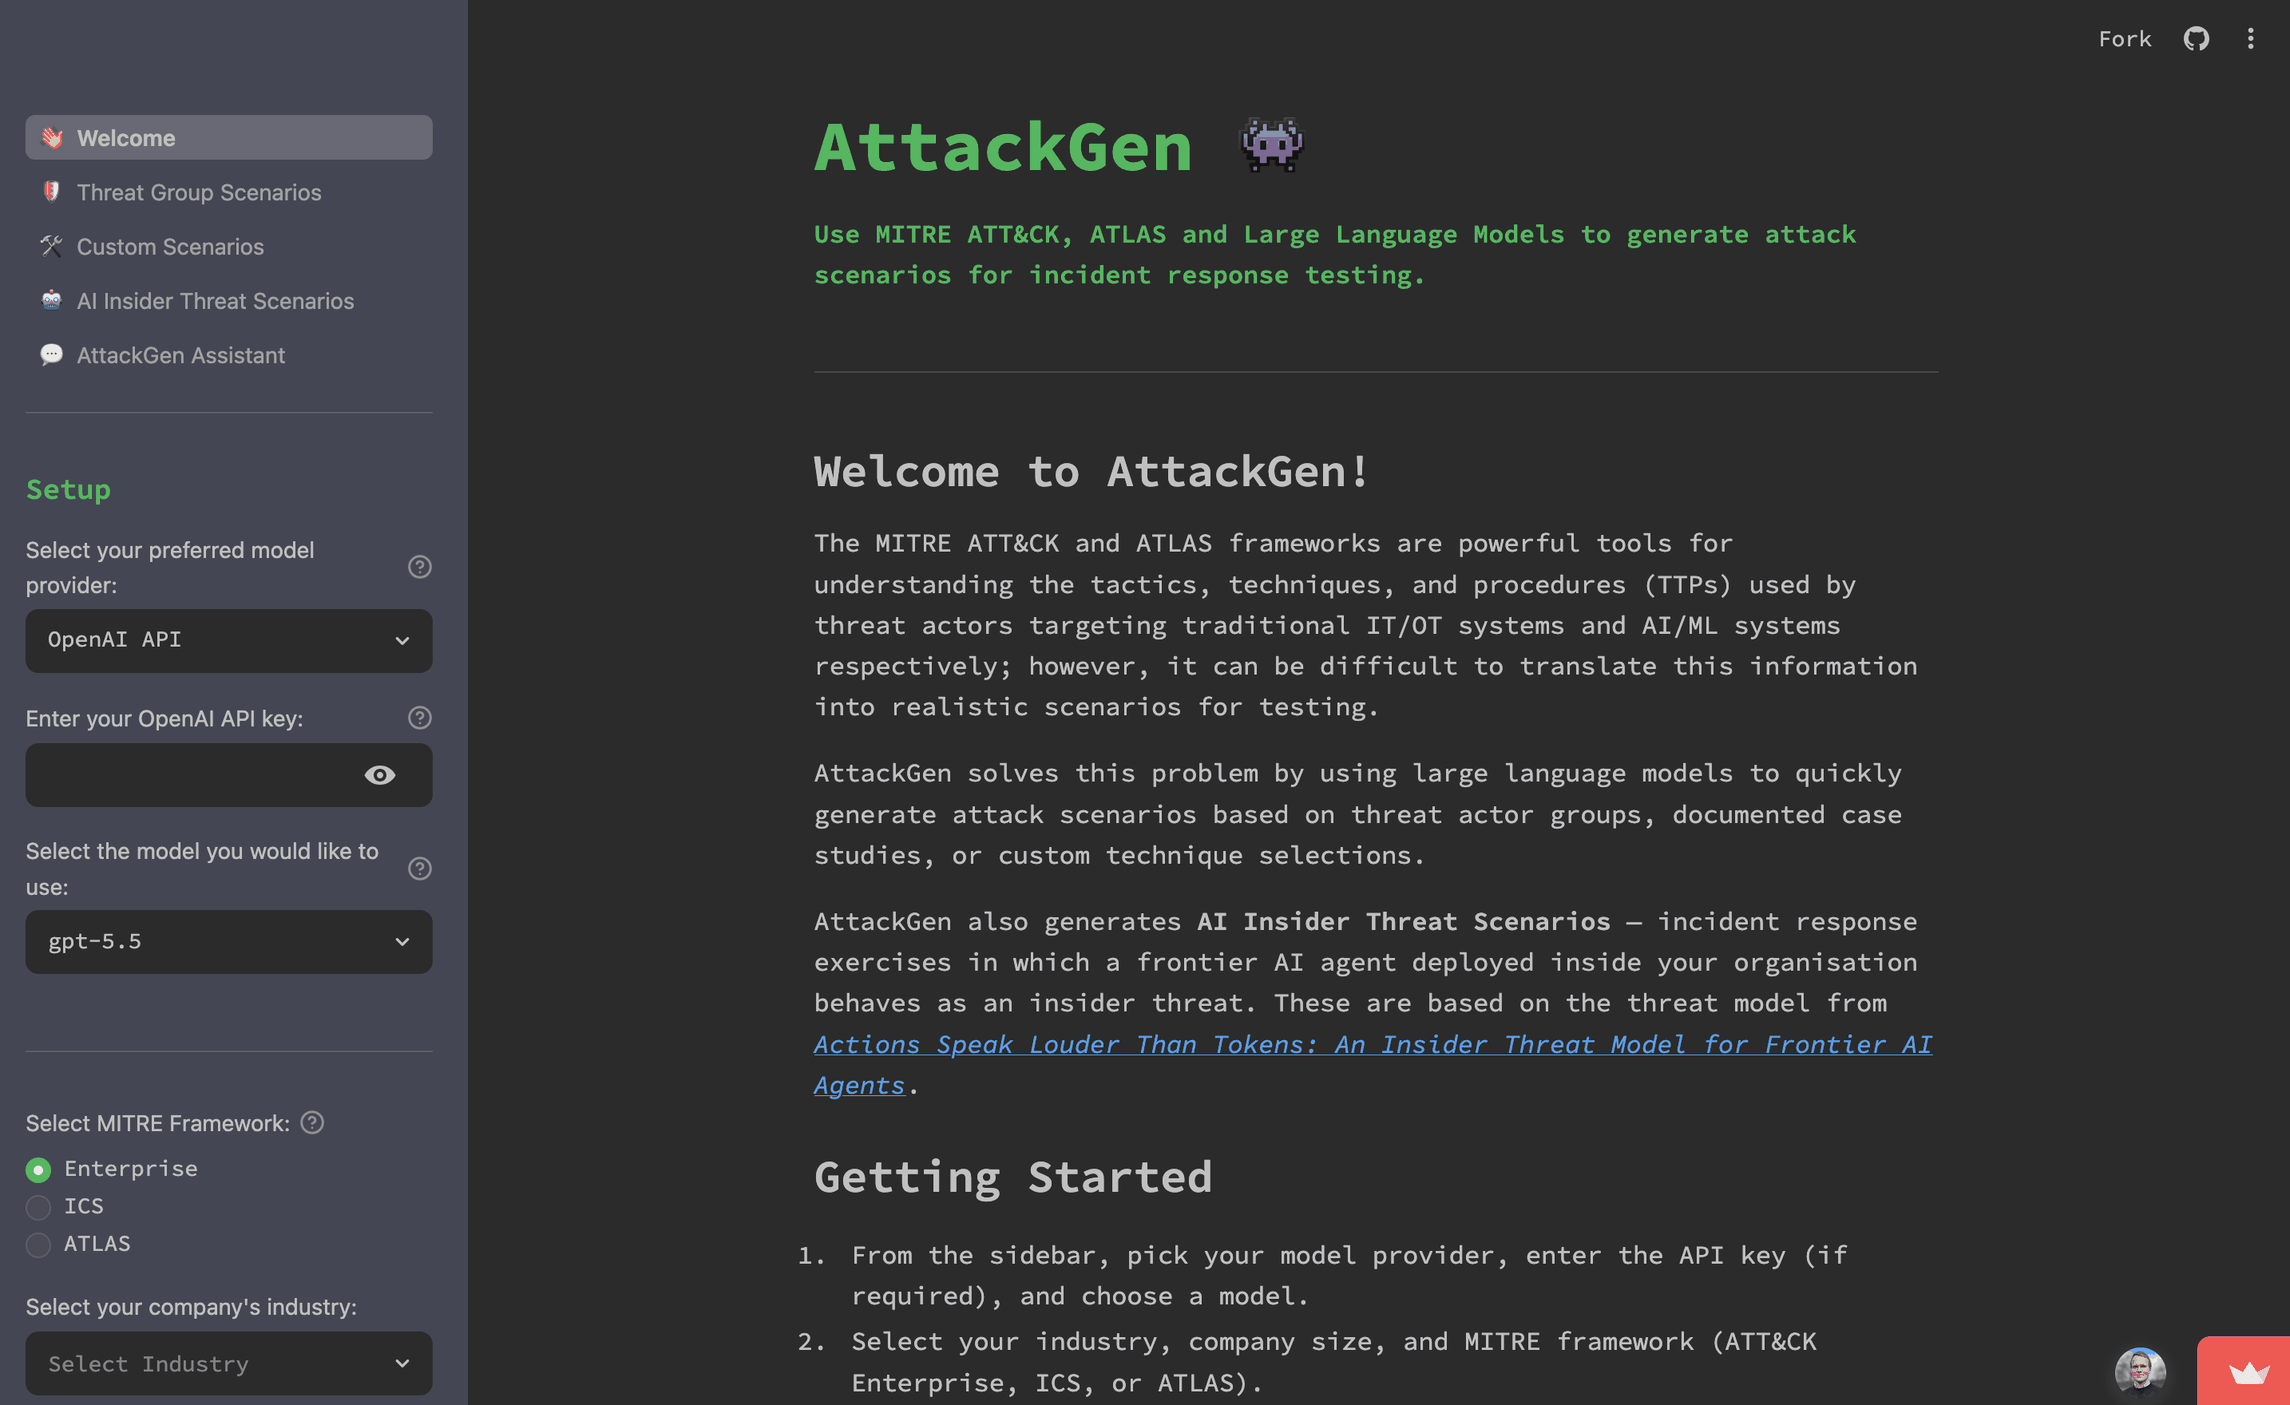 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 neo23x0/auditd
Best Practice Auditd Configuration
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
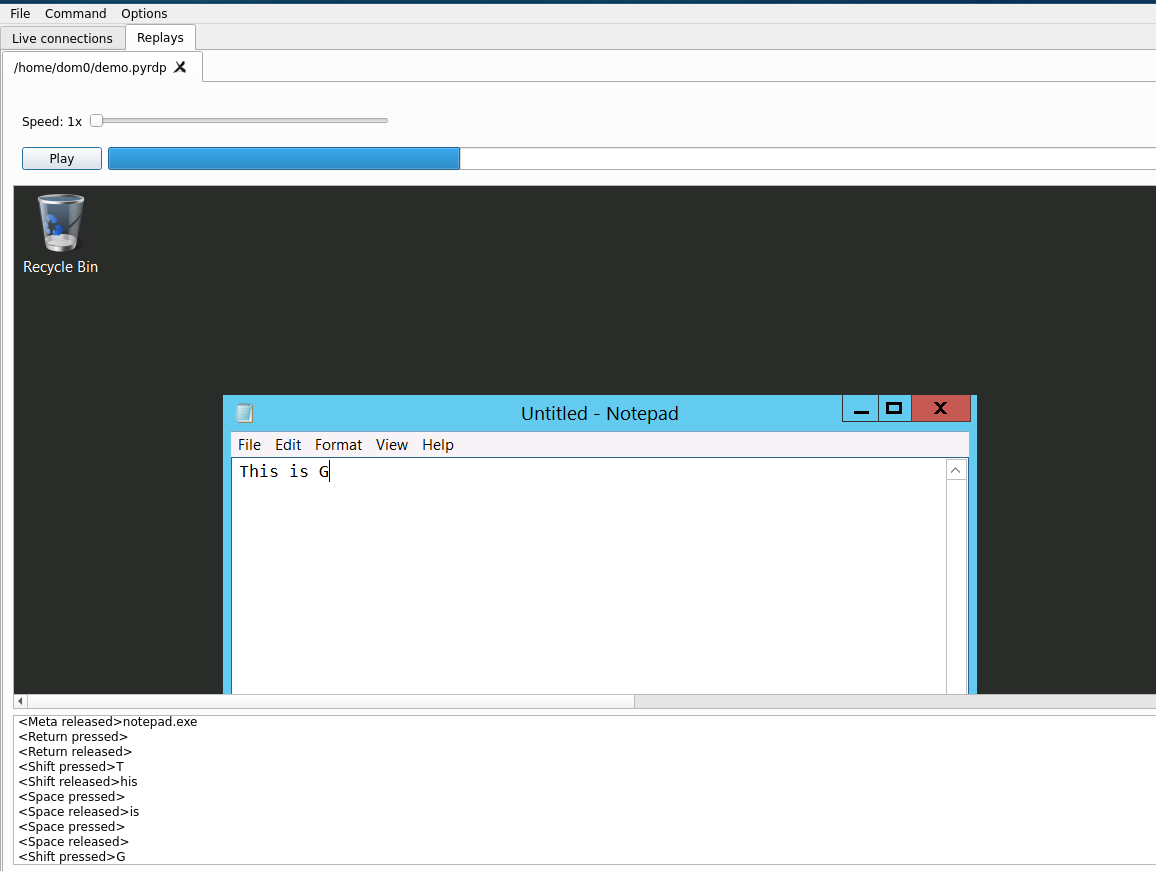 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
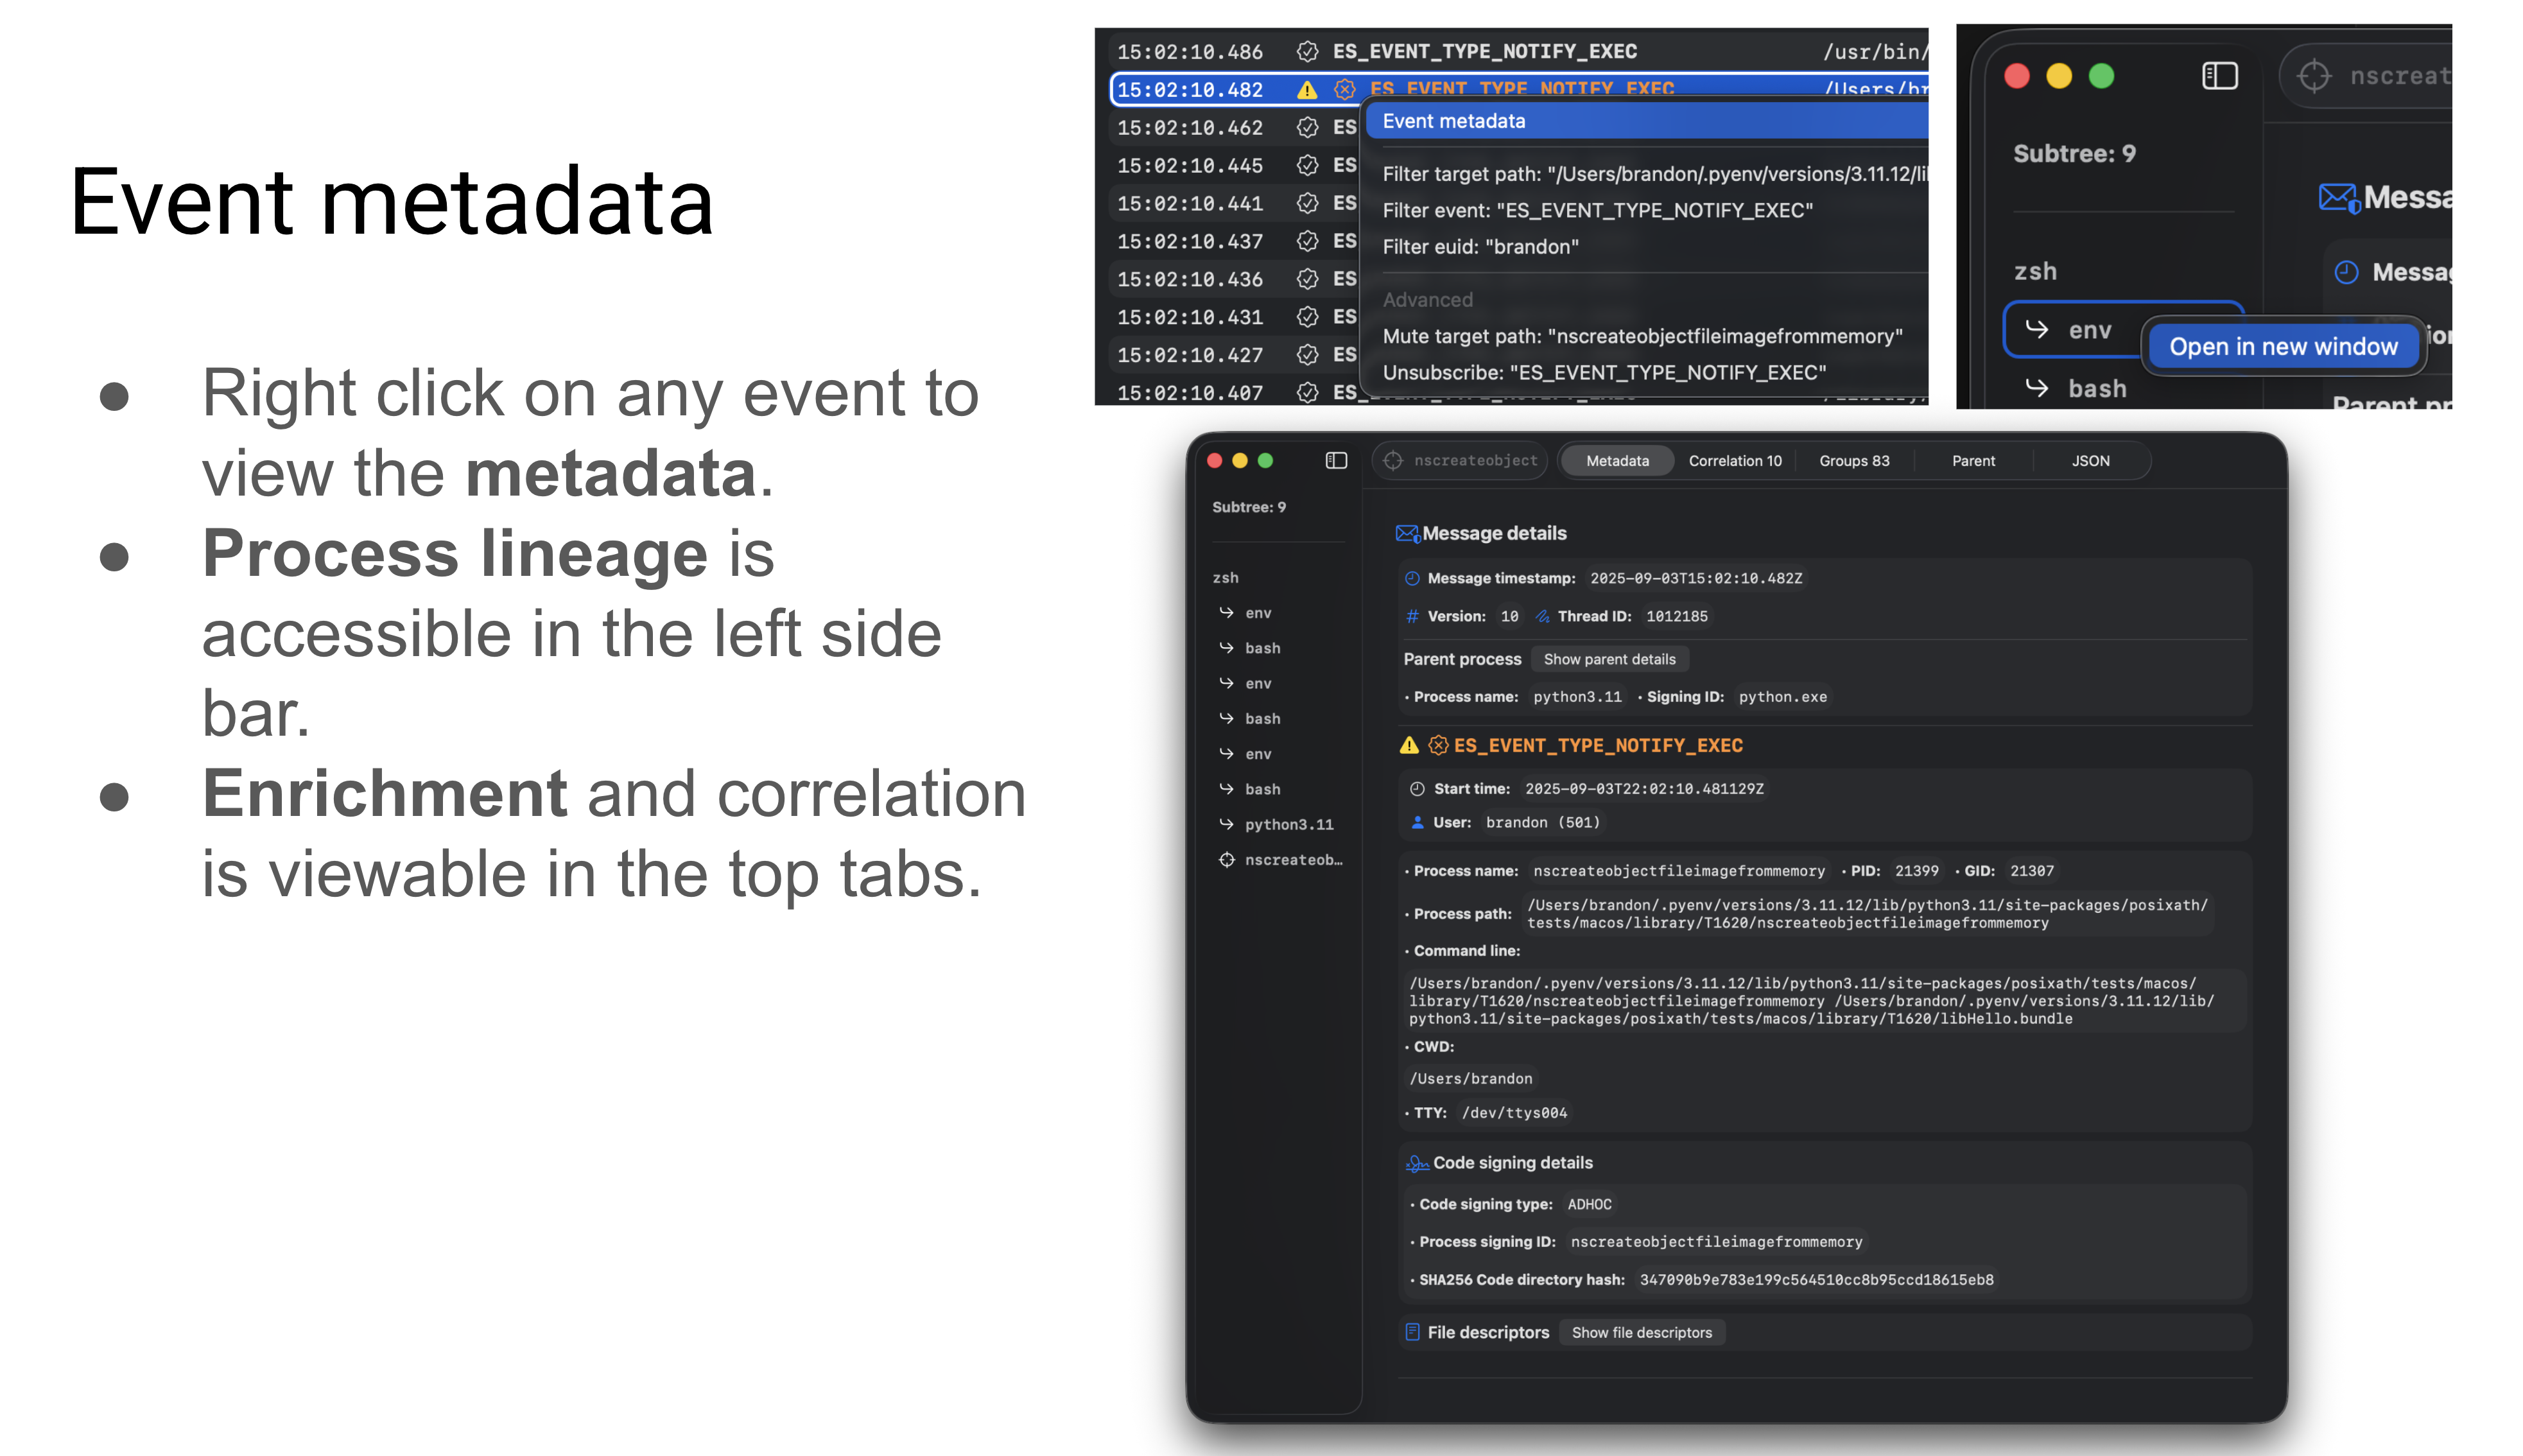 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 target/strelka
Real-time, container-based file scanning at enterprise scale
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 securitytemplates/sectemplates
Open source templates you can use to bootstrap your security programs
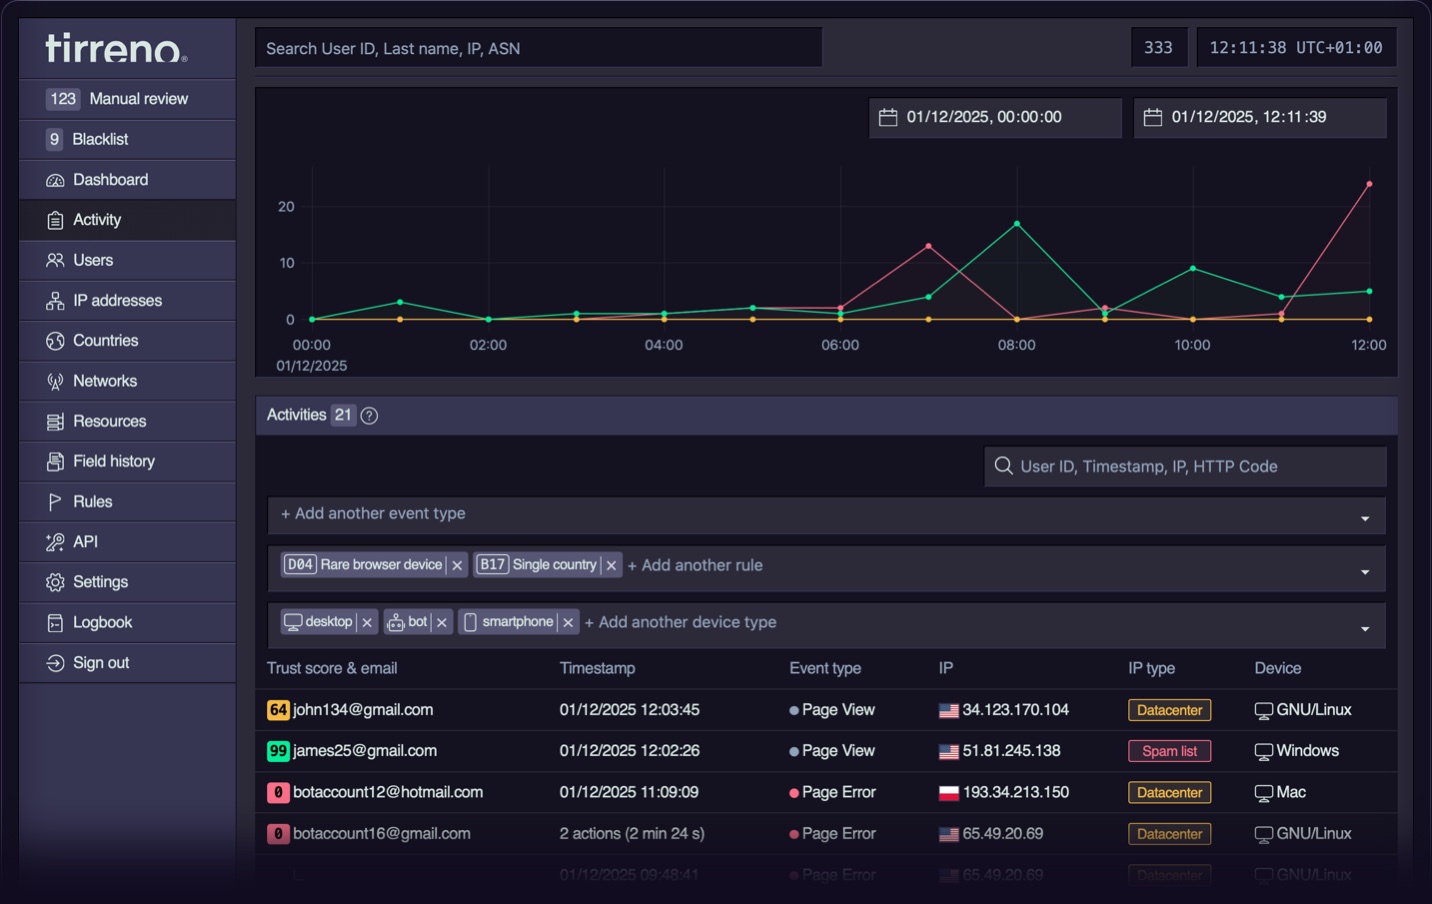 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 kubeshop/botkube
An app that helps you monitor your Kubernetes cluster, debug critical deployments & gives recommendations for standard practices
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…