
 #1
Hardware security modules, TPM, secure enclave, and hardware trust tools.
Kitploit recommended
 freax13/cve-2023-20573-poc
Proof-of-concept demonstrating CVE-2023-20573: a hardware vulnerability in AMD SEV-SNP that allows exception reinjection suppression in KVM, enabling…
 innotecsystem/device-reversing
Este repo contiene write-ups de reversing de dispositivos.
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
 ph4r05/ledger-app-monero-1.42-vuln
PoC repository for CVE-2020-6861: Ledger Monero App Spend key Extraction
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyer
Hardware-level security protocol for mitigating cache-based side-channel attacks.
 cyberaz0r/gl.inet-multiple-vulnerabilities
Exploits for GL.iNet CVE-2023-46454, CVE-2023-46455 and CVE-2023-46456
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 pussycat0x/cve-2021-40859
Auerswald VoIP System Secret Backdoors -PoC
 killvxk/cve-2021-3972
Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
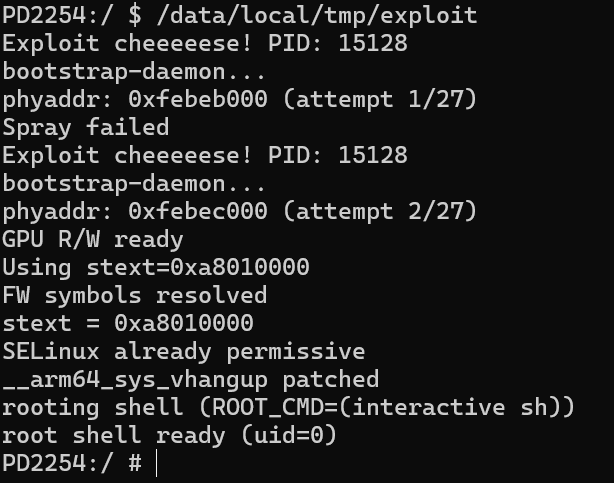 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research
 nccgroup/powerg-tools
Tools for reverse engineering and interacting with the PowerG radio protocol
 wizlab-it/anviz-m3-rfid-cve-2019-11523-poc
Anviz M3 RFID CVE-2019-11523 PoC
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…








