
 #1
Tools for assessing the security of physical hardware, embedded systems, and IoT devices.
Kitploit recommended

 yousif-iq/cve-2026-39259
CVE-2026-39259
 scy-phy/minicps
Real-time simulation framework for cyber-physical systems with physical process/control device models and Mininet-based network emulation, built for…
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 jiaoxianjun/btle
Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).
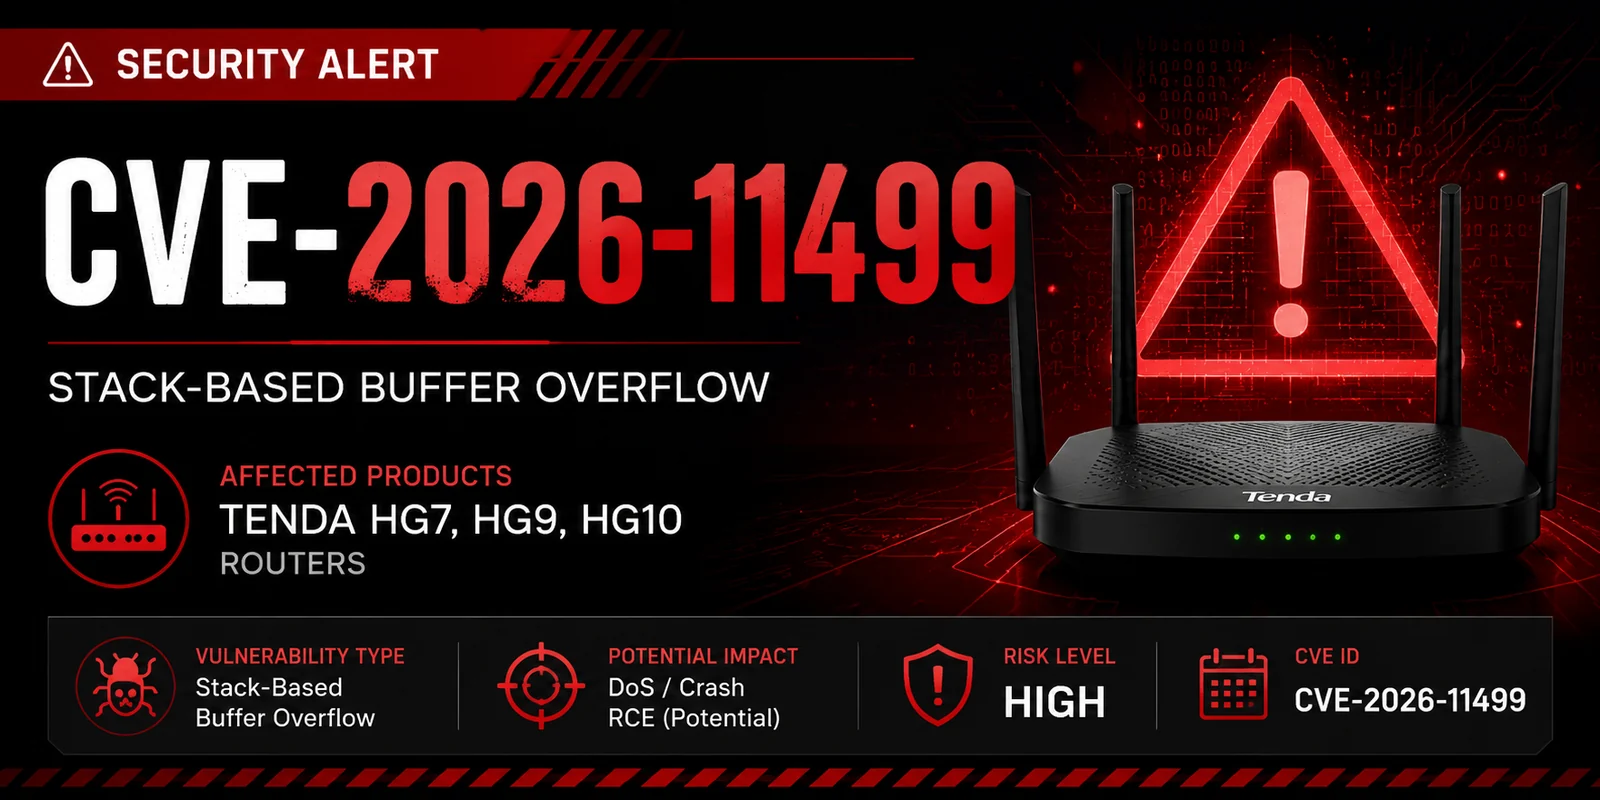 ashrafzaryouh/cve-2026-11499
Advisory and technical analysis of CVE-2026-11499, a stack-based buffer overflow (CWE-121) in Tenda HG7, HG9 and HG10 routers, covering impact,…
 0xblackash/cve-2026-11499
CVE-2026-11499
 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 yoloshii/privacy-first-network
Whole-home VPN router with kill switch. OpenWrt + WireGuard + AmneziaWG. Protects every device, no VPN apps needed.
 openl2d/moc3ingbird
MOC3ingbird Exploit for Live2D (CVE-2023-27566)
 gumbraise/cve-2024-54887-poc
TypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)








