
 #1
Fuzz testing, mutation-based, generation-based, and coverage-guided fuzzing tools.
Kitploit recommended

 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 thumpbo/cve-2025-30208-exp
CVE-2025-30208-EXP
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 cytopia/urlbuster
Powerful mutable web directory fuzzer to bruteforce existing and/or hidden files or directories.
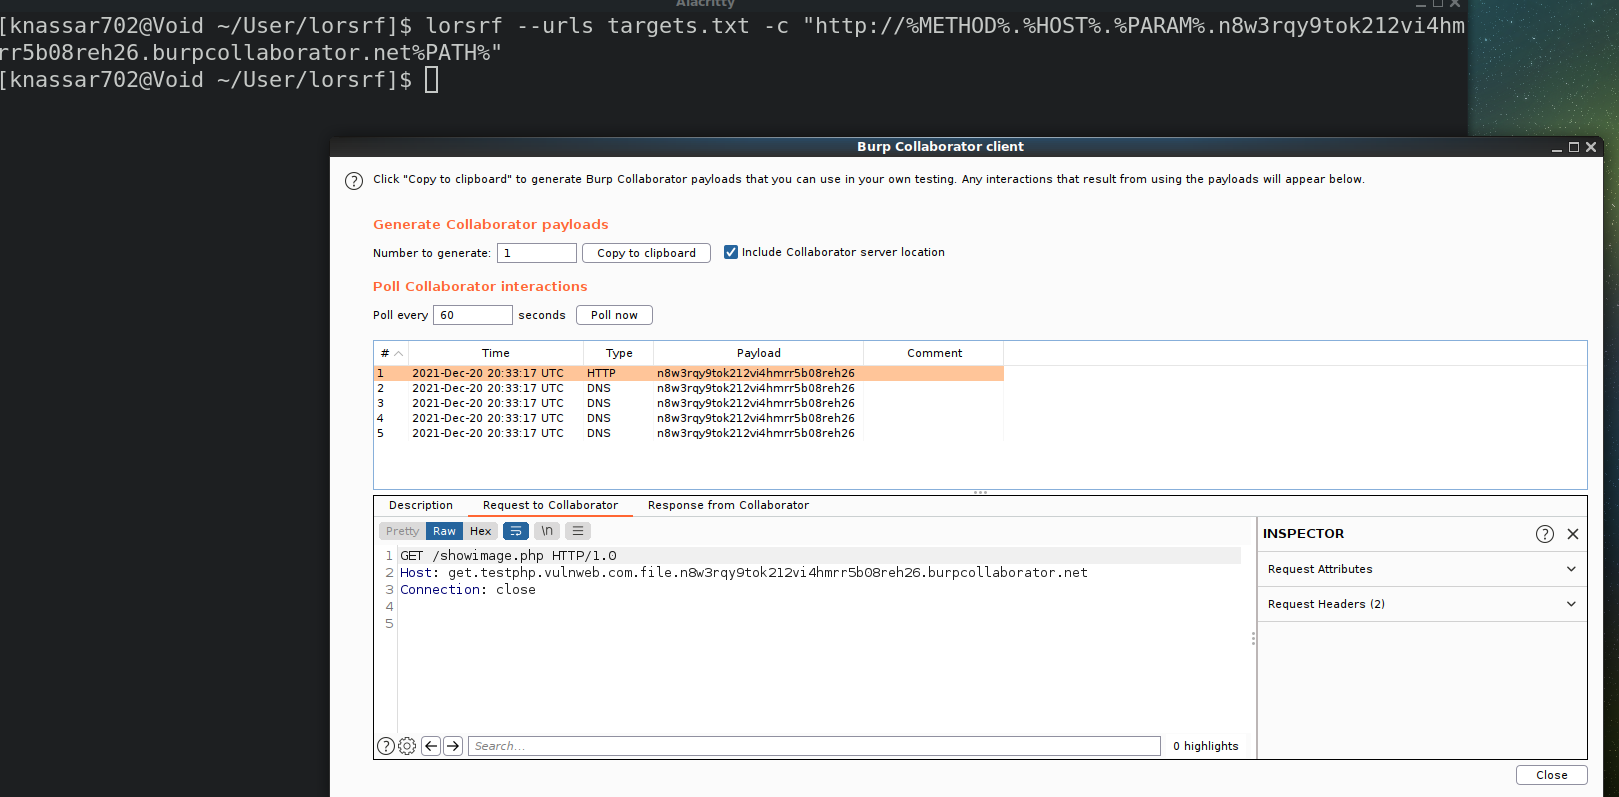 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
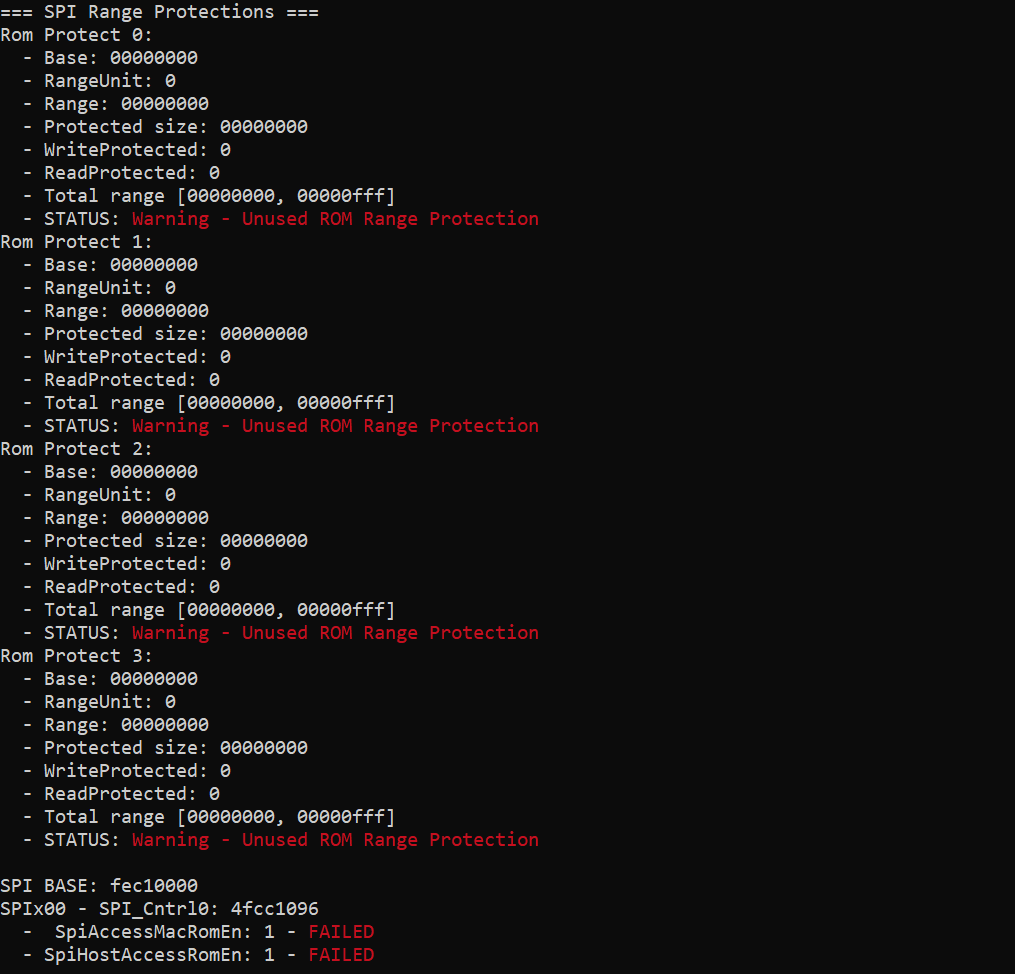 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 s0duku/cve-2022-31705
CVE-2022-31705 (Geekpwn 2022 Vmware EHCI OOB) POC
 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 niloofarkheirkhah/nili
Nili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
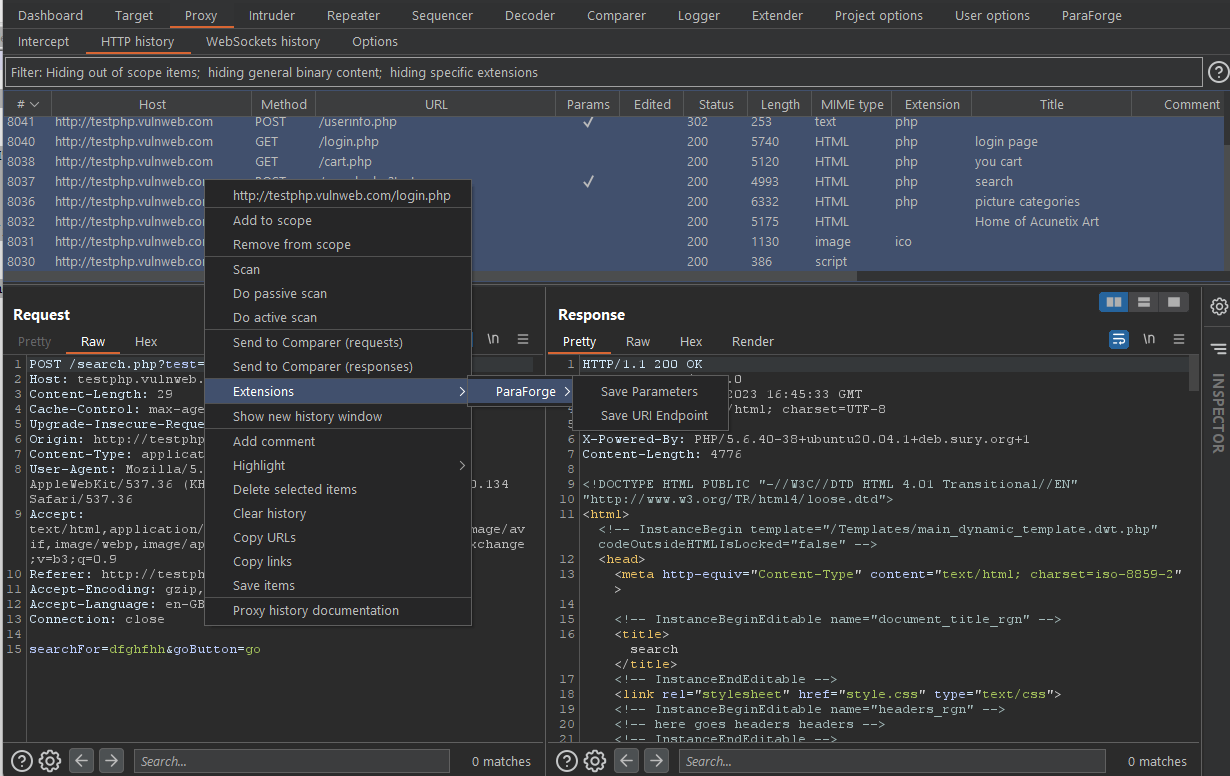 anof-cyber/paraforge
A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing
 henshin/filebuster
An extremely fast and flexible web fuzzer
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…








