#1
Digital forensics, evidence collection, timeline analysis, and incident investigation tools.
Kitploit recommended

 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
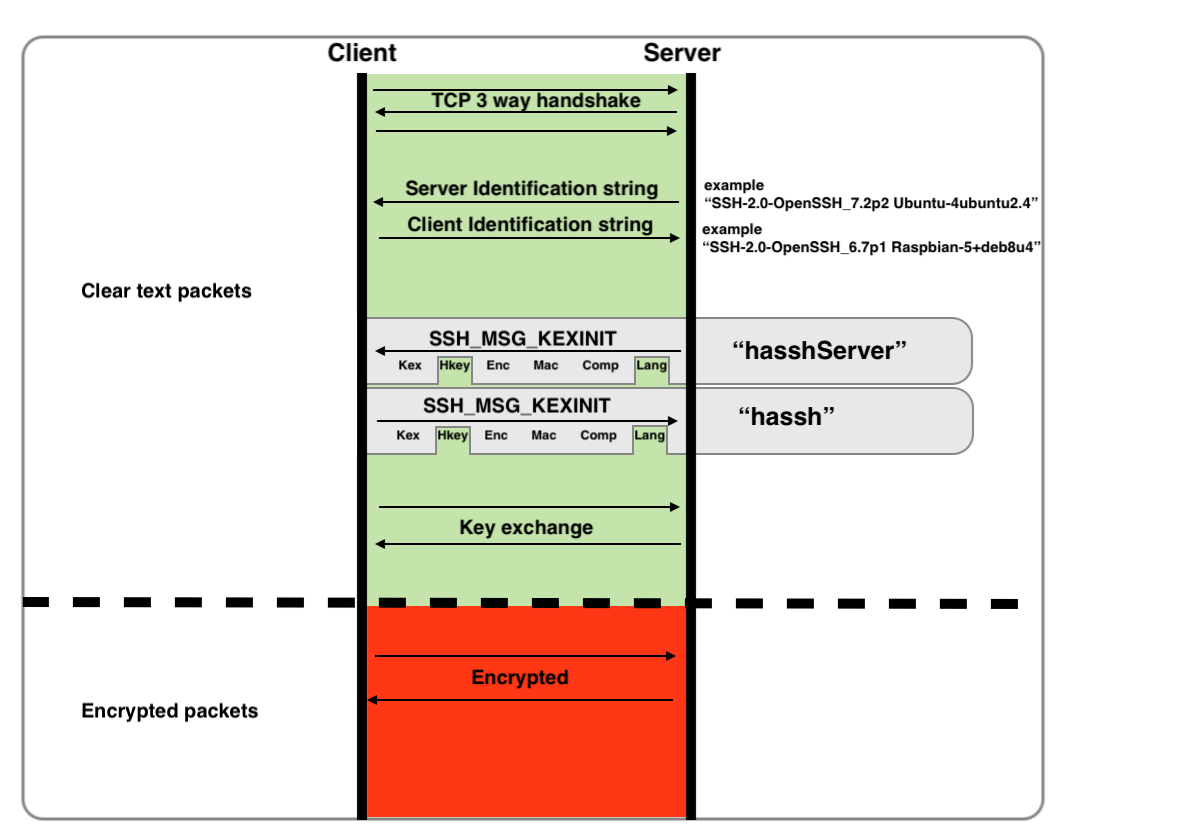 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 nowsecure/android-forensics
Open source Android Forensics app and framework
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 certcc/keyfinder
A tool for finding and analyzing private (and public) key files, including support for Android APK files.
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 504ensicslabs/damm
Differential Analysis of Malware in Memory
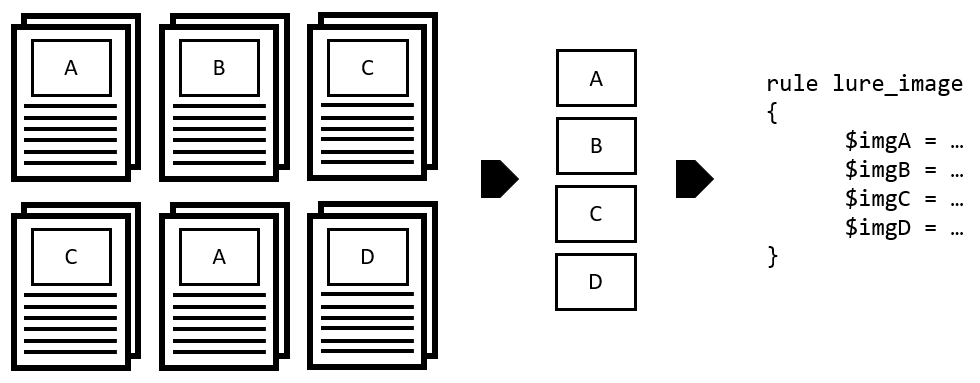 target/halogen
Automatically create YARA rules from malicious documents.
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
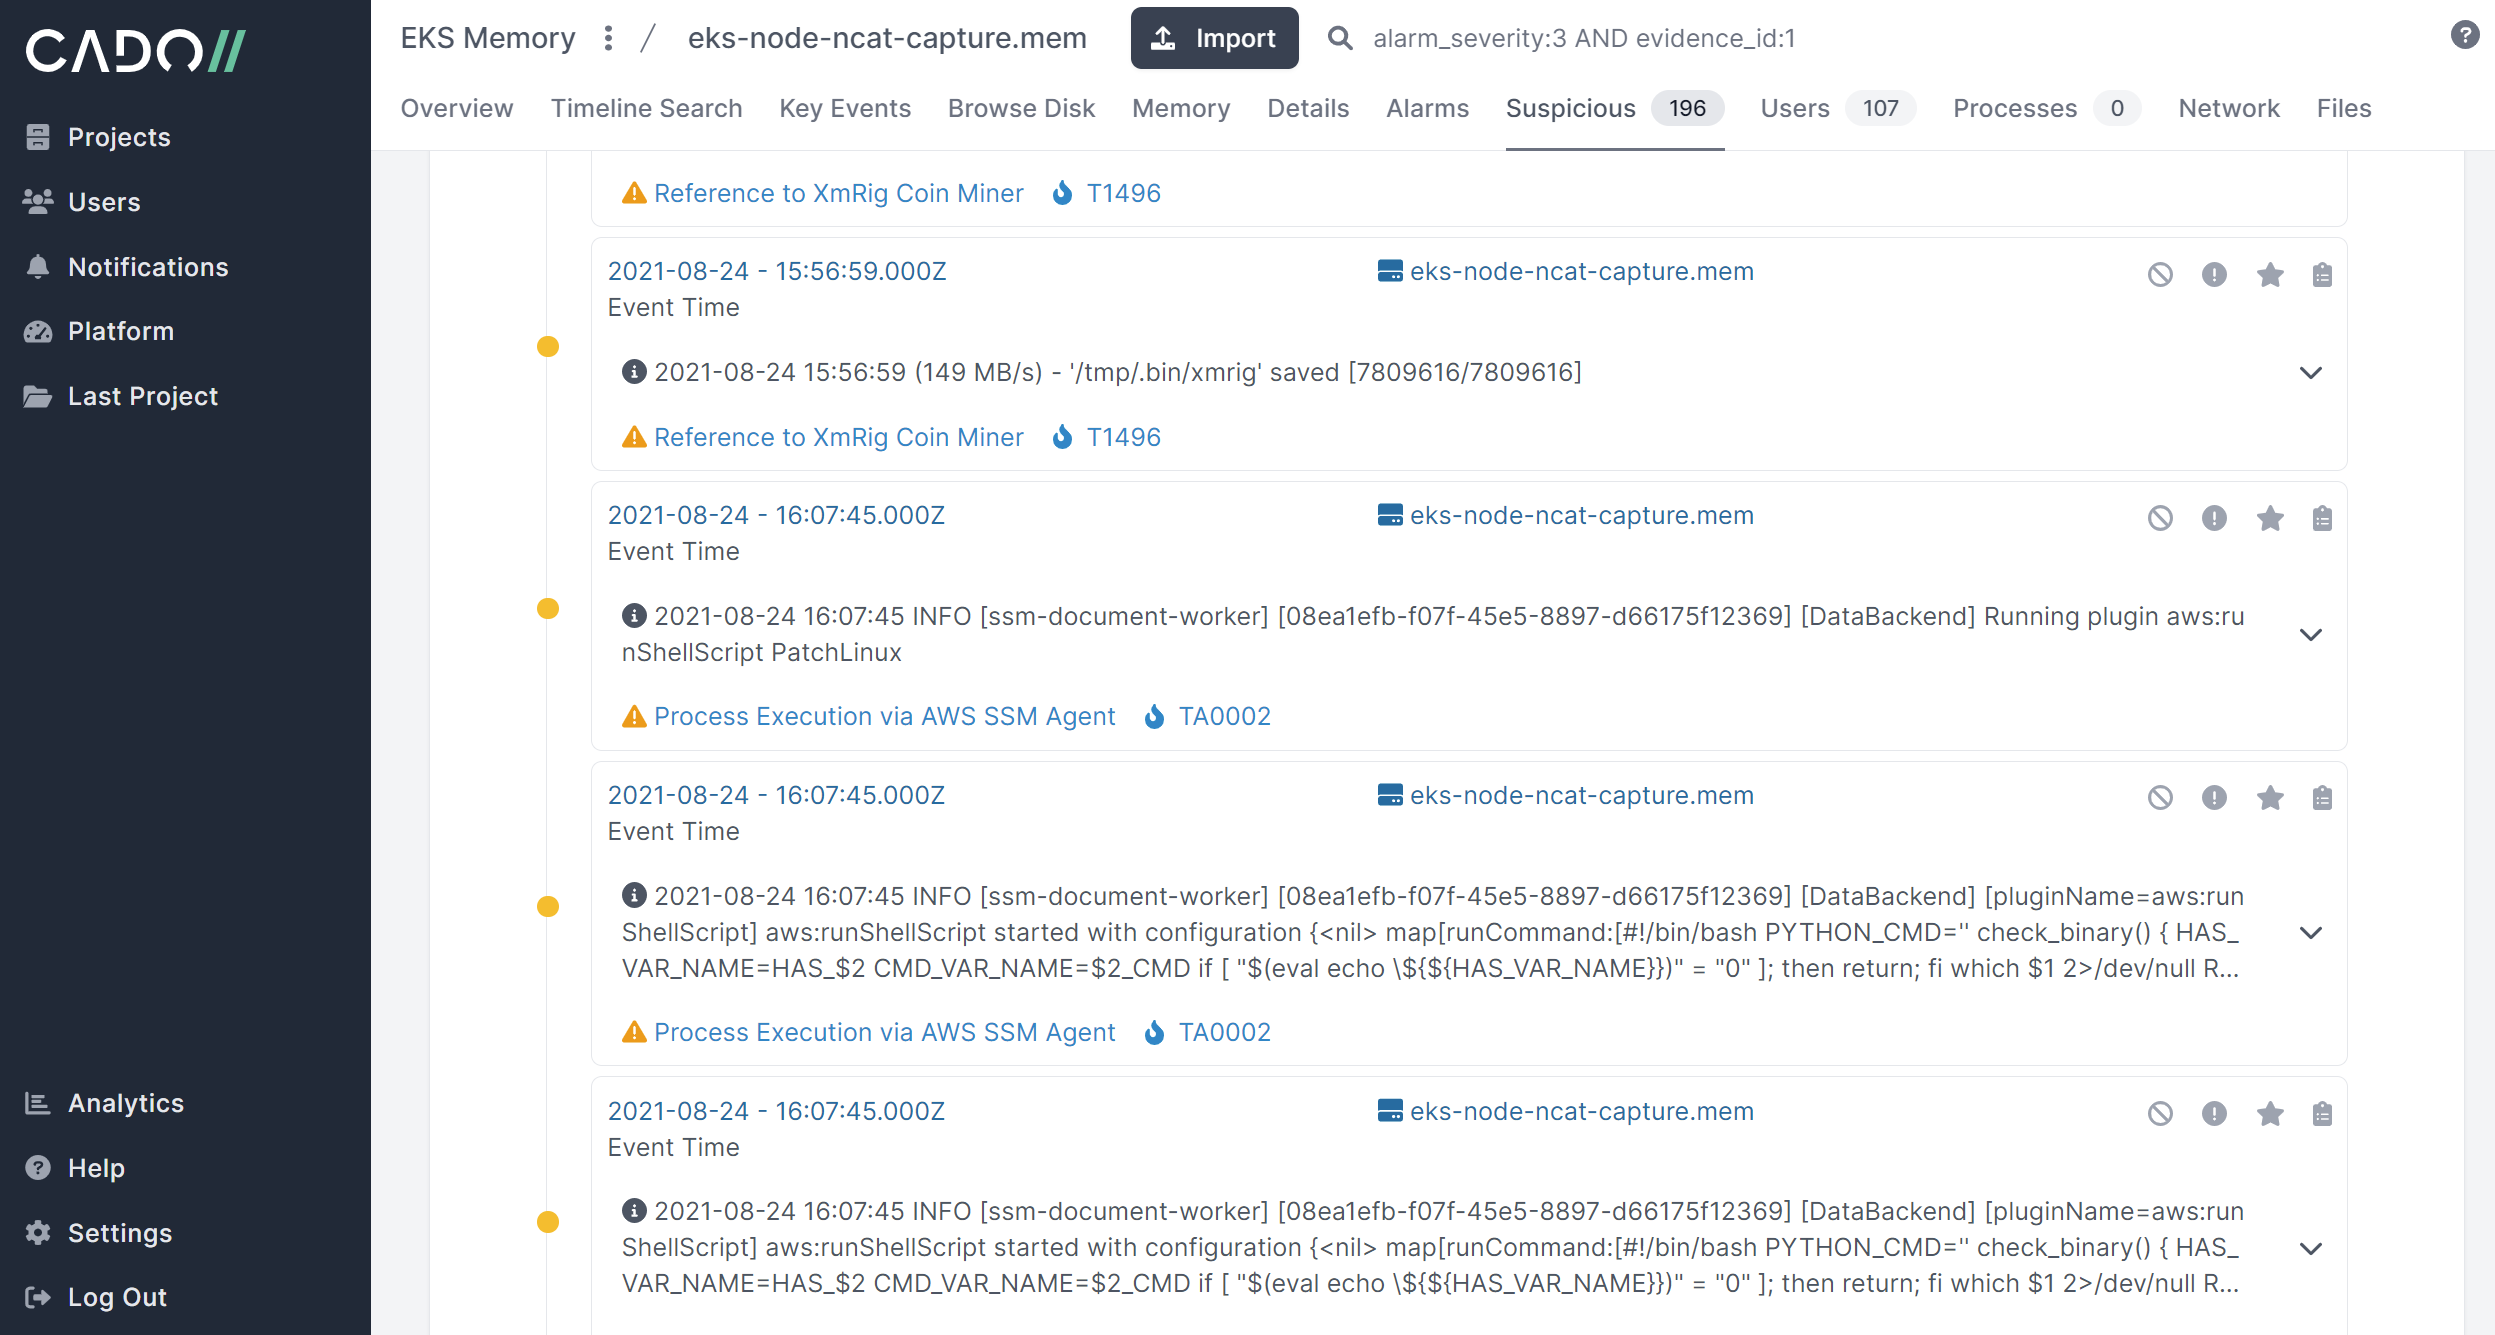 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
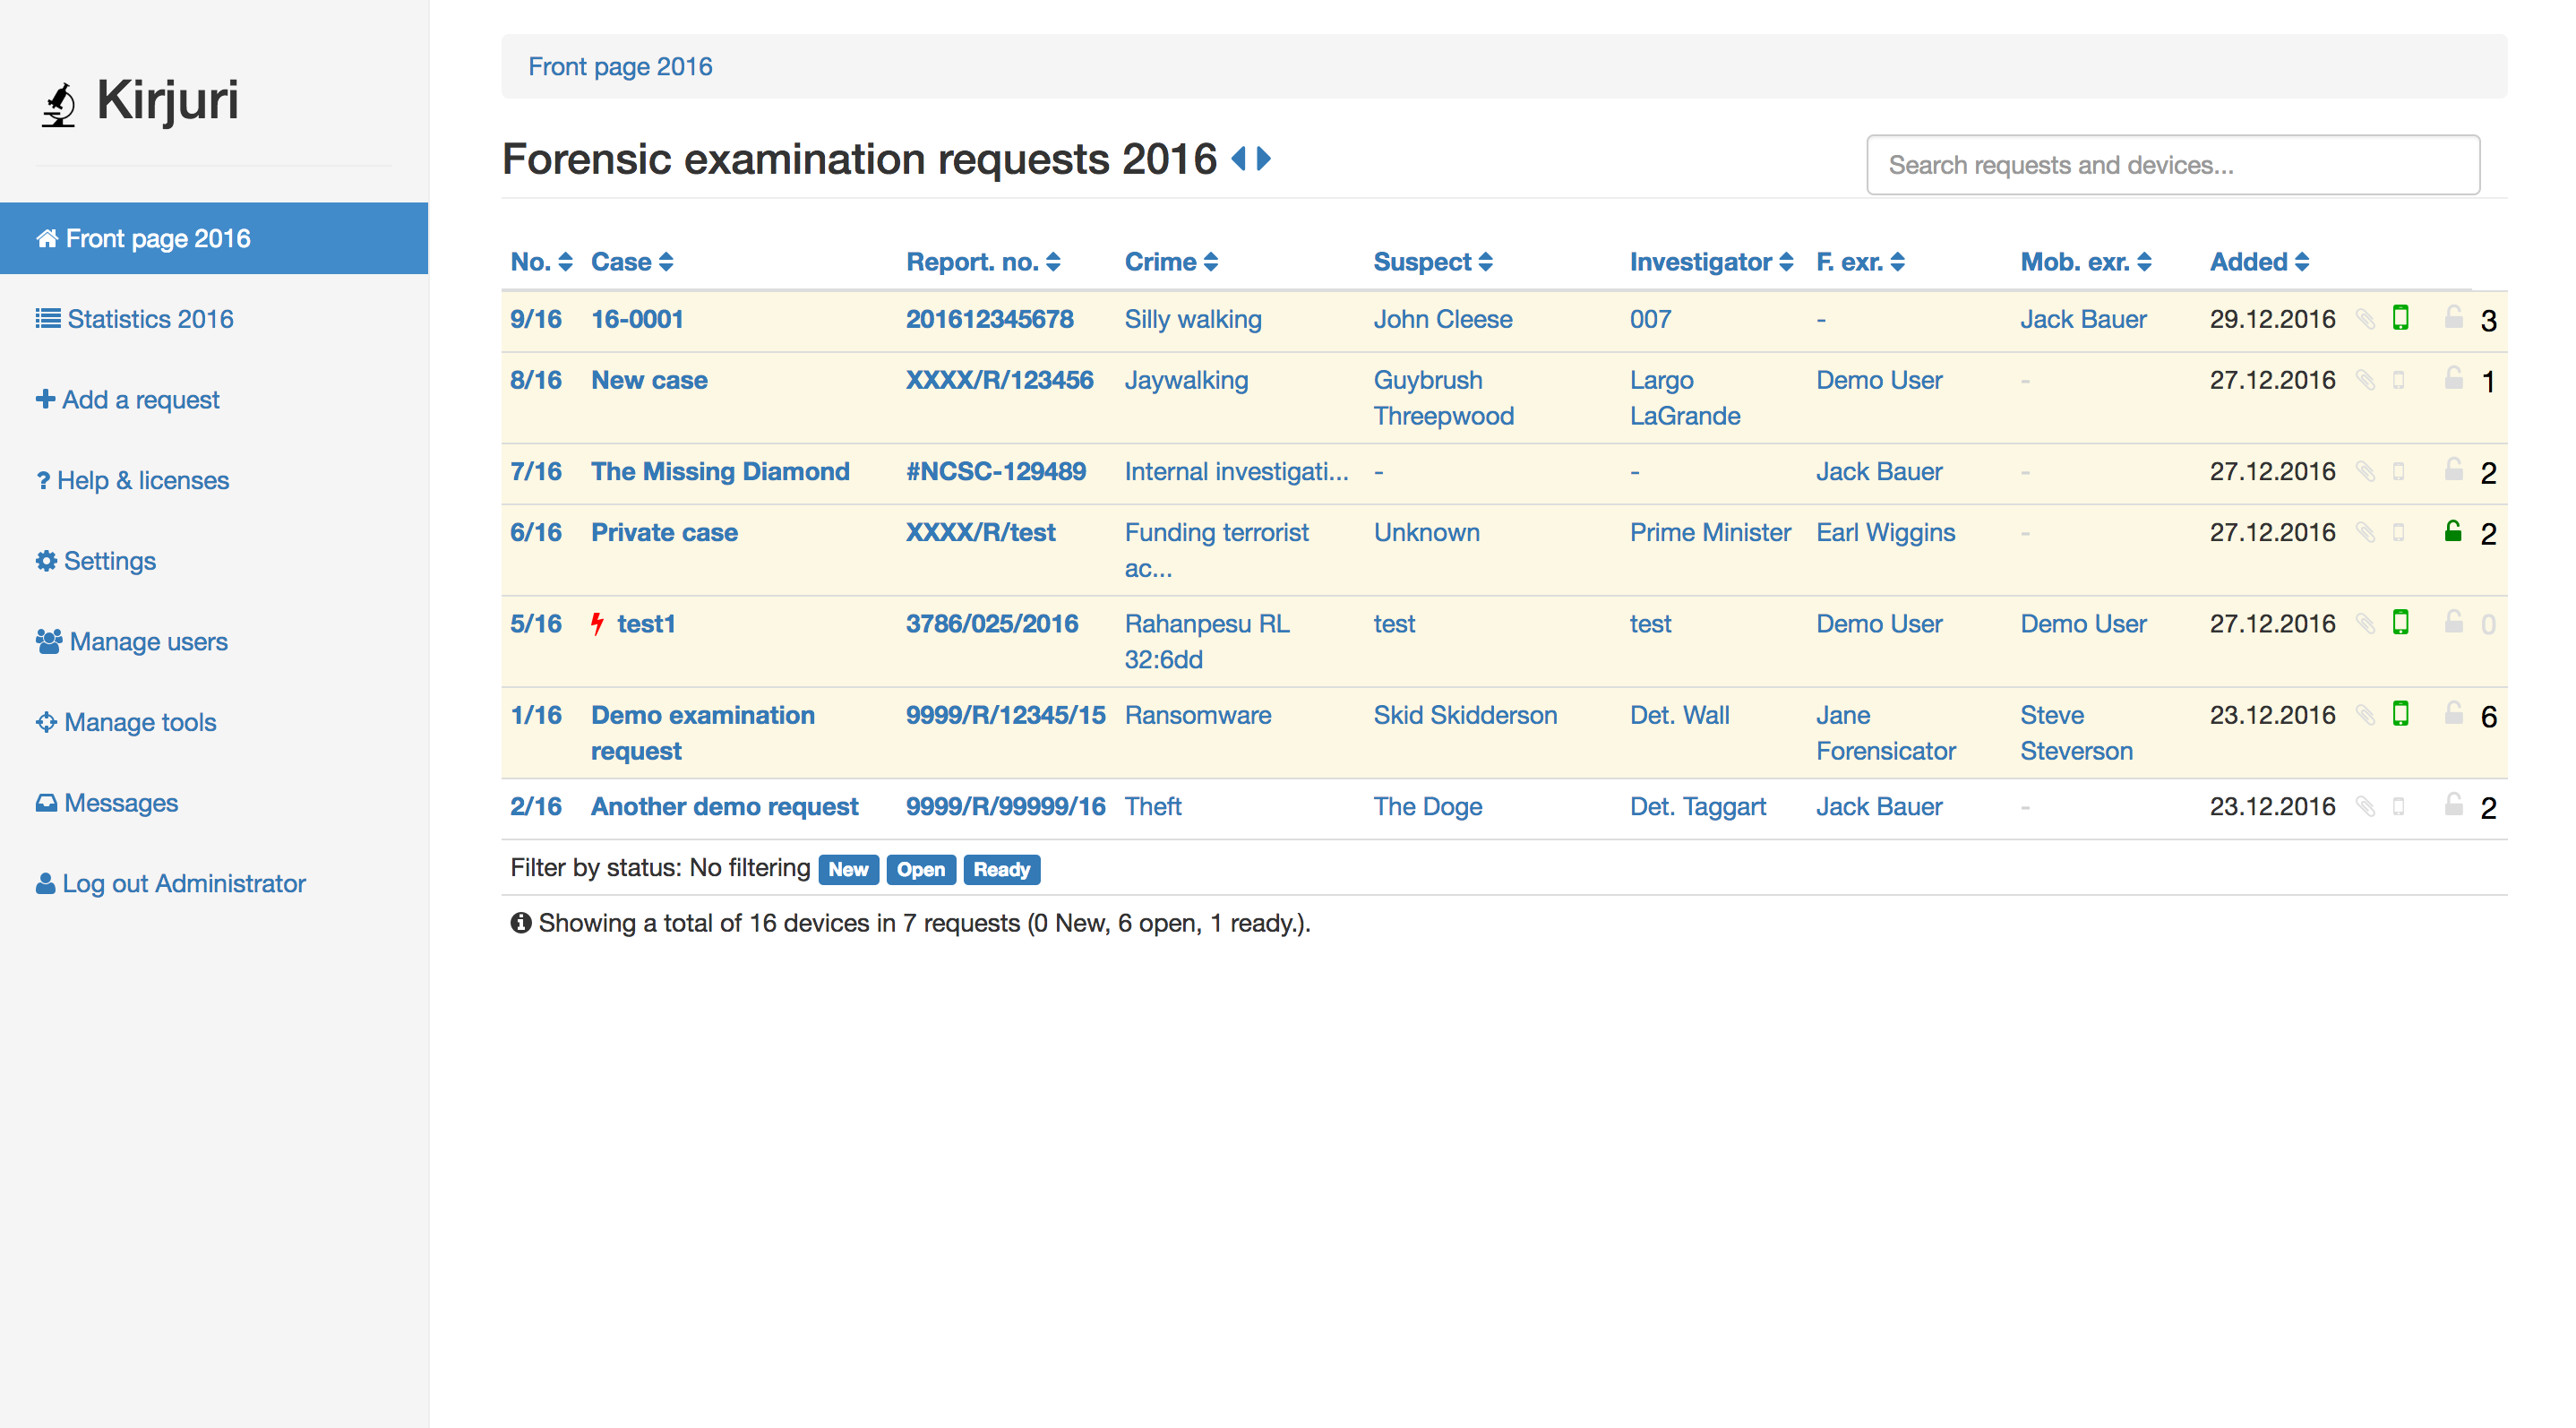 anttikurittu/kirjuri
Kirjuri is a web application for managing cases and physical forensic evidence items.
 cert-lv/exchange_webshell_detection
Detect webshells dropped on Microsoft Exchange servers exploited through "proxylogon" group of vulnerabilites (CVE-2021-26855, CVE-2021-26857,…
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781