
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Forensics | Kitploit
Categories

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit recommended

Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k4 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k7 days ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k6 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k11 days ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k23 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k13h 15m ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k3h 52m ago
mvt preview#8

mvt

GitHubmvt-project/mvt
14.6k2 days ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23023 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k22h 31m ago
NewestRelevanceMost popularRecently updated
909 results
cuckoo preview
Archived

cuckoo

GitHubcuckoosandbox/cuckoo

Cuckoo Sandbox is an automated dynamic malware analysis system

dynamic-analysis-sandboxingvulnerability-analysisforensics+2
6.0k4 years ago
frida-dexdump preview
Archived

frida-dexdump

GitHubhluwa/frida-dexdump

A frida tool to dump dex in memory to support security engineers analyzing malware.

android-securitydynamic-analysis-sandboxingmemory-forensics+5
4.6k3 years ago
Depixelization_poc preview
Archived

Depixelization_poc

GitHubspipm/depixelization_poc

Depix is a PoC for a technique to recover plaintext from pixelized screenshots.
osintencryption-decryption-toolsforensics+3
4.5k5 months ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

memory-forensicsreverse-engineeringforensics+3
2.0k5 years ago
PacketStreamer preview
Archived

PacketStreamer

GitHubdeepfence/packetstreamer

⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
packet-sniffing-analysiscontainer-securitynetwork-mapping+6
1.9k2 years ago
osxcollector preview
Archived

osxcollector

GitHubyelparchive/osxcollector

A forensic evidence collection & analysis toolkit for OS X

disk-forensicsosintmemory-forensics+3
1.9k7 years ago
malice preview
Archived

malice

GitHubmaliceio/malice

VirusTotal Wanna Be - Now with 100% more Hipster
container-securitydynamic-analysis-sandboxingvulnerability-analysis+6
1.9k3 years ago
stenographer preview
Archived

stenographer

GitHubgoogle/stenographer

Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…

packet-sniffing-analysisnetwork-forensicsforensics+3
1.8k5 years ago
viper preview
Archived

viper

GitHubviper-framework/viper

Binary analysis and management framework
exploit-frameworksvulnerability-analysisreverse-engineering+3
1.6k3 years ago
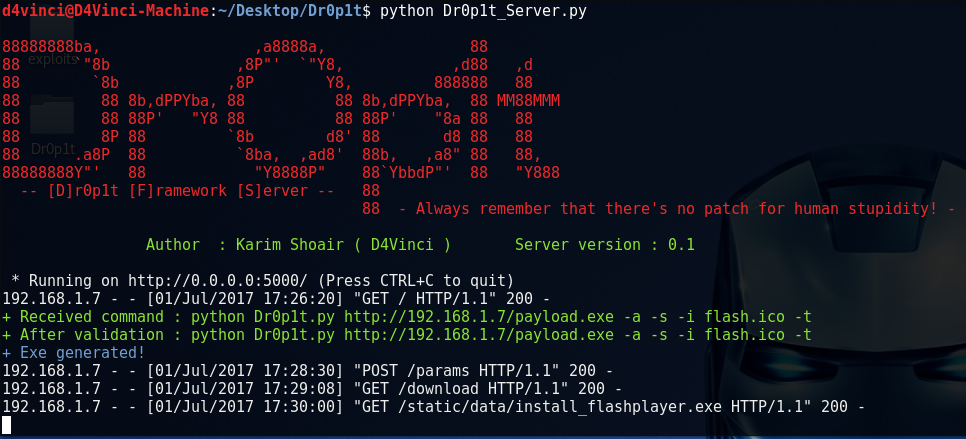
Dr0p1t-Framework preview
Archived

Dr0p1t-Framework

GitHubd4vinci/dr0p1t-framework

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
privilege-escalationpayload-generationpersistence-mechanisms+9
1.5k7 years ago
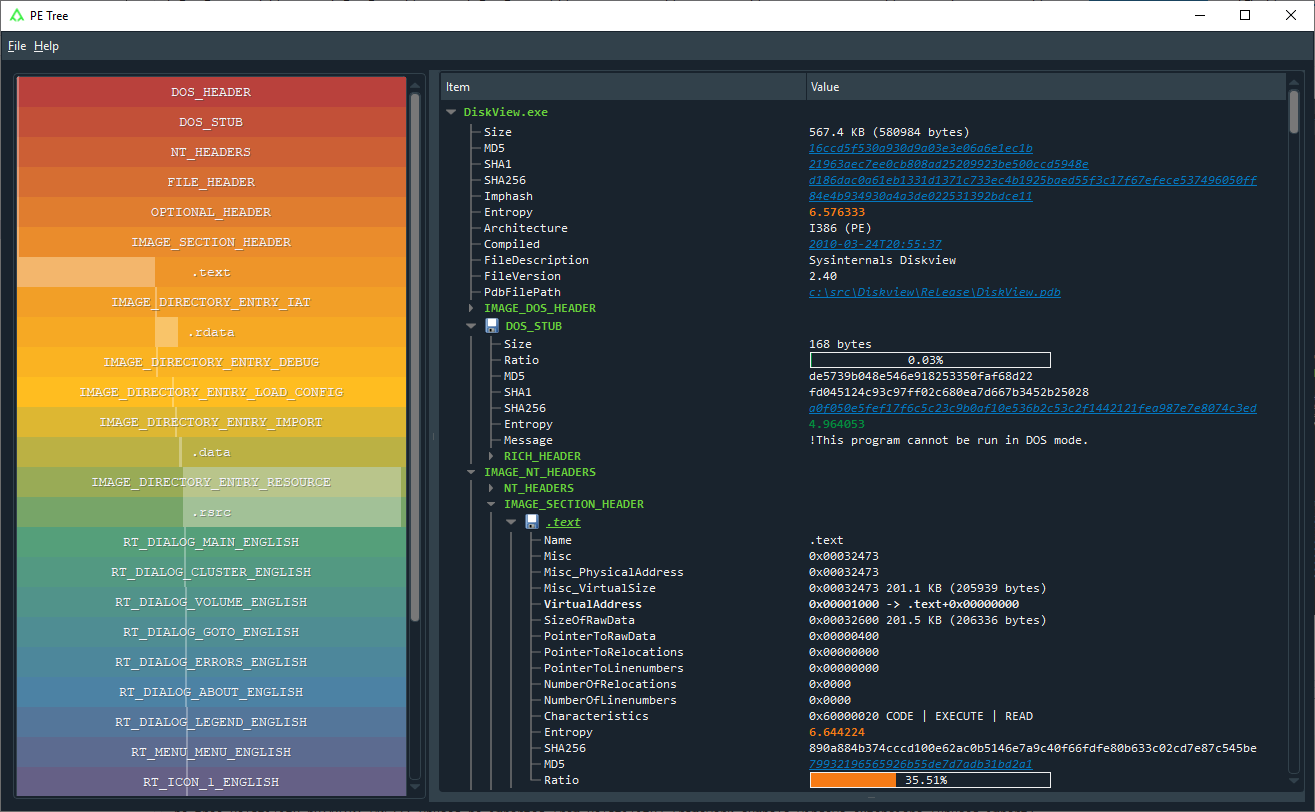
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
memory-forensicsvulnerability-analysisreverse-engineering+5
1.3k4 years ago
mig preview
Archived

mig

GitHubmozilla/mig

Distributed & real time digital forensics at the speed of the cloud
disk-forensicsmemory-forensicsvulnerability-analysis+6
1.2k7 years ago
usbrip preview
Archived

usbrip

GitHubsnovvcrash/usbrip

Tracking history of USB events on GNU/Linux

forensicsdigital-forensicsthreat-intelligence+2
1.2k3 years ago
LSB-Steganography preview
Archived

LSB-Steganography

GitHubrobindavid/lsb-steganography

Python program to steganography files into images using the Least Significant Bit.
encryption-decryption-toolsdata-exfiltrationforensics+3
9574 years ago
SilkETW preview
Archived

SilkETW

GitHubmandiant/silketw

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

defensive-toolsmemory-forensicsforensics+8
8523 years ago
MIDAS preview
Archived

MIDAS

GitHubetsy/midas

Mac Intrusion Detection Analysis System

defensive-toolsforensicsintrusion-detection+2
82611 years ago
grapl preview
Archived

grapl

GitHubgrapl-security/grapl

Graph platform for Detection and Response

reconnaissancethreat-feeds-aggregatorsforensics+8
6993 years ago
StalkPhish preview
Archived

StalkPhish

GitHubt4d/stalkphish

StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
osintforensicsinformation-gathering+3
6692 years ago
Previous1…48495051Next