Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Forensics — Page 28 | Kitploit
Categories

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit recommended

Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k6 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k5 days ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k21 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k9h 50m ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k21 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k12h 3m ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k7 days ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.7k4 days ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23013 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k9 days ago
NewestRelevanceMost popularRecently updated
942 results
gargamel preview

gargamel

GitHublifars/gargamel

A forensic evidence acquirer

memory-forensicsforensicsinformation-gathering+3
865 years ago
autoresponder preview

autoresponder

GitHublawiet47/autoresponder

Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…
forensicsincident-response
566 years ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files

static-analysisreverse-engineeringforensics+2
998 months ago
citrix-2025 preview

citrix-2025

GitHubncsc-nl/citrix-2025

Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…

forensicsnetwork-securitydigital-forensics+2
521 year ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolspersistence-mechanismshash-analysis+4
661 year ago
Exif-Grabber preview

Exif-Grabber

GitHubd4vinci/exif-grabber

A python tool that will extract exif data from picture with two methods
osintforensicsinformation-gathering+3
4210 years ago
syd preview

syd

GitHubsydsec/syd

Offline AI Security Assistant for Air-Gapped Pentesting

osintmemory-forensicsvulnerability-analysis+8
866 months ago
OpenFPC preview

OpenFPC

GitHubleonward/openfpc

OpenFPC, Open Source Full Packet Capture

packet-sniffing-analysisnetwork-forensicsforensics+1
7310 years ago
TransitionPlayer preview

TransitionPlayer

GitHubcanyie/transitionplayer

CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
android-securityprivilege-escalationexploitation+4
322 months ago
sandy preview

sandy

GitHubdonctl/sandy

Release of the sandy framework.
android-securityencryption-decryption-toolspassword-attacks+5
3912 years ago
iocs preview

iocs

GitHubnextronsystems/iocs

Indicators of compromise from to analysis and research by Nextron Threat Research team

ioc-managementthreat-feeds-aggregatorsforensics+4
233 days ago
truehunter preview

truehunter

GitHubadoreste/truehunter

Truehunter

disk-forensicsencryption-decryption-toolsforensics+2
317 years ago
evtx-baseline preview

evtx-baseline

GitHubnextronsystems/evtx-baseline

A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
forensicsdigital-forensicseducation+2
932 years ago
CVE-2025-24104 preview

CVE-2025-24104

GitHubifpdz/cve-2025-24104

Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…
ios-securityvulnerability-analysisexploitation+4
511 year ago
filterforge preview

filterforge

GitHubcloudflare/filterforge

Tool for solving BPF filters and crafting packets based on these.
packet-sniffing-analysisvulnerability-analysisreverse-engineering+5
637 months ago
dpapi-toolkit preview

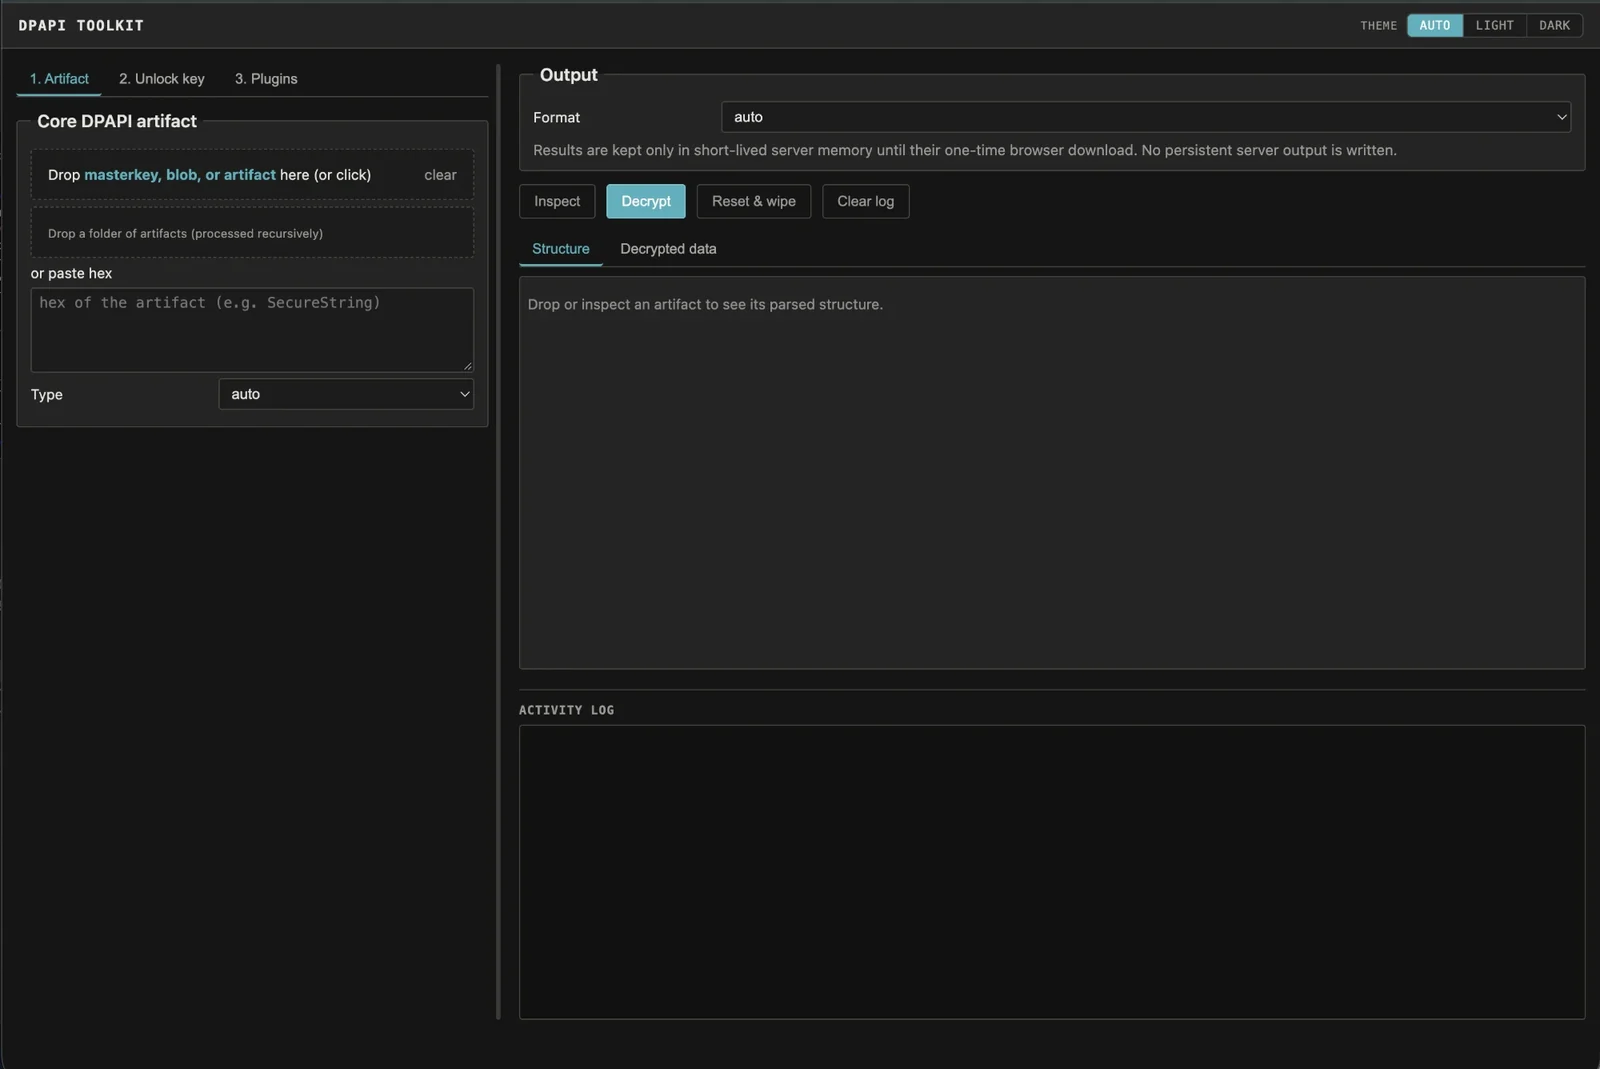
dpapi-toolkit

GitHubcrypt0p3g/dpapi-toolkit

Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
password-crackingencryption-decryption-toolshash-analysis+7
301 month ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

dynamic-analysis-sandboxingmemory-forensicsvulnerability-analysis+7
584 months ago
macos-collector preview

macos-collector

GitHublethal-forensics/macos-collector

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

persistence-mechanismsforensicsdigital-forensics+2
491 month ago
Previous1…272829…53Next